MXNB Audit 2024
CertiK reviewed MXNB (MXNB Audit 2024) on 15 May 2024: 3 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 0 |
HighCentralization Related RisksOpen
In the contract `Rescuable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the rescuer address. 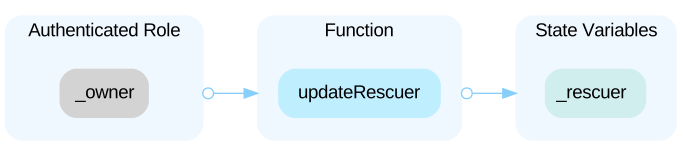 In the contract `Rescuable` the role `_rescuer` has authority over the functions shown in the diagram below. Any compromise to the `_rescuer` account may allow the hacker to take advantage of this authority and transfer tokens in this contract to any address. 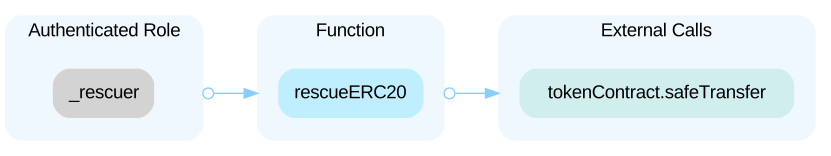 ----- In the contract `Blacklistable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the blacklister address. 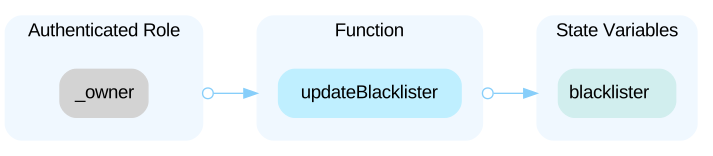 In the contract `Blacklistable` the role `blacklister` has authority over the functions shown in the diagram below. Any compromise to the `blacklister` account may allow the hacker to take advantage of this authority and add an account to the blacklist and remove the account from the blacklist. 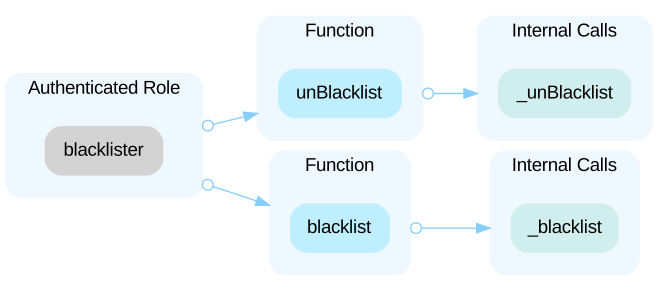 ----- In the contract `FiatTokenV1` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the master minter address. 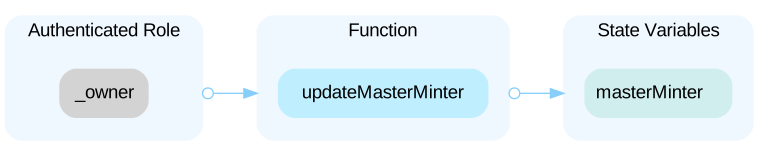 In the contract `FiatTokenV1` the role `masterMinter` has authority over the functions shown in the diagram below. Any compromise to the `masterMinter` account may allow the hacker to take advantage of this authority and add or update a new minter with a mint allowance and remove a minter. 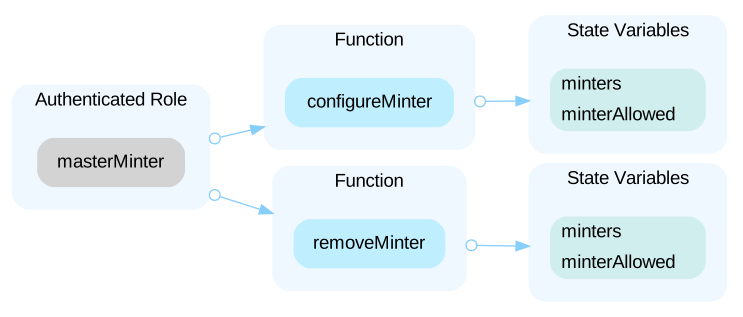 In the contract `FiatTokenV1` the role `minters` has authority over the functions shown in the diagram below. Any compromise to the `minters` account may allow the hacker to take advantage of this authority and mint fiat tokens to an address and allow minters to burn their own tokens. 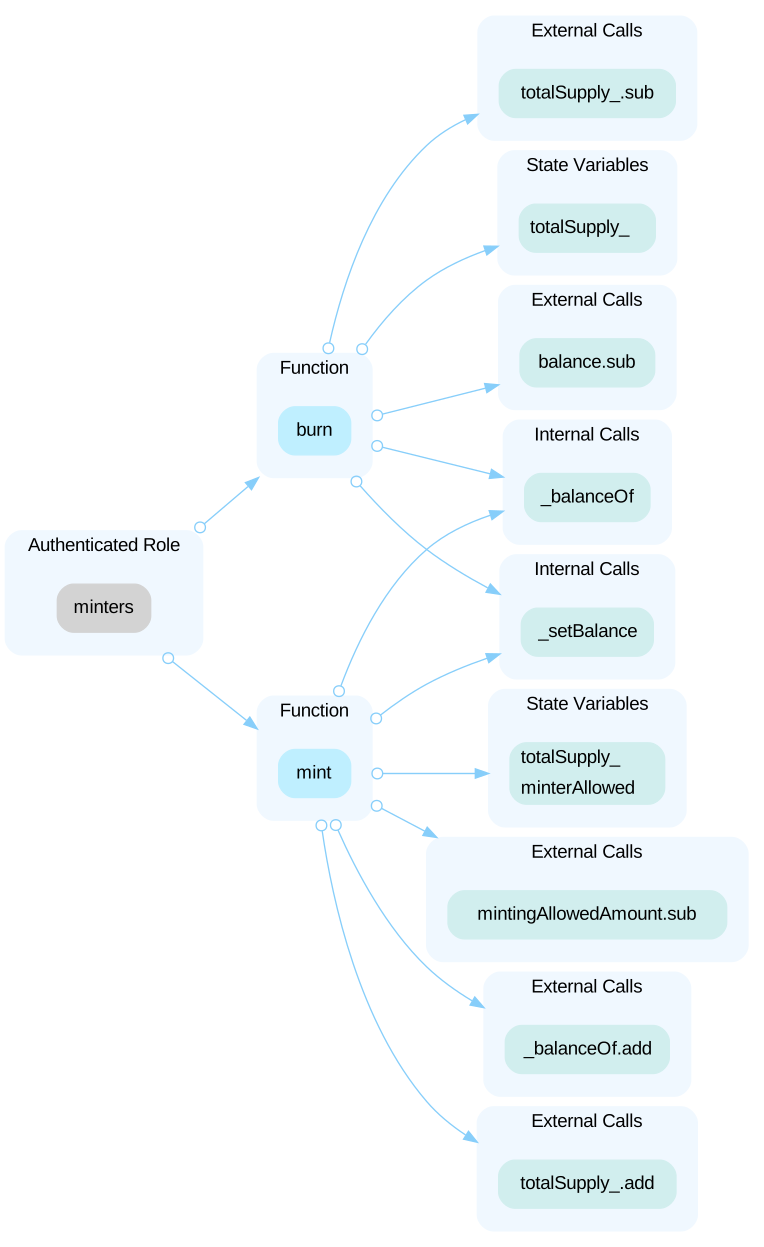 ----- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and allow the current owner to transfer control of the contract to a new owner. 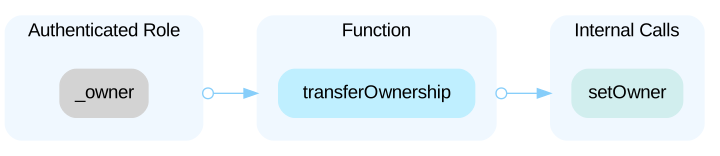 ----- In the contract `Pausable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the pauser address. 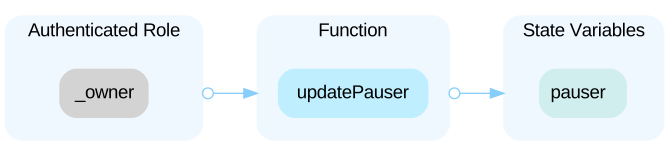 In the contract `Pausable` the role `pauser` has authority over the functions shown in the diagram below. Any compromise to the `pauser` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 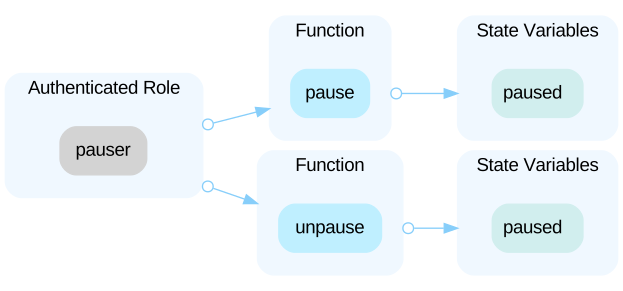
LowFunction `initialize()` Is UnprotectedOpen
The `initialize()` function is not called by another contract atomically after the contract is deployed, so it's possible for a malicious user to call `initialize()` which, if it's noticed in time, would require the project to re-deploy the contract in order to properly initialize. The functions `initializeV2()`, `initializeV2_1()` and `initializeV2_2()` have the same issue.
LowPull-Over-Push Pattern In `transferOwnership()` FOpen
The change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x72beddf7032eec58f199857b79a8e37020c14e42 | Chain: Ethereum | Source code: Verified source |
Part of MXNB’s security record
 MXNB
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us