
MXNB audit reports
MXNB has 1 public audit report from CertiK; dated 15 May 2024; no critical findings reported. It also holds 1 deployed contract on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm3
Statuses are the security firms’ own
3 findings are still open or acknowledged in the firms’ reports: 1 high, 2 low (all open).
- High
- 1
- Low
- 2
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| MXNB Audit 2024 | Security firm: CertiK | Date: | Scope: 1 address on Ethereum | None open | Findings: 1 high · 2 low 3 open | skynet.certik.com ↗ |
Findings3
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 0 |
HighCentralization Related RisksMXNB Audit 2024 · CertiK · 15 May 2024Open
In the contract `Rescuable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the rescuer address. 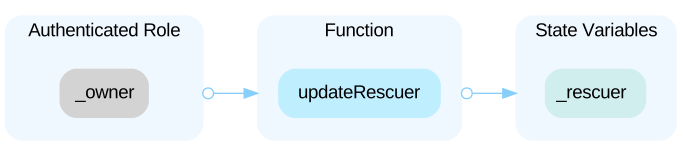 In the contract `Rescuable` the role `_rescuer` has authority over the functions shown in the diagram below. Any compromise to the `_rescuer` account may allow the hacker to take advantage of this authority and transfer tokens in this contract to any address. 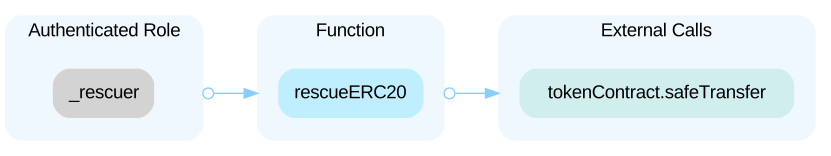 ----- In the contract `Blacklistable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the blacklister address. 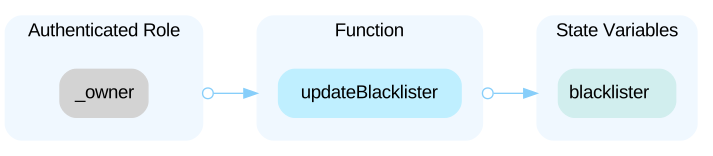 In the contract `Blacklistable` the role `blacklister` has authority over the functions shown in the diagram below. Any compromise to the `blacklister` account may allow the hacker to take advantage of this authority and add an account to the blacklist and remove the account from the blacklist. 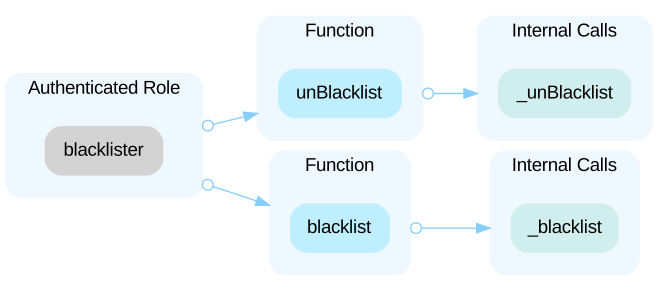 ----- In the contract `FiatTokenV1` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the master minter address. 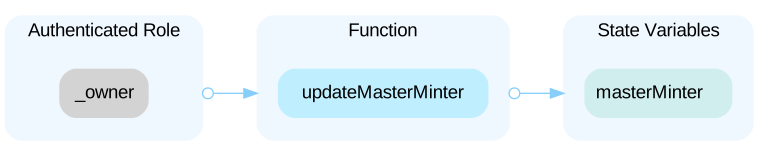 In the contract `FiatTokenV1` the role `masterMinter` has authority over the functions shown in the diagram below. Any compromise to the `masterMinter` account may allow the hacker to take advantage of this authority and add or update a new minter with a mint allowance and remove a minter. 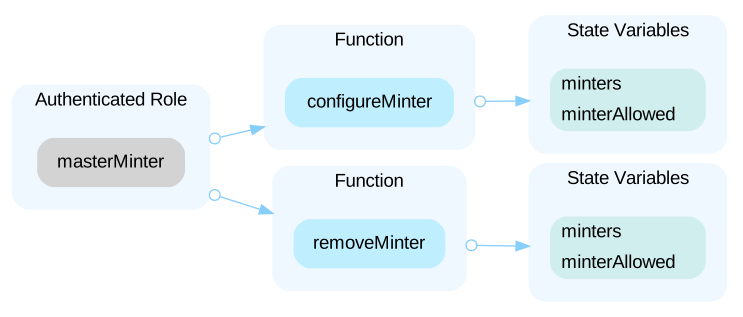 In the contract `FiatTokenV1` the role `minters` has authority over the functions shown in the diagram below. Any compromise to the `minters` account may allow the hacker to take advantage of this authority and mint fiat tokens to an address and allow minters to burn their own tokens. 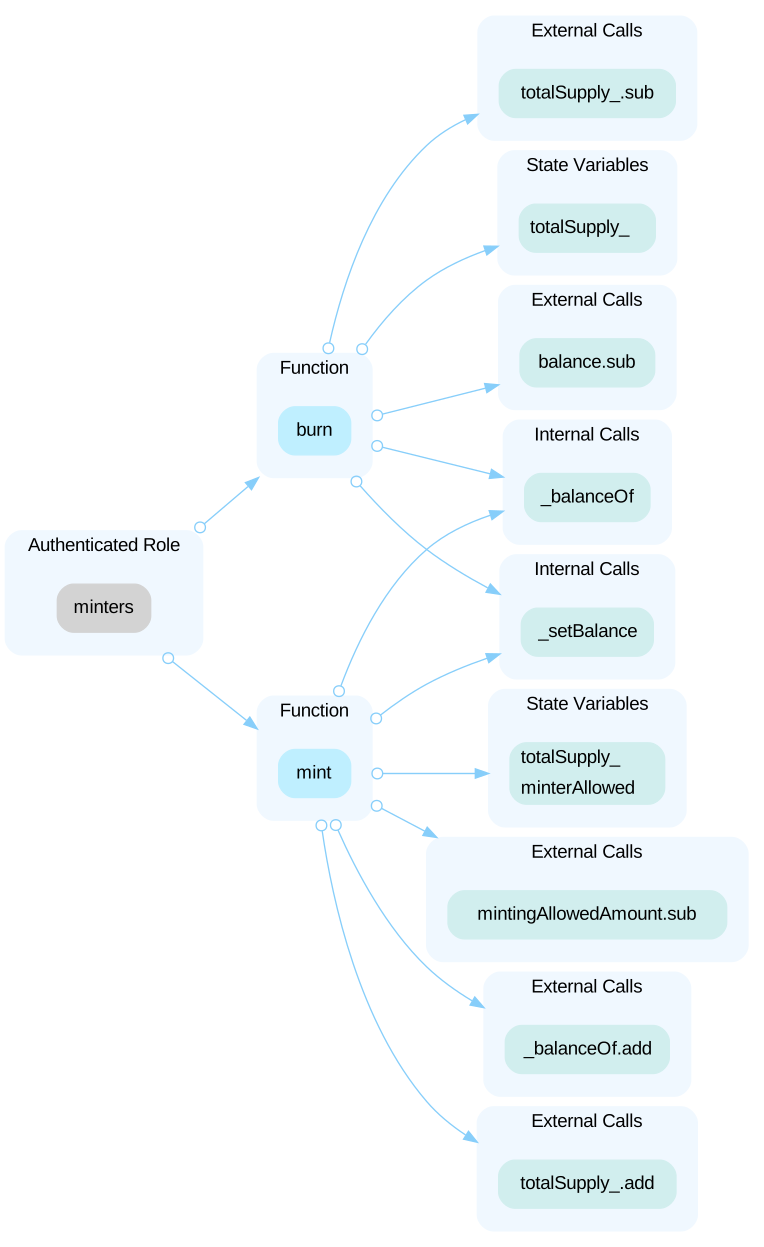 ----- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and allow the current owner to transfer control of the contract to a new owner. 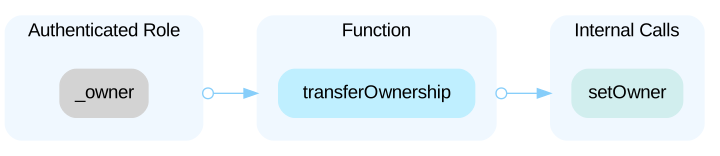 ----- In the contract `Pausable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the pauser address. 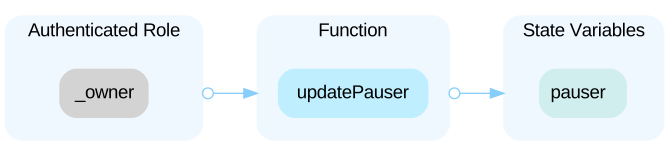 In the contract `Pausable` the role `pauser` has authority over the functions shown in the diagram below. Any compromise to the `pauser` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 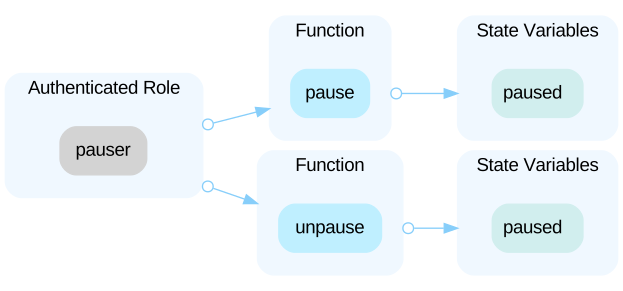
Open the reportLowFunction `initialize()` Is UnprotectedMXNB Audit 2024 · CertiK · 15 May 2024Open
The `initialize()` function is not called by another contract atomically after the contract is deployed, so it's possible for a malicious user to call `initialize()` which, if it's noticed in time, would require the project to re-deploy the contract in order to properly initialize. The functions `initializeV2()`, `initializeV2_1()` and `initializeV2_2()` have the same issue.
Open the reportLowPull-Over-Push Pattern In `transferOwnership()` FMXNB Audit 2024 · CertiK · 15 May 2024Open
The change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x72beddf7032eec58f199857b79a8e37020c14e42 | Chain: Ethereum | Source code: Verified source |
MXNB: questions
Is MXNB audited?
Trustblock holds 1 public audit report for MXNB, dated 15 May 2024. The latest is by CertiK (“MXNB Audit 2024”).
Who audited MXNB?
CertiK wrote the report Trustblock holds for MXNB.
Are there open findings in MXNB’s audits?
3 findings are still open or acknowledged in the firms’ reports: 1 high, 2 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="mxnb-token"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us