0x9a6aea7c2b0d563eab701e3255110d30f08b5a64
As of 21 Nov 2026, Trustblock’s record holds 0x9a6aea7c2b0d563eab701e3255110d30f08b5a64 on Ethereum as a contract of Metapolitans. 1 audit report on Trustblock lists this address: CertiK, 21 Jun 2023. 8 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| Metapolitans-MAPS | CertiK | Not recorded (see the report) | Open |
2 High, 6 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `BaseErc20` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 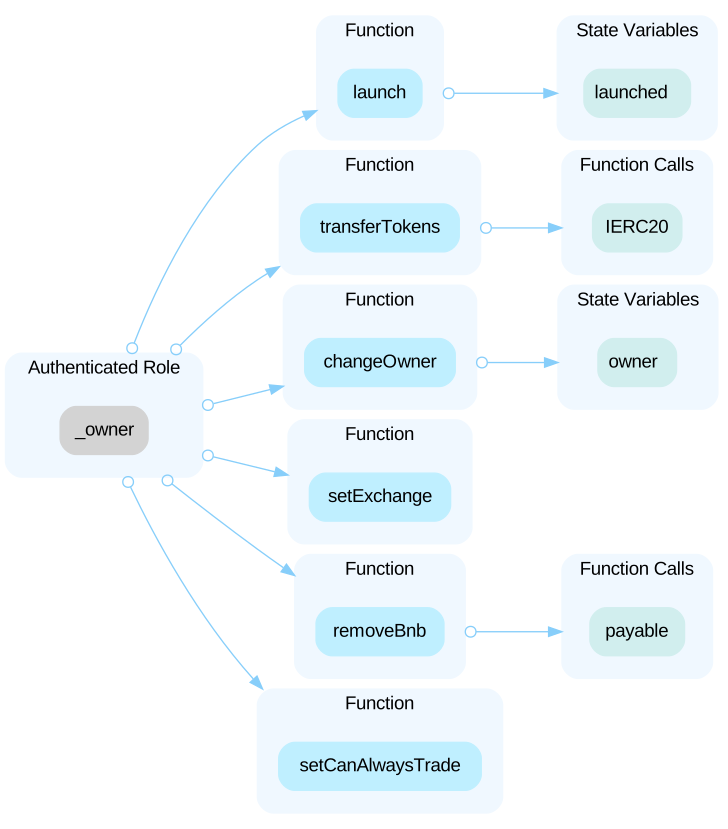 In the contract `Taxable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 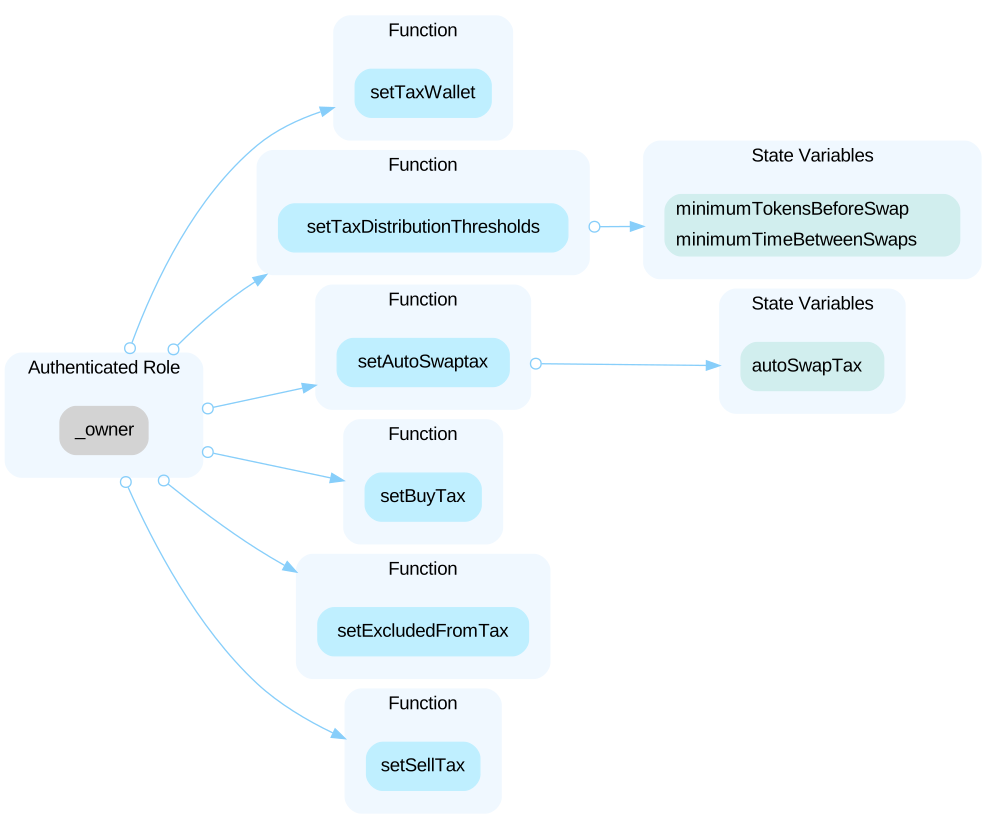 In the contract `Burnable` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority. 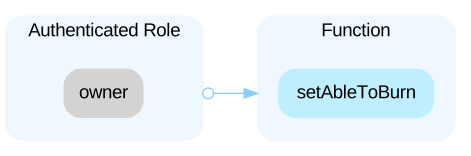 In the contract `AntiSniper` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority. 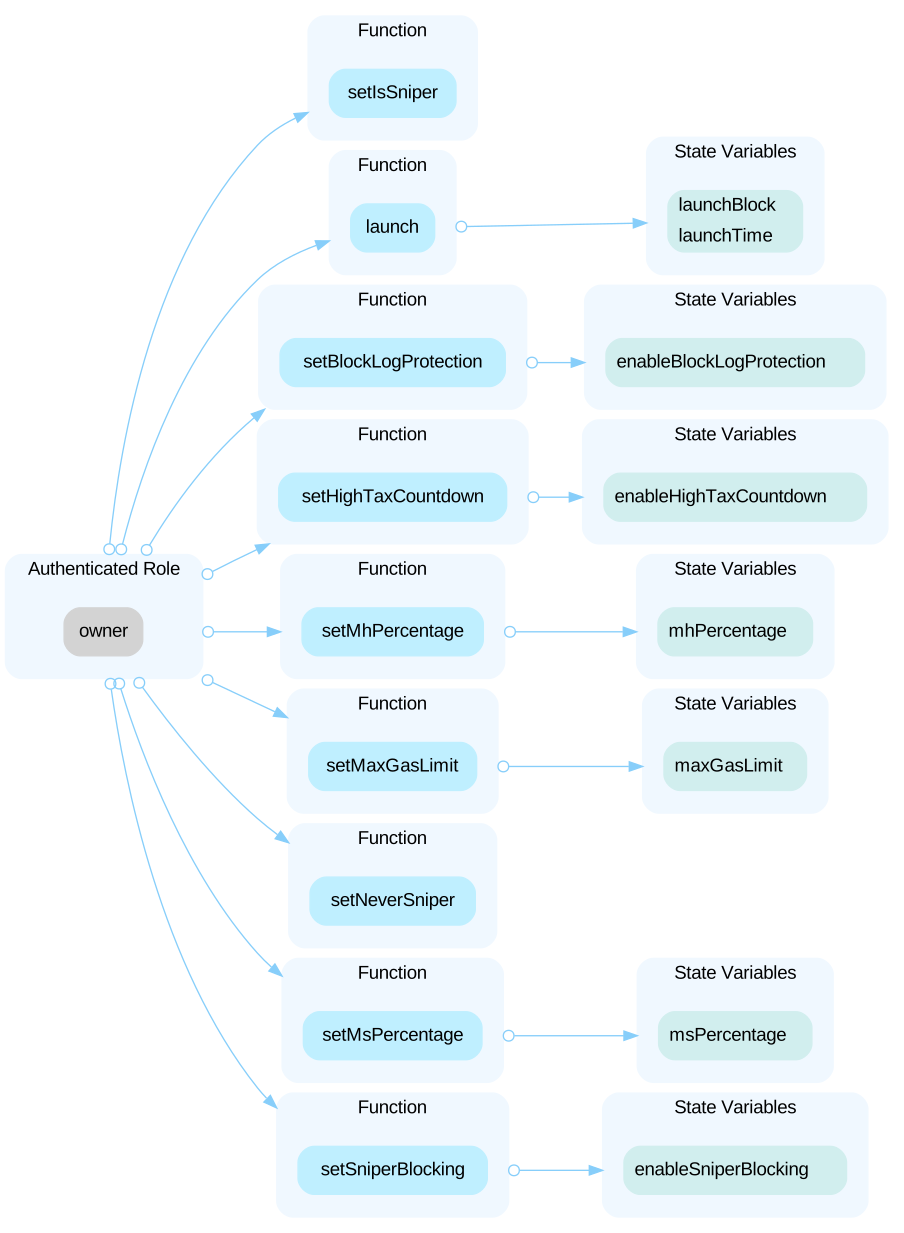 In the contract `Metapolitans` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority. 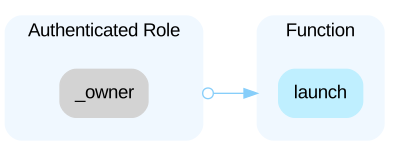 In the contract `TaxDistributor` the role `_token` has authority over the functions shown in the diagram below. Any compromise to the `_token` account may allow the hacker to take advantage of this authority. Additionally, the design of these functions indicates that the `_token` role must be either the `Taxable` or `Metapolitans` contract in order for the design to function properly. 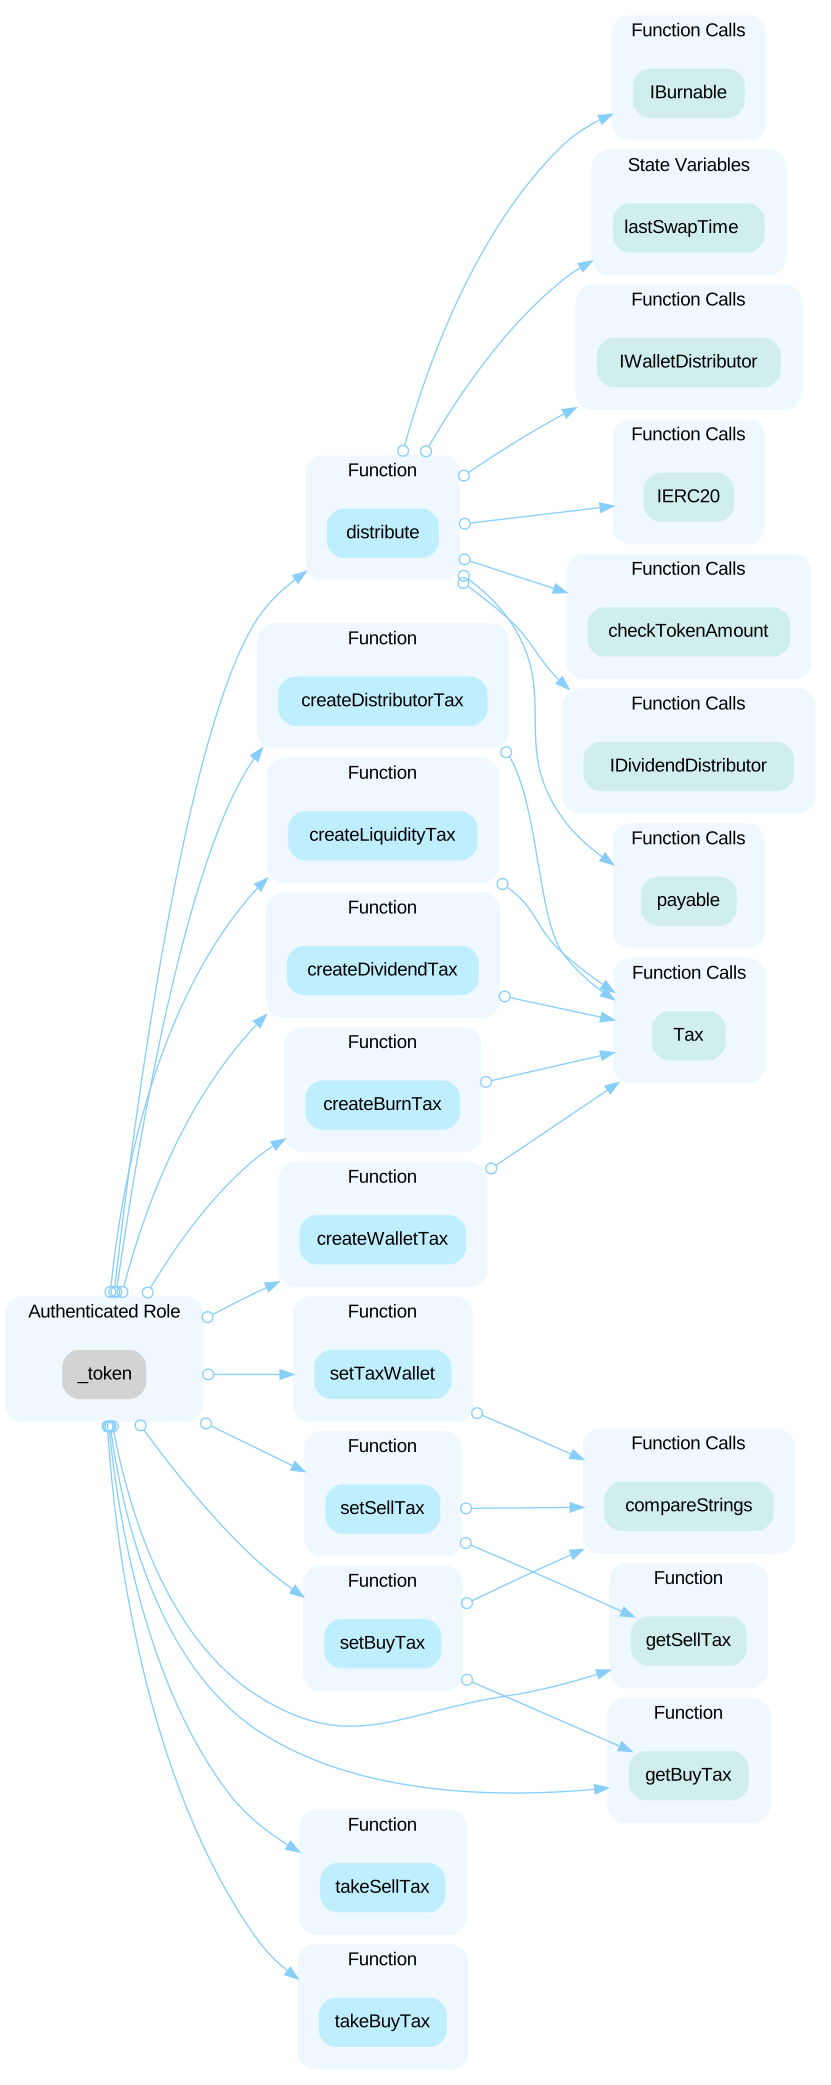
The audit on Trustblock · Open the reportAll of the **MAPS** tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe event `ConfigurationChanged` lacks a parameter to display detailed information about the update, making it impossible to record historical data through this event. For example, when setting `exchanges[who] = isExchange`, the `isExchange` could be either true or false, but the emitted event would always be `change to exchange list`.
The audit on Trustblock · Open the reportThe variables `minAmount`, `minTime`, and `taxAmount` do not have reasonable boundaries, so they can be given arbitrarily values by the `owner`.
The audit on Trustblock · Open the reportAs per the finding TDH-05, there will be a certain amount of BNBs remaining in the contract, hence the check `amountBNB == amts[1]` will always fail as it assumes that all BNBs have originated from the swap. This implies that the event will be emitted every time.
The audit on Trustblock · Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
The audit on Trustblock · Open the reportA sandwich attack may happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by back running (executing after the target) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `_router.swapExactTokensForETH()` - `_router.addLiquidityETH()`
The audit on Trustblock · Open the reportThe setting function for `_useSafeTransfer` is not available, so it will always default to zero. As a result, the subsequent code is unnecessary. ```solidity function _transfer(address from, address to, uint256 value) private { ... if (_useSafeTransfer) { _balances[from] = _balances[from] - value; _balances[to] = _balances[to] + value; emit Transfer(from, to, value); } else { ... } } ``` In addition, the function to set `excludedFromSelling[from]` is missing as well, thus the list of exclusions cannot be added.
The audit on Trustblock · Open the reportThe Metapolitans security record · Every Metapolitans address · This address on the explorer