BlackCardCoin - Audit 2
CertiK reviewed BlackCardCoin (BlackCardCoin - Audit 2) on 27 Jun 2024: 4 findings, 0 critical; 1 marked fixed, 1 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 1 |
HighCentralization Related RisksOpen
**In commit 38c0ead5c61997e022d198349cded53028875922:** In the contract `BCCoin` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause token transfers. 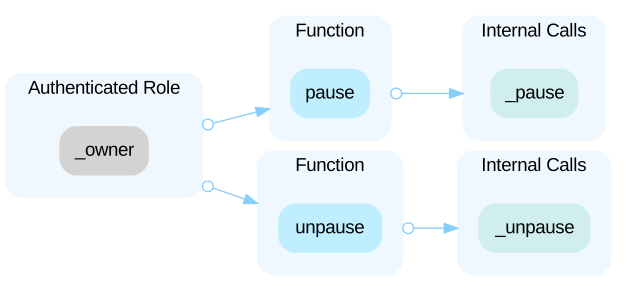 --- In the contract `Blacklist` the role `blacklistRole` has authority over the functions shown in the diagram below. Any compromise to the `blacklistRole` account may allow the hacker to take advantage of this authority and add/remove accounts from the blacklist. Accounts in the blacklist cannot transfer or receive BCCoin tokens. 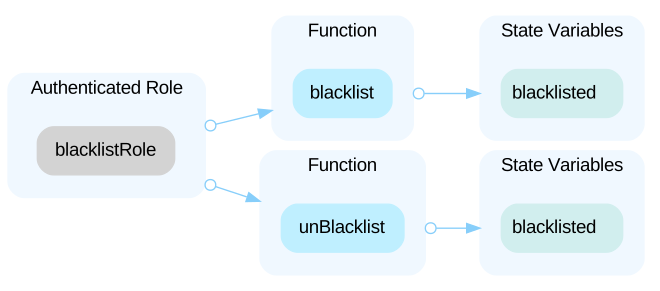 In the contract `Blacklist` the role `_owner` has authority over the function shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the `blacklistRole`. 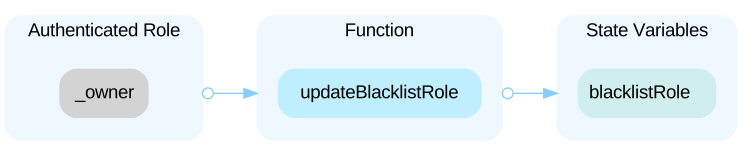 ----- In the contract `BCCoinMigration` the role `DEFAULT_ADMIN_ROLE` has authority over the function shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and transfer `newToken` out from the contract to the `withdrawAddress`. 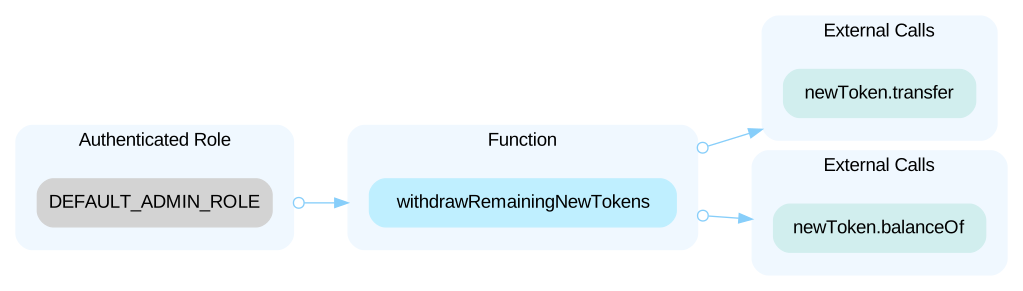 In the contract `BCCoinMigration` the role `MIGRATE_ROLE` has authority over the function shown in the diagram below. Any compromise to the `MIGRATE_ROLE` account may allow the hacker to take advantage of this authority and burn all `legacyToken` from a beneficiary and transfer the same amount of `newToken` to the beneficiary. 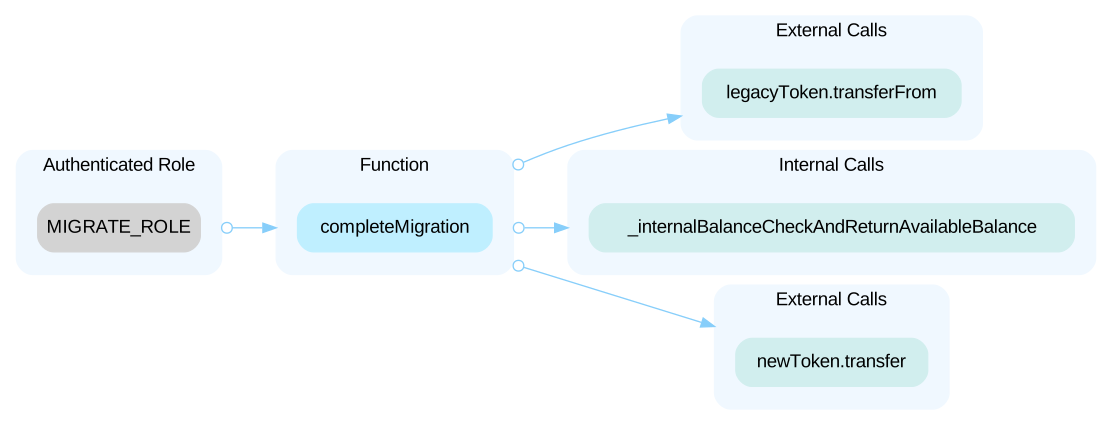 --- In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. --- In the contract `Ownable` the role `_owner` has authority over the following functions: - transferOwnership() - renounceOwnership() Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer or renounce the ownership. **In commit b0b83486a7f0a16c4047d2578841b47731e9eaec:** - The `withdrawRemainingNewTokens()` function in the `BCCoinMigration` contract was removed. - The `completeMigration()` function in the `BCCoinMigration` contract was updated, it now burns all `legacyToken` from a beneficiary and transfer the same amount of `newToken` from the `bccLiquidityAddress` to the beneficiary.
HighInitial Token DistributionOpen
All of the BCCoin tokens are sent to the `liquidityAddress` and `rewardAddress` accounts. This is a centralization risk because these accounts can distribute tokens without obtaining the consensus of the community. Any compromise to the addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of BlackCardCoin’s security record
 BlackCardCoin
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us