W3-Macondo
CertiK reviewed Macondo (W3-Macondo) on 4 Jan 2023: 23 findings, 0 critical; 11 marked fixed, 4 acknowledged, 8 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings23
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 0 | 1 | 1 |
| Low | 8 | 0 | 10 |
HighCentralization Related RisksAcknowledged
MacondoBFB --- In the contract `MacondoBFB` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint any amount of token to any address. 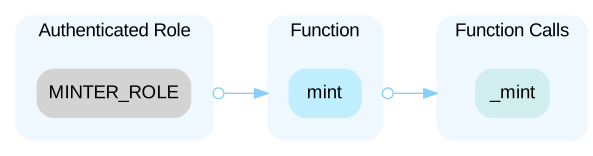 ---- In the contract `MacondoBFB` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause or unpause the contract. 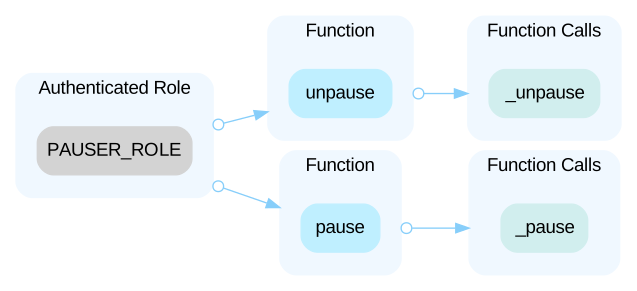 ---- In the contract `MacondoBFB` the role `UPGRADER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `UPGRADER_ROLE` account may allow the hacker to take advantage of this authority and potentially upgrade the logic implementation of the contract. 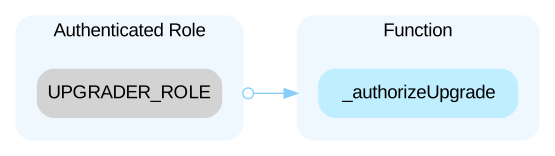 ---- ---- RandomOracleConsumer ---- In the contract `RandomOracleConsumer` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and request random words and get the random words corresponding to a specific request id. 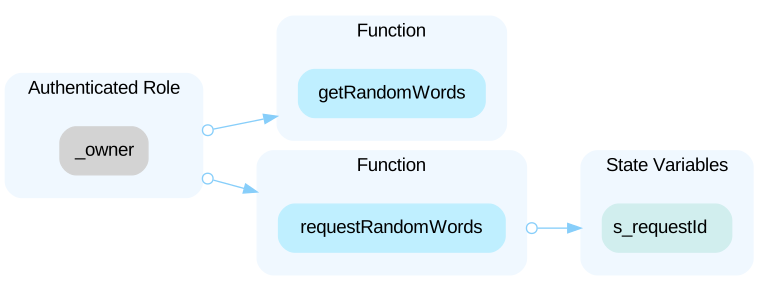 ---- ---- PokerValidator --- In the contract `PokerValidator` the role `UPGRADER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `UPGRADER_ROLE` account may allow the hacker to take advantage of this authority and potentially upgrade the implementation of the contract. 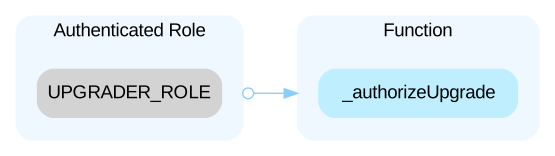 ---- ---- TokenCollection --- In the contract `TokenCollection` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause or unpause the contract. 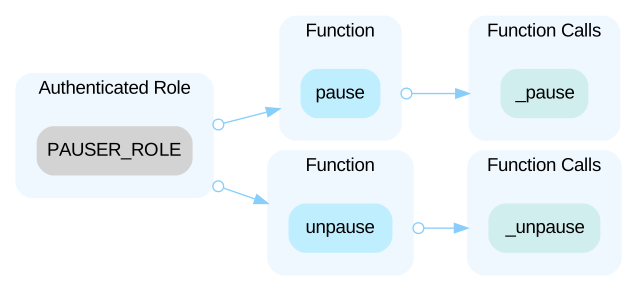 ---- In the contract `TokenCollection` the role `WITHDRAW` has authority over the functions shown in the diagram below. Any compromise to the `WITHDRAW` account may allow the hacker to take advantage of this authority and drain `BNB` from the contract. 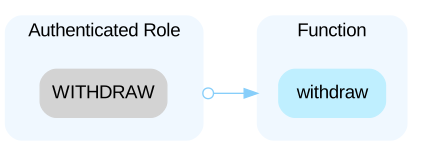 ---- In the contract `TokenCollection` the role `WITHDRAW_ERC20` has authority over the functions shown in the diagram below. Any compromise to the `WITHDRAW_ERC20` account may allow the hacker to take advantage of this authority and drain any ERC20 tokens from the contract. 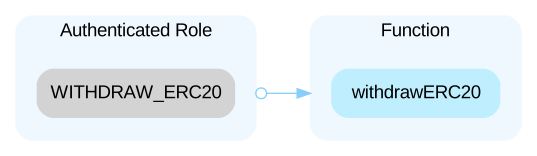 ---- In the contract `TokenCollection` the role `WITHDRAW_ERC721` has authority over the functions shown in the diagram below. Any compromise to the `WITHDRAW_ERC721` account may allow the hacker to take advantage of this authority and steal ERC721 tokens from the contract. 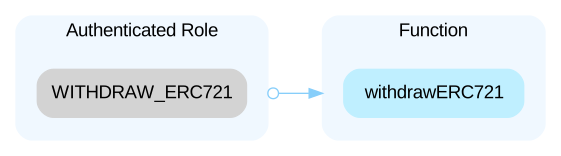 ---- ---- MacondoTableNFT ---- In the contract `MacondoTableNFT` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens to any address they want. 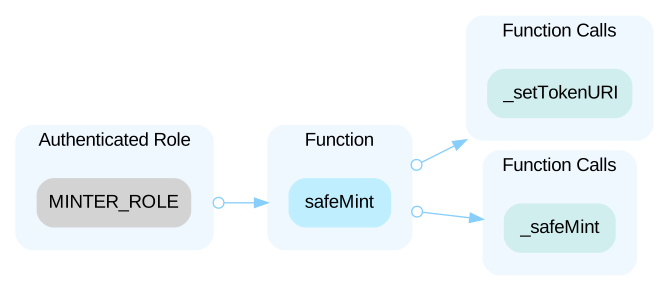 ---- In the contract `MacondoTableNFT` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority and pause or unpause the contract. 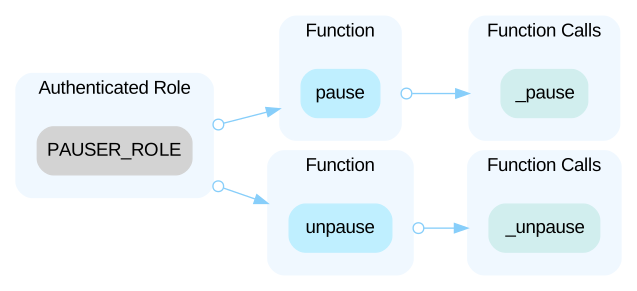 ---- In the contract `MacondoTableNFT` the role `UPGRADER_ROLE` has authority over the functions shown in the diagram
HighCentralized Control of Contract UpgradeAcknowledged
The linked contracts are upgradeable contracts, a privileged role can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
HighInitial Token DistributionAcknowledged
All `MacondoMCD` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `MCD` tokens without the consensus of the community.
MediumLack of Storage Gap in Upgradeable ContractAcknowledged
There is no storage gap preserved in the logic contract. Any logic contract that acts as a base contract that needs to be inherited by other upgradeable child should have a reasonable size of storage gap preserved for the new state variable introduced by the future upgrades.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (11)
- contracts/token/nft-table/MacondoTableNFTMinterBlindBox.sol
- contracts/core/utils/random/OnChainRandomUpgradeable.sol
- contracts/token/token-MCD/MacondoMCD.sol
- contracts/game/poker/PokerValidator.sol
- contracts/core/nft-store/NFTStoreSellerIncrease.sol
- contracts/core/nft-store/NFTStore.sol
- contracts/token/token-MCD/MacondoMCDVestingEcosystemWallet.sol
- contracts/token/token-BFB/MacondoBFB.sol
- contracts/token/nft-table/MacondoTableNFT.sol
- contracts/random/RandomOracleConsumer.sol
- contracts/TokenCollection.sol
Part of Macondo’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us