Wemix Retainer 74 (DIOSV3)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 74 (DIOSV3)) on 16 Aug 2024: 10 findings, 0 critical; 4 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 1 | 0 | 1 |
| Low | 3 | 0 | 3 |
HighCentralization Related RisksOpen
In the contract `DollarInAndOutStabilizer3` the role `operator` has authority over the functions shown in the diagram below. Any compromise to the `operator` account may allow the hacker to take advantage of this authority and trigger the `WEMIX$` price stabilizing functions `syncToBaseTick` and `syncToRandomTick`. 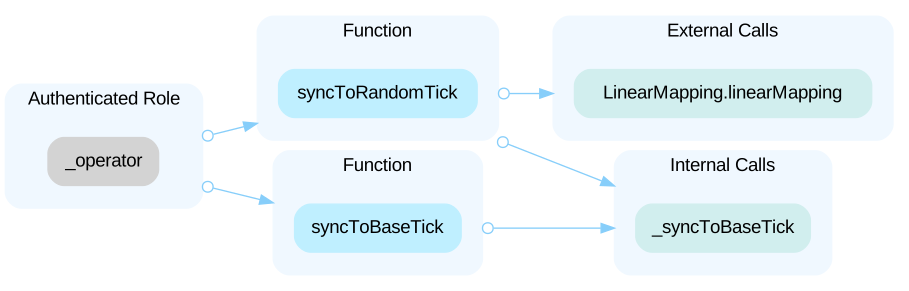 In the contract `OperatorManagement` the role `operatorManager` has authority over the functions shown in the diagram below. Any compromise to the `operatorManager` account may allow the hacker to take advantage of this authority and add/remove the operator role. 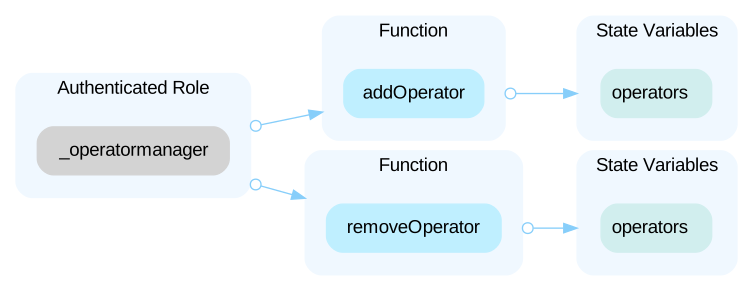 In the contract `DollarInAndOutStabilizer3` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the rewarder address or the tick threshold value. 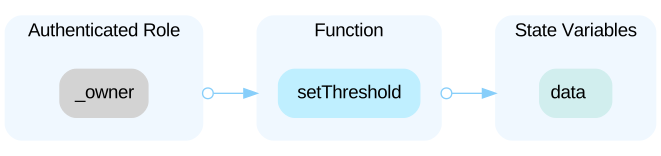 In the contract `OperatorManagement` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set an arbitrary account as the `operatorManager` role. 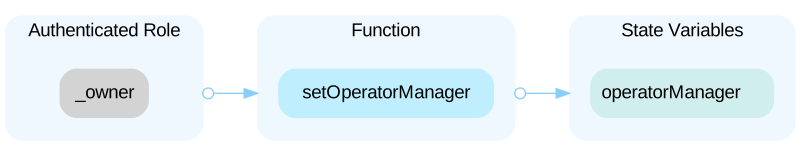
HighCentralized Control of Contract UpgradeOpen
`OperatorManagement` and `DollarInAndOutStabilizer3` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the proxy admin account, he can change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
MediumPotential MEV Sandwich Attacks due to Missing SliOpen
A sandwich attack may happen when an attacker observes a transaction swapping tokens without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by backrunning (executing after the target) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: ```solidity=241 function _executeSwap( address tokenIn, address tokenOut, uint256 amountIn ) internal returns (uint256 amountOut) { bool zeroForOne = tokenIn < tokenOut; (int256 amount0, int256 amount1) = pair.swap( address(this), zeroForOne, amountIn.toInt256(), zeroForOne ? TickMath.MIN_SQRT_RATIO + 1 : TickMath.MAX_SQRT_RATIO - 1, abi.encodePacked(tokenIn) ); return uint256(-(zeroForOne ? amount1 : amount0)); } ```
LowFunction `initialize()` Is UnprotectedOpen
One or more logic contracts do not protect their initializers. An attacker can call the initializer and assume ownership of the logic contract, whereby he can perform privileged operations that trick unsuspecting users into believing that he is the owner of the upgradeable contract. ```solidity=20 contract DollarInAndOutStabilizer3 is OperatorManagement, IDollarInAndOutStabilizer3 ``` - `DollarInAndOutStabilizer3` is an upgradeable contract that does not protect its initializer. ```solidity=63 function initialize( IWeswapV3Pool _pair, ISwapRouter _swapRouter, IWeswapRouter _weswapRouter, IAMA _ama, address _rewarder, uint160 _baseSqrtPriceX96 ) external initializer { ``` - `initialize` is an unprotected initializer function.
LowModifier `Onlyinitializing` should be used for InOpen
For upgradeable contracts, it is recommended to use `onlyInitializing` to protect initialization functions in parent contracts so that they can only be invoked by functions with the `initializer` and `reinitializer` modifiers. Reference: https://docs.openzeppelin.com/contracts/4.x/api/proxy#Initializable-onlyInitializing--
LowSafeMath Not UsedOpen
`SafeMath` library is not used in the linked contract, making it possible for overflow/underflow to occur and lead to inaccurate calculations. ```solidity=144 data.minSqrtPriceX96 = (data.baseSqrtPriceX96 * 99993) / 100000; data.maxSqrtPriceX96 = (data.baseSqrtPriceX96 * 100007) / 100000; ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/DollarInAndOutStabilizer3.sol
- contracts/extentions/OperatorManagement.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us