BabyCate - Audit
CertiK reviewed BabyCate (BabyCate - Audit) on 8 Oct 2024: 9 findings, 0 critical; 4 marked fixed, 5 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 1 |
| Medium | 0 | 1 | 0 |
| Low | 0 | 3 | 3 |
HighCentralization Risks in BabyCate.solFixed
In the contract `BabyCate`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and exclude or include accounts from fees, set automated market maker pair status, update the transfer fees, retrieve stuck tokens, set the swap tokens amount, toggle swap back status, update the sell fees, update the buy fees, and set the marketing wallet. 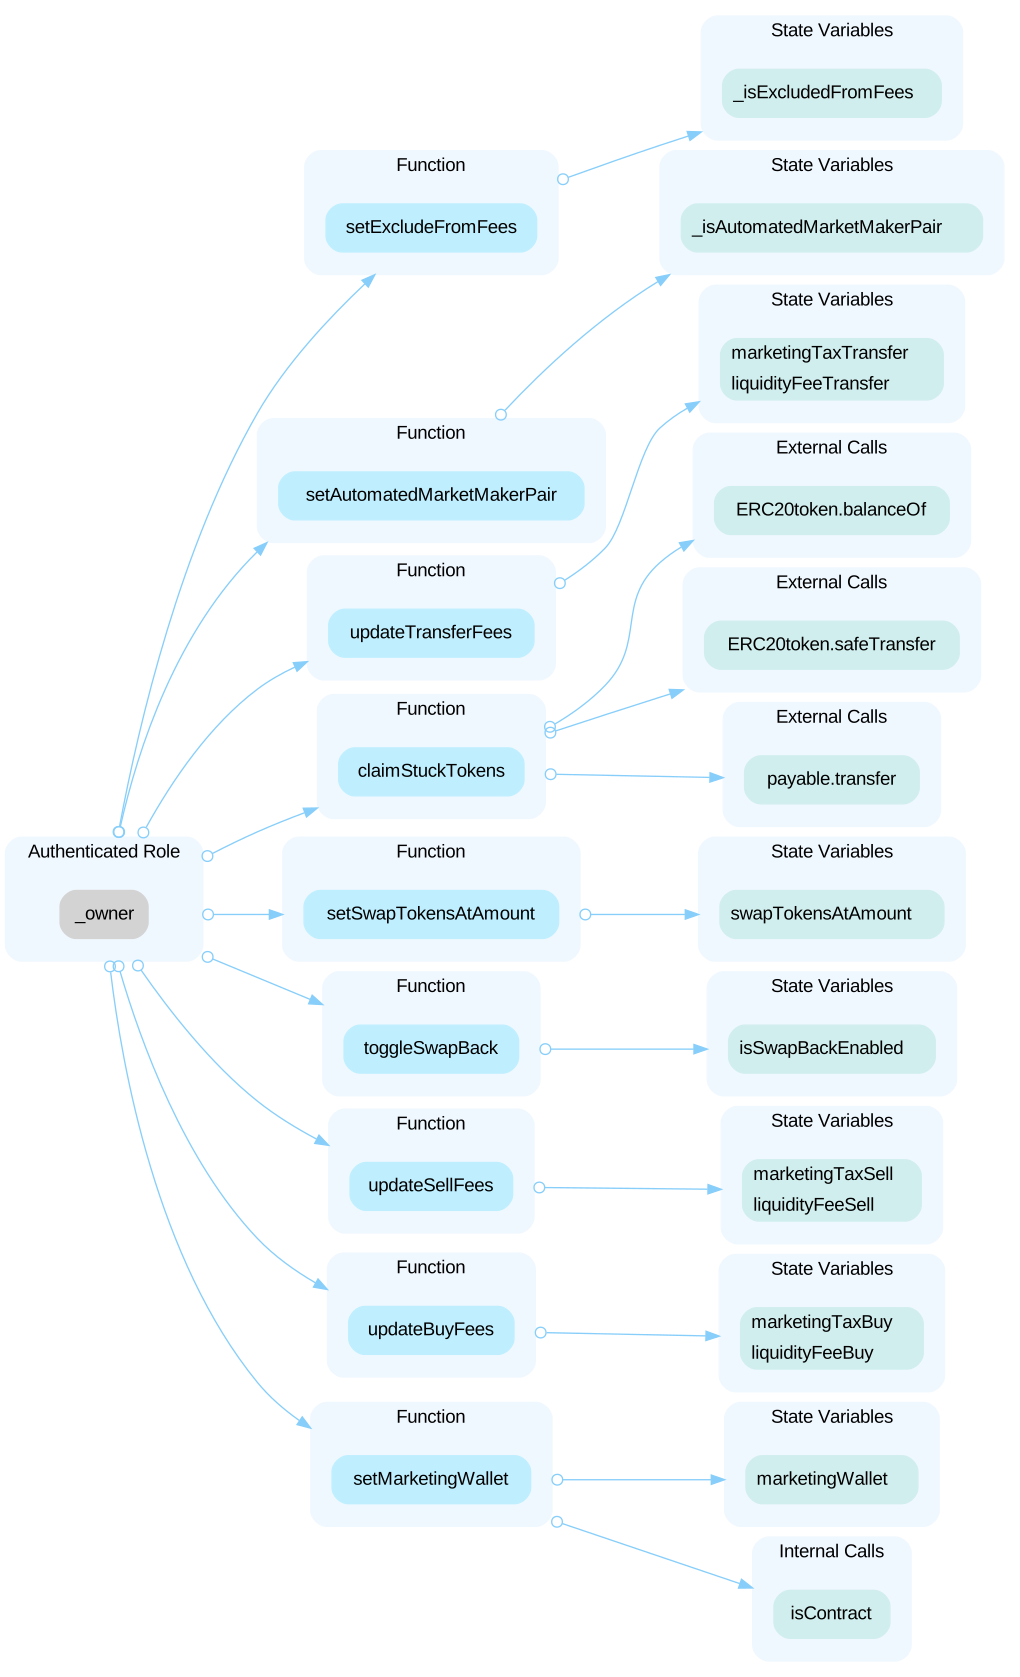 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership, renounce contract ownership. 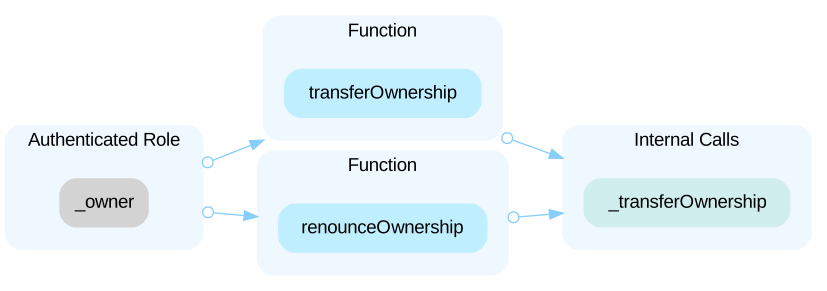
LowIneffective `isContract` CheckFixed
The `isContract` check cannot cover all scenarios. The check can be bypassed if the call is from the constructor of a contract or when the contract is destroyed. In that case, `isContract` will return `false` because its `codesize` will be zero. The comment in the `isContract` implementation from the OpenZeppelin library also says that "item_output is unsafe to assume that an address for which this function returns false is an externally-owned account (EOA), and not a contract." - Reference: https://github.com/OpenZeppelin/openzeppelin-contracts/blob/3dac7bbed7b4c0dbf504180c33e8ed8e350b93eb/contracts/utils/Address.sol ```solidity=1133 require( !isContract(_marketingWallet), "Marketing wallet cannot be a contract" ); ```
LowPull-Over-Push Pattern In `transferOwnership()` FFixed
The change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` is able to actuate transactions on-chain.
LowUsage of `transfer()` for sending EtherFixed
It is not recommended to use Solidity's `transfer()` and `send()` functions for transferring native tokens, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=1116 payable(msg.sender).transfer(address(this).balance); ``` - `BabyCate.claimStuckTokens` uses `transfer()`.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x76b560b628f74bf192be09f0449abef8e456be79 | Chain: BNB Chain | Source code: Verified source |
Part of BabyCate’s security record
 BabyCate
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us