Darkpool - private sale
CertiK reviewed Brightpool (Darkpool - private sale) on 22 Jun 2023: 48 findings, 3 critical; 46 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings48
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 1 | 0 | 1 |
| Medium | 1 | 0 | 8 |
| Low | 0 | 0 | 34 |
HighCentralization Related RisksOpen
The following represents the current state of the protocol as of the final commit referenced by this audit. Any changes made because of the audit are included to best convey the current status of the protocol. Please also see the alleviations section for multi-sig information as well. ### BRI.sol In the contract `BRI` the role `_adminorowner` has authority over the functions shown in the diagram below. Any compromise to the `_adminorowner` account may allow the hacker to take advantage of this authority and change the `oracle` address which has the privileged functions outlined below. It should be noted that this has also uses the `BrightPoolWarden` subjecting this change to a 24 hour time-lock and requiring both the `admin` and `owner` to execute this function. 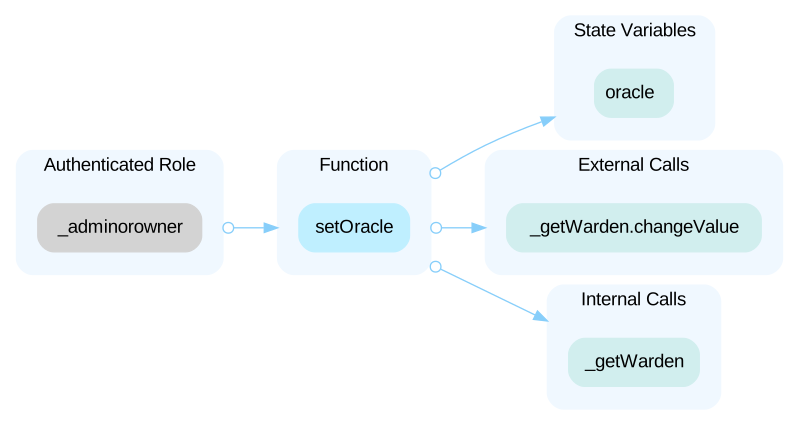 In the contract `BRI` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and call `killTransfers()` which can prevent transfers for up to 24 hours. 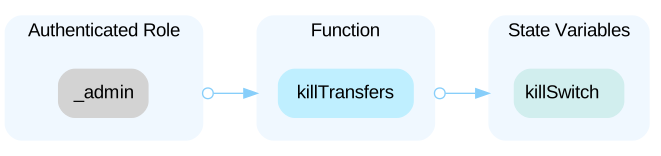 In the contract `BRI` the role `_ledger` has authority over the functions shown in the diagram below. Any compromise to the `_ledger` account may allow the hacker to take advantage of this authority and mint or burn `BRI` for any address. 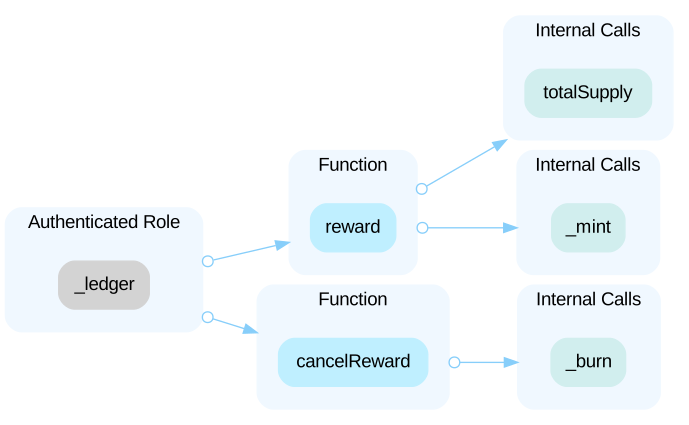 In the contract `BRI` the role `_oracle` has authority over the functions shown in the diagram below. Any compromise to the `_oracle` account may allow the hacker to take advantage of this authority and mint or burn `BRI` for any address. 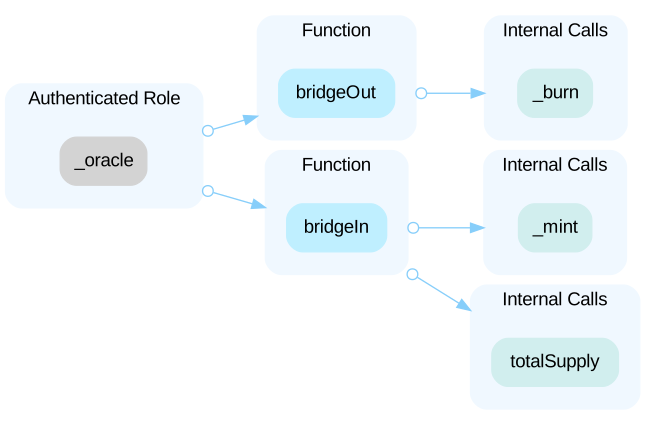 --- ### BRINFT.sol In the contract `BRINFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - set the sale contract, which can do the following priviledged actions below. However, the function can only be called once; - mint tokens to any address, but this can only be called once; 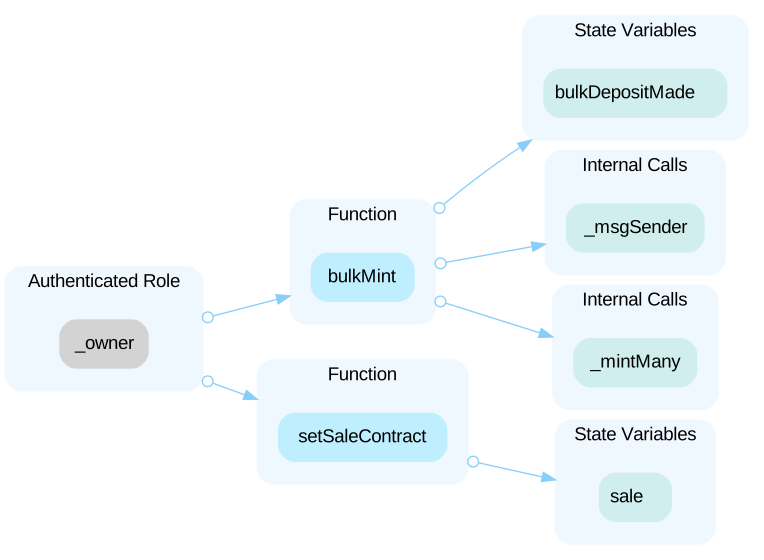 In the contract `BRINFT` the role `_adminorowner` has authority over the functions shown in the diagram below. Any compromise to the `_admin` or `_owner` account may allow the hacker to take advantage of this authority and change the price and token URI for a given tokenID, however, this function can only be called once. 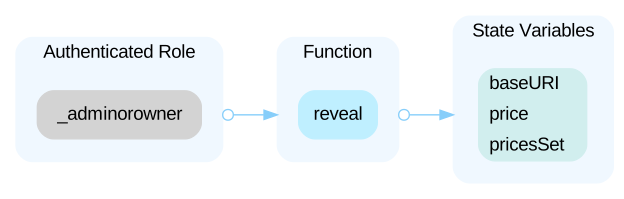 In the contract `BRINFT` the role `_salecontract` has authority over the functions shown in the diagram below. Any compromise to the `_salecontract` account may allow the hacker to take advantage of this authority and burn or mint tokens. 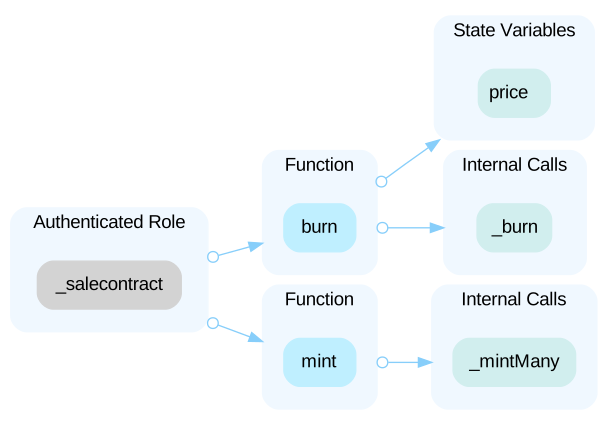 --- ### IBrightPoolLedger In the contract `IBrightPoolLedger` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the manager contract through the `BrightPoolWarden` giving it access to the privileges outlined in `BrightPoolLedger`. As it goes through the `BrightPoolWarden` this is subject to a 24 hour time-lock. This contract is inherited by `BrightPoolLedger`. 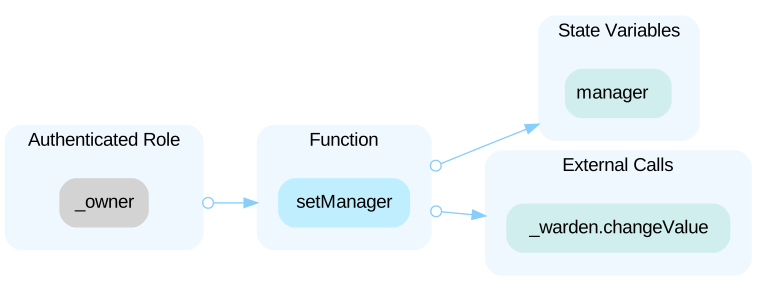 --- ### BrightPoolLedger.sol In the contract `BrightPoolLedger` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - add a malicious exchange, however this is executed via `BrightPoolWarder` and thus is subjected to a 24 hour time-lock; - remove an exchange, which can be used to ensure a certain exchange is used whose price could be manipulated. 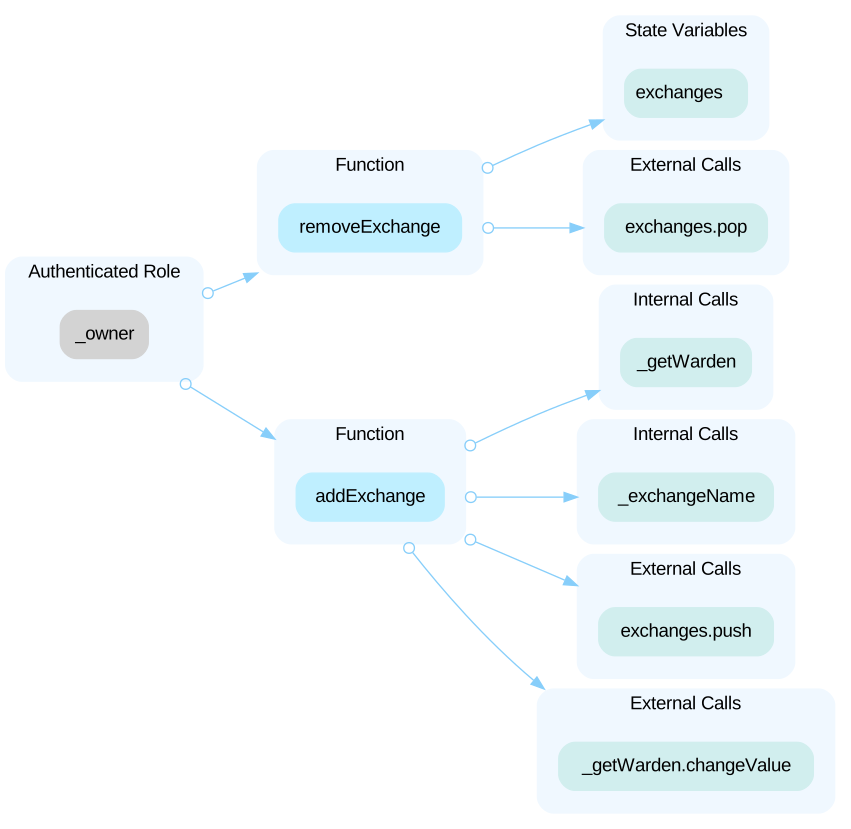 In the contract `BrightPoolLedger` the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to
MediumInitial Token DistributionOpen
All `Bri` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `Bri` tokens without the consensus of the community.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (13)
- src/BrightPoolTreasury.sol
- src/NFTSale.sol
- src/UniswapExchange.sol
- src/VestedSale.sol
- src/BRINFT.sol
- src/BrightPoolManager.sol
- src/IBrightPoolConsumer.sol
- src/IBrightPoolExchangeable.sol
- src/IBrightPoolExchange.sol
- src/BrightPoolLedger.sol
- src/Sale.sol
- src/VestingToken.sol
- src/BRI.sol
Part of Brightpool’s security record
 Brightpool
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us