
Brightpool audit reports
Brightpool has 2 public audit reports from Zokyo and CertiK; the latest is Zokyo, 9 Feb 2024; 3 critical findings, all marked fixed by the firms.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm2
Statuses are the security firms’ own
2 findings are still open or acknowledged in the firms’ reports: 1 high, 1 medium (all open).
- High
- 1
- Medium
- 1
Audits2
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Brightpool Finance Smart Contracts Review | Security firm: Zokyo | Date: | Scope: Files listed | None open | Findings: 1 high · 1 low 2 fixed | IPFS ↗ |
| Darkpool - private sale | Security firm: CertiK | Date: | Scope: Files listed | 3 critical findings, fixed | Findings: 3 critical · 2 high · 9 medium · 34 low 46 fixed · 2 open | skynet.certik.com ↗ |
Findings51
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 1 | 0 | 2 |
| Medium | 1 | 0 | 8 |
| Low | 0 | 0 | 35 |
HighCentralization Related RisksDarkpool - private sale · CertiK · 22 Jun 2023Open
The following represents the current state of the protocol as of the final commit referenced by this audit. Any changes made because of the audit are included to best convey the current status of the protocol. Please also see the alleviations section for multi-sig information as well. ### BRI.sol In the contract `BRI` the role `_adminorowner` has authority over the functions shown in the diagram below. Any compromise to the `_adminorowner` account may allow the hacker to take advantage of this authority and change the `oracle` address which has the privileged functions outlined below. It should be noted that this has also uses the `BrightPoolWarden` subjecting this change to a 24 hour time-lock and requiring both the `admin` and `owner` to execute this function. 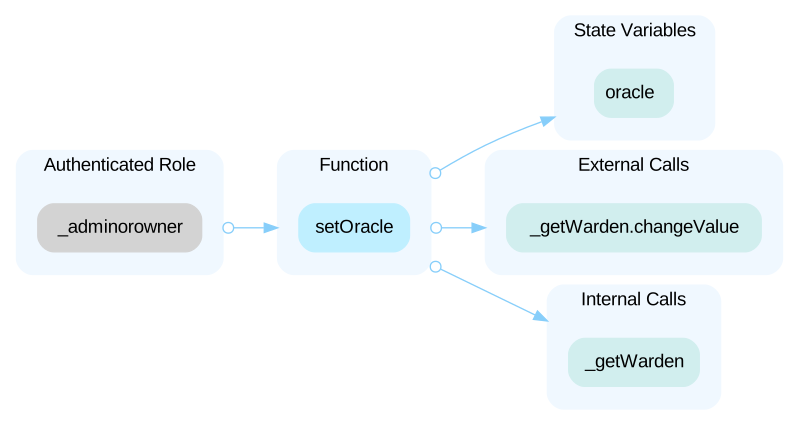 In the contract `BRI` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and call `killTransfers()` which can prevent transfers for up to 24 hours. 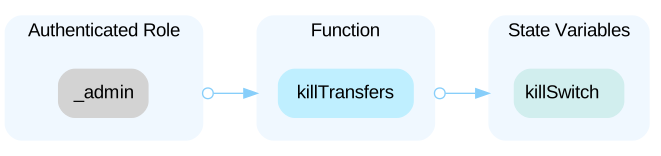 In the contract `BRI` the role `_ledger` has authority over the functions shown in the diagram below. Any compromise to the `_ledger` account may allow the hacker to take advantage of this authority and mint or burn `BRI` for any address. 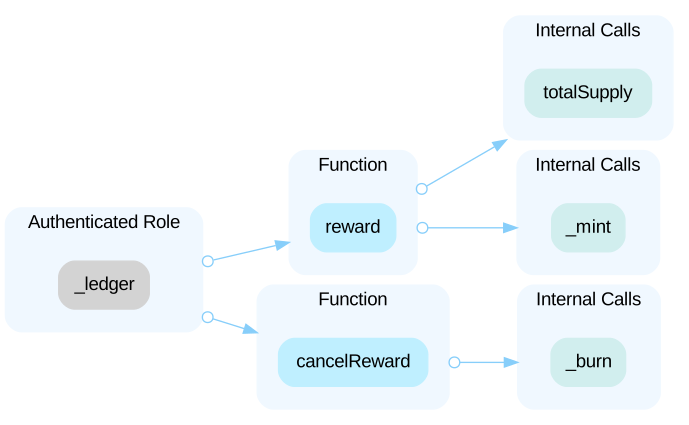 In the contract `BRI` the role `_oracle` has authority over the functions shown in the diagram below. Any compromise to the `_oracle` account may allow the hacker to take advantage of this authority and mint or burn `BRI` for any address. 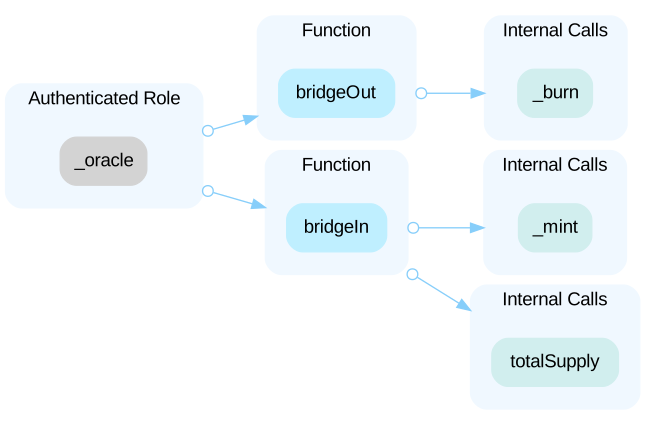 --- ### BRINFT.sol In the contract `BRINFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - set the sale contract, which can do the following priviledged actions below. However, the function can only be called once; - mint tokens to any address, but this can only be called once; 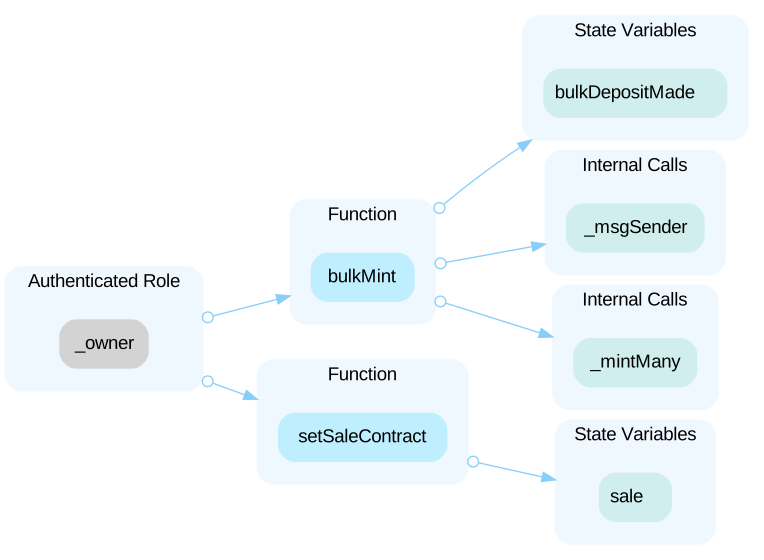 In the contract `BRINFT` the role `_adminorowner` has authority over the functions shown in the diagram below. Any compromise to the `_admin` or `_owner` account may allow the hacker to take advantage of this authority and change the price and token URI for a given tokenID, however, this function can only be called once. 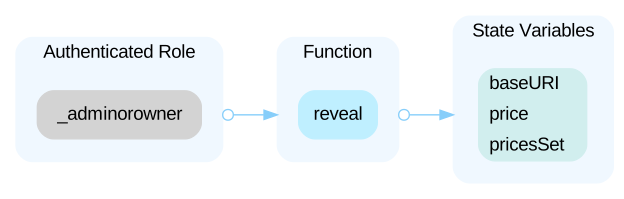 In the contract `BRINFT` the role `_salecontract` has authority over the functions shown in the diagram below. Any compromise to the `_salecontract` account may allow the hacker to take advantage of this authority and burn or mint tokens. 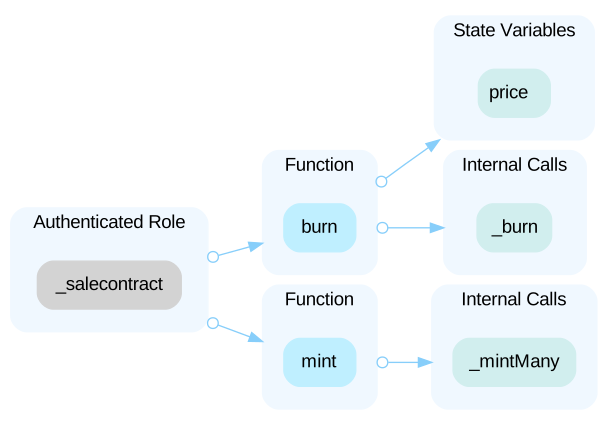 --- ### IBrightPoolLedger In the contract `IBrightPoolLedger` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the manager contract through the `BrightPoolWarden` giving it access to the privileges outlined in `BrightPoolLedger`. As it goes through the `BrightPoolWarden` this is subject to a 24 hour time-lock. This contract is inherited by `BrightPoolLedger`. 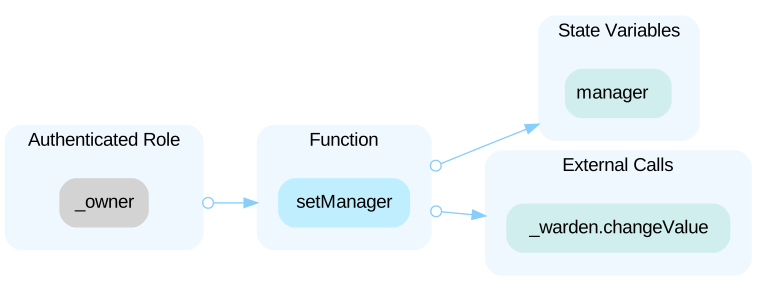 --- ### BrightPoolLedger.sol In the contract `BrightPoolLedger` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - add a malicious exchange, however this is executed via `BrightPoolWarder` and thus is subjected to a 24 hour time-lock; - remove an exchange, which can be used to ensure a certain exchange is used whose price could be manipulated. 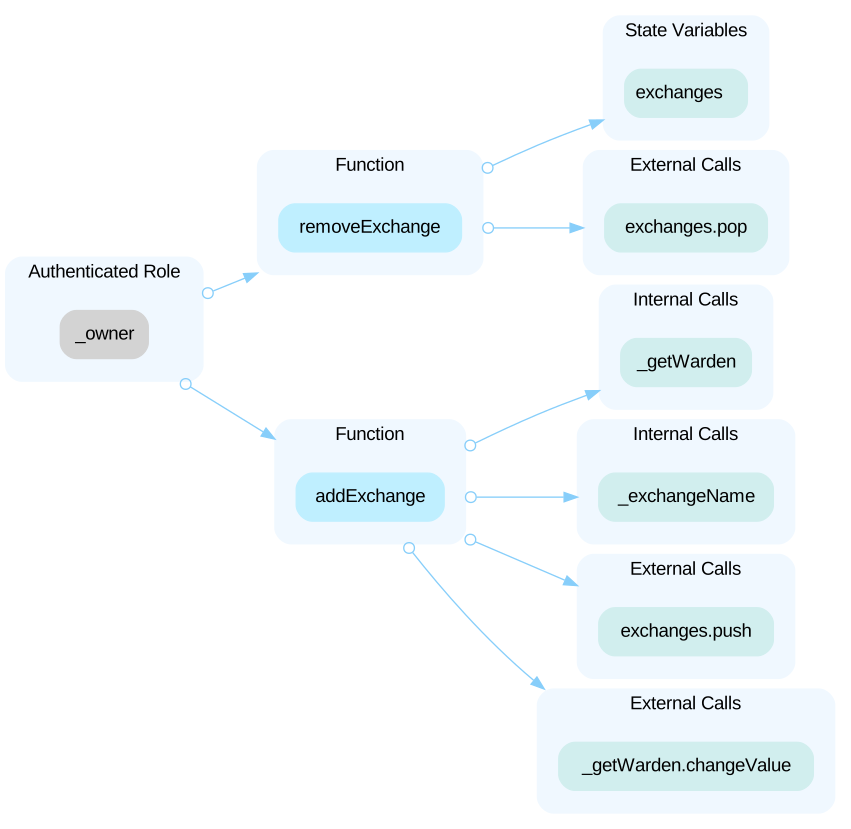 In the contract `BrightPoolLedger` the role `_manager` has authority over the functions shown in the diagram below. Any compromise to the `_manager` account may allow the hacker to
Open the reportMediumInitial Token DistributionDarkpool - private sale · CertiK · 22 Jun 2023Open
All `Bri` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `Bri` tokens without the consensus of the community.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Brightpool: questions
Is Brightpool audited?
Trustblock holds 2 public audit reports for Brightpool, dated 22 Jun 2023 to 9 Feb 2024. The latest is by Zokyo (“Brightpool Finance Smart Contracts Review”).
Who audited Brightpool?
2 security firms wrote the reports Trustblock holds for Brightpool: Zokyo and CertiK.
Are there open findings in Brightpool’s audits?
2 findings are still open or acknowledged in the firms’ reports: 1 high, 1 medium (all open). Of 3 critical findings: all marked fixed by the firms. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="brightpool-finance"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us