Seedify finance Locked-Yield-Farming
CertiK reviewed Seedify (Seedify finance Locked-Yield-Farming) on 13 Nov 2023: 9 findings, 0 critical; 6 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 6 |
HighCentralization Risks in LockedFarming.solOpen
In the contract `SMD_v5` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set rewards periods, extend the current period, pause/unpause functions, and withdraw excess tokens mistakenly sent to the contract. Notably, the hacker can prevent users from withdrawing staked tokens by updating `lockDuration` to a large value via `setNewPeriod()`. 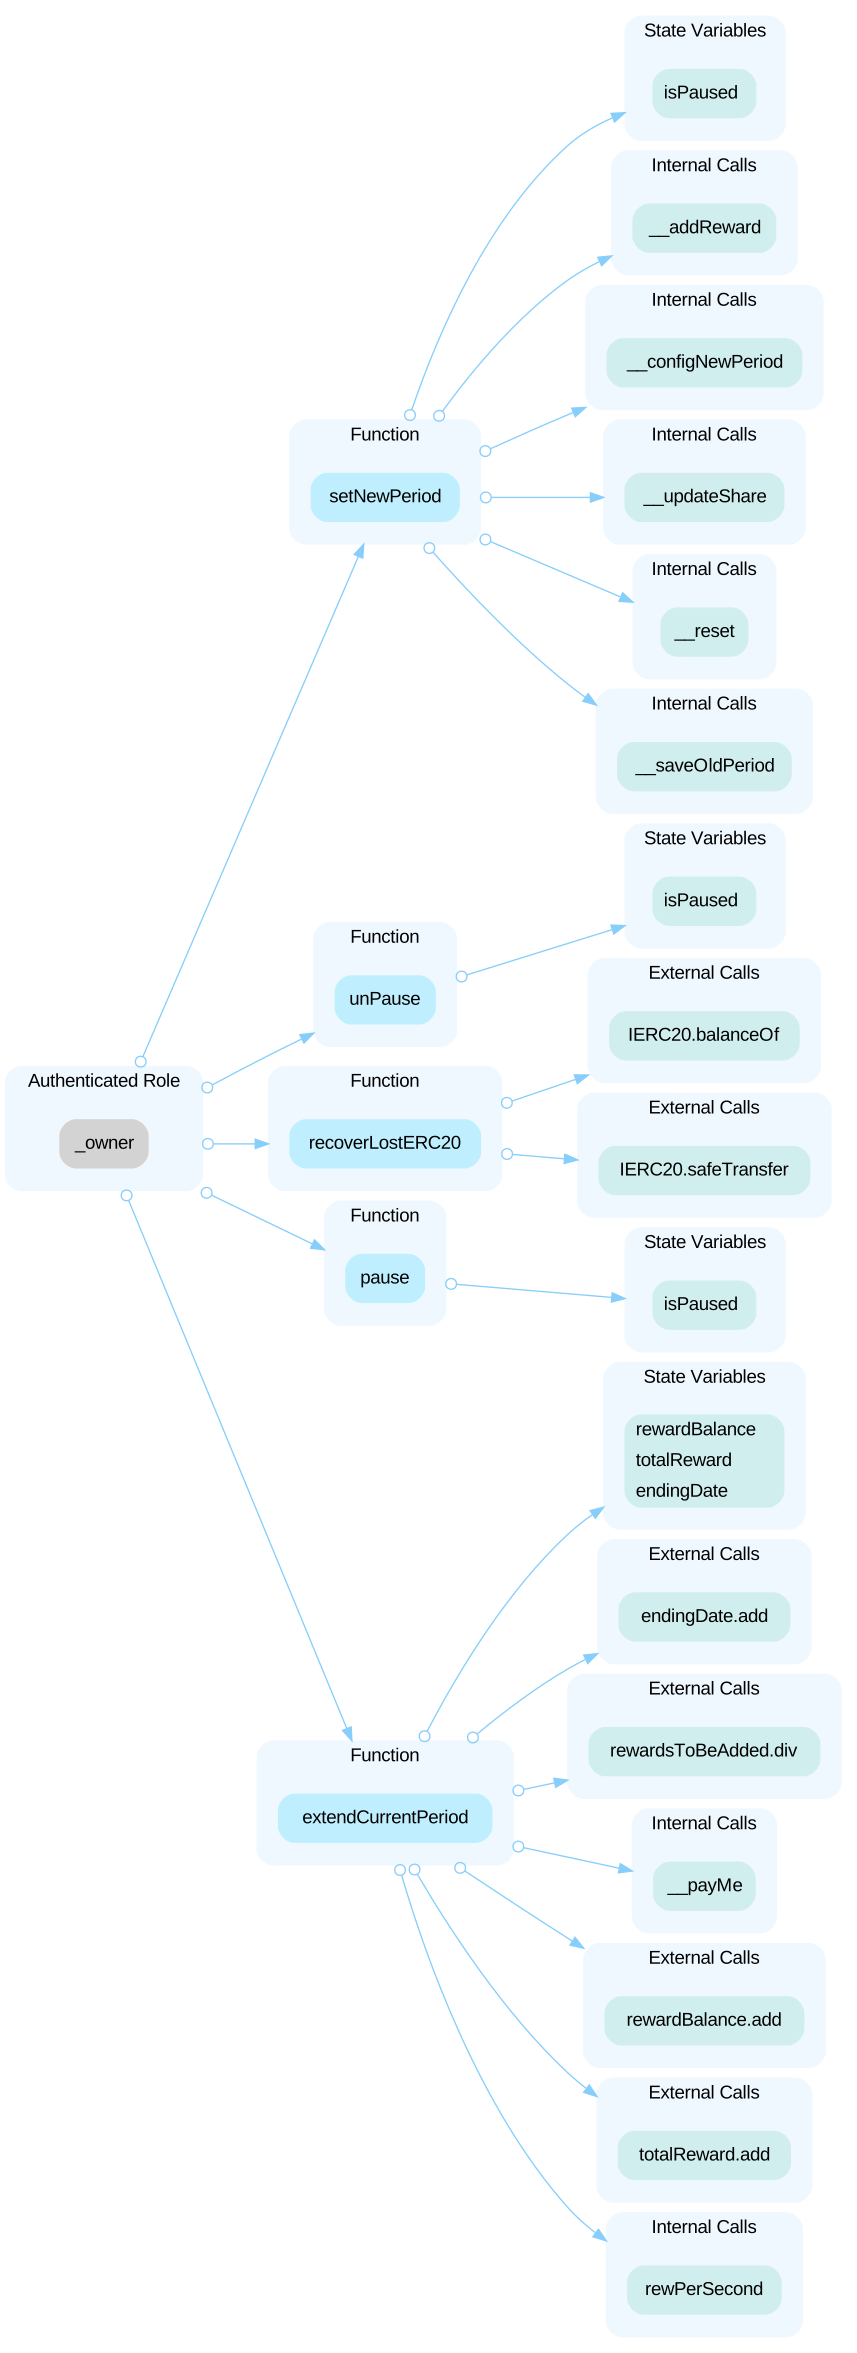
HighIncompatibility With Deflationary TokensOpen
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrive in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. If `tokenAddress` (the staking token) is deflationary, an attacker can repeatedly call `deposit()` and `withdraw()`/`emergencyWithdraw()` to empty the contract's funds and put other users' tokens at risk. Similarly, if the `rewardTokenAddress` (the rewards token) is deflationary, the actual balance is lower than anticipated, leaving the potential for insufficient funds when disbursing rewards. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
LowThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with tokens `tokenAddress` and `rewardTokenAddress`. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/LockedFarming.sol
Part of Seedify’s security record
 Seedify
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us