
Seedify security record
As of 22 Oct 2026, Seedify has 9 audit reports by 2 security firms on Trustblock; the latest is by Hacken, dated 10 Oct 2025. Those reports list no open critical findings. It also holds 4 deployed contracts on 3 chains.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits9
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Seedify.fund / MyToken Audit | Security firm: Hacken | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · hacken.io |
| Seedify.fund / BondingCurve | Security firm: Hacken | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · hacken.io |
| Seedify Fund / IDO & Linear Vesting | Security firm: Hacken | Date: | Scope: 3 addresses on Ethereum, BNB Chain and Arbitrum | No open critical findings | Open · hacken.io |
| Seedify layer zero | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Seedify NFT Launchpad | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Vesting Update | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Seedify finance Locked-Yield-Farming | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Seedify.fund (nft-vanguards) | Security firm: CertiK | Date: | Scope: Files named in the report | 1 critical finding, fixed | Open · skynet.certik.com |
| Old IDO & NFT Launchpads Upgrades (Agency Work) | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings78
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 7 | 0 | 5 |
| Medium | 6 | 0 | 6 |
| Low | 12 | 1 | 40 |
HighCentralization Related RisksSeedify layer zero · CertiK · 3 Oct 2024Open
**Note:** The finding only concerns those centralized functions within the scope of the audit, and does not include those which may exist within the contract due to out-of-scope inheritances. ### LzIDO.sol In the contract `LzIDO`, the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and update the refund period both in the `LzIDO` contract and in the corresponding cross-chain `LzLinearVesting` contract. 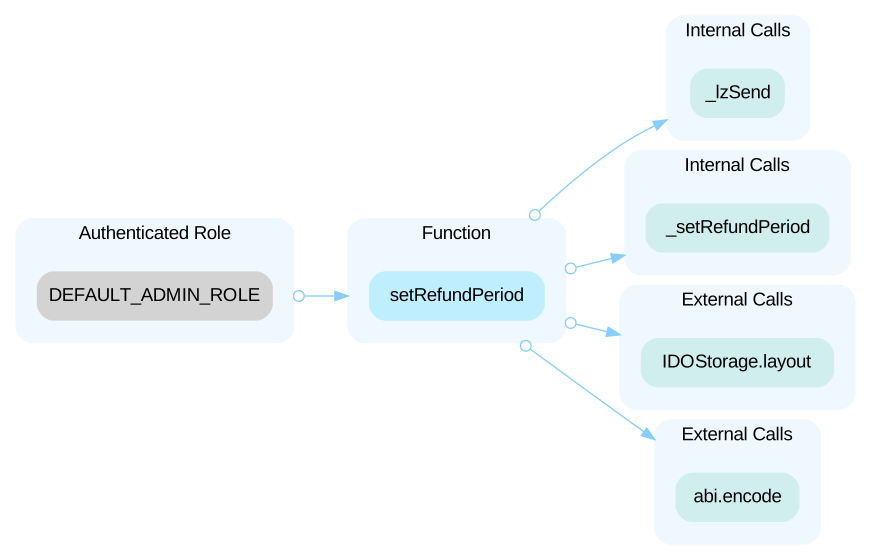 In the contract `LzIDO`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the destination chain id from its original, changing the chain the contract sends messages to and receives messages from. 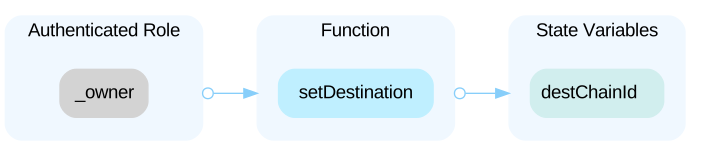 --- ### LzLinearVesting.sol In the contract `LzLinearVesting`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the destination chain id from its original, changing the chain the contract sends messages to and receives messages from. 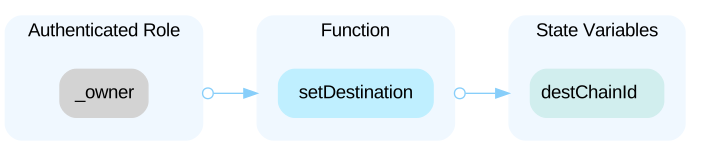
Open the reportHighCentralized Control of Contract UpgradeSeedify layer zero · CertiK · 3 Oct 2024Open
In the contract `INO`, the role `admin` has the authority to update the implementation contract behind the contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract appointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Open the reportHighCentralization Risks in LinearVesting.solVesting Update · CertiK · 19 Mar 2024Open
In the contract `LinearVesting` the role `_owner` has authority over the functions shown below. - `pause()`: Pauses all vesting activities, preventing users from claiming tokens. Only the contract owner (`onlyOwner`) can call this function. - `unpause()`: Unpauses all vesting activities, allowing users to resume claiming tokens. Only the contract owner (`onlyOwner`) can call this function. - `update(bytes32 merkleRoot_, uint32 startTime_, uint32 endTime_, uint256 toClaim)`: Updates the vesting schedule settings, including the Merkle root, start time, end time, and the amount of tokens to be claimed. It also allows the transfer of additional tokens to the contract for vesting. Only the contract owner (`onlyOwner`) can call this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functionalities of the project.
Open the reportHighCentralization Risks in LockedFarming.solSeedify finance Locked-Yield-Farming · CertiK · 13 Nov 2023Open
In the contract `SMD_v5` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set rewards periods, extend the current period, pause/unpause functions, and withdraw excess tokens mistakenly sent to the contract. Notably, the hacker can prevent users from withdrawing staked tokens by updating `lockDuration` to a large value via `setNewPeriod()`. 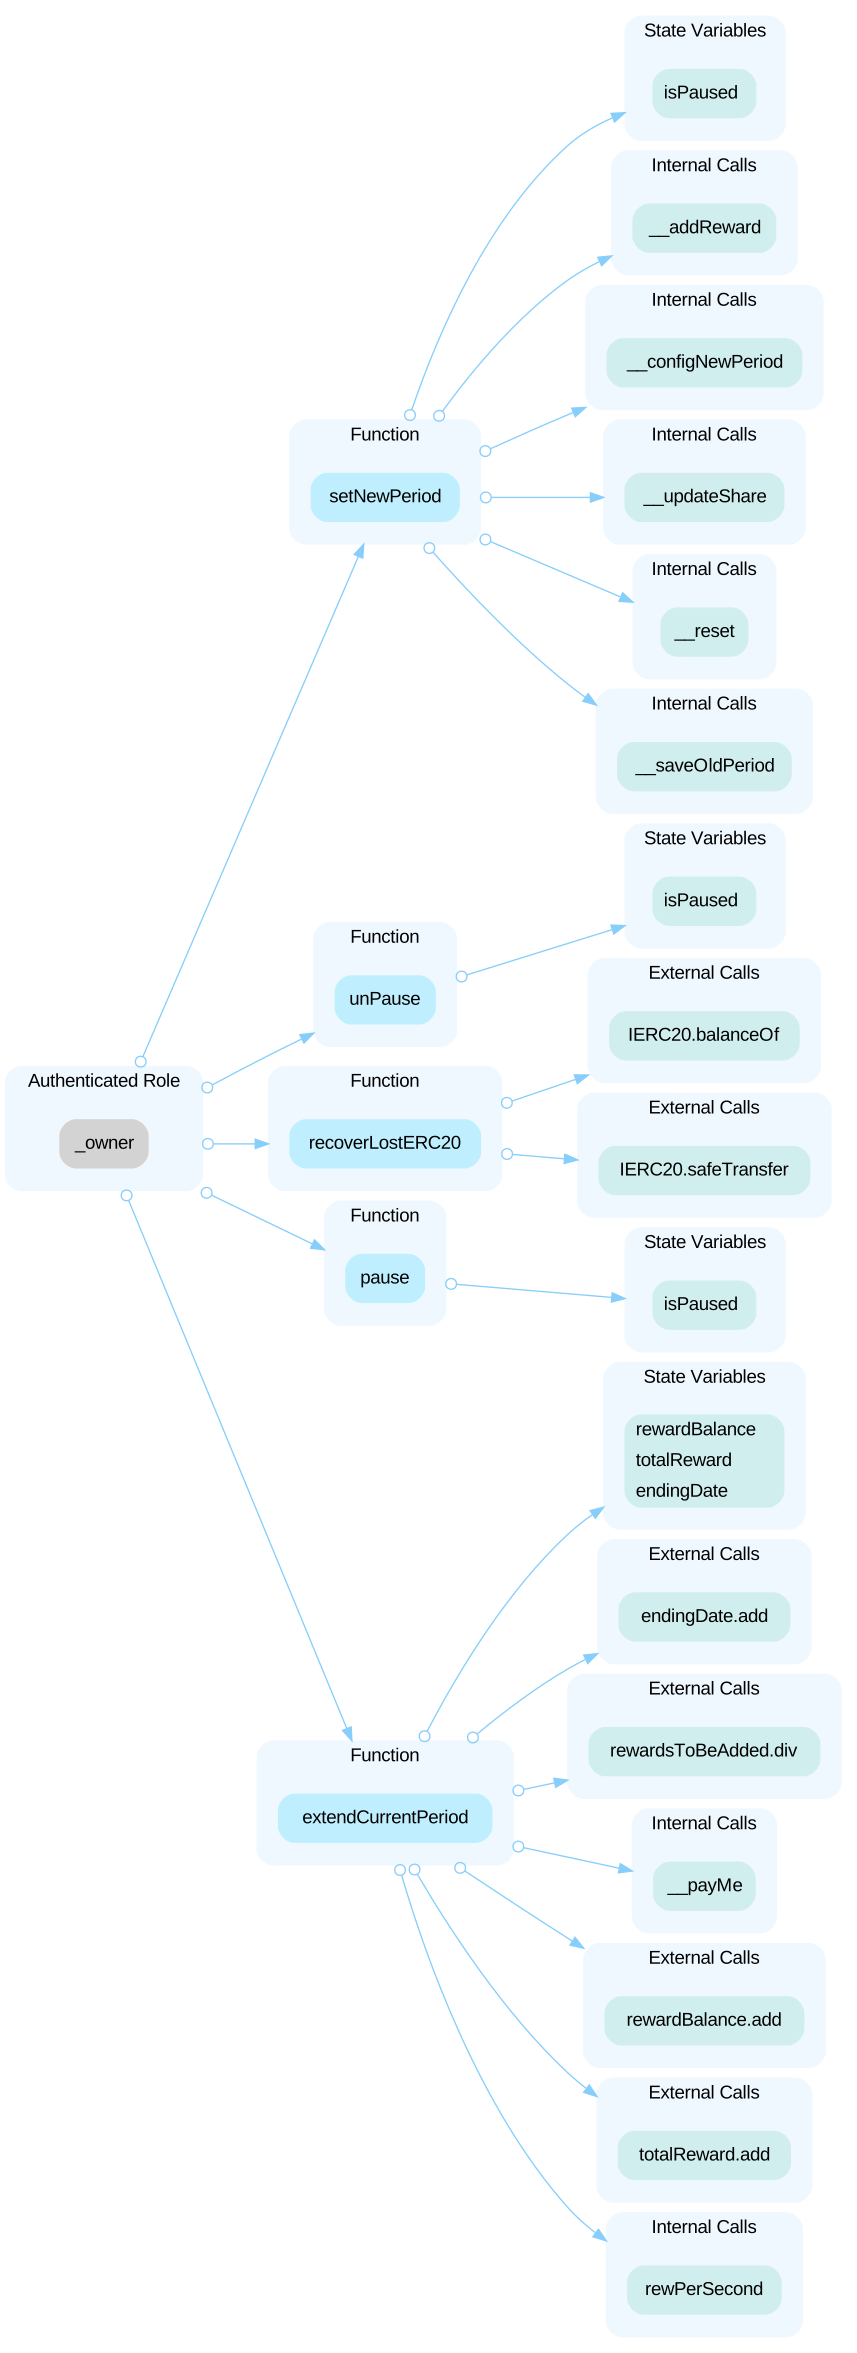
Open the reportHighIncompatibility With Deflationary TokensSeedify finance Locked-Yield-Farming · CertiK · 13 Nov 2023Open
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrive in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. If `tokenAddress` (the staking token) is deflationary, an attacker can repeatedly call `deposit()` and `withdraw()`/`emergencyWithdraw()` to empty the contract's funds and put other users' tokens at risk. Similarly, if the `rewardTokenAddress` (the rewards token) is deflationary, the actual balance is lower than anticipated, leaving the potential for insufficient funds when disbursing rewards. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
Open the reportHighCentralization Related RisksSeedify.fund (nft-vanguards) · CertiK · 15 Sep 2023Open
In the contract `BlackBoxVanguard` from the commit hash `58381fbee616cd801f73dde2d25dc6e8eacf11a6`, the role `_owner` has authority over the functions shown in the diagram below. 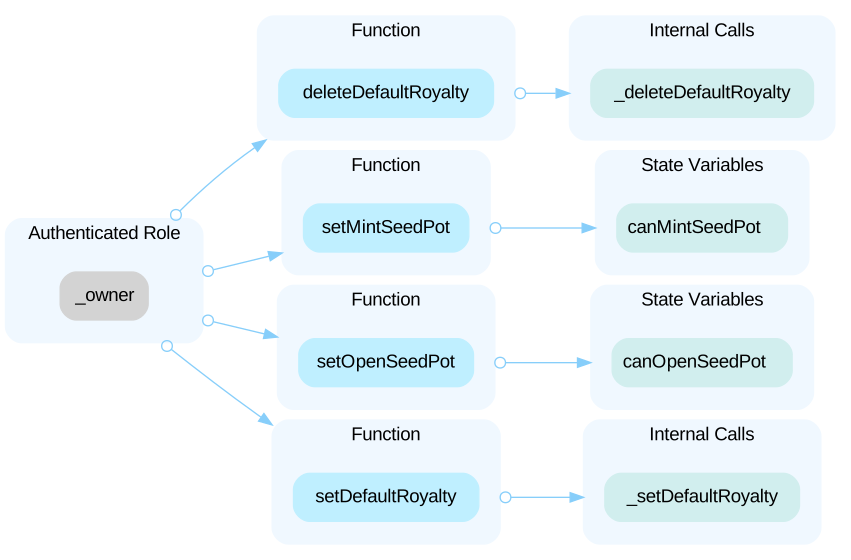 In addition, the `openBox()` function is callable when it is both the box owner and the `_owner` address. The `findBox()` is callable by the whitelisted addresses that can be verified by MerkleProof library, which are not defined in the scope of this contract. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. --- In the contract `Vanguard` from the commit hash `58381fbee616cd801f73dde2d25dc6e8eacf11a6`, the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 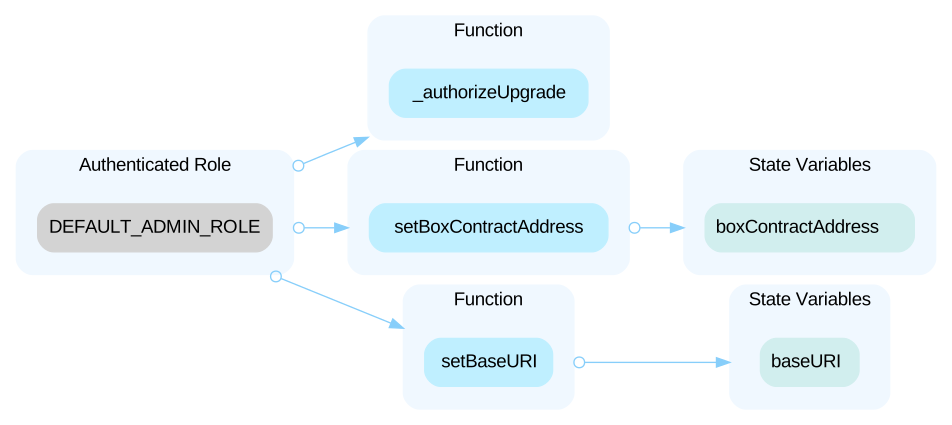 In the contract `Vanguard` from the commit hash `58381fbee616cd801f73dde2d25dc6e8eacf11a6`, the role `boxContractAddress` has authority over the functions shown in the diagram below. Any compromise to the `boxContractAddress` account may allow the hacker to take advantage of this authority. 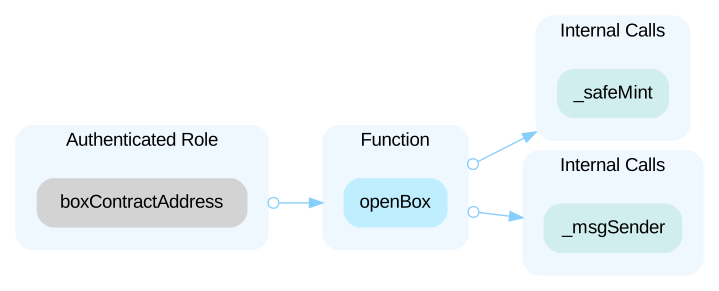 --- Note that this finding is also applicable in the `dc1b4d74d3968e855911145c54adce7b6d82b040` commit. Please see the alleviation section for the functions changing details.
Open the reportHighCentralization RisksOld IDO & NFT Launchpads Upgrades (Agency Work) · CertiK · 3 Jan 2023Open
In the contract `SeedifyFundBUSD.sol` the role `_owner` has authority over the functions: - `addWhitelist()` - `updateTierUsersValue()` - `updateTierValues()` - `setTokensPerBUSD()` - `setRefundThresholdTime()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and 1) Add users to the whitelist using the `addWhitelist()` function allowing them to buy tokens using the `buyToken()` function. 2) Change the `tiersMaxCap[]` array that decides the maximum amount of tokens that can be bought by users of one particular tier, and the `maxAllocaPerUserInTiers[]` array that decides the amount of tokens that can be bought by a user in a particular tier. 3) Change the 'totalUserInTiers[]' array that keeps track of the total number of users in a whitelist, alongside the `maxAllocaPerUserInTiers[]` array. 4) Change the `tokensPerBUSD` and `refundThresholdTime` using the `setTokensPerBUSD()` and `setRefundThresholdTime()` functions respectively. In addition, in the contract `SeedifyFundBUSD.sol` the `projectOwner` is set in the `constructor()` and receives all `BUSD` from buys and also is the source of `BUSD` in `refund()`. If the `projectOwner` does not hold enough `BUSD`, then `refund()` will revert. In the contract `INOLaunchpadSmartContract.sol` the role `_owner` has the authority over the following functions: - `updateNFTprice()` - `pause()` - `unpause()` - `addWhitelist()` - `removeWhitelist()` Any compromise to the '_owner' account may allow the hacker to take advantage of this authority and 1) Alter the `nftPrice` using the `updateNFTprice()` function. 2) Prevent everyone from buying new tokens using the 'pause()' function. 3) Allow users to buy new tokens using the `unpause()` functions, when they are not intended to. 4) Add or remove users from the `whitelist[]` array, using the `addWhitelist()` and `removeWhitelist()` functions respectively.
Open the reportMediumMalicious Owner Can Drain Contract Funds, Blocking User ClaimsSeedify Fund / IDO & Linear Vesting · Hacken · 14 Apr 2025Open
The report gives no description here.
Open the reportMediumUsers Can Be Blocked From Refunds on Multiple ContributionsSeedify Fund / IDO & Linear Vesting · Hacken · 14 Apr 2025Open
The report gives no description here.
Open the reportMediumInadequate Validation of `startTime_` and `endTimVesting Update · CertiK · 19 Mar 2024Open
In the `update()` function of the `LinearVesting` contract, there is a lack of validation for the `startTime_` parameter. Specifically, the function does not check whether `startTime_` is greater than the current block timestamp (`block.timestamp`). This omission allows for the possibility of setting a start time in the past, which could lead to unexpected behavior in the vesting logic and potentially enable exploitation by malicious actors. Similarly, updating `endTime_` without considering the current claimed tokens may bring unexpected result.
Open the reportShow 10 more
MediumIncompatibility with Deflationary TokensVesting Update · CertiK · 19 Mar 2024Open
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f ```solidity=82 ERC20Interface.safeTransferFrom( msg.sender, address(this), toClaim ); ``` - Transferring tokens by `toClaim`. ```solidity=87 totalVested += toClaim; ``` - The `toClaim` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
Open the reportMediumPotential Cross-Chain Replay Attack Due to Non-UnVesting Update · CertiK · 19 Mar 2024Open
The `LinearVesting` contract uses a Merkle root to verify user allocations for token vesting. If the same Merkle root is deployed in identical vesting contracts across multiple chains, there is a risk of a cross-chain replay attack. In such a scenario, a user could use the same Merkle proof to claim tokens on each chain, potentially leading to unauthorized token acquisition or double-spending.
Open the reportMediumIncompatibility With Deflationary TokensOld IDO & NFT Launchpads Upgrades (Agency Work) · CertiK · 3 Jan 2023Open
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee) in a MasterChef contract, only 90 tokens actually arrive in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. In the `buyTokens()` function, the amount of tokens sent to the msg.sender is tracked by the variable `buyInOneTier[]`. If the token is deflationary, the amount of tokens received by the msg.sender would be less than what the `buyInOneTier[]` is increased by and in the `refund()` function, even if the `buyInOneTier[msg.sender] >= amount`, the `msg.sender` might still not have enough tokens.
Open the reportLowInitializer Could Be Front-runSeedify.fund / MyToken Audit · Hacken · 10 Oct 2025Open
The report gives no description here.
Open the reportLowMissing Storage GapSeedify.fund / MyToken Audit · Hacken · 10 Oct 2025Open
The report gives no description here.
Open the reportLowNon Disabled Implementation ContractSeedify Fund / IDO & Linear Vesting · Hacken · 14 Apr 2025Open
The report gives no description here.
Open the reportLowOwner Can Arbitrarily Modify Vesting Terms and Impact User BalancesSeedify Fund / IDO & Linear Vesting · Hacken · 14 Apr 2025Open
The report gives no description here.
Open the reportLowUnnecessary Setting of `ido` AddressSeedify layer zero · CertiK · 3 Oct 2024Open
The following comment is above the constructor of `LzLinearVesting`: ```solidity // @param _ido The IDO contract address - only to set on NON CROSSCHAIN IDO. ``` Within the constructor, `LinearVestingStorage.layout().isCrosschainIDO` is set to `true`, confirming that setting the `ido` state is unnecessary.
Open the reportLowDivide Before MultiplyVesting Update · CertiK · 19 Mar 2024Open
Performing integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=137 uint256 timePassedRatio = (timePassed * 1e18) / timeLeft; ``` ```solidity=139 claimableAmount = (((amount - startAmount) * timePassedRatio) / 1e18) + startAmount; ```
Open the reportLowRounding Issue in Linear Vesting CalculationVesting Update · CertiK · 19 Mar 2024Open
The `getClaimableAmount()` function in the `LinearVesting` contract calculates the amount of tokens that a user is eligible to claim based on a linear vesting schedule. The calculation involves division operations that can introduce rounding issues due to Solidity's integer arithmetic, which always rounds down. These rounding issues can result in small discrepancies in the calculated claimable amount.
Open the reportShow 5 more
LowThird-Party Dependency UsageVesting Update · CertiK · 19 Mar 2024Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=29 IERC20 public immutable ERC20Interface; ``` - The contract `LinearVesting` interacts with third party contract with `IERC20` interface via `ERC20Interface`.
Open the reportLowThird-Party Dependency UsageSeedify finance Locked-Yield-Farming · CertiK · 13 Nov 2023Open
The contract is serving as the underlying entity to interact with tokens `tokenAddress` and `rewardTokenAddress`. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets.
Open the reportLowThird-Party DependenciesSeedify.fund (nft-vanguards) · CertiK · 15 Sep 2023Open
The contract is serving as the underlying entity to interact with third-party interface `IMagicEdenContract`. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. Note that this finding is also applicable in the `dc1b4d74d3968e855911145c54adce7b6d82b040` commit.
Open the reportLowThird Party DependencyOld IDO & NFT Launchpads Upgrades (Agency Work) · CertiK · 3 Jan 2023Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. The contract `SeedifyFundsContract` interacts with third party contract with `IERC20` interface via `ERC20Interface` and `IGOTokenInterface`.
Open the reportLowTypoOld IDO & NFT Launchpads Upgrades (Agency Work) · CertiK · 3 Jan 2023Open
There are the following typos in `INOLaunchpadSmartContract`: - In `buyTokens()`, it should be "You have already bought the item" instead of "You have already buy the item". - In `buyTokens()`, it should be "Amount is different" instead of "amount is different". - In the comment for `totalBUSDReceivedInAllTier` it should be `BUSD` not `bnd`.
Open the reportContracts4
| Address | Chain | Source code |
|---|---|---|
| 0xffda10b7fd9cf172e0502a6bc0e5e355516c5232 | Chain: BNB Chain | Source code: Verified source. Powered by Etherscan.io APIs |
| 0x477bc8d23c634c154061869478bce96be6045d12 | Chain: BNB Chain | Source code: Verified source |
| 0x560363bda52bc6a44ca6c8c9b4a5fadbda32fa60 | Chain: Arbitrum | Source code: Verified source |
| 0x560363bda52bc6a44ca6c8c9b4a5fadbda32fa60 | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="seedifyfund"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us