Seedify layer zero
CertiK reviewed Seedify (Seedify layer zero) on 3 Oct 2024: 8 findings, 0 critical; 5 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 5 |
HighCentralization Related RisksOpen
**Note:** The finding only concerns those centralized functions within the scope of the audit, and does not include those which may exist within the contract due to out-of-scope inheritances. ### LzIDO.sol In the contract `LzIDO`, the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and update the refund period both in the `LzIDO` contract and in the corresponding cross-chain `LzLinearVesting` contract. 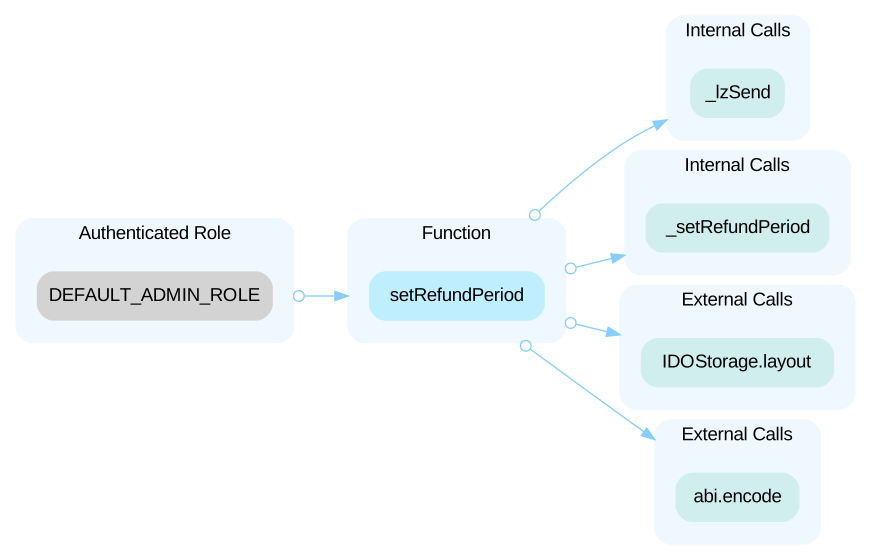 In the contract `LzIDO`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the destination chain id from its original, changing the chain the contract sends messages to and receives messages from. 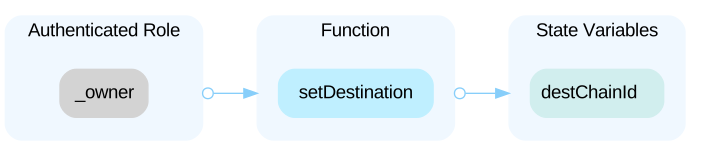 --- ### LzLinearVesting.sol In the contract `LzLinearVesting`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the destination chain id from its original, changing the chain the contract sends messages to and receives messages from. 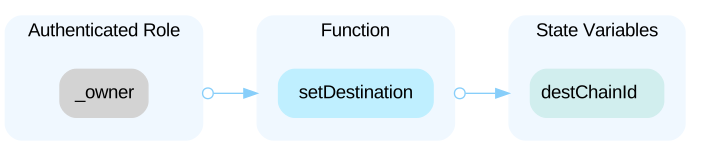
HighCentralized Control of Contract UpgradeOpen
In the contract `INO`, the role `admin` has the authority to update the implementation contract behind the contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract appointed by proxy and therefore execute potential malicious functionality in the implementation contract.
LowUnnecessary Setting of `ido` AddressOpen
The following comment is above the constructor of `LzLinearVesting`: ```solidity // @param _ido The IDO contract address - only to set on NON CROSSCHAIN IDO. ``` Within the constructor, `LinearVestingStorage.layout().isCrosschainIDO` is set to `true`, confirming that setting the `ido` state is unnecessary.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- src/ido/lzApp/LzIDO.sol
- src/ino/INO.sol
- src/linearvesting/lzApp/LzLinearVesting.sol
Part of Seedify’s security record
 Seedify
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us