TribalIsland
CertiK reviewed Tribal Island (TribalIsland) on 15 Jun 2023: 4 findings, 0 critical; 2 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `TICToken` the role `DEPLOYER_ROLE` has authority over the functions shown in the diagram below. 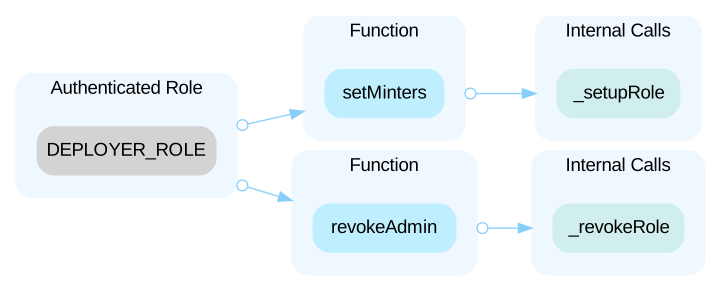 - `setMinters(address[] memory minters)`: Assigns the MINTER_ROLE to the specified list of addresses, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. - `revokeAdmin(address addr)`: Revokes the DEFAULT_ADMIN_ROLE from the specified address, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. Any compromise to the `DEPLOYER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TICToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. 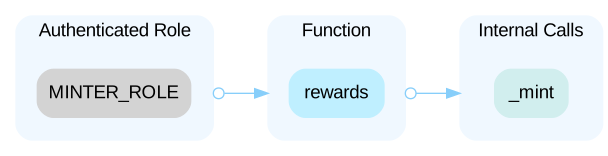 - `rewards(address account, uint256 amount)`: Mints new tokens and adds them to the specified account's balance, can only be called by a user with the MINTER_ROLE. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TICToken` the role `MULTSIG_ROLE` has authority over the functions shown in the diagram below. 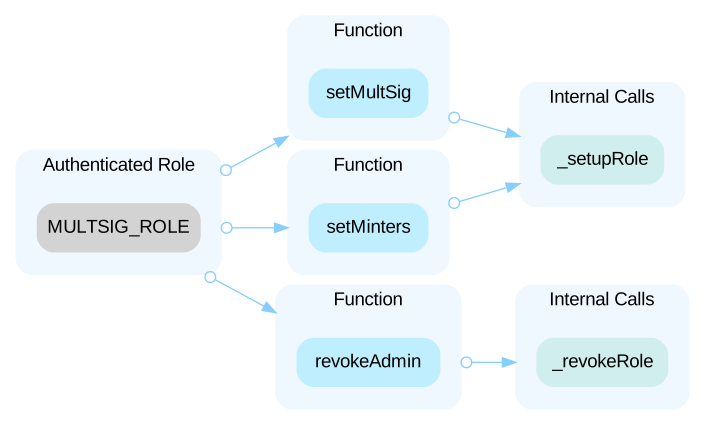 - `setMinters(address[] memory minters)`: Assigns the MINTER_ROLE to the specified list of addresses, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. - `setMultSig(address _multSigAddress)`: Sets a new address with the DEFAULT_ADMIN_ROLE, which is responsible for managing the MULTSIG_ROLE, can only be called by a user with the MULTSIG_ROLE. - `revokeAdmin(address addr)`: Revokes the DEFAULT_ADMIN_ROLE from the specified address, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. Any compromise to the `MULTSIG_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `DEPLOYER_ROLE` has authority over the functions shown in the diagram below. 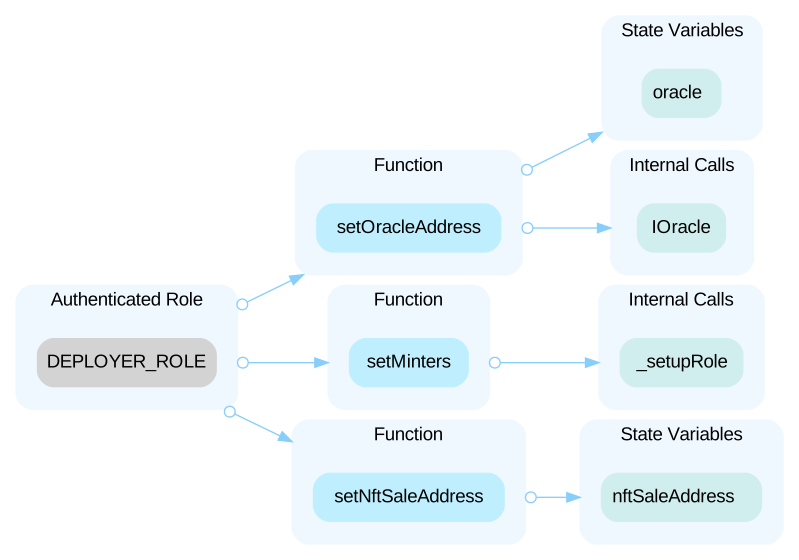 - `setNftSaleAddress(address _nftSaleAddress)`: Set the NFT sale contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setMinters(address[] memory minters)`: Set multiple minter addresses, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setOracleAddress(address _oracleAddress)`: Set the oracle contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. Any compromise to the `DEPLOYER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. 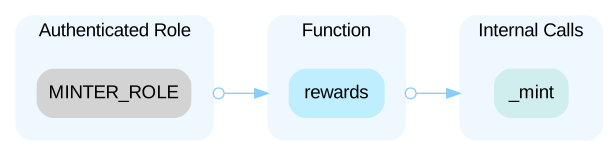 - `rewards(address account, uint256 amount)`: Mint new tokens as rewards for an account, only callable by addresses with the `MINTER_ROLE`. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `MULTSIG_ROLE` has authority over the functions shown in the diagram below. 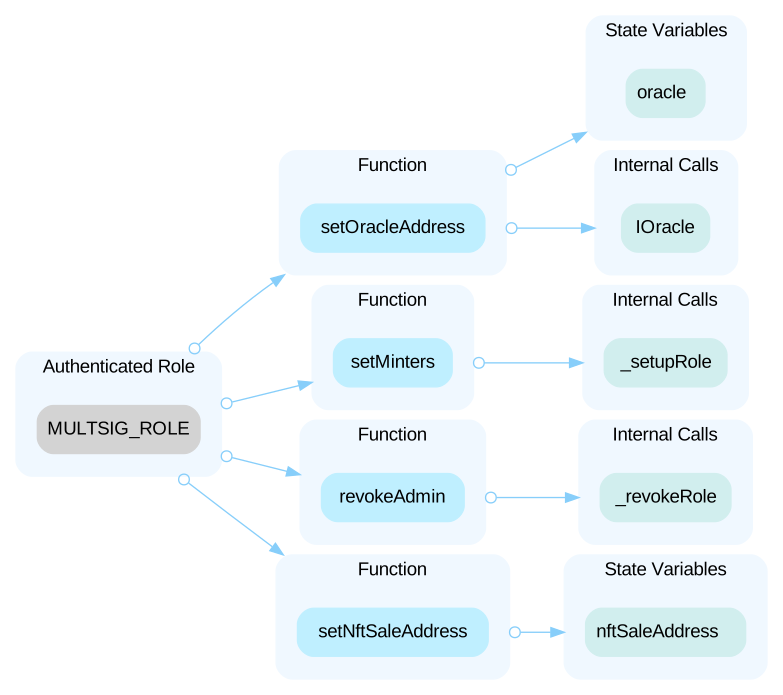 - `setNftSaleAddress(address _nftSaleAddress)`: Set the NFT sale contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setMinters(address[] memory minters)`: Set multiple minter addresses, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setOracleAddress(address _oracleAddress)`: Set the oracle contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `revokeAdmin(address addr)`: Revoke the `DEPLOYER_ROLE` from an address, only callable by addresses with the `MULTSIG_ROLE`. Any compromise to the `MULTSIG_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `nftSaleAddress` has authority over the functions shown in the diagram
HighInitial Token DistributionOpen
All `TIC` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `TIC` tokens without the consensus of the community.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- TICToken.sol
- TIToken.sol
Part of Tribal Island’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us