Tribal Island has 1 public audit report from CertiK; dated 15 Jun 2023; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Statuses are the security firms’ own
2 findings are still open or acknowledged in the firms’ reports: 2 high (all open).
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| TribalIsland | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 2 low 2 fixed · 2 open | skynet.certik.com ↗ |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 2 |
In the contract `TICToken` the role `DEPLOYER_ROLE` has authority over the functions shown in the diagram below. 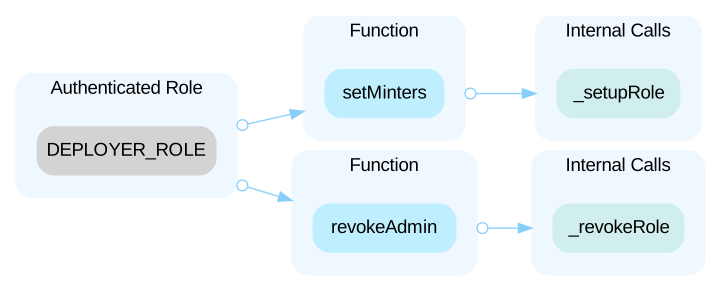 - `setMinters(address[] memory minters)`: Assigns the MINTER_ROLE to the specified list of addresses, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. - `revokeAdmin(address addr)`: Revokes the DEFAULT_ADMIN_ROLE from the specified address, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. Any compromise to the `DEPLOYER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TICToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. 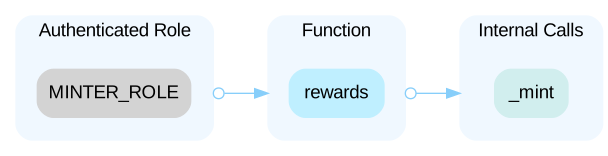 - `rewards(address account, uint256 amount)`: Mints new tokens and adds them to the specified account's balance, can only be called by a user with the MINTER_ROLE. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TICToken` the role `MULTSIG_ROLE` has authority over the functions shown in the diagram below. 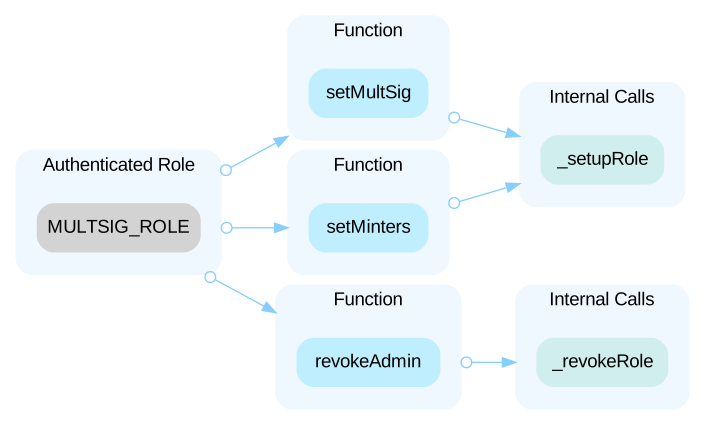 - `setMinters(address[] memory minters)`: Assigns the MINTER_ROLE to the specified list of addresses, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. - `setMultSig(address _multSigAddress)`: Sets a new address with the DEFAULT_ADMIN_ROLE, which is responsible for managing the MULTSIG_ROLE, can only be called by a user with the MULTSIG_ROLE. - `revokeAdmin(address addr)`: Revokes the DEFAULT_ADMIN_ROLE from the specified address, can only be called by a user with the DEPLOYER_ROLE or MULTSIG_ROLE. Any compromise to the `MULTSIG_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `DEPLOYER_ROLE` has authority over the functions shown in the diagram below. 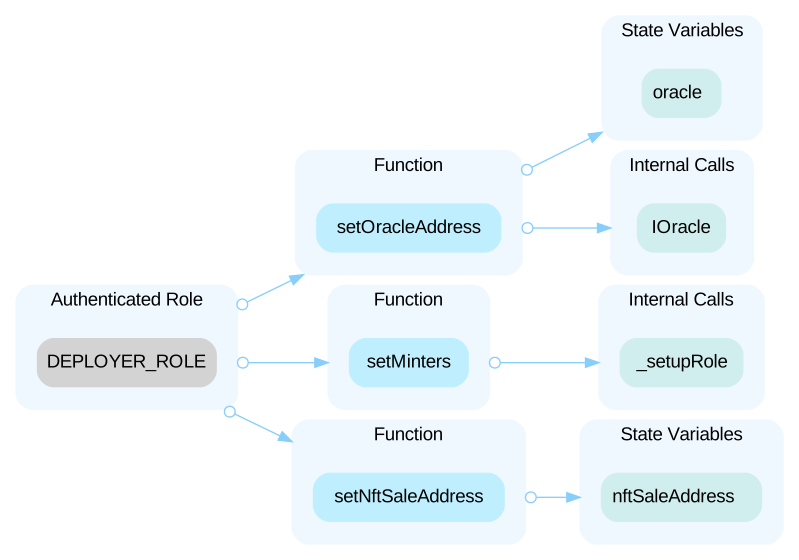 - `setNftSaleAddress(address _nftSaleAddress)`: Set the NFT sale contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setMinters(address[] memory minters)`: Set multiple minter addresses, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setOracleAddress(address _oracleAddress)`: Set the oracle contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. Any compromise to the `DEPLOYER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. 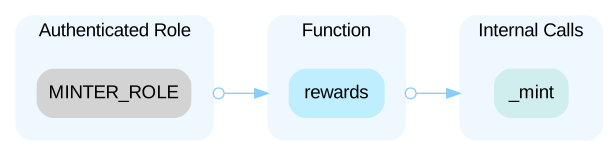 - `rewards(address account, uint256 amount)`: Mint new tokens as rewards for an account, only callable by addresses with the `MINTER_ROLE`. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `MULTSIG_ROLE` has authority over the functions shown in the diagram below. 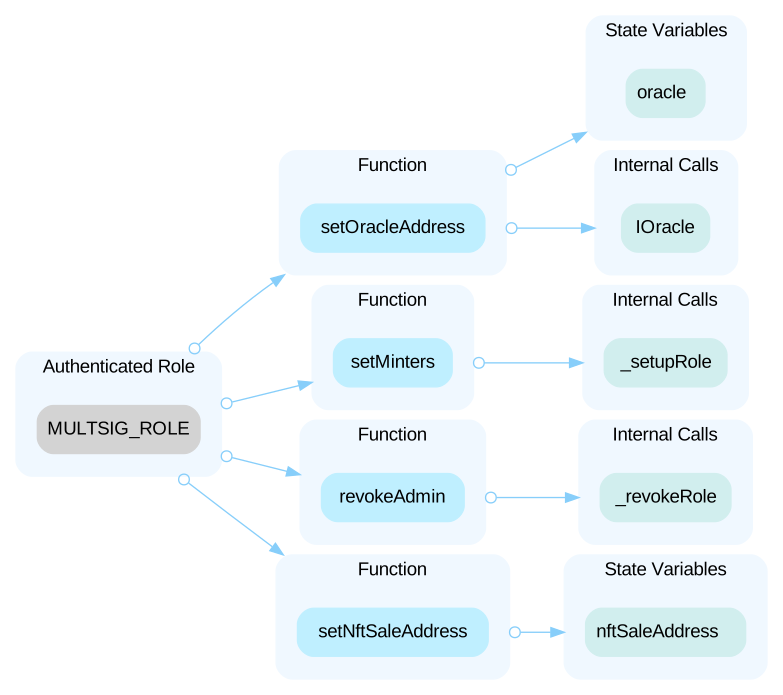 - `setNftSaleAddress(address _nftSaleAddress)`: Set the NFT sale contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setMinters(address[] memory minters)`: Set multiple minter addresses, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `setOracleAddress(address _oracleAddress)`: Set the oracle contract address, only callable by addresses with the `DEPLOYER_ROLE` or `MULTSIG_ROLE`. - `revokeAdmin(address addr)`: Revoke the `DEPLOYER_ROLE` from an address, only callable by addresses with the `MULTSIG_ROLE`. Any compromise to the `MULTSIG_ROLE` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project. --- In the contract `TIToken` the role `nftSaleAddress` has authority over the functions shown in the diagram
Open the reportAll `TIC` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `TIC` tokens without the consensus of the community.
Open the reportThe reports name a repository or files. Open a report to see its scope.
Trustblock holds 1 public audit report for Tribal Island, dated 15 Jun 2023. The latest is by CertiK (“TribalIsland”).
CertiK wrote the report Trustblock holds for Tribal Island.
2 findings are still open or acknowledged in the firms’ reports: 2 high (all open). No critical finding is reported. Statuses are the security firms’ own.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="tribal-island"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us