PD Land
CertiK reviewed PD Land on 18 Apr 2022: 17 findings, 0 critical; 5 marked fixed, 12 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings17
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 4 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 8 | 0 | 3 |
HighCentralization Related Risks in the function `minOpen
In the function `mintAfterSale`, the role `owner` could mint any amount of tokens to itself after the public sale only if each type of tokens are no more than `MAX_PUBLIC_LAND_SALE_PER_TYPE`.
HighCentralization Risk in LandNFT.solOpen
In the contract `LandNFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 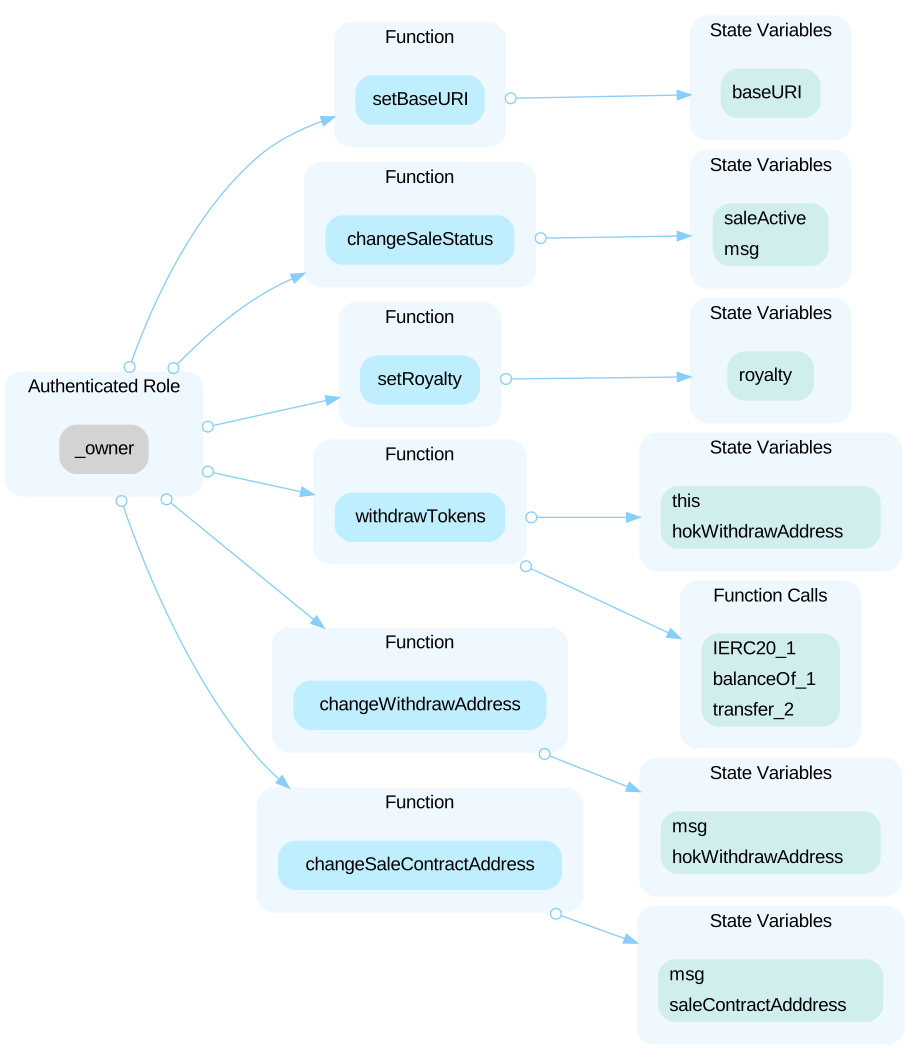 In the contract `LandNFT` the role `hokWithdrawAddress` has authority over the functions shown in the diagram below. Any compromise to the `hokWithdrawAddress` account may allow the hacker to take advantage of this authority. 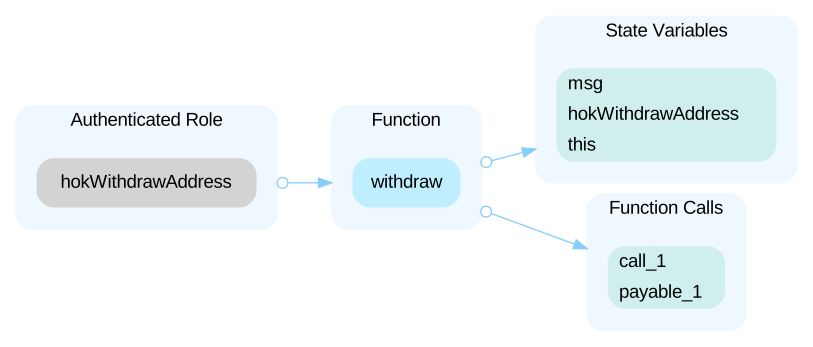 In the contract `LandNFT` the role `saleContractAdddress` has authority over the functions shown in the diagram below. Any compromise to the `saleContractAdddress` account may allow the hacker to take advantage of this authority. 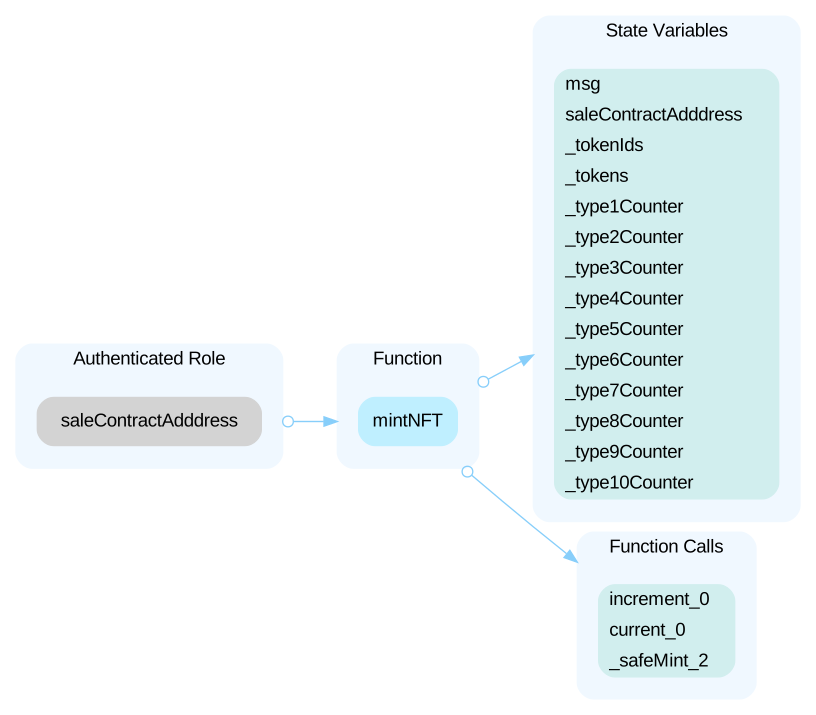
HighCentralization Risk in PrivatePublicSale.solOpen
In the contract `PrivatePublicLandSale` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 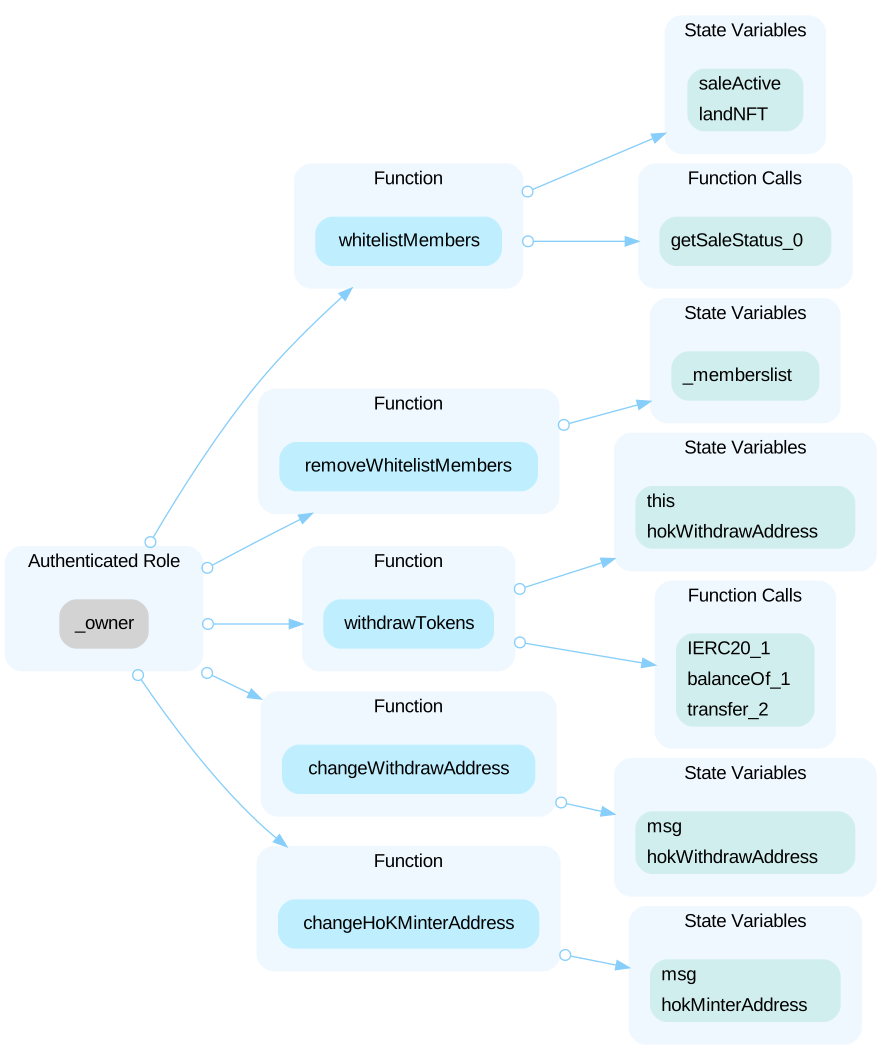 In the contract `PrivatePublicLandSale` the role `hokMinterAddress` has authority over the functions shown in the diagram below. Any compromise to the `hokMinterAddress` account may allow the hacker to take advantage of this authority. 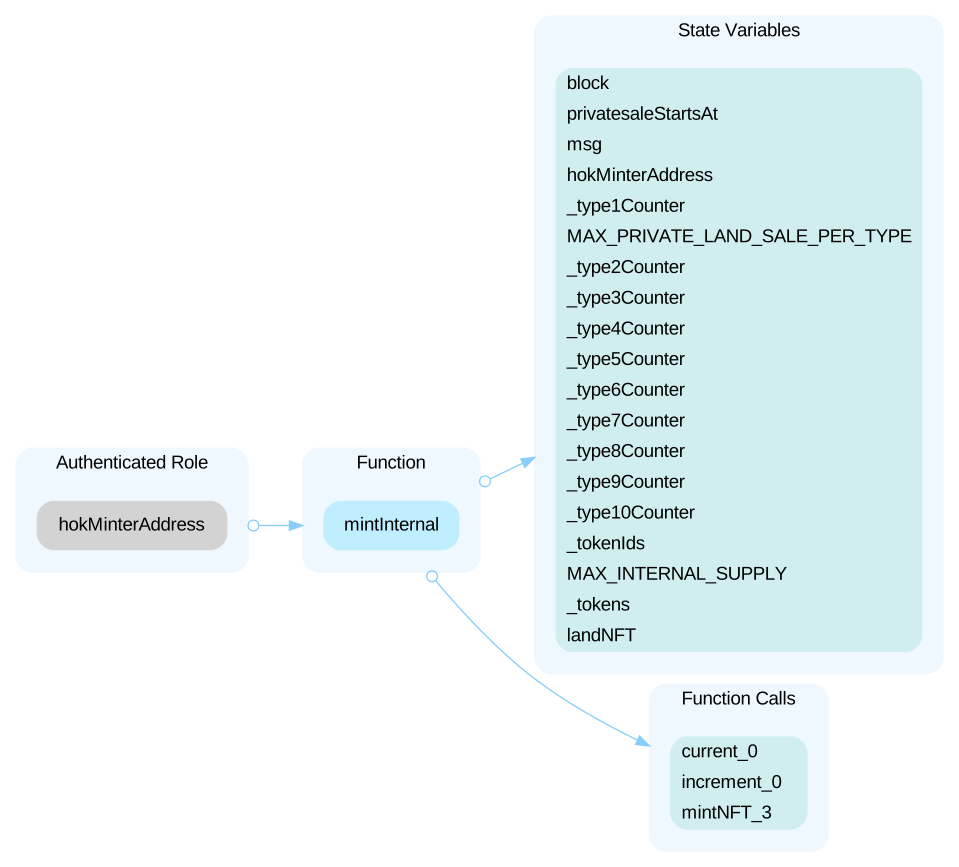 In the contract `PrivatePublicLandSale` the role `hokWithdrawAddress` has authority over the functions shown in the diagram below. Any compromise to the `hokWithdrawAddress` account may allow the hacker to take advantage of this authority. 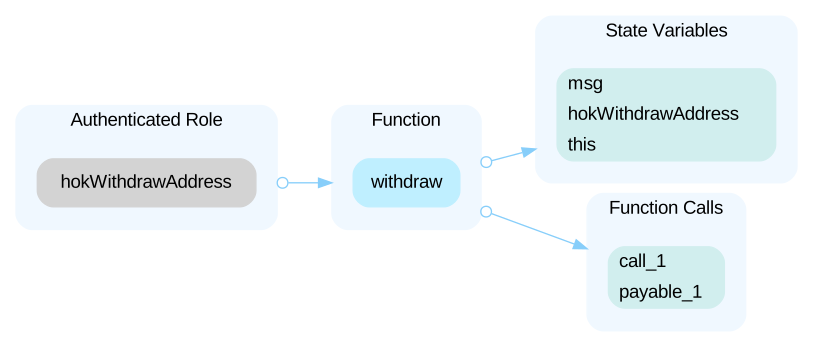
HighWithdraw ETHs to EOAOpen
In the contract `LandNFT` and `PrivatePublicLandSale`, the role `hokWithdrawAddress` could withdraw all the ETHs to the `hokWithdrawAddress`, which is an EOA. In addition, the `owner` role could change the `hokWithdrawAddress` to any address, which could be EOA as well.
LowImproper Usage of `public` and `external` TypeOpen
`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
LowLack of the time limitOpen
In the functions `getPrivateRemLandType()`, `getPublicRemLandType()`, `getRemPrivateSaleSupply()` and `getRemPublicSaleSupply()`, since the counters and `_tokenIds` are shared in each sale stage, the calling of these functions may cause logical issue. e.g. After the private sale, the calling of `getPrivateRemLandType()` may result in an overflow error or a wrong number.
LowLogical issue of `mintInternal()`Open
Before private sale, the `hokMinterAddress` could mint 700 tokens at most to itself, and the limit for each token type is 500. However, if the `hokMinterAddress` mints 500 tokens in one type, no one could mint this type of token in the private sale. In addition, keeping 500 tokens in one type for the `hokMinterAddress` may cause the price raising of this token type, however, it gives the power that the `hokMinterAddress` may sell all of them in another market and crash the price, as a result, the investors may suffer losses.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowThe `_memberslist[users[i]].balance` should be viOpen
In the function `isWhitelisted()`, users could view if they are in the `_memberslist`, however, they cannot know their `_memberslist[users[i]].balance` conveniently.
LowThird Party DependenciesOpen
The contract is serving as the underlying entity to implement the third-party ERC721A protocols. The scope of the audit treats 3rd party entities as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts.
Show 2 more
LowVariables That Could Be Declared as `constant`Open
The linked variables could be declared as `constant` since these state variables are never modified.
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- LandNFT.sol
- PrivatePublicSale.sol
Part of PD Land’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us