Venus - Liquidator Contract
Part of CertiK’s series
CertiK reviewed Venus Protocol (Venus - Liquidator Contract) on 4 Jul 2023: 11 findings, 0 critical; 9 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings11
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 8 |
HighCentralization Risks in Liquidator.solOpen
In the contract `Liquidator` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the `_accessControlManager` which can allow them to give any of the privledges outline below or the `protocolShareReserve` to collect the protocols share for themselves. 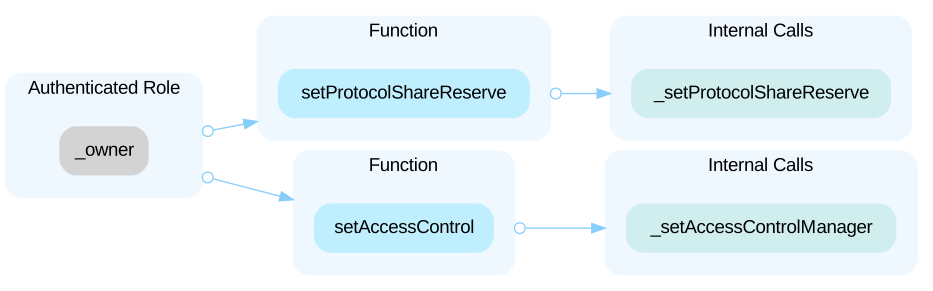 --- In the contract `Liquidator`, the `_accessContolManager` contract can give privilege to the following functions: - `restrictLiquidation()`, which can be used to prevent a borrower from being liquidated by having no liquidators on their allowlist. - `unrestrictLiquidation()`, which can be used to allow a non-allowlisted user to liquidate an account. - `addToAllowlist()`, which can allow any address to liquidate an account. - `removeFromAllowlist()`, which can remove an liquidators ability to liquidate an account. If all liquidators are removed from a borrowers allowlist this will make it so they cannot be liquidated. - `setTreasuryPercent()`, which can be set so that the protocol share reserve receives none of the liquidation incentive. Or it can be set so that it receives all of the liquidation incentive. - `setMinLiquidatableVAI()`, which can be set to a small value so that a liquidator would always need to liquidate VAI before they could liquidate any other borrows. - `setPendingRedeemChunkLength()`, which can be set to a large value and cause a denial of service if the `pendingRedeem` array is too large. Or set to zero to prevent any tokens pending redemption from being redeemed. - `pauseForceVAILiquidate()`, which can be used to not have to liquidate VAI borrows before others. - `resumeForceVAILiquidate()`, which can be used to ensure that VAI borrows are liquidated before any others.
HighCentralized Control of Contract UpgradeOpen
`Liquidator.sol` is an upgradeable contract. The owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/Liquidator/LiquidatorStorage.sol
- contracts/Liquidator/Liquidator.sol
Part of Venus Protocol’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us