Venus - RewardsDistributor
Part of CertiK’s series
CertiK reviewed Venus Protocol (Venus - RewardsDistributor) on 10 Jul 2023: 5 findings, 0 critical; 3 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 2 |
HighCentralization RisksOpen
In the contract `RewardsDistributor` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Change the contributor reward token speed to any value; - Change the max loops, which limits that amount of `vToken` that `claimRewardToken()` can be called on at one time; - Grant any amount of reward tokens, provided enough are held by the contract, to any user. 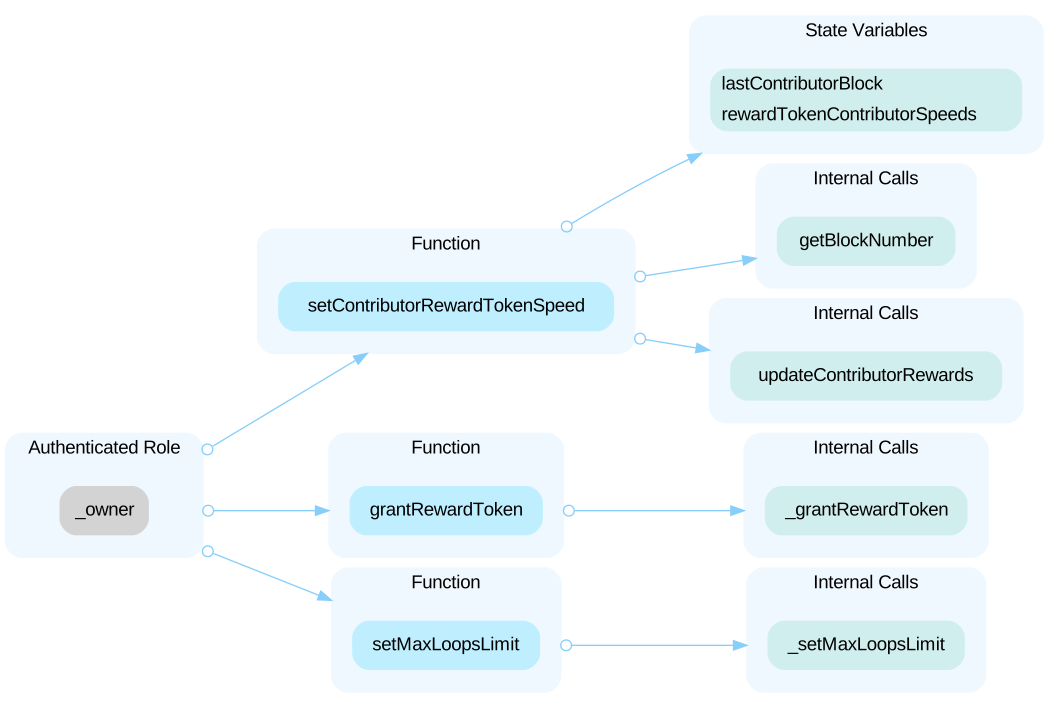 In the contract `RewardsDistributor` the role `DEFAULT_ADMIN_ROLE` of the Access Control Manager can grant addresses the privilege to call the following functions: - `setRewardTokenSpeeds()` - `setLastRewardingBlocks()` Any compromise to the `DEFAULT_ADMIN_ROLE` or these privileged functions may allow the hacker to take advantage of this authority and do the following: - change the reward token speed to any value; - set the last rewarding blocks to either stop rewards early or to lengthen the amount of blocks rewards are given for.
HighCentralized Control of Contract UpgradeOpen
`RewardsDistributor` is an upgradeable contract. The owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract as well as change the logic of the contract to return incorrect prices.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- contracts/Rewards/RewardsDistributor.sol
- contracts/Lens/PoolLens.sol
Part of Venus Protocol’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us