Rubydex - Audit
CertiK reviewed RubyDex (Rubydex - Audit) on 3 Jul 2023: 14 findings, 0 critical; 6 marked fixed, 5 acknowledged, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 5 | 6 |
HighCentralization Related RisksOpen
In the contract `UpdateState` the role `admin` has authority over the function shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and update the implementation contract. 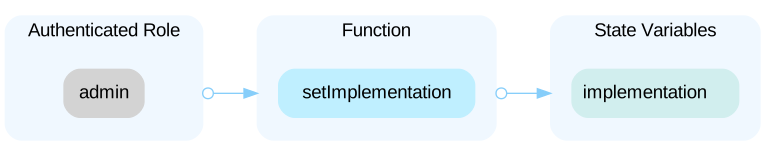 In the contract `UpdateStateImplementation` the role `admin` has authority over the function shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and set operators. 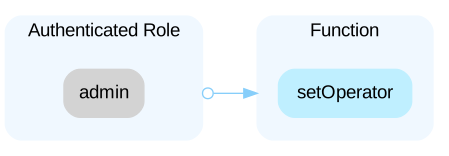 In the contract `UpdateStateImplementation` the role `operator` has authority over the functions shown in the diagram below. Any compromise to the `operator` account may allow the hacker to take advantage of this authority and add/update/delist symbols or update users' balances and positions. 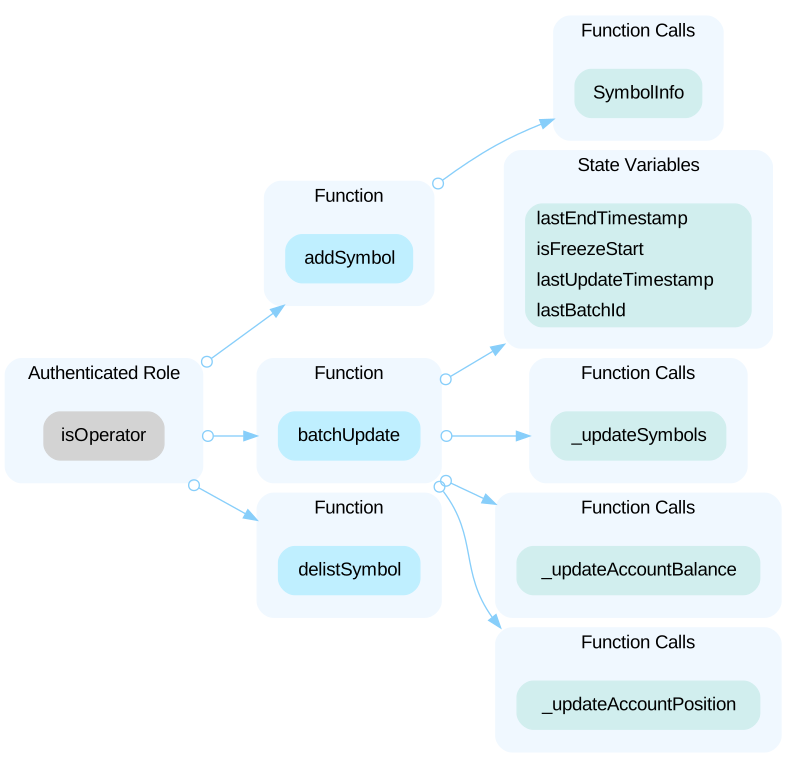 In the contract `UpdateStateImplementation` the role `vault` has authority over the following functions: - `updateBalance()` - `updatePosition()` - `resetFreezeStart()` Any compromise to the `vault` account may allow the hacker to take advantage of this authority and update the variable `isFreezeStart` and update users' balances and positions. In the contract `Admin` the role `admin` has authority over the function shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and transfer the admin role. 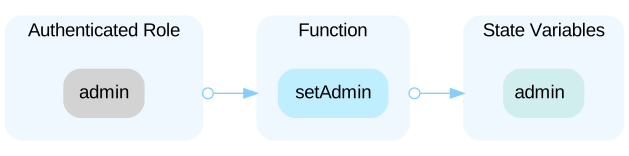 In the contract `Vault` the role `admin` has authority over the function shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and update the implementation contract. 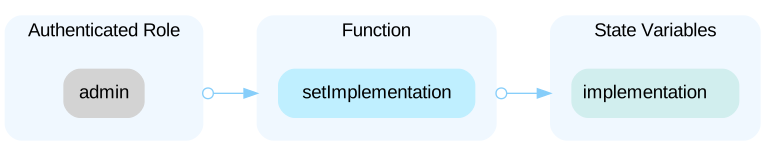 In the contract `VaultImplementation` the role `admin` has authority over the functions shown in the diagram below. Any compromise to the `admin` account may allow the hacker to take advantage of this authority and add/remove signers, set operators, pause/unpause contract, and set the minimal number of signers needed for withdrawals. 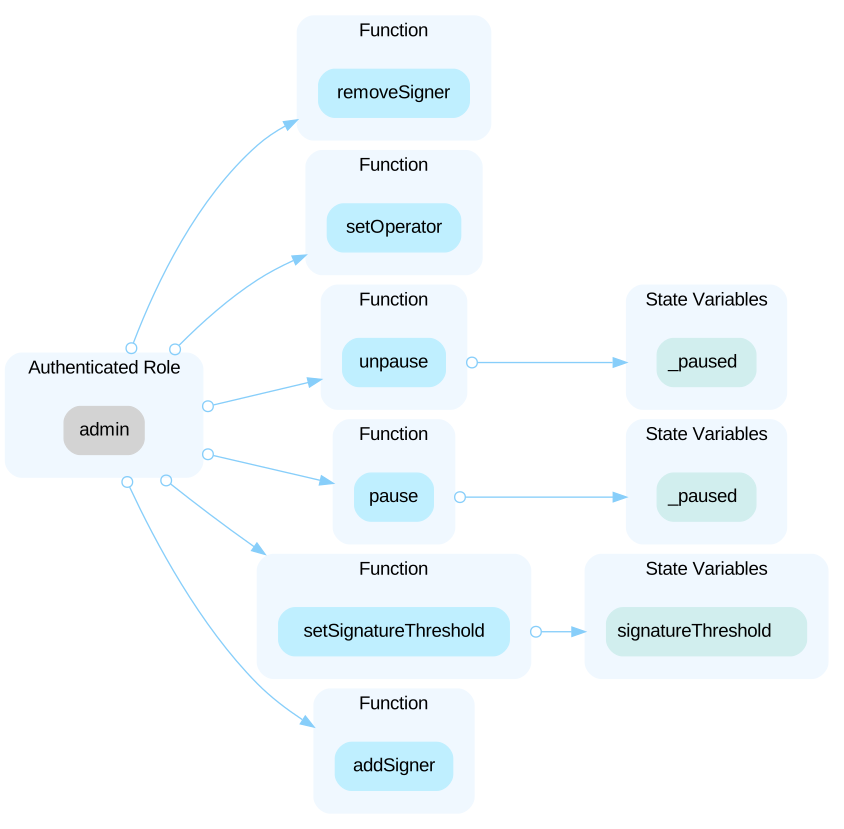 In the contract `VaultImplementation` the role `operator` has authority over the functions shown in the diagram below. Any compromise to the `operator` account may allow the hacker to take advantage of this authority and add/remove assets and execute withdrawals. 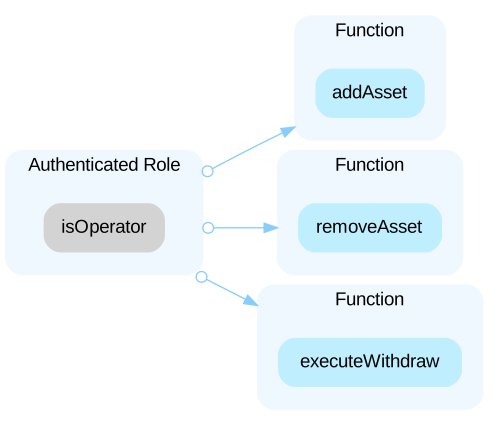 In the contract `VaultImplementation` the role `update` has authority over the following function: - `transferOut()` Any compromise to the `update` account may allow the hacker to take advantage of this authority and transfer tokens out.
HighCentralized Control of Contract UpgradeOpen
The `UpdateState` and `Vault` contracts are upgradeable via their respective proxy contracts, which allows the owner to update the contract's implementation without the community's commitment. However, if an attacker gains access to the owner's account, they can modify the contract's implementation and drain tokens from the contract without the community's knowledge or consent.
HighDangerous External CallOpen
The `VaultImplementation` contract contains the `swapAndDeposit()` and `tryExecuteWithdraw()` functions that can trigger the `swap()` function in the `MegaSwapper` contract. The `swap()` function performs an external call to the user-input address `caller`, which can potentially be a contract with unknown and potentially malicious code. This vulnerability could be exploited by attackers to carry out various types of attacks.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (19)
- contracts/vault/Vault.sol
- contracts/utils/Admin.sol
- contracts/utils/RevertReasonParser.sol
- contracts/vault/IVault.sol
- contracts/utils/IAdmin.sol
- contracts/vault/VaultStorage.sol
- contracts/update/UpdateStateStorage.sol
- contracts/update/IUpdateState.sol
- contracts/update/ForcedAction.sol
- contracts/utils/INameVersion.sol
- contracts/utils/IERC20.sol
- contracts/swapper/ISwapper.sol
- contracts/update/UpdateStateImplementation.sol
- contracts/utils/SafeMath.sol
- contracts/vault/VaultImplementation.sol
- contracts/utils/NameVersion.sol
- contracts/update/UpdateState.sol
- contracts/swapper/MegaSwapper.sol
- contracts/utils/Log.sol
Part of RubyDex’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us