Venus - XVS Token Bridge
Part of CertiK’s series
CertiK reviewed Venus Protocol (Venus - XVS Token Bridge) on 26 Dec 2023: 21 findings, 0 critical; 20 marked fixed, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings21
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 19 |
HighCentralization Related RisksOpen
### BaseXVSProxyOFT In the contract `BaseXVSProxyOFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - Set the oracle to an address that does not provide accurate pricing information. - Pause or unpause the movement of tokens through the contract at critical periods. - Set the max daily limit, the max daily receive limit, the max single transaction limit, and the max single receive transaction limit to values that either are advantageous to the hacker moving funds across chains, or the hacker may set these values to 0 to prevent users from moving funds out of a vulnerable environment. - Set an address they control to be whitelisted and circumvent the bridged amount checks. - Set or remove the trusted remote address, either allowing a malicious remote address or denying service to a trusted remote address. - Remove tokens that correspond to the `outboundAmount` without updating the `outboundAmount`, creating a discrepancy where it appears more tokens are locked in the source bridge than actually are. - Enable or disable the use of `sendAndCall()`. 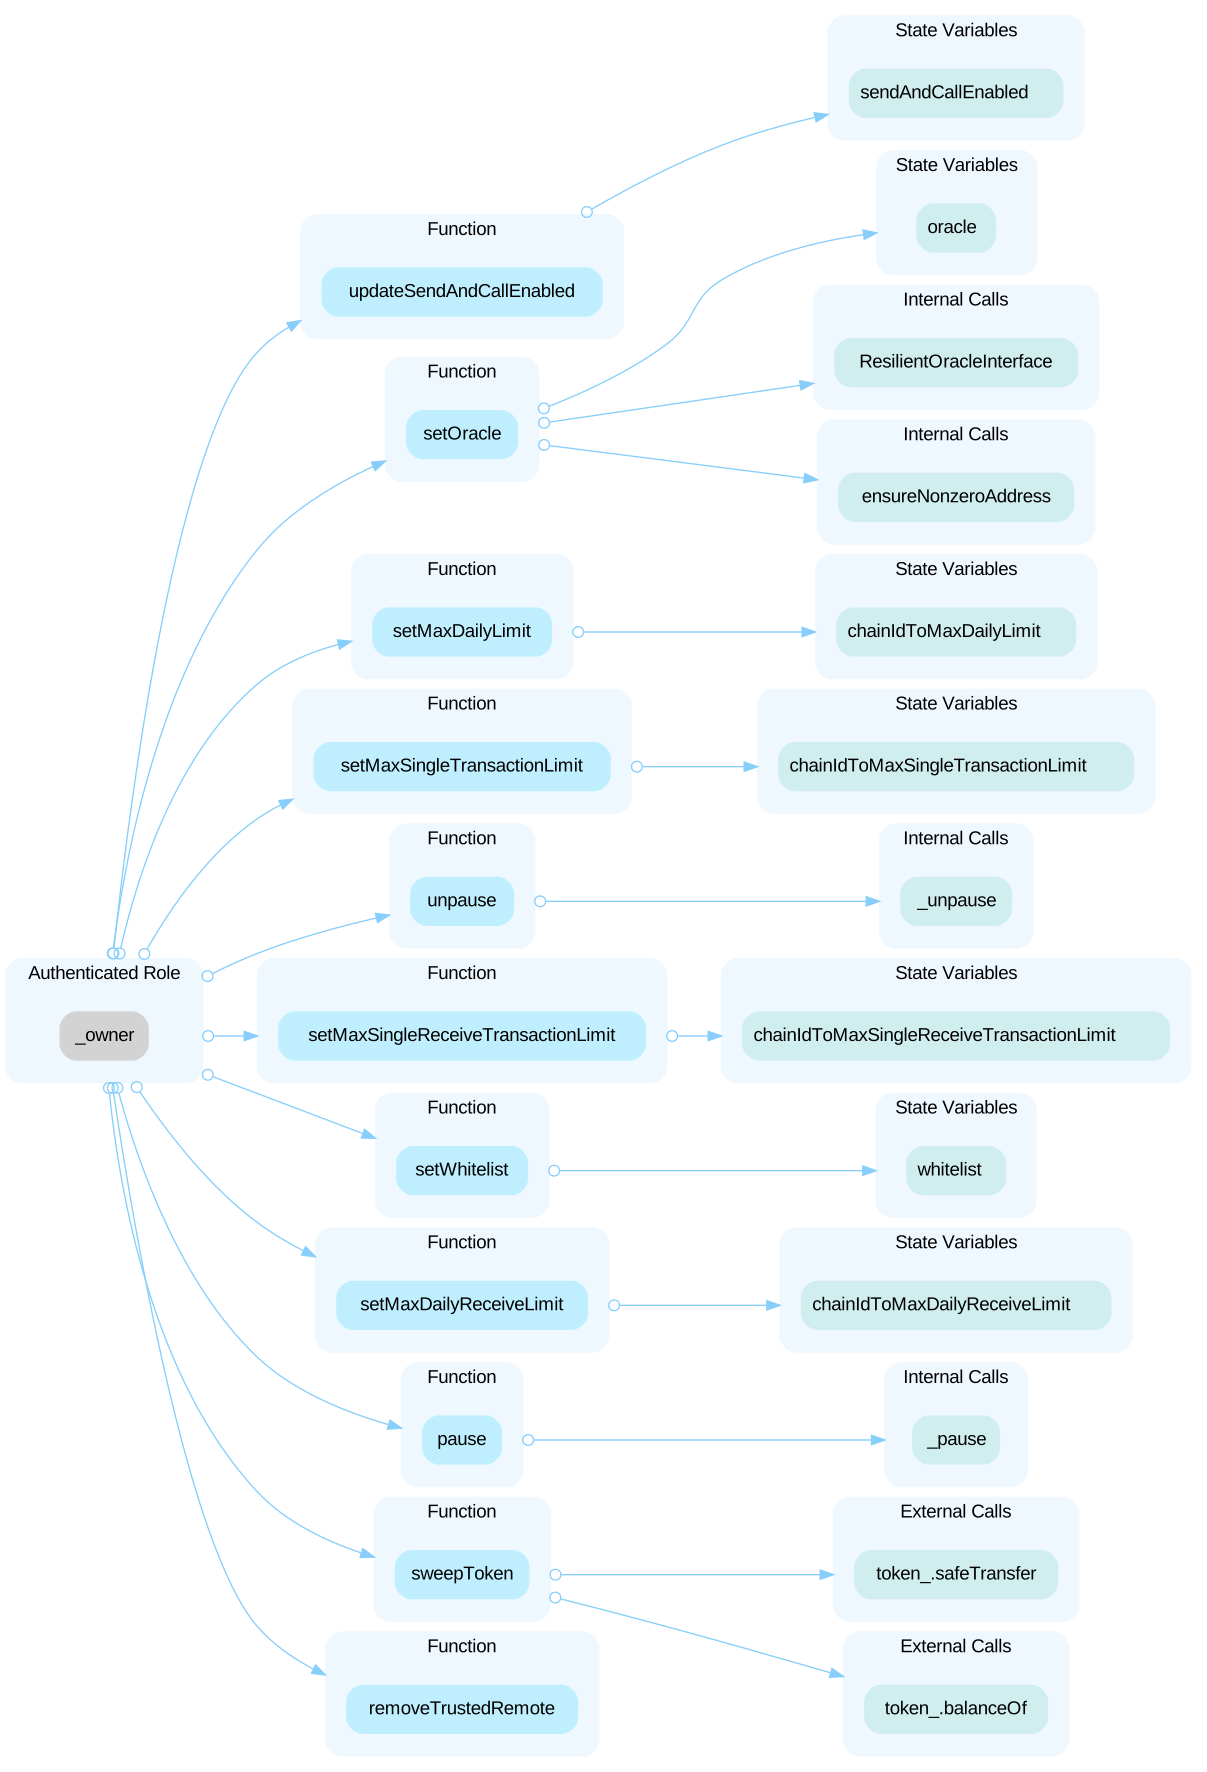 --- ### XVSBridgeAdmin In the contract `XVSBridgeAdmin` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and make a function signature active within the `functionRegistry` mapping in order to give their account access to this bridge logic through the privilege outlined below. 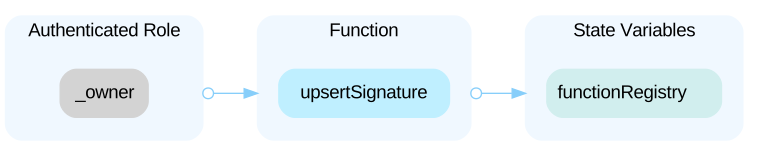 In the contract `XVSBridgeAdmin` the role `DEFAULT_ADMIN_ROLE` of the `AccessControlManager` can grant addresses the privilege to call the following functions: - Functions within the XVS Bridge via the `fallback()` function in `XVSBridgeAdmin` - `setTrustedRemoteAddress()` - `transferBridgeOwnership()` Any compromise to the `DEFAULT_ADMIN_ROLE` or accounts granted this privilege may allow the hacker to take advantage of this authority and do the following: - Call privileged functions that the `XVSBridgeAdmin` controls within the XVS Bridge, potentially allowing the hacker to steal funds locked in the bridge or using the bridge minting privilege to steal funds from a pool on one of the bridged chains. - Add a malicious trusted remote contract address in order to take steps to do the above. - Give an account they access the owner privilege of the bridge in order to access other functions so they can take steps to perform the above. --- ### XVSProxyOFTDest In the contract `XVSProxyOFTDest` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - Remove a failed message from the system so that it cannot be retried. 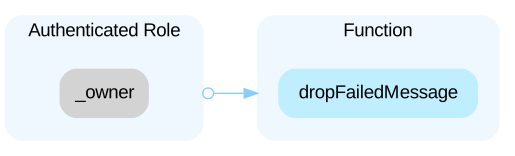 --- ### XVSProxyOFTSrc In the contract `XVSProxyOFTSrc` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - Remove a failed message from the system so that it cannot be retried. - Remove any amount of XVS funds currently held by the contract. - Use the function to inaccurately update the `outboundAmount` through a combination of calls to `sweepToken()` and `fallbackDeposit()`. This may cause a discrepancy where the `outboundAmount` is far larger than the balance the contract actually holds. 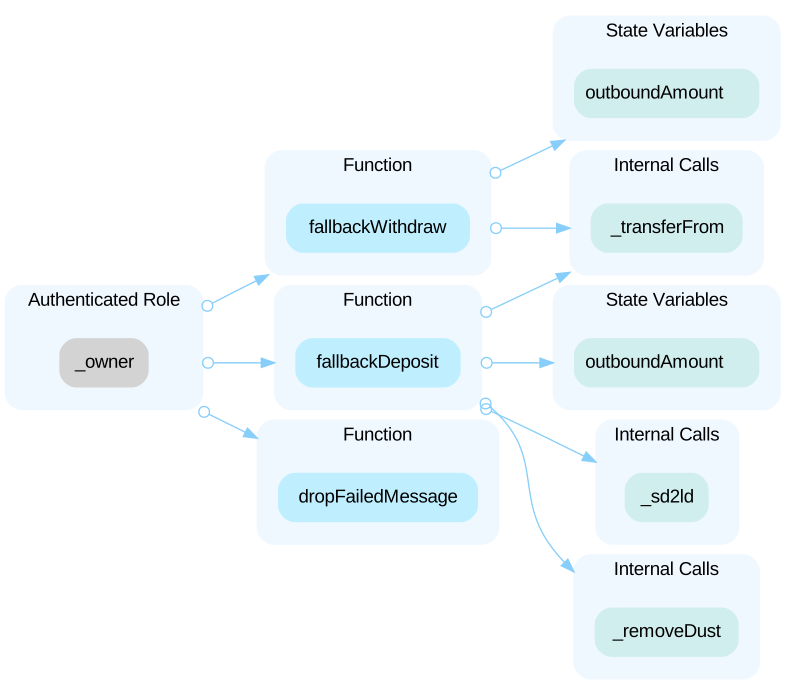 --- ### TokenController In the contract `TokenController` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the `accessControlManager` to an address they control so that they can make updates via the functions outlined below. 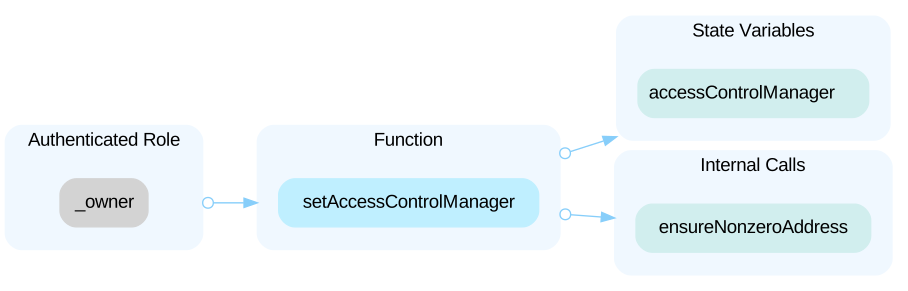 In the contract `TokenController`, the role `DEFAULT_ADMIN_ROLE` of the `AccessControlManager` can grant addresses the privilege to call the following functions: - `pause()` - `unpause()` - `updateBlacklist()` - `setMintCap()` - `migrateMinterTokens()` Any compromise to the `DEFAULT_ADMIN_ROLE` or accounts granted this privilege may al
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (8)
- contracts/Bridge/XVSProxyOFTDest.sol
- contracts/Bridge/token/XVS.sol
- contracts/Bridge/token/TokenController.sol
- contracts/Bridge/interfaces/IXVSProxyOFT.sol
- contracts/Bridge/BaseXVSProxyOFT.sol
- contracts/Bridge/XVSProxyOFTSrc.sol
- contracts/Bridge/interfaces/IXVS.sol
- contracts/Bridge/XVSBridgeAdmin.sol
Part of Venus Protocol’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us