Ducatus Wallet - Pentest
CertiK reviewed ducatus.com (Ducatus Wallet - Pentest) on 25 Apr 2024: 5 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 1 | 0 | 0 |
| Low | 3 | 0 | 0 |
HighSensitive Wallet Information Disclosed in MemoryOpen
The wallet by default stores the private key and the mnemonics for each wallet in plain text. The mnemonics for the backed up wallets are also available in memory in plain text. 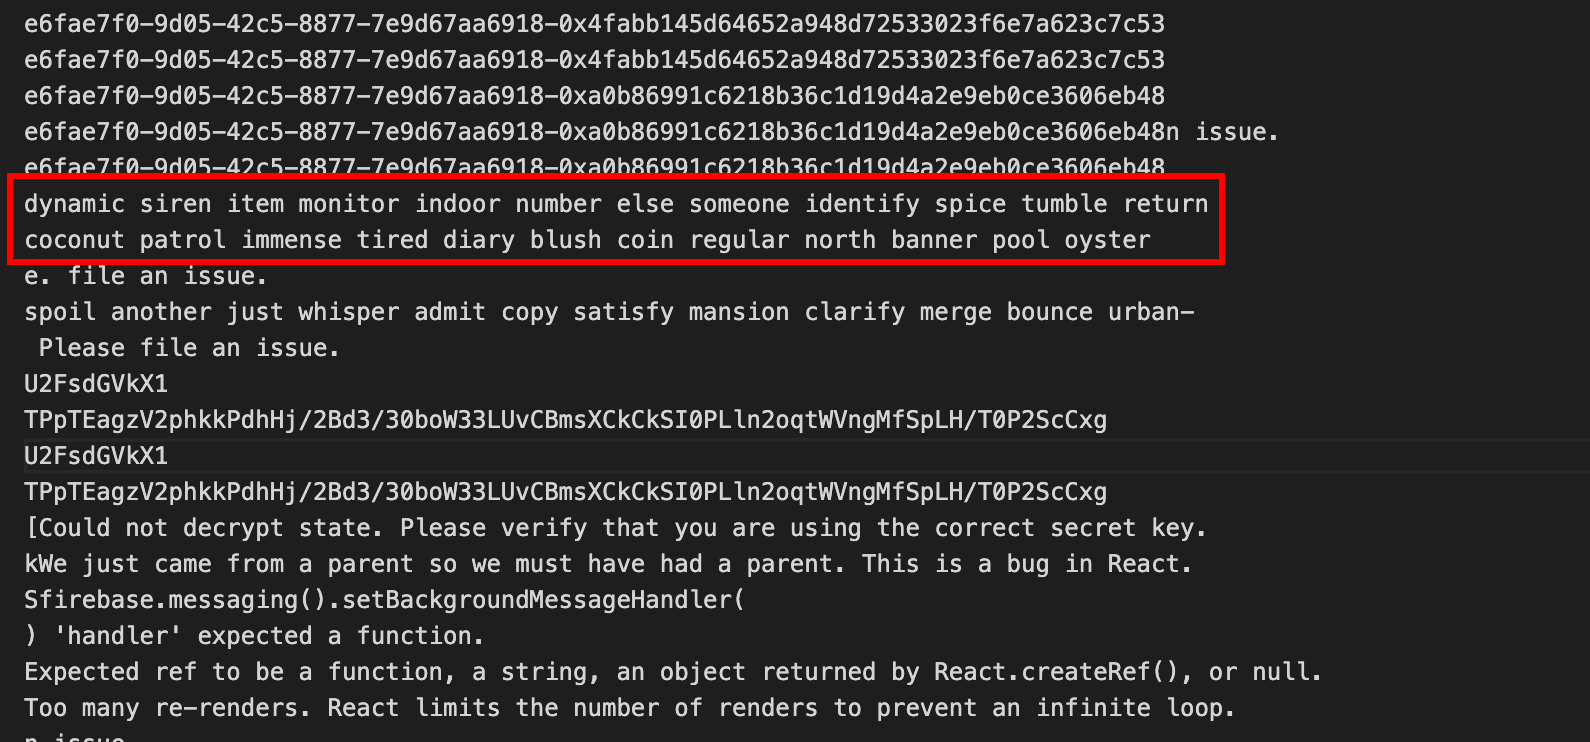 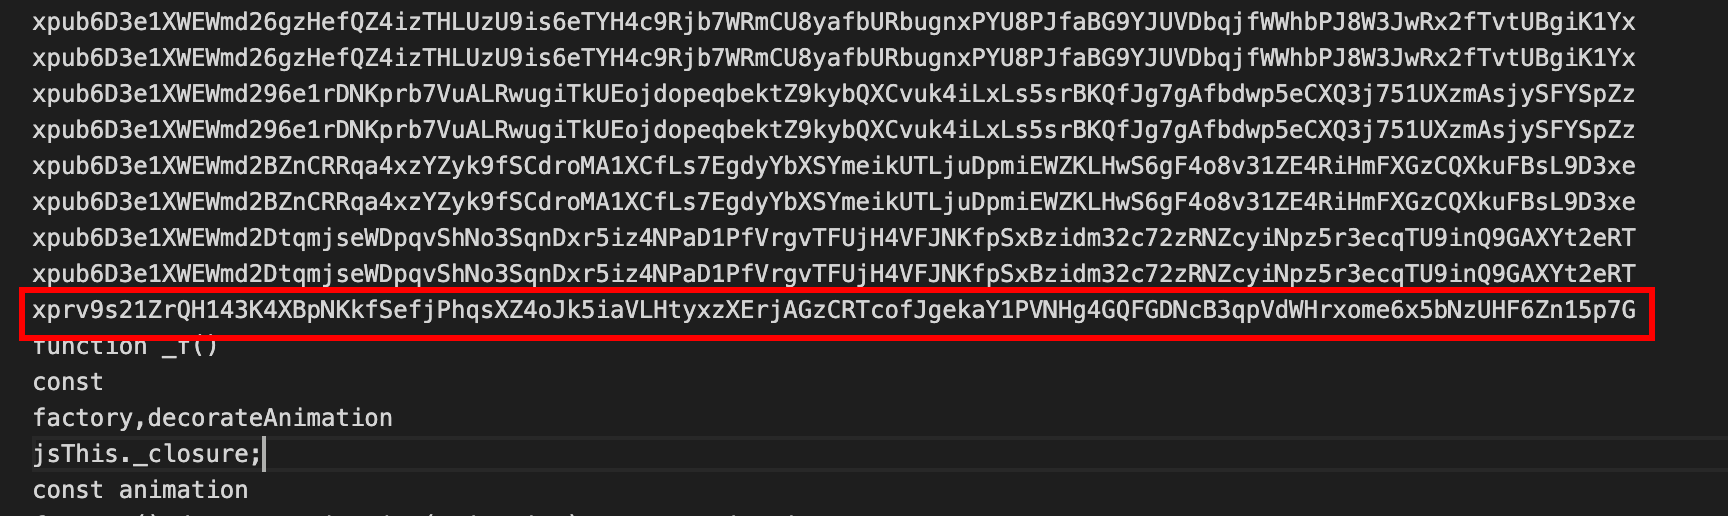 The option to encrypt the private key using a password is provided, but even after encrypting with the password, the password, the mnemonic and the private key can be found in the memory of the application. 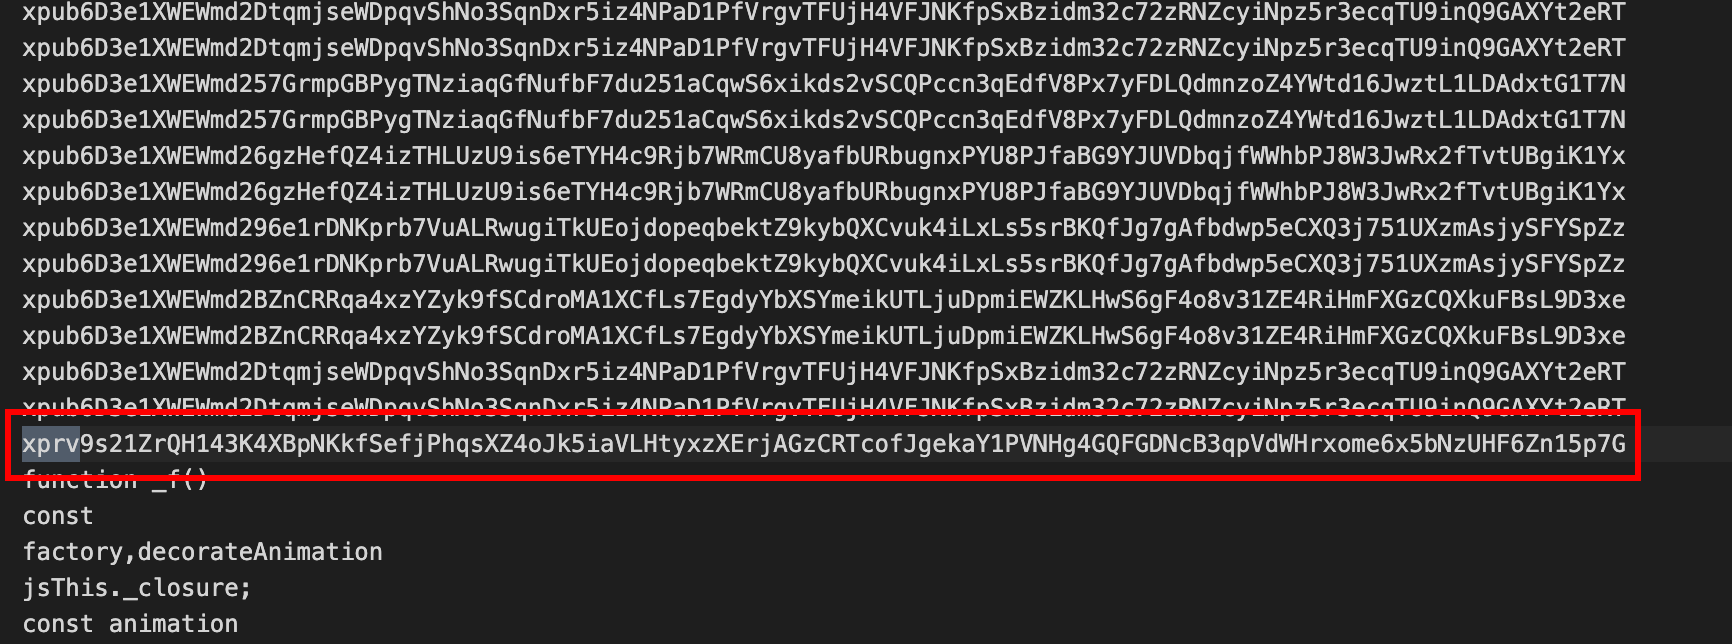 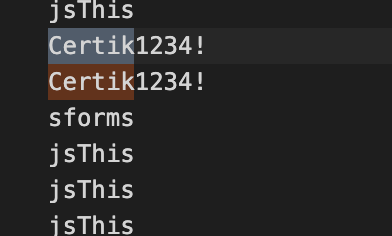 After reviewing the code, the component which handles the private key seems to store the private key in the class memory. This leads to the private key being globally available. The private key is only set to null when it is encrypted, upon decryption, the global variable `xPrivKey` is set to the plain text private key. 
MediumUnsafe DependenciesOpen
Some of the dependencies used on the project are unmaintained and have high-risk security vulnerabilities. The usage of [sjcl](https://github.com/bitwiseshiftleft/sjcl), which has not been updated for over 5 years, may expose the application to timing attacks. (https://github.com/bitwiseshiftleft/sjcl/issues/438) The code available does not seem to make use of Elliptic Curve cryptography but the timing attacks may occur in other functions of the library as well. It is recommended to use the standard Crypto library for Node.js (https://nodejs.org/api/crypto.html) to perform cryptographic operations, as this provides protection against timing attacks. It was also observed that the project uses outdated dependencies with known vulnerabilities. Below is a list: - lodash 4.17.20 - https://www.cve.org/CVERecord?id=CVE-2021-23337 - loader-utils 1.4.0 - https://www.cve.org/CVERecord?id=CVE-2022-37601 - ajv 6.12.0 - https://www.cve.org/CVERecord?id=CVE-2020-15366 - async 2.6.3 - https://www.cve.org/CVERecord?id=CVE-2021-43138 - semver 6.3.0 - https://www.cve.org/CVERecord?id=CVE-2022-25883
LowLack of SSL PinningOpen
Certificate pinning is the process of associating the backend server with a particular X.509 certificate or public key instead of accepting any certificate signed by a trusted certificate authority. After storing ("pinning") the server certificate or public key, the mobile app will subsequently connect to the known server only. Withdrawing trust from external certificate authorities reduces the attack surface (after all, there are many cases of certificate authorities that have been compromised or tricked into issuing certificates to impostors). The certificate can be pinned and hardcoded into the app or retrieved at the time the app first connects to the backend. In the latter case, the certificate is associated with ("pinned" to) the host when the host is seen for the first time. This alternative is less secure because attackers intercepting the initial connection can inject their own certificates.
LowLogging of Sensitive InformationOpen
The application's `signFreeze` in `deposit.effects.ts` function is currently configured to log out the user's private WIF key in plain text. This logging statement was found within the function's implementation, posing a security risk regarding confidential data handling and storage. It is not clear if this log is also being saved on the filesystem. ```typescript=28 const privateWifKey = (await dispatch<any>( getWifPrivKey(wallet, addressPath ? address?.path! : data.private_path), )) as any; dispatch(LogActions.info('[privateWifKey]:', privateWifKey)); ```
LowMissing Jailbreak detectionOpen
Jailbreak detection mechanisms are added to reverse engineering defense to make running the app on a jailbroken device more difficult. This blocks some of the tools and techniques reverse engineers like to use. Like most other types of defense, jailbreak detection is not very effective by itself, but scattering checks throughout the app's source code can improve the effectiveness of the overall anti-tampering scheme. It was observed that the iOS application does not adequately detect if the device is jailbroken. As a result, the data which is stored via the iOS application can be exposed when the device that is jailbroken.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of ducatus.com’s security record
 ducatus.com
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us