Ignore Fud Bridge
CertiK reviewed 4. Ignore Fud (Ignore Fud Bridge) on 16 May 2023: 8 findings, 0 critical; 6 marked fixed, 1 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 4 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 1 | 0 |
HighPotential Rug Pull Risks Introduced by CentralizeOpen
In the contract `LzApp` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set configuration of the LayerZero endpoint - set the send version of the LayerZero endpoint - set the receive version of the LayerZero endpoint - resume the message flow in blocking mode and clear the stored payload - set the trusted path for the cross-chain communication - set the trusted remote address - set precrime - set the minimum gas parameter for a packet type on a given chain - set payload size limit 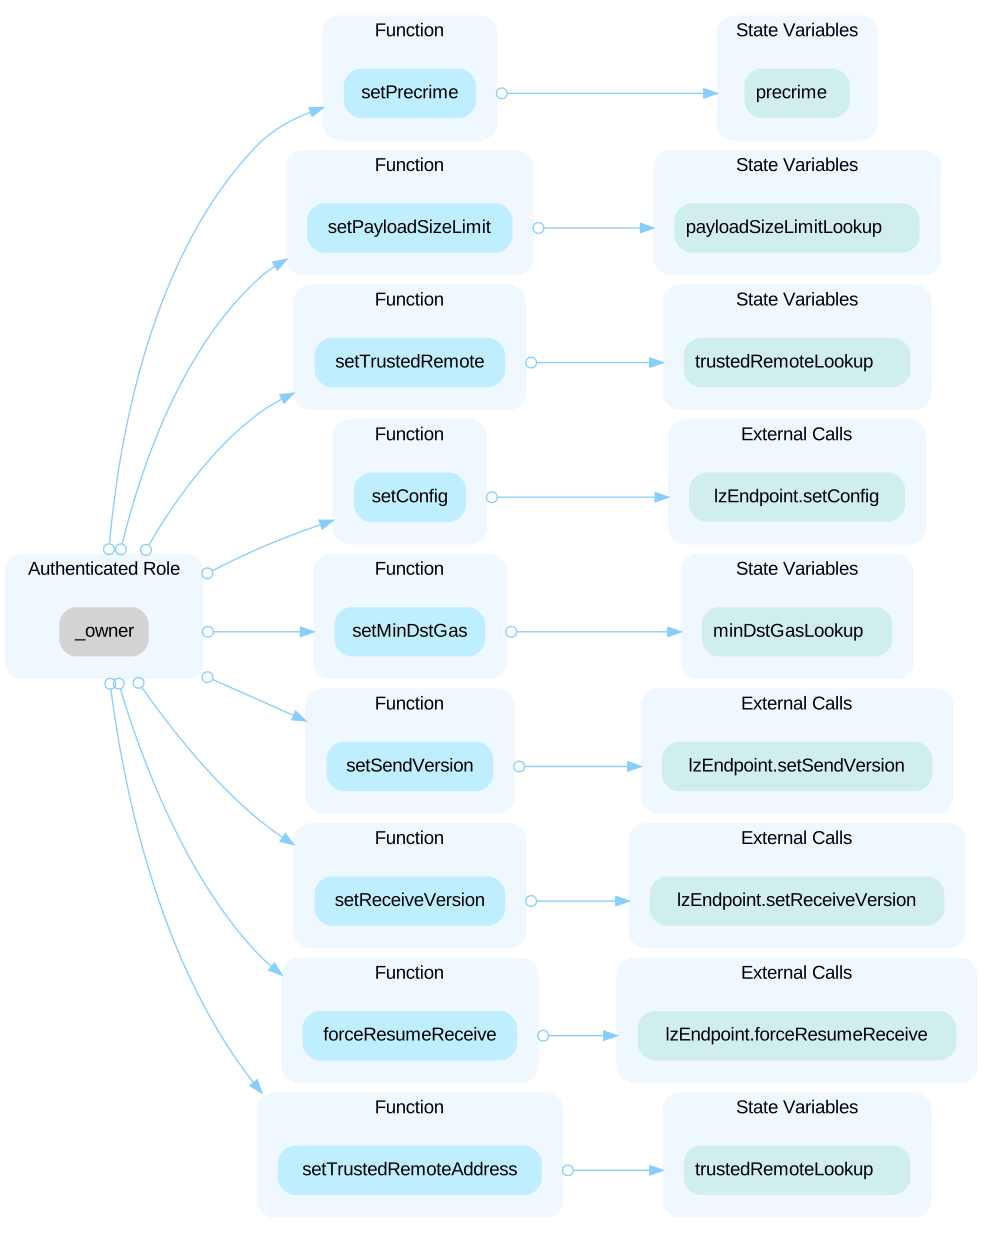 In the contract `TokenBridgeBase` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set the `useCustomAdapterParams` flag indicating whether the contract uses custom adapter parameters or the default ones 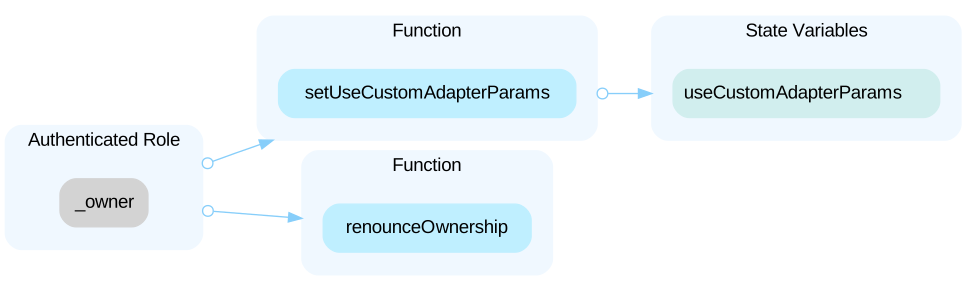 In the contract `WrappedTokenBridge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - register a token supported in this bridge - set withdrawal fee bps 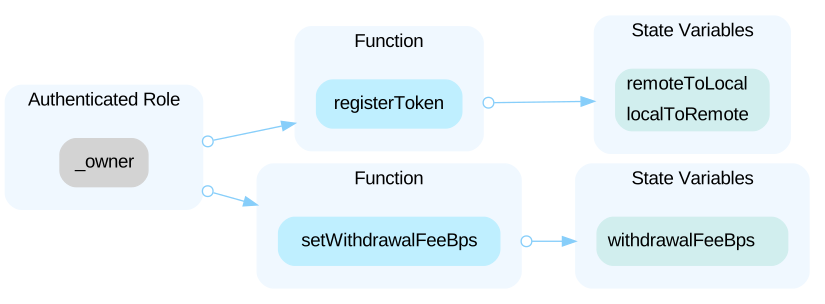 In the contract `OriginalTokenBridge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - register a token supported in this bridge and set the decimals - set remote chain id - withdraw fee from the contract 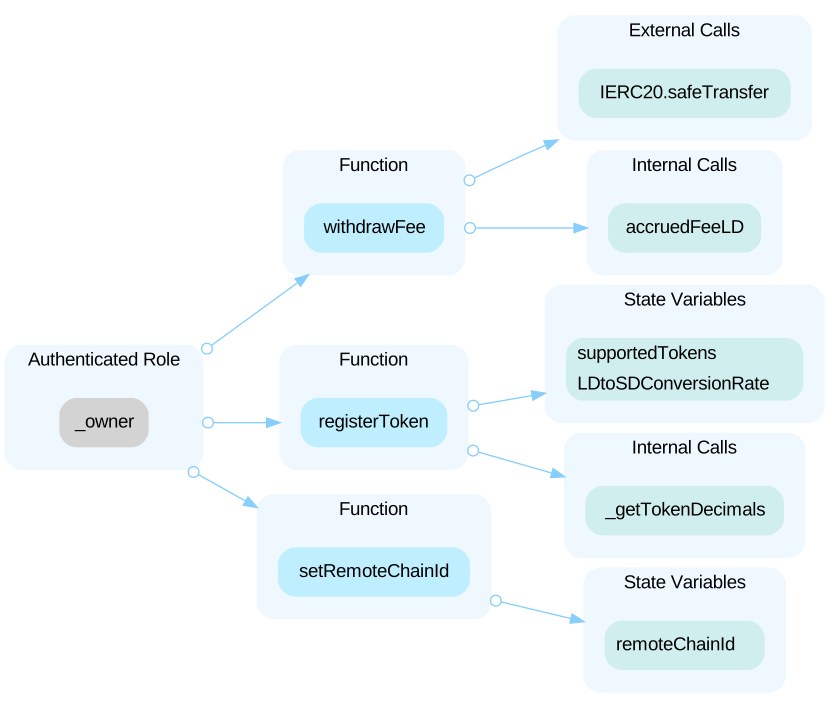 **Improper configuration of the above bridge parameters could compromise the functionality of the bridge, obstruct message transmission, or even result in the lockout or theft of users' funds.** **More details can be found in finding OTB-02 and OTB-04, **
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x04cbefb3d208172336f74448d529148b429d4d7f | Chain: BNB Chain | Source code: Verified source |
Part of 4. Ignore Fud’s security record
 4. Ignore Fud
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us