
4. Ignore Fud security record
As of 3 Nov 2026, 4. Ignore Fud has 1 audit report on Trustblock, by CertiK, dated 16 May 2023. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Ignore Fud Bridge | Security firm: CertiK | Date: | Scope: 1 address on BNB Chain | No open critical findings | Open · skynet.certik.com |
Findings8
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 4 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 1 | 0 |
HighPotential Rug Pull Risks Introduced by CentralizeIgnore Fud Bridge · CertiK · 16 May 2023Open
In the contract `LzApp` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set configuration of the LayerZero endpoint - set the send version of the LayerZero endpoint - set the receive version of the LayerZero endpoint - resume the message flow in blocking mode and clear the stored payload - set the trusted path for the cross-chain communication - set the trusted remote address - set precrime - set the minimum gas parameter for a packet type on a given chain - set payload size limit 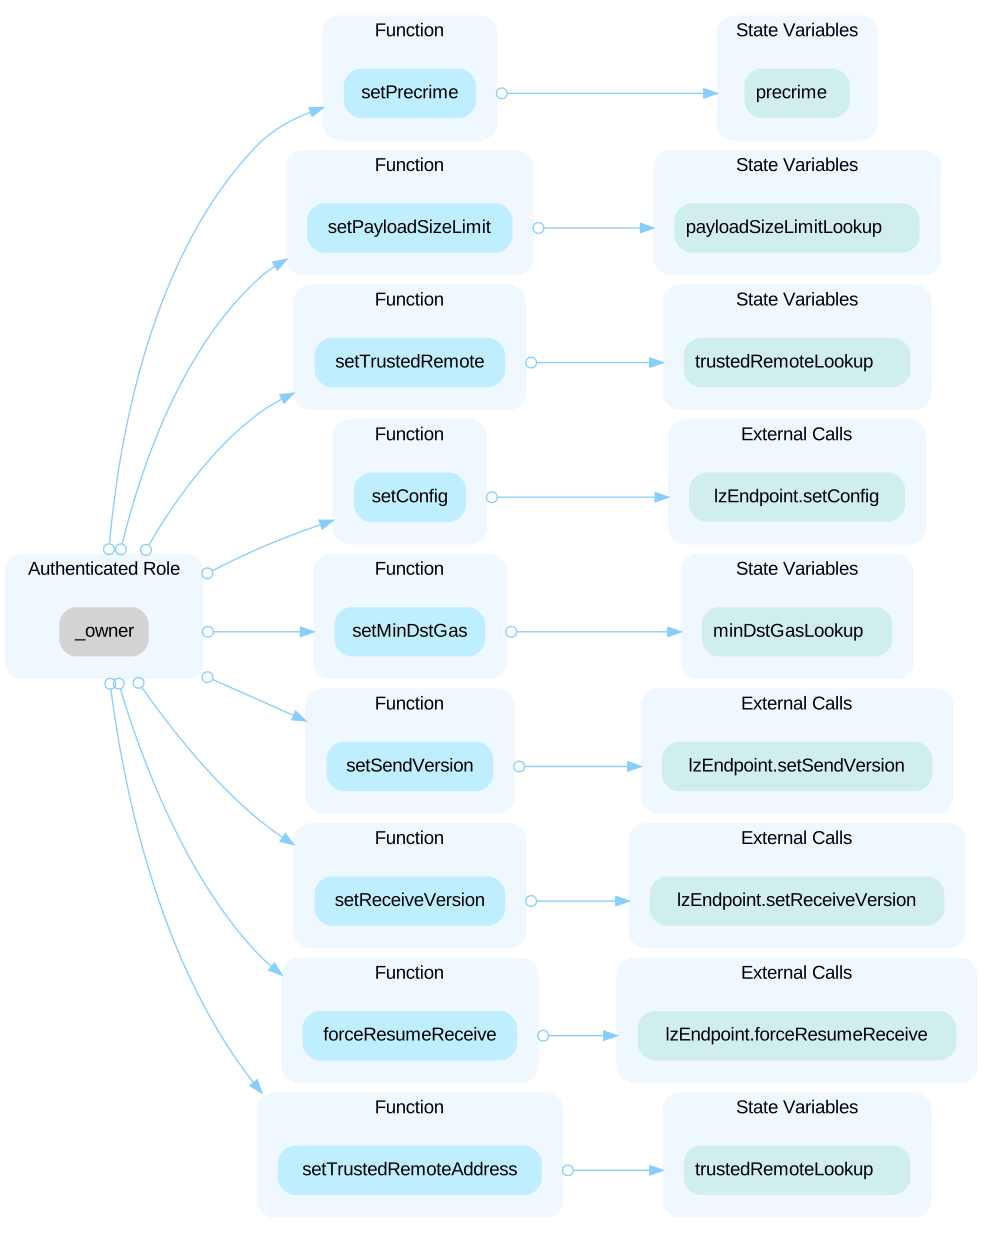 In the contract `TokenBridgeBase` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set the `useCustomAdapterParams` flag indicating whether the contract uses custom adapter parameters or the default ones 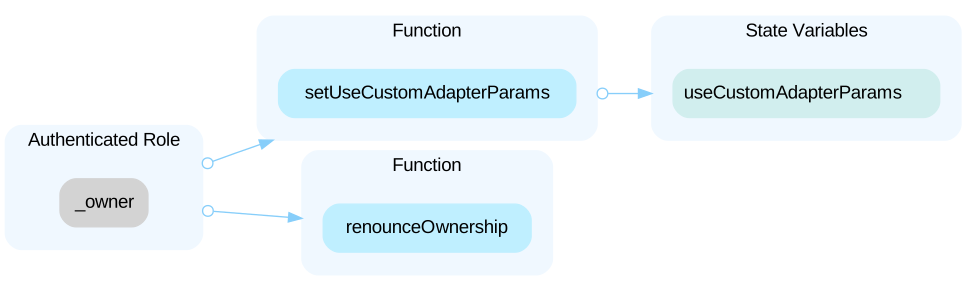 In the contract `WrappedTokenBridge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - register a token supported in this bridge - set withdrawal fee bps 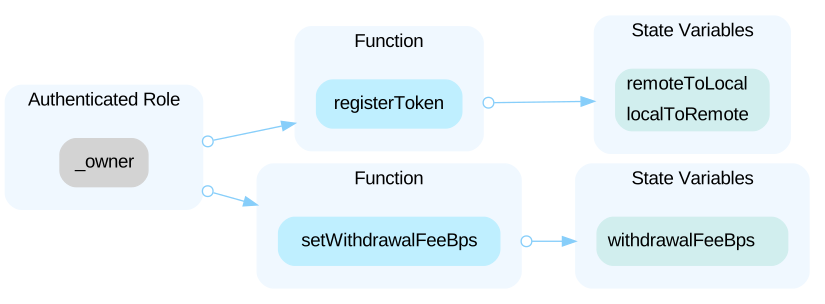 In the contract `OriginalTokenBridge` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - register a token supported in this bridge and set the decimals - set remote chain id - withdraw fee from the contract 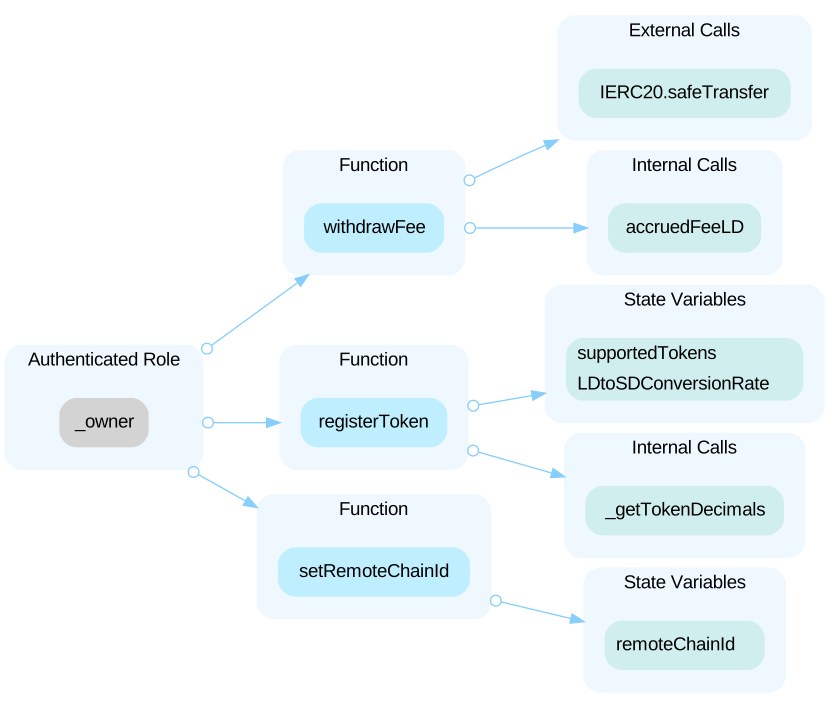 **Improper configuration of the above bridge parameters could compromise the functionality of the bridge, obstruct message transmission, or even result in the lockout or theft of users' funds.** **More details can be found in finding OTB-02 and OTB-04, **
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x04cbefb3d208172336f74448d529148b429d4d7f | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="ignore-fud"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us