Venus - Native Token Gateway
Part of CertiK’s series
CertiK reviewed Venus Protocol (Venus - Native Token Gateway) on 26 Feb 2024: 8 findings, 0 critical; 7 marked fixed, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 0 | 5 |
HighCentralization Related RisksOpen
Note that any centralization risks present in the existing codebase before the PR's in scope of this audit were not considered. Only those added to the in-scope PRs are addressed. We recommend all users carefully review the centralization risks, much of which can be found in our previous audits, which can be found here: [https://skynet.certik.com/projects/venus](https://skynet.certik.com/projects/venus). In the contract `NativeTokenGateway` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer any wrappedNativeToken or native token held by the contract to themselves. 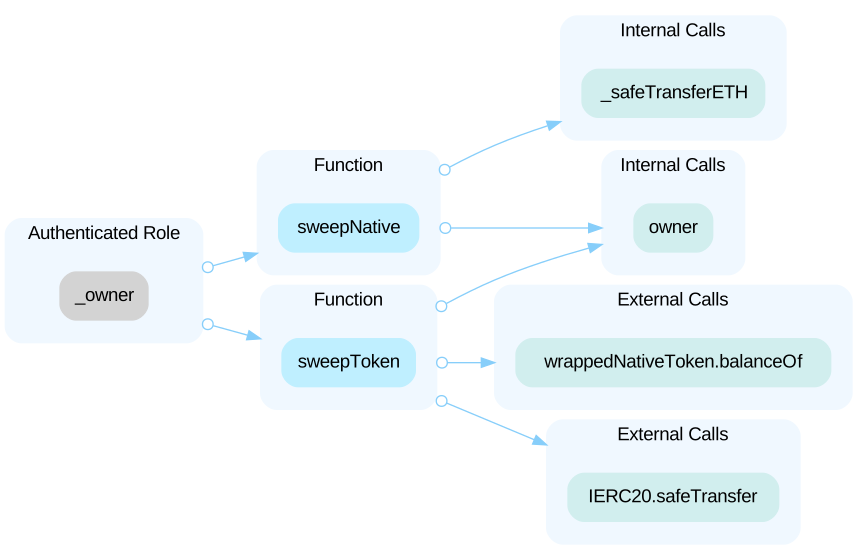
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (10)
- contracts/Tokens/VTokens/VToken.sol
- contracts/Gateway/Interfaces/IVtoken.sol
- contracts/ComptrollerStorage.sol
- contracts/Tokens/VTokens/VBep20.sol
- contracts/VTokenInterfaces.sol
- contracts/Gateway/INativeTokenGateway.sol
- contracts/Comptroller.sol
- contracts/Gateway/NativeTokenGateway.sol
- contracts/Gateway/Interfaces/IWrappedNative.sol
- contracts/VToken.sol
Part of Venus Protocol’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us