Beincom - Audit
CertiK reviewed Beincom (Beincom - Audit) on 2 Aug 2024: 5 findings, 0 critical; 2 marked fixed, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 2 | 0 | 2 |
HighCentralization Risks in BicTokenPaymaster.solOpen
In the contract `BicTokenPaymaster` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and block/unblock any address, change the Oracle and Factory address, pause/unpause token transfers, and mint large amount of tokens to affiliated addresses. Additionally, the `constructor()` of the contract approves maximum tokens to the `owner` address, who can withdraw tokens from the contract, which comes from users' payment for transaction gas cost. Such privilege is preserved in the `transferOwnership()` function. 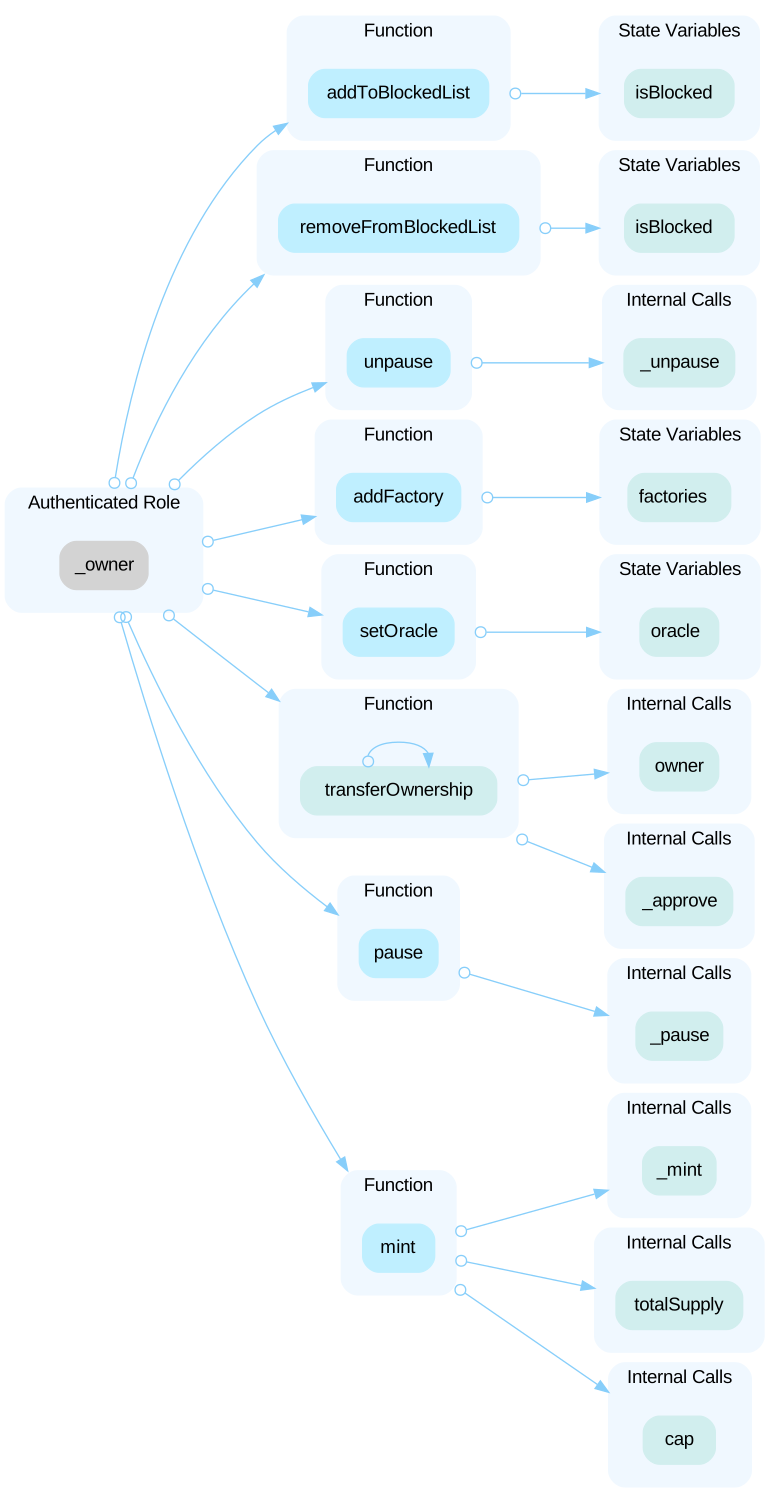
LowInheritance of ERC20 in the `BicTokenPaymaster` COpen
The `BicTokenPaymaster` contract inherits both the `BasePaymaster` and `ERC20Votes` contracts, instead of using an external ERC20 token as a passed in parameter for users to compensate the pay master for sponsoring the gas fee.
LowThird-Party DependenciesOpen
The `BicTokenPaymaster` contract is serving as the underlying entity to interact with third-party or out-of-scope contracts, including but is not limited to: `Oracle`, `factory`, and other contracts in the Account Abstraction workflow such as the `Entrypoint` contract and the `BicAccount` contract. The scope of the audit treats third-party and out-of-scope entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. For example, if the `Oracle` returns incorrect pricing info, users might overpay the token relative to the cost of actual gas spent for a `UserOp` transaction. If the `BicAccount` contract does not have proper signature verification, then the `BicTokenPaymaster` contract might force transfer the token from a compromised `BicAccount` contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/token/BicTokenPaymaster.sol
Part of Beincom’s security record
 Beincom
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us