
Beincom security record
As of 25 Oct 2026, Beincom has 3 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 19 Mar 2025. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits3
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Beincom - Audit 3 | Security firm: CertiK | Date: | Scope: Repository at commit 221ff14 | No open critical findings | Open · skynet.certik.com |
| Beincom - Audit 2 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Beincom - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings28
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 4 | 0 |
| Medium | 0 | 2 | 3 |
| Low | 5 | 0 | 12 |
HighCentralization Risks in BicRedeemFactory.solBeincom - Audit 2 · CertiK · 12 Sep 2024Open
In the contract `BicRedeemFactory`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and create a redeem token and schedule for any arbitrary address. 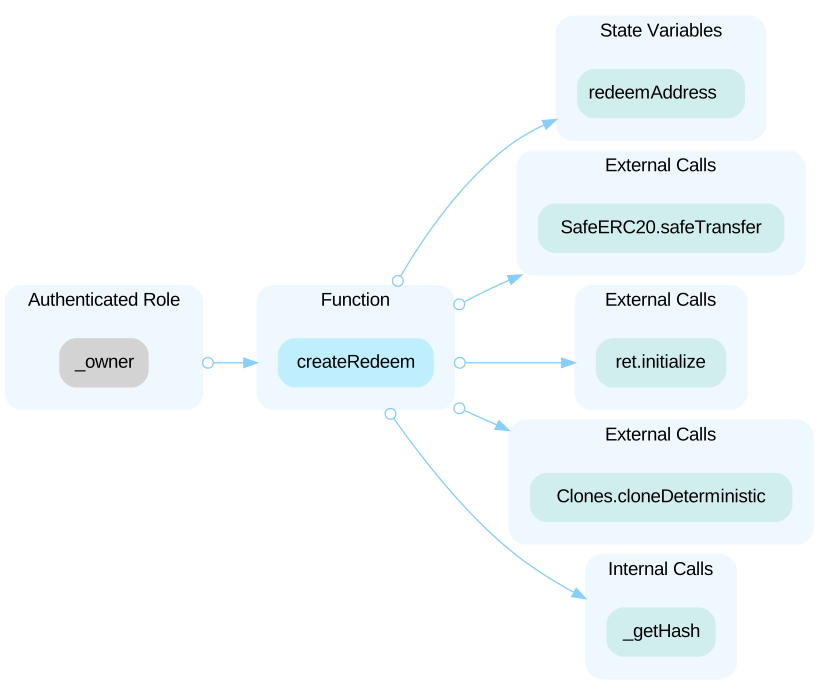
Open the reportHighCentralization Risks in BicTokenPaymaster.solBeincom - Audit · CertiK · 2 Aug 2024Open
In the contract `BicTokenPaymaster` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and block/unblock any address, change the Oracle and Factory address, pause/unpause token transfers, and mint large amount of tokens to affiliated addresses. Additionally, the `constructor()` of the contract approves maximum tokens to the `owner` address, who can withdraw tokens from the contract, which comes from users' payment for transaction gas cost. Such privilege is preserved in the `transferOwnership()` function. 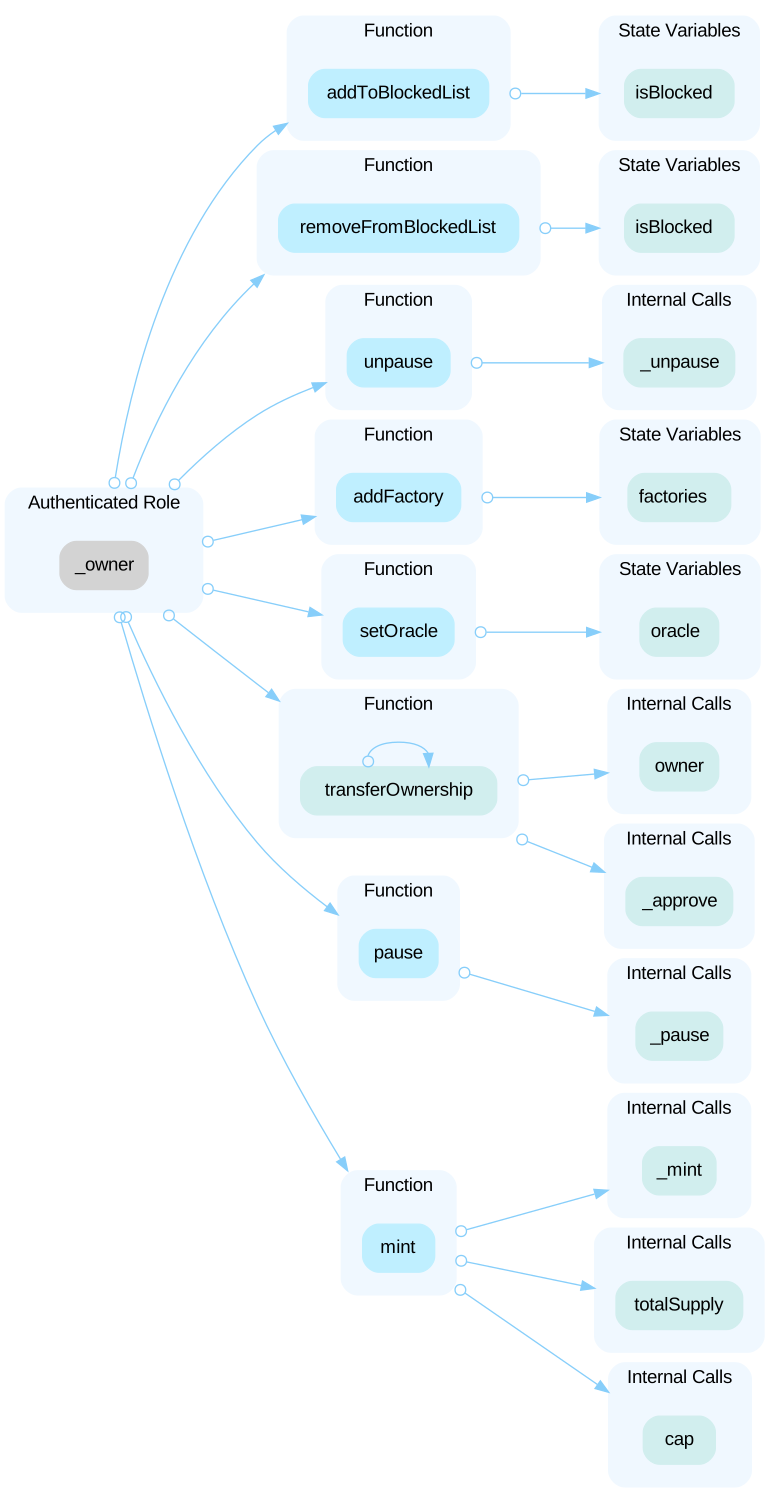
Open the reportLowERC-4337 is a Draft EIPBeincom - Audit 3 · CertiK · 19 Mar 2025Open
The contract `BicTokenPaymaster` is implementing the [ERC-4337](https://eips.ethereum.org/EIPS/eip-4337). This EIP is a draft and as a consequence: > "This EIP is not yet recommended for general use or implementation, as it is subject to normative (breaking) changes." Being a draft, ERC-4337 is still undergoing revisions and has not achieved final consensus within the Ethereum community. This status means that the standard may experience significant modifications, potentially affecting the compatibility and security of implementations relying on it.
Open the reportLowPotential Sandwich AttacksBeincom - Audit 3 · CertiK · 19 Mar 2025Open
A sandwich attack can occur when an attacker notices a transaction involving token swaps or liquidity additions that lack slippage restrictions or minimum output amount settings. The attacker can exploit this by frontrunning the transaction to purchase one of the assets, thereby manipulating the exchange rate, and then backrunning the transaction to sell the asset for a profit. The referenced functions are invoked without setting slippage restrictions or minimum output amounts, making transactions that trigger these functions particularly vulnerable to sandwich attacks, especially when large input amounts are involved.
Open the reportLowLack of Prevention to Metamorphic Contract DeployBeincom - Audit 2 · CertiK · 12 Sep 2024Open
The `BicFactory` contract uses `CREATE2` for deploying contracts, which can lead to a vulnerability where an initially harmless contract can be replaced with a malicious one at the same address using the `selfdestruct` function followed by re-deployment. This metamorphic behavior could deceive users into interacting with a malicious contract, thinking it is still the original, benign contract. By utilizing non-deterministic initialization code, contracts can suddenly mutate in-place and swap in arbitrary bytecode. As one example of non-determinism, the initialization code could call in to some external contract with mutable storage and use the returned data to construct the final bytecode.
Open the reportLowInheritance of ERC20 in the `BicTokenPaymaster` CBeincom - Audit · CertiK · 2 Aug 2024Open
The `BicTokenPaymaster` contract inherits both the `BasePaymaster` and `ERC20Votes` contracts, instead of using an external ERC20 token as a passed in parameter for users to compensate the pay master for sponsoring the gas fee.
Open the reportLowThird-Party DependenciesBeincom - Audit · CertiK · 2 Aug 2024Open
The `BicTokenPaymaster` contract is serving as the underlying entity to interact with third-party or out-of-scope contracts, including but is not limited to: `Oracle`, `factory`, and other contracts in the Account Abstraction workflow such as the `Entrypoint` contract and the `BicAccount` contract. The scope of the audit treats third-party and out-of-scope entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. For example, if the `Oracle` returns incorrect pricing info, users might overpay the token relative to the cost of actual gas spent for a `UserOp` transaction. If the `BicAccount` contract does not have proper signature verification, then the `BicTokenPaymaster` contract might force transfer the token from a compromised `BicAccount` contract.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="beincom"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us