Beincom - Audit 2
CertiK reviewed Beincom (Beincom - Audit 2) on 12 Sep 2024: 3 findings, 0 critical; 1 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 1 |
HighCentralization Risks in BicRedeemFactory.solOpen
In the contract `BicRedeemFactory`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and create a redeem token and schedule for any arbitrary address. 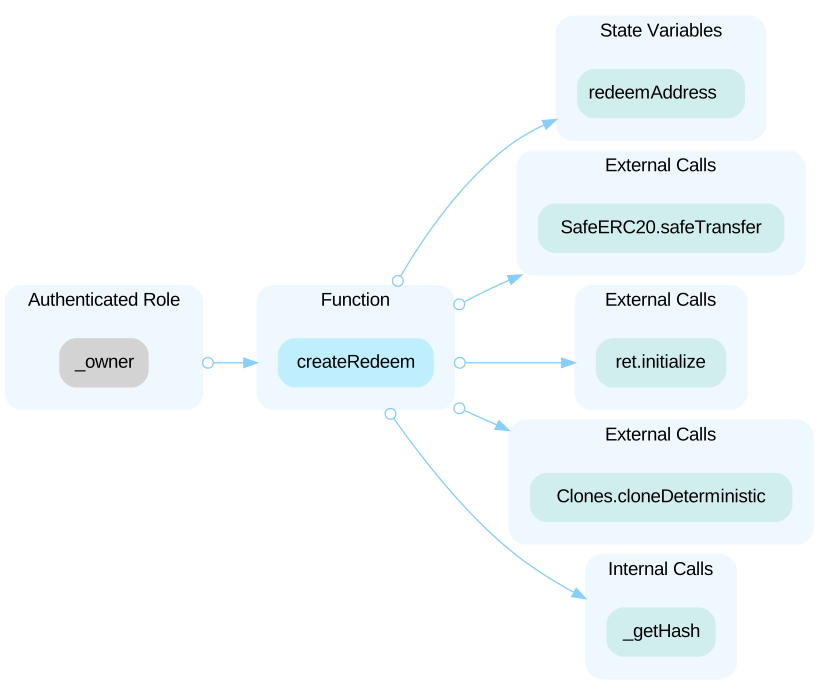
LowLack of Prevention to Metamorphic Contract DeployOpen
The `BicFactory` contract uses `CREATE2` for deploying contracts, which can lead to a vulnerability where an initially harmless contract can be replaced with a malicious one at the same address using the `selfdestruct` function followed by re-deployment. This metamorphic behavior could deceive users into interacting with a malicious contract, thinking it is still the original, benign contract. By utilizing non-deterministic initialization code, contracts can suddenly mutate in-place and swap in arbitrary bytecode. As one example of non-determinism, the initialization code could call in to some external contract with mutable storage and use the returned data to construct the final bytecode.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- contracts/infra/BicFactory.sol
- contracts/token-redeem/BicRedeemFactory.sol
- contracts/token-redeem/BicRedeemToken.sol
Part of Beincom’s security record
 Beincom
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us