
Beincom security record
As of 30 Oct 2026, Beincom has 3 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 19 Mar 2025. Those reports list no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Trustblock does not review code.
Audits3
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Beincom - Audit 3 | Security firm: CertiK | Date: | Scope: Repository at commit 221ff14 | No open critical findings | Open · skynet.certik.com |
| Beincom - Audit 2 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
| Beincom - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings28
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 4 | 0 |
| Medium | 0 | 2 | 3 |
| Low | 5 | 0 | 12 |
HighCentralization Related RisksBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
### BICVestingFactory In the contract `BICVestingFactory`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and create and initialize new redeem contracts with custom parameters. 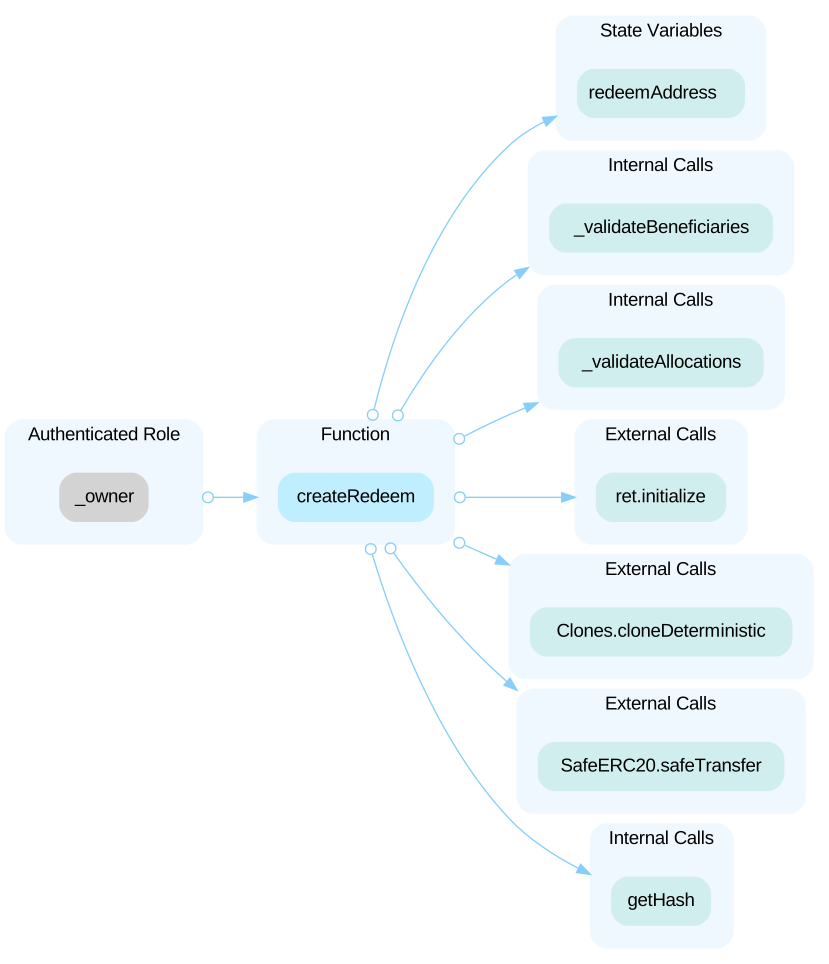 ----- ### MultiSigner In the contract `MultiSigner`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to an address they control, remove a signer, or add a signer. 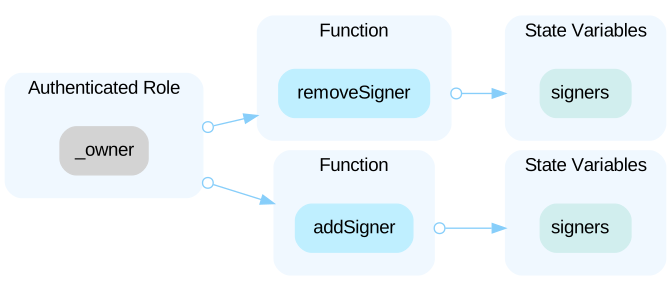 ----- ### TokenSingletonPaymaster In the contract `TokenSingletonPaymaster`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to an address they control, set the Oracle address to a malicious address, and add any address as a valid factory address. 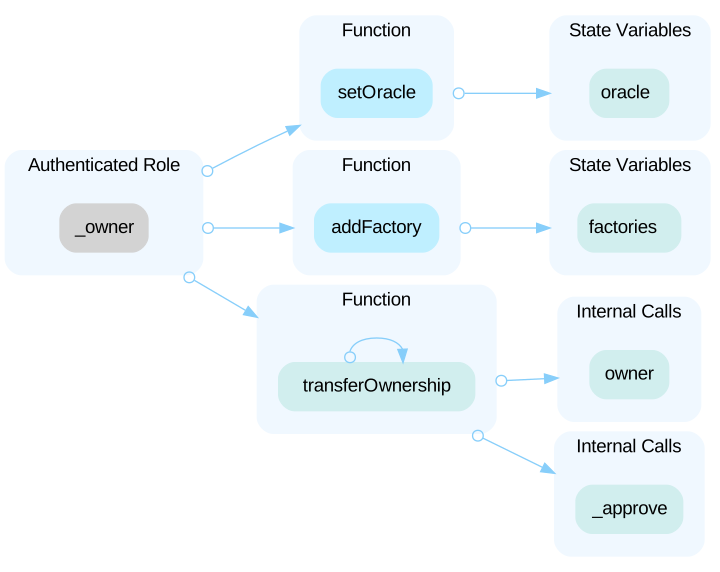 ----- ### BicTokenPaymaster In the contract `BicTokenPaymaster`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to an address they control, enable or disable pre-public status at any time, add or remove any address from the pre-public whitelist, set the pre-public rounds, set liquidity treasury address to receive LP tokens, block or unblock address status to prevent or allow an address to transfer tokens, set the liquidity fee limits, add or remove any address as a valid pool, change the LF period, the LF start time and the LF reduction value to interfere with the fee calculation, set swap back status and minimum swap back amount, grant or remove the privileged status `isExcluded` for multiple addresses, pause or unpause transfer for non-privileged addresses, withdraw any tokens and ETH to any address. 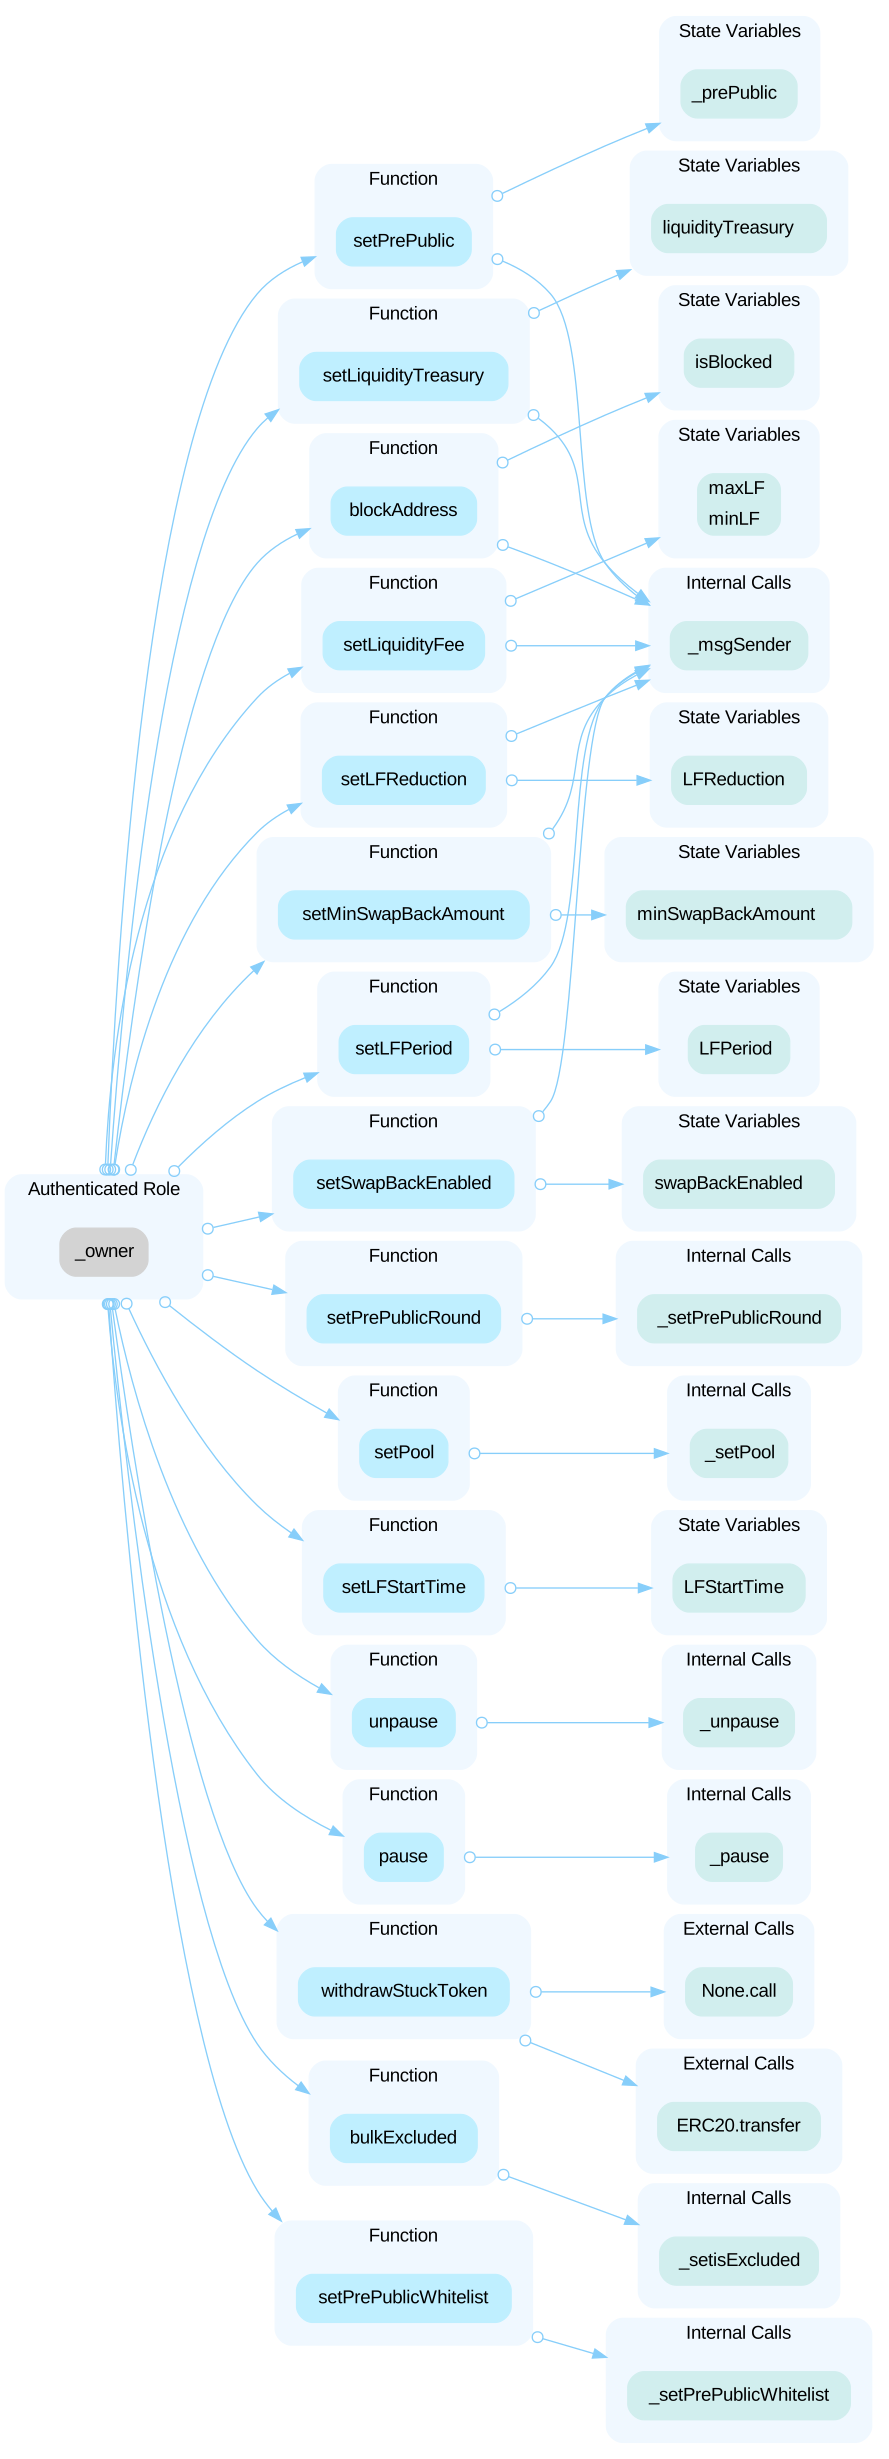
Open the reportHighCentralized Control of LP TokensBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
The contract design allows the owner of `liquidityTreasury` address, to control the LP (liquidity provider) tokens. \ This centralized control creates a significant risk if the private keys of the privileged role are compromised, as an could remove the liquidity from the pool and withdraw the LP tokens. Such actions could severely impact users and the protocol’s stability, as liquidity removal often results in token price manipulation and loss of trust in the system.
Open the reportHighInitial Token DistributionBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
All of the `BIC` tokens are sent to the `superController` address provided by the deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighUnrestricted Withdrawal of Accumulated Tokens inBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
The `withdrawStuckToken()` function enables the owner to withdraw any tokens (including ETH when `token == address(0)`) stored in the contract and transfer them to any address. While this might be intended for operational flexibility, it creates a risk if their private keys are compromised. Specifically, an attacker could withdraw tokens intended for liquidity or other purposes, potentially harming users and the protocol's integrity.
Open the reportMediumInadequate Oracle Management in `TokenSingletonPaBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
The `TokenSingletonPaymaster` relies exclusively on a single oracle (`oracle`) for token exchange rates in `getTokenValueOfEth`, but it lacks key safeguards: - The contract never checks the oracle's operational status. - Oracle responses are never verified for correctness. - There is no alternative mechanism if the oracle fails or returns invalid data. This single dependency introduces a risk of denial of service, and potential data integrity vulnerabilities, where invalid or manipulated oracle data could be exploited to affect token valuations or operations.
Open the reportMediumRounding Errors in Token ReleaseBeincom - Audit 3 · CertiK · 19 Mar 2025Acknowledged
The token allocation mechanism in the `BICVesting` contract uses percentages, which can lead to fairness issues due to rounding errors: 1. **Incomplete Allocations**: Allocations are not required to sum to 100%. Any remaining percentage is implicitly allocated to the final beneficiary, creating discrepancies between the expected and actual distributions. 2. **Rounding Discrepancies**: For small claimable amounts, rounding errors can result in zero distribution for all beneficiaries except the last one, who receives the entire claimable amount. Additionally to the fairness issue, this causes transparency issues as users reviewing allocations may not see accurate results due to the points above.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="beincom"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us