BlobToken-Audit
CertiK reviewed Blob DAO (BlobToken-Audit) on 26 Sep 2023: 12 findings, 0 critical; 6 marked fixed, 1 acknowledged, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 3 | 0 | 1 |
| Low | 0 | 1 | 4 |
HighCentralization Related RisksOpen
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce ownership and transfer ownership to any address. 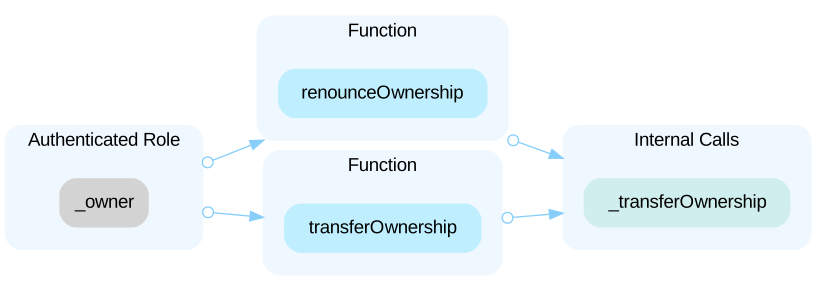 In the contract `ERC20Mod` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add/remove presale addresses, set deploy, and distribute tax. 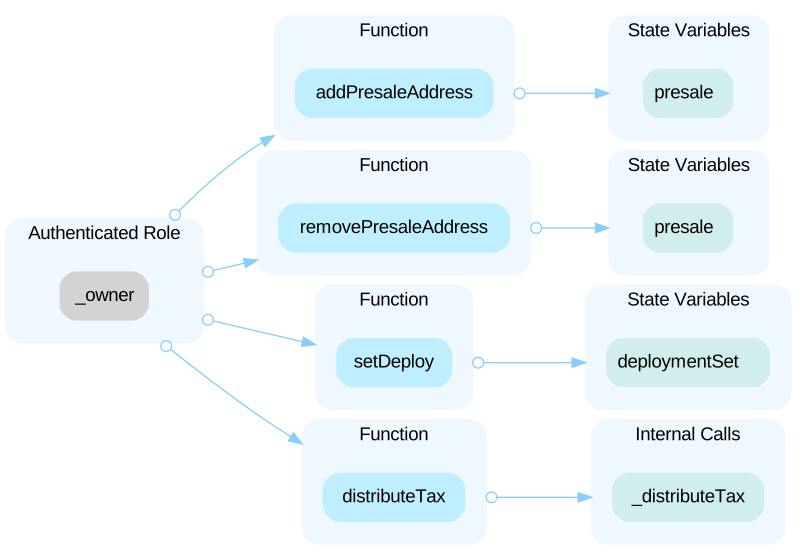 In the contract `Taxable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add/remove DEX addresses, add/update/remove Tax addresses, update threshold and tax, set priceFeed, reward and router addresses, add/remove tax exempts addresses 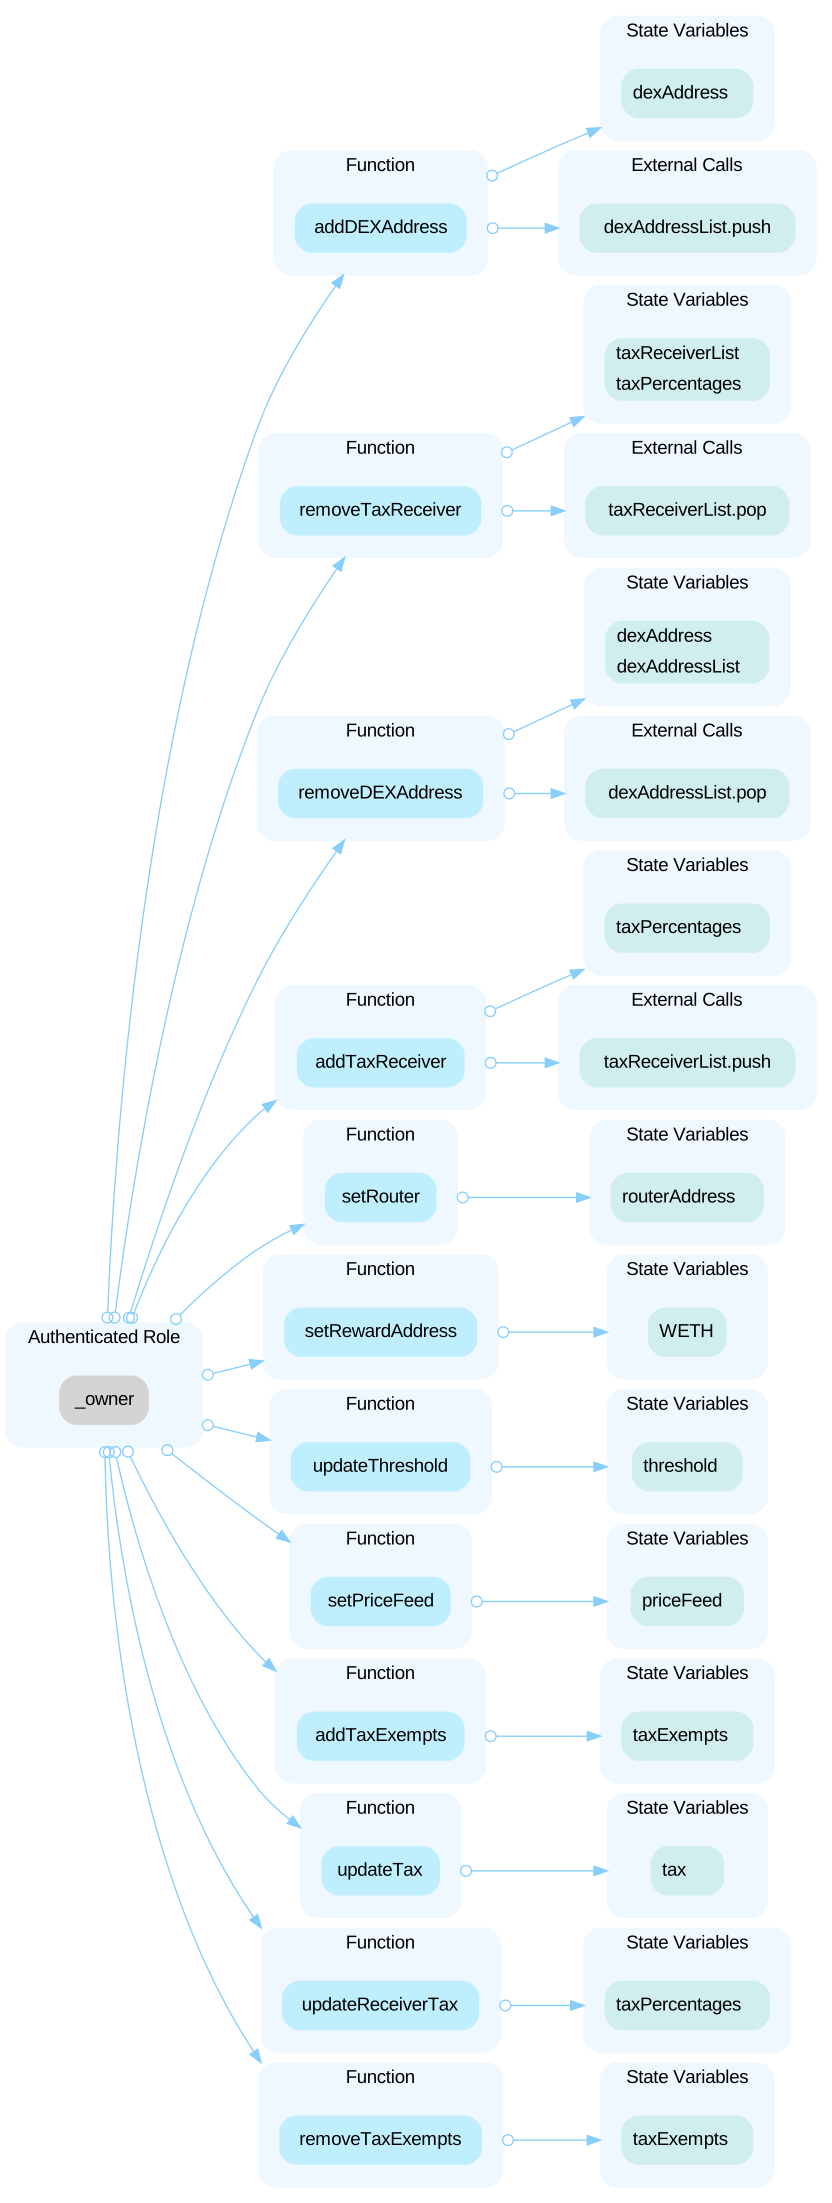 In the contract `Feeding` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set router and reward addresses, set the reward threshold for the feed pool, set the growth rate increase for reward calculation, set the base growth rate for reward calculation, set the token path to blob for a feed token, add/remove feed token and withdraw funds from the contract to an external account. 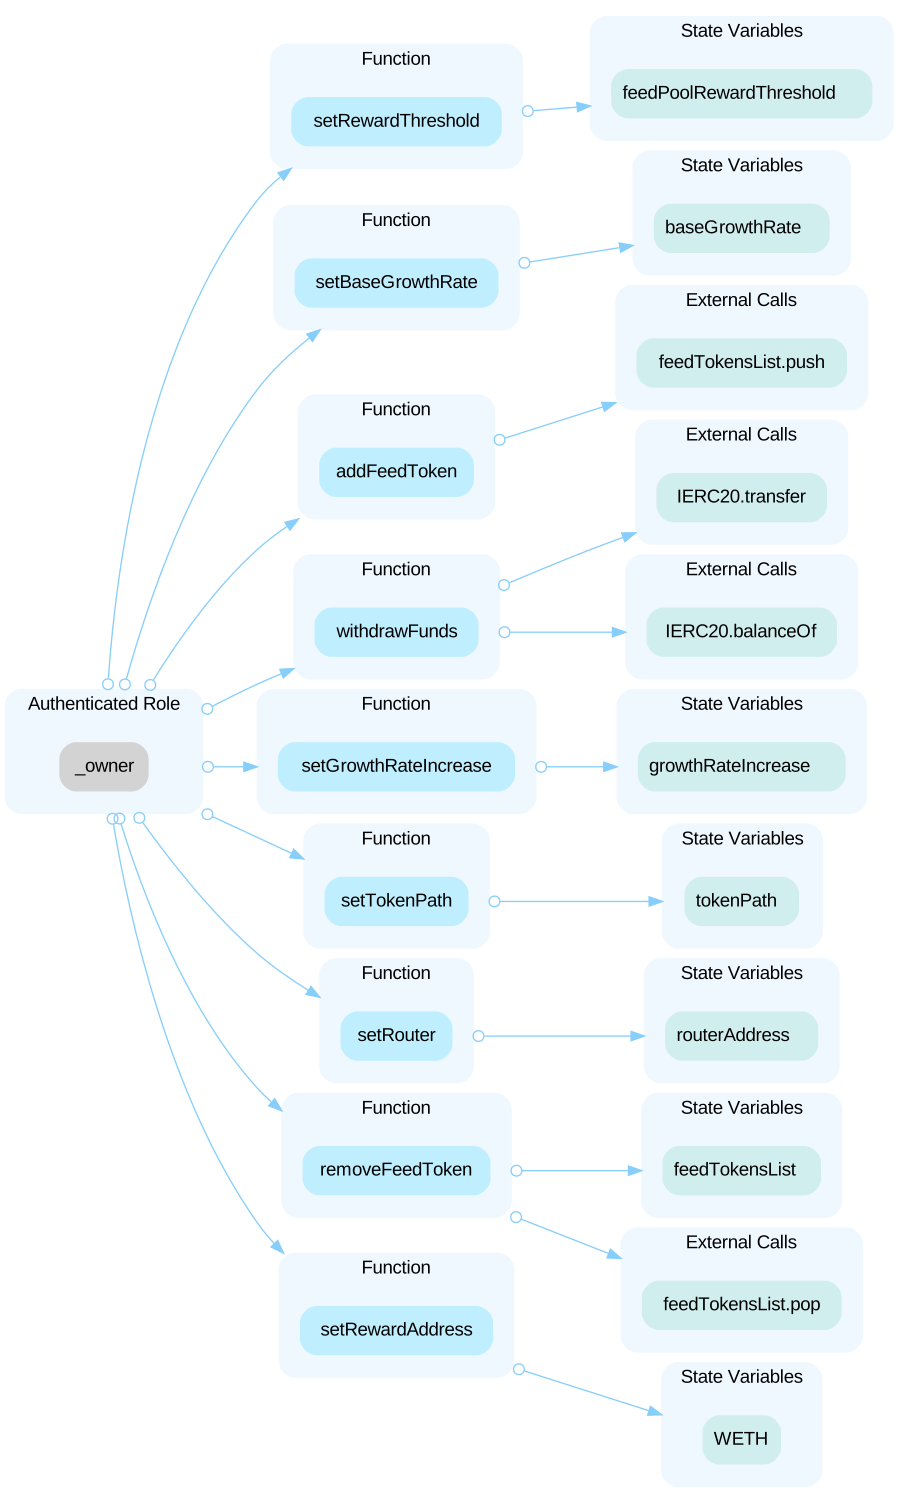
HighInitial Token DistributionOpen
`10_000_000_000 * 10 ** 18` of the `Blob` tokens are sent to the contract deployer or one or several externally owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
MediumLack a Sanity Check for `tokenPath`Open
The `feed()` function lacks a sanity check for both `_tokenIn` and `WETH` to ensure their token paths are accurately configured. In the event of an incorrectly set token path, the `_swap()` function will trigger a reversion, preventing users from successfully executing the feeding action.
MediumPotential Sandwich AttacksOpen
A sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction is attacked) a transaction to purchase one of the assets and make profits by backrunning (after the transaction is attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `IUniswapV2Router02(routerAddress).swapExactTokensForTokensSupportingFeeOnTransferTokens`
MediumPotential Transfer RevertOpen
Within the `_transfer()` function, when `deploymentSet` is set to true, and both `currentTaxAmount` and the outgoing amount surpass the specified `threshold`, tax distribution occurs. Nevertheless, the successful execution of the `_distributeTax()` function necessitates a cumulative tax percentage of 100. Any inaccuracies in configuring tax receivers and percentages will result in a reversion of the `_transfer()` function, thereby preventing users from engaging in token transactions, whether buying or selling.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of Blob DAO’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us