qiibee - Token Sale
CertiK reviewed qiibee foundation $QBX (qiibee - Token Sale) on 10 Sep 2024: 6 findings, 1 critical; 3 marked fixed, 1 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 1 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 3 |
HighCentralization Related RisksAcknowledged
In the contract `Raffle` the role `_owner` has authority over the functions shown in the diagram below. 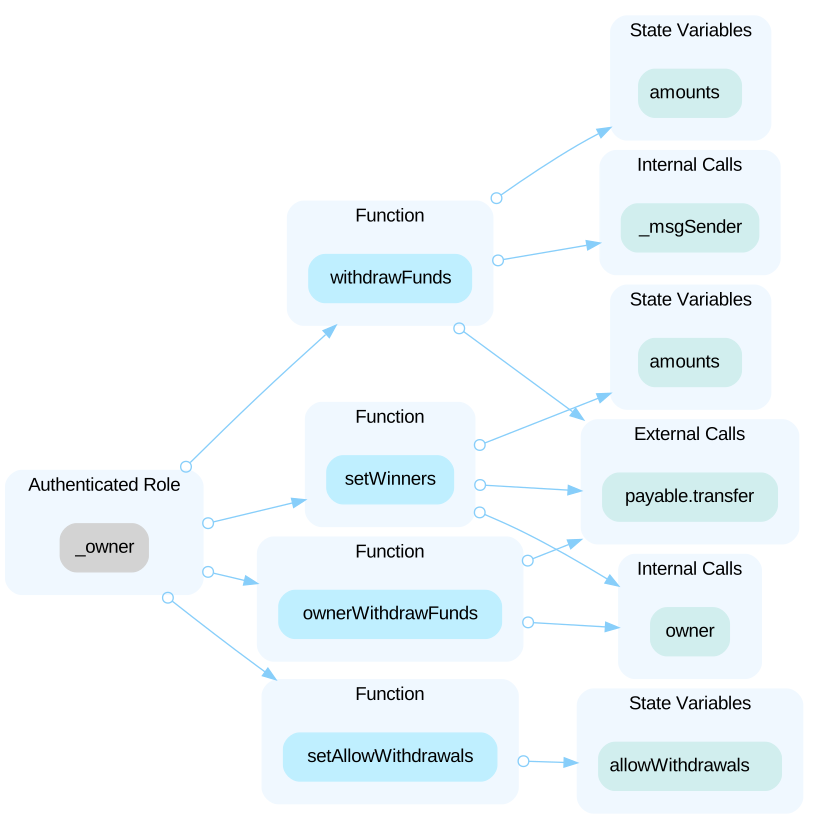 - `setAllowWithdrawals(bool flag)`: This function allows the contract owner to enable or disable the ability for funds to be withdrawn from the contract after the raffle has ended, based on the boolean flag provided. **Privileged role**: Only the contract owner can call this function. - `setWinners(address[] calldata winners, uint256[] calldata amountList)`: This function allows the contract owner to set winners after the raffle has ended and transfer the specified amounts from the winners' balances to the owner's address. **Privileged role**: Only the contract owner can call this function. - `withdrawFunds()`: Allows the contract owner to withdraw funds that have been deposited into the raffle under their address. **Privileged role**: Only the contract owner can call this function. - `ownerWithdrawFunds()`: This function permits the contract owner to withdraw all funds from the contract. **Privileged role**: Only the contract owner can call this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/Raffle.sol
Part of qiibee foundation $QBX’s security record
 qiibee foundation $QBX
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us