DEX Finance (dexVAULTS & dex ETF)
CertiK reviewed Dex Finance (DEX Finance (dexVAULTS & dex ETF)) on 1 Mar 2023: 17 findings, 1 critical; 16 marked fixed, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings17
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 1 | 0 | 2 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 12 |
HighCentralization Related RisksOpen
In the contract `DexFiLPZapper` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 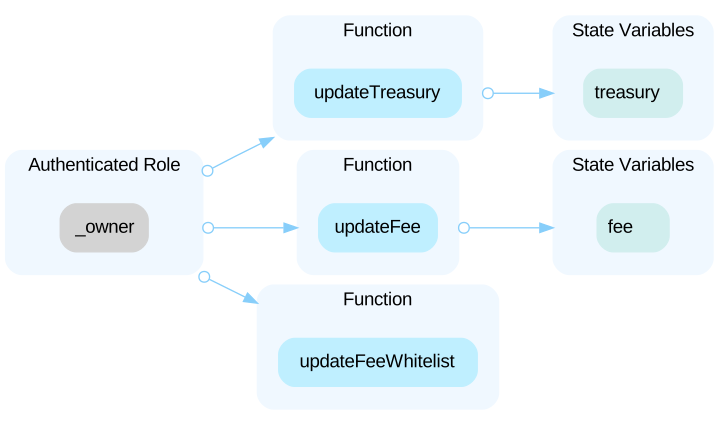 In the contract `DexFiTreasury` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 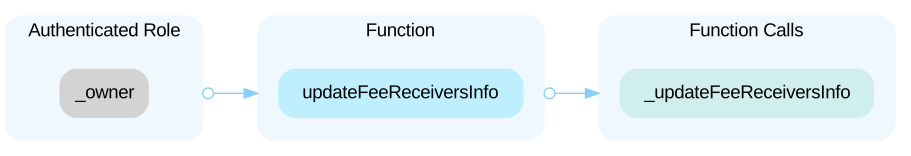 In the contract `DexFiVault` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 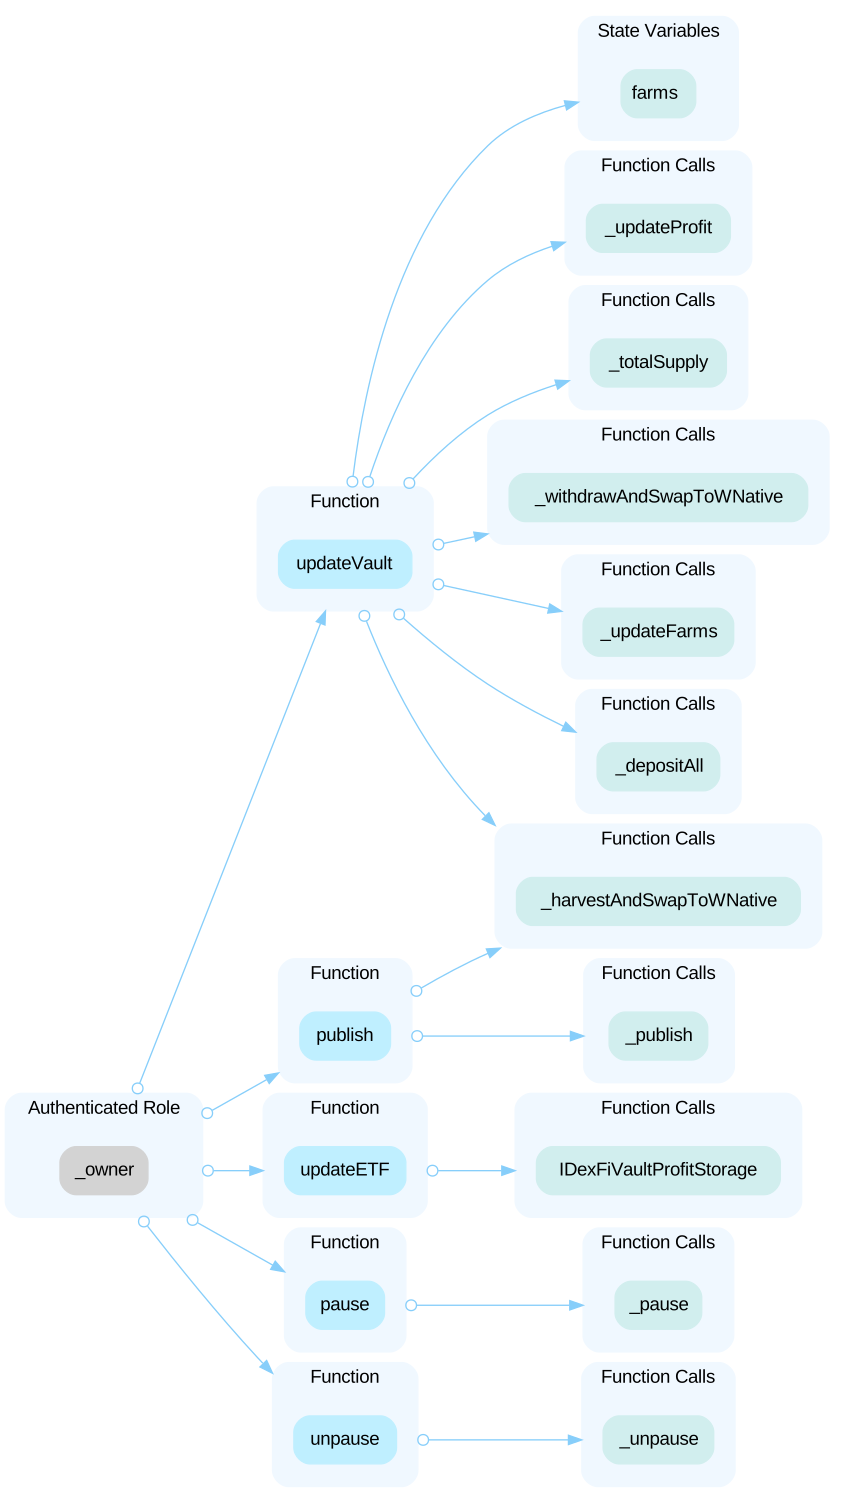 In the contract `DexFiVaultFactory` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 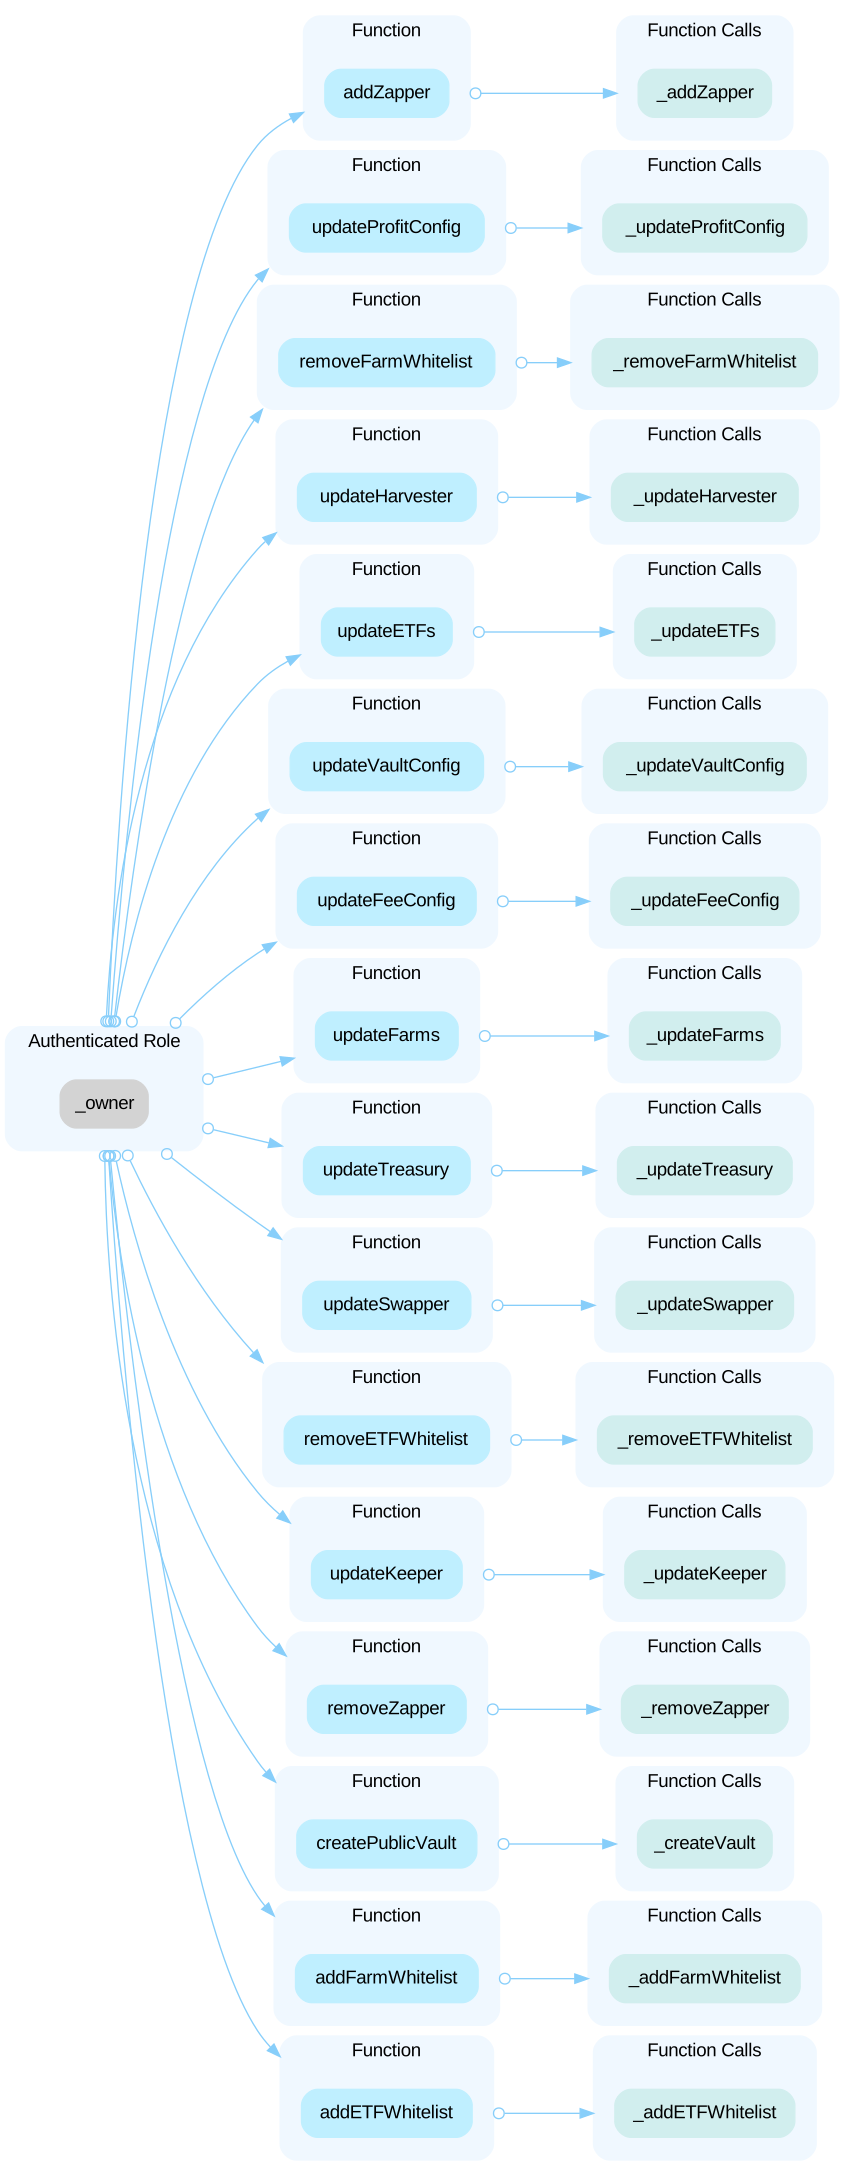 In the contract `DexFiVaultProfitStorage` the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority. 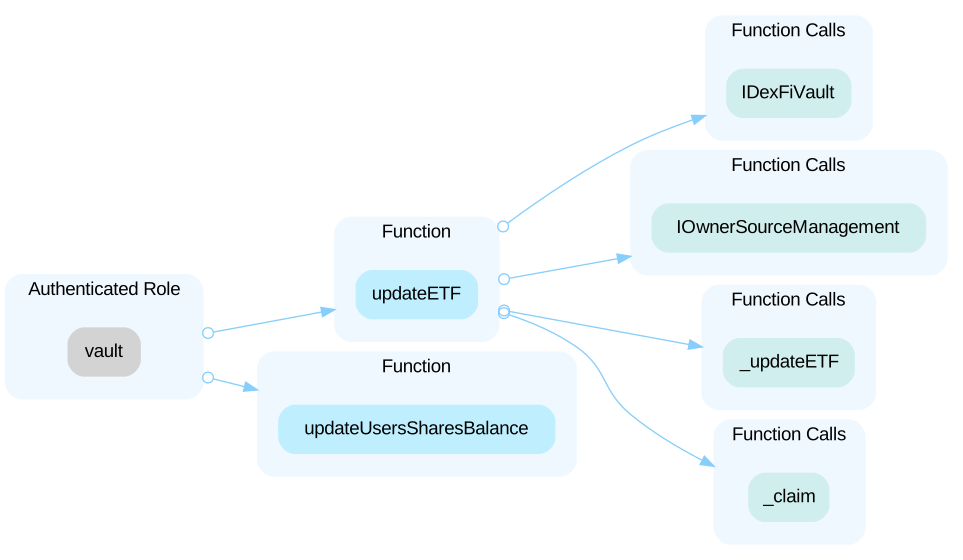 In the contract `DexFiFarmOutsidePoolConnector` the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority. 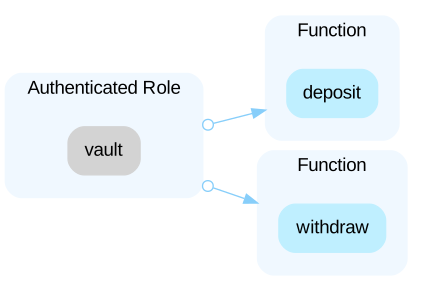 In the contract `DexShareRewardPoolConnector` the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority. 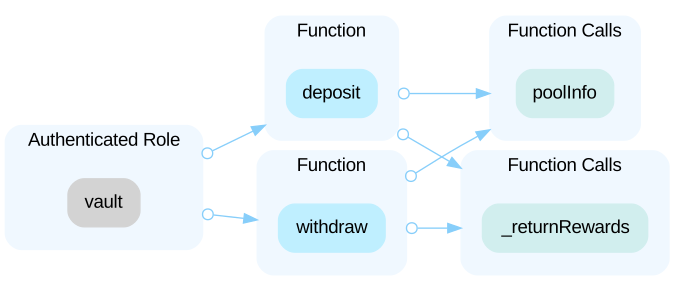 In the contract `PancakeMasterPoolConnector` the role `vault` has authority over the functions shown in the diagram below. Any compromise to the `vault` account may allow the hacker to take advantage of this authority. 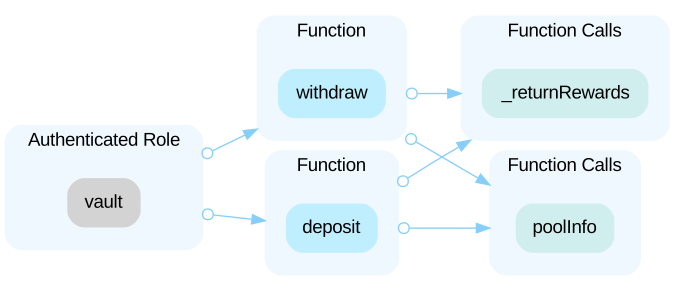 In the contract `DexFiETF` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 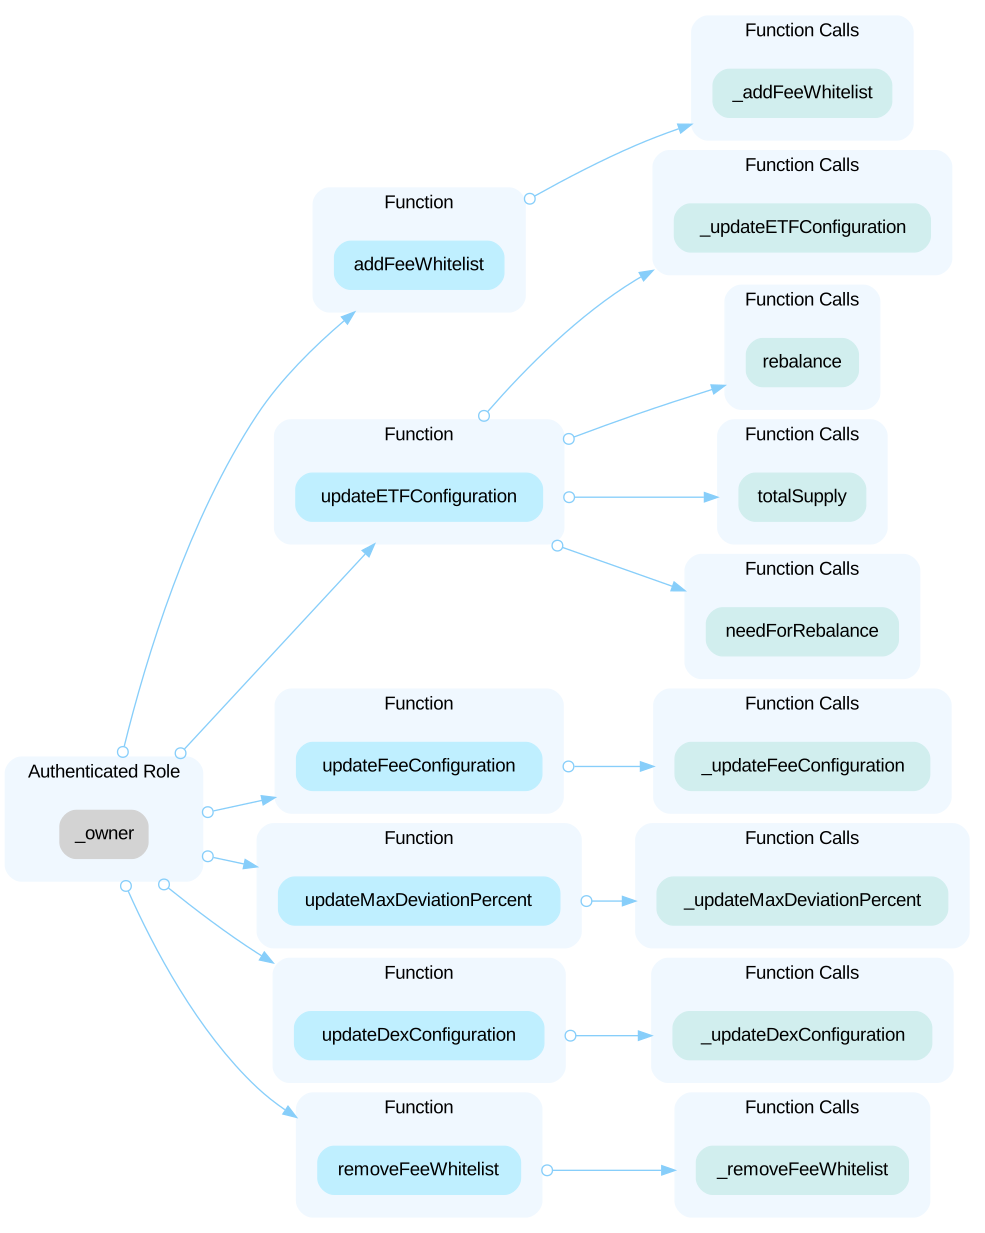 In the contract `DexFiETFZapper` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 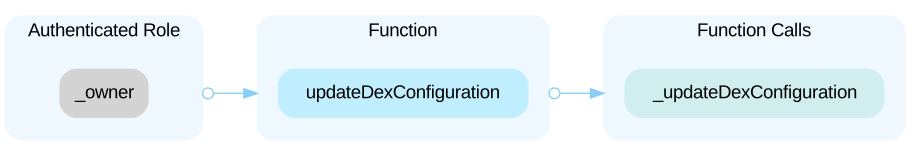 In the contract `OwnerSourceManagement` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 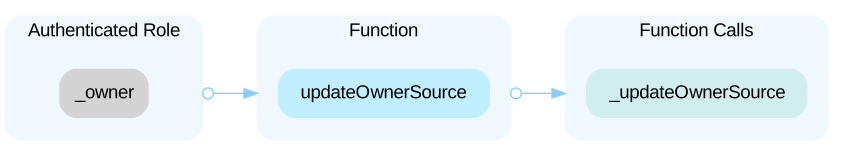 In the contract `DexFiVaultHarvester` the role `keeper` has authority over the function `harvest()`, which harvests rewards and pays the `keeper` for the service. Any compromise to the `keeper` account may allow the hacker to take advantage of this authority. In the contract `VaultHarvesterDebtManagement` the role `harvester` has authority over the function `increaseHarvesterDebt()`, which increases the amount that needs to be paid to the `keeper` for harvesting. Any compromise to the `harvester` account may allow the hacker to take advantage of this authority. In commit [64b0850cccc1cfc1464064d63db9d235baf5f1e1](https://github.com/dexfinance-com/vaults-pro/commit/64b0850cccc1cfc1464064d63db9d235baf5f1e1), the role `_owner` is added to the contract `DexFiVaultZapper`. The role `_owner` has authority over the functions listed below: - `addTokensWhitelis
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (88)
- contracts/core/abstracts/ETFZapper/ETFZapperDexConfigurationManagement.sol
- contracts/core/abstracts/OwnerSourceManagement.sol
- contracts/core/abstracts/ETF/ETFDexConfigurationManagement.sol
- contracts/core/abstracts/vault/VaultProfitManagement.sol
- contracts/core/interfaces/vault/IVaultPublish.sol
- contracts/core/interfaces/factory/IFactoryFeeManagement.sol
- contracts/core/interfaces/IDexFiVaultPreviousVersion.sol
- contracts/core/DexFiTreasury.sol
- contracts/core/interfaces/ETF/IETFCalculationsUtilities.sol
- contracts/core/abstracts/ETF/ETFConstants.sol
- contracts/core/abstracts/factory/FactoryFarmsManagement.sol
- contracts/core/abstracts/factory/FactoryFeeManagement.sol
- contracts/core/interfaces/ETF/IETF.sol
- contracts/core/interfaces/Dex/IFactory.sol
- contracts/core/abstracts/Constants.sol
- contracts/core/interfaces/IDexFiVaultHarvester.sol
- contracts/core/interfaces/factory/IFactoryETFsManagement.sol
- contracts/core/interfaces/IDexFiDexManagement.sol
- contracts/core/interfaces/IDexFiETF.sol
- contracts/core/interfaces/ETFZapper/IETFZapperDexConfigurationManagement.sol
- contracts/core/DexFiETF.sol
- contracts/core/farms/PancakeMasterPool/IPancakeMasterPool.sol
- contracts/core/interfaces/Dex/IPair.sol
- contracts/core/abstracts/ETF/ETFFeeConfigurationManagement.sol
- contracts/core/interfaces/factory/IFactoryFarmsManagement.sol
- contracts/core/interfaces/IDexFiTreasury.sol
- contracts/core/interfaces/Dex/IWrapped.sol
- contracts/core/abstracts/factory/FactoryHarvesterManagement.sol
- contracts/core/libraries/DexLibrary.sol
- contracts/core/interfaces/factory/IFactoryProfitManagement.sol
- contracts/core/DexFiVaultHarvester.sol
- contracts/core/DexFiETFZapper.sol
- contracts/core/interfaces/IDexFiLPZapper.sol
- contracts/core/interfaces/Dex/IRouter.sol
- contracts/core/abstracts/vault/VaultFarmsManagement.sol
- contracts/core/interfaces/vault/IVaultStructs.sol
- contracts/core/interfaces/ETFZapper/IETFZapper.sol
- contracts/core/interfaces/factory/IFactoryIntegrationManagement.sol
- contracts/core/abstracts/factory/FactoryETFsManagement.sol
- contracts/core/abstracts/ETF/ETFCalculationsUtilities.sol
- contracts/core/abstracts/vault/VaultStakingAndRewardTokenSwaps.sol
- contracts/core/abstracts/vault/VaultHarvesterDebtManagement.sol
- contracts/core/abstracts/vault/VaultPublish.sol
- contracts/core/interfaces/factory/IFactoryVaultManagement.sol
- contracts/core/interfaces/vault/IVaultFarmsManagement.sol
- contracts/core/DexFiVaultZapper.sol
- contracts/core/interfaces/IDexConfigurationManagementBase.sol
- contracts/core/abstracts/DexFiWNativeManagement.sol
- contracts/core/interfaces/factory/IFactoryStructs.sol
- contracts/core/interfaces/IOwnerSourceManagement.sol
- contracts/core/abstracts/vault/VaultCore.sol
- contracts/core/abstracts/factory/FactoryProfitManagement.sol
- contracts/core/abstracts/ETF/ETFConfigurationManagement.sol
- contracts/core/farms/DexShareRewardPool/IDexShareRewardPool.sol
- contracts/core/interfaces/IDexFiFarmOutsidePoolConnector.sol
- contracts/core/DexFiLPZapper.sol
- contracts/core/farms/DexShareRewardPool/DexShareRewardPoolConnector.sol
- contracts/core/abstracts/ETFZapper/ETFZapperCalculationsUtilities.sol
- contracts/core/DexFiVaultFactory.sol
- contracts/core/DexFiVaultSwapper.sol
- contracts/core/interfaces/ETF/IETFDexConfigurationManagement.sol
- contracts/core/abstracts/DexFiDexManagement.sol
- contracts/core/abstracts/DexFiFarmOutsidePoolConnector.sol
- contracts/core/DexFiVault.sol
- contracts/core/interfaces/vault/IVaultCore.sol
- contracts/core/interfaces/IDexFiVaultFactory.sol
- contracts/core/abstracts/factory/FactoryVaultManagement.sol
- contracts/core/interfaces/IDexFiWNativeManagement.sol
- contracts/core/interfaces/IDexFiVaultZapper.sol
- contracts/core/interfaces/IDexFiVault.sol
- contracts/core/interfaces/factory/IFactoryHarvesterManagement.sol
- contracts/core/interfaces/IDexFiVaultProfitStorage.sol
- contracts/core/abstracts/vault/VaultTokenSwaps.sol
- contracts/core/interfaces/ETF/IETFConfigurationManagement.sol
- contracts/core/interfaces/IStructs.sol
- contracts/core/DexFiVaultProfitStorage.sol
- contracts/core/abstracts/factory/FactoryIntegrationManagement.sol
- contracts/core/interfaces/factory/IDexFiFactory.sol
- contracts/core/interfaces/IDexFiETFZapper.sol
- contracts/core/interfaces/vault/IVaultProfitManagement.sol
- contracts/core/DexFiOwner.sol
- contracts/core/interfaces/vault/IVault.sol
- contracts/core/farms/PancakeMasterPool/PancakeMasterPoolConnector.sol
- contracts/core/abstracts/DexConfigurationManagementBase.sol
- contracts/core/interfaces/IDexFiVaultSwapper.sol
- contracts/core/interfaces/ETF/IETFFeeConfigurationManagement.sol
- contracts/core/abstracts/DexFiSwapTokenToToken.sol
- contracts/core/interfaces/vault/IVaultHarvesterDebtManagement.sol
Part of Dex Finance’s security record
 Dex Finance
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us