Metacade - Audit
CertiK reviewed Metacade (Metacade - Audit) on 1 Dec 2022: 14 findings, 0 critical; 8 marked fixed, 6 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 3 | 0 | 8 |
HighCentralization RisksOpen
In the contract `Metacade` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and withdraw all ETH and tokens stored in the contract. 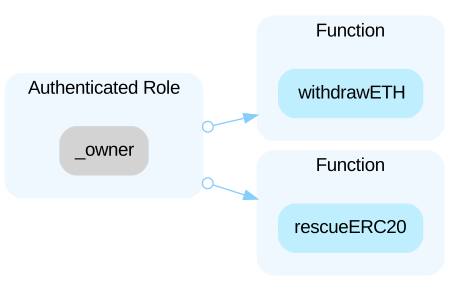 Furthermore, the role `_owner` has authority over the functions `transferOwnership()` and `renounceOwnership()`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the owner address of the contract. In the contract `Presale` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause or unpause the contract, change certain contract settings, and to set the claim start time and sale token address. 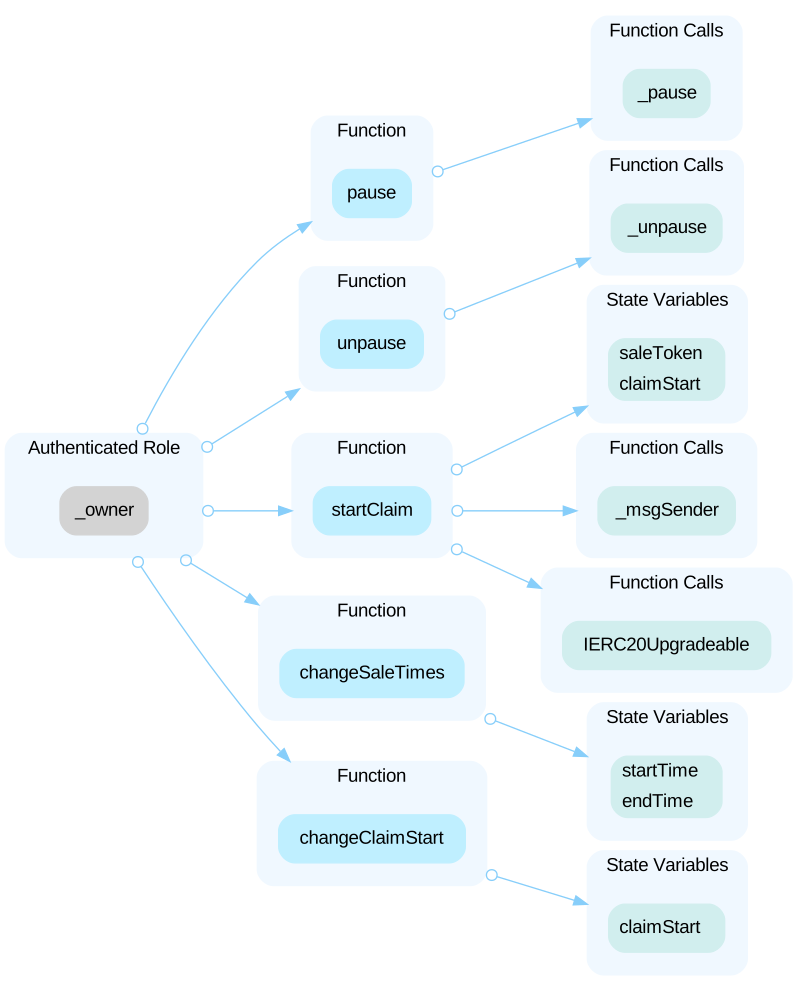
HighCentralized Control of Contract UpgradeOpen
The `Presale` contract is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, they can change the implementation of the contract and drain tokens from the contract.
HighInitial Token DistributionOpen
All of the `MetaCade` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `MetaCade` tokens without obtaining the consensus of the community.
LowThird Party DependenciesOpen
The contract is serving as the underlying entity to interact with the third party contract `Aggregator` from Chainlink and the IERC20Upgradeable contract USDT. The scope of the audit treats 3rd party entities as black boxes and assumes their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. Additionally, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
LowUnchecked ERC-20 `transfer()`/`transferFrom()` CaOpen
The return value of the `transfer()` and `transferFrom()` calls is not checked. ```solidity=395 IERC20Upgradeable(saleToken).transfer(_msgSender(), amount); ``` --- ```solidity=357 IERC20Upgradeable(_saleToken).transferFrom( _msgSender(), address(this), noOfTokens ); ```
LowUnsafe Integer CastOpen
The type conversion `uint256(price)` from type int256 to type uint256 may flip the value's sign: ```solidity=220 return uint256(price); ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of Metacade’s security record
 Metacade
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us