Moongate - Audit
CertiK reviewed Moongate (Moongate - Audit) on 6 Nov 2024: 6 findings, 0 critical; 4 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 4 |
HighCentralization Related RisksOpen
In the contract `MoongateERC1155AirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC1155Airdrop` smart contract. 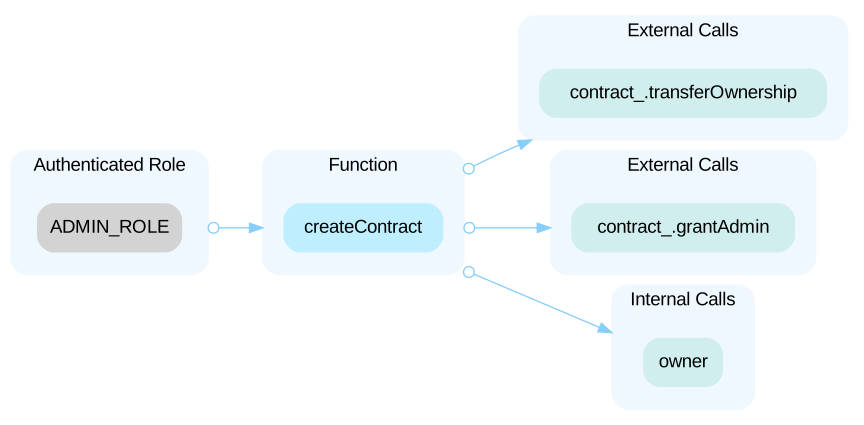 ----- In the contract `MoongateERC721AirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC721AirdropFactory` smart contract. 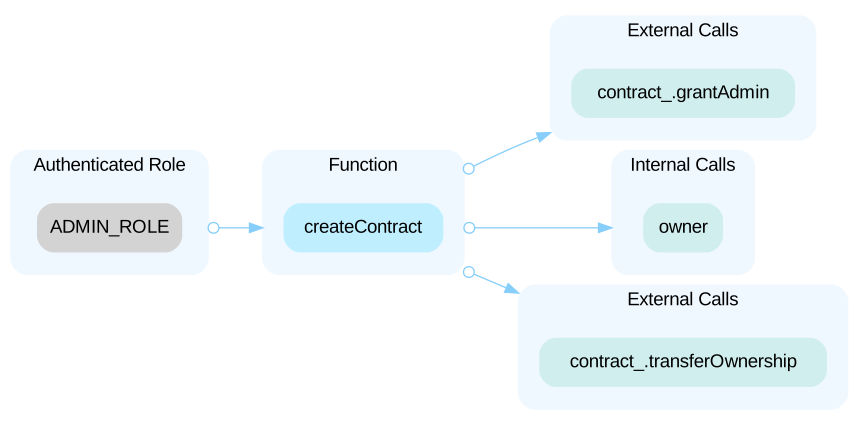 ----- In the contract `MoongateERC721SoulboundAirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC721SoulboundAirdropFactory` smart contract. 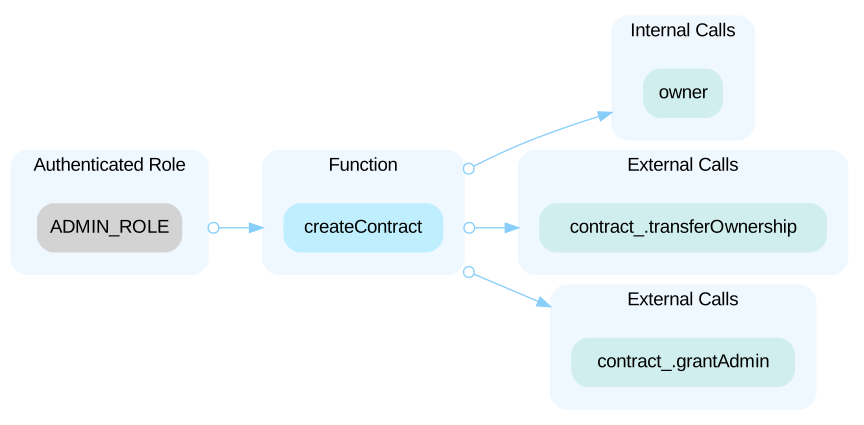 ----- In the contract `MoongateERC1155Airdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the default and token royalty - change the URI - pause and unpause the smart contract 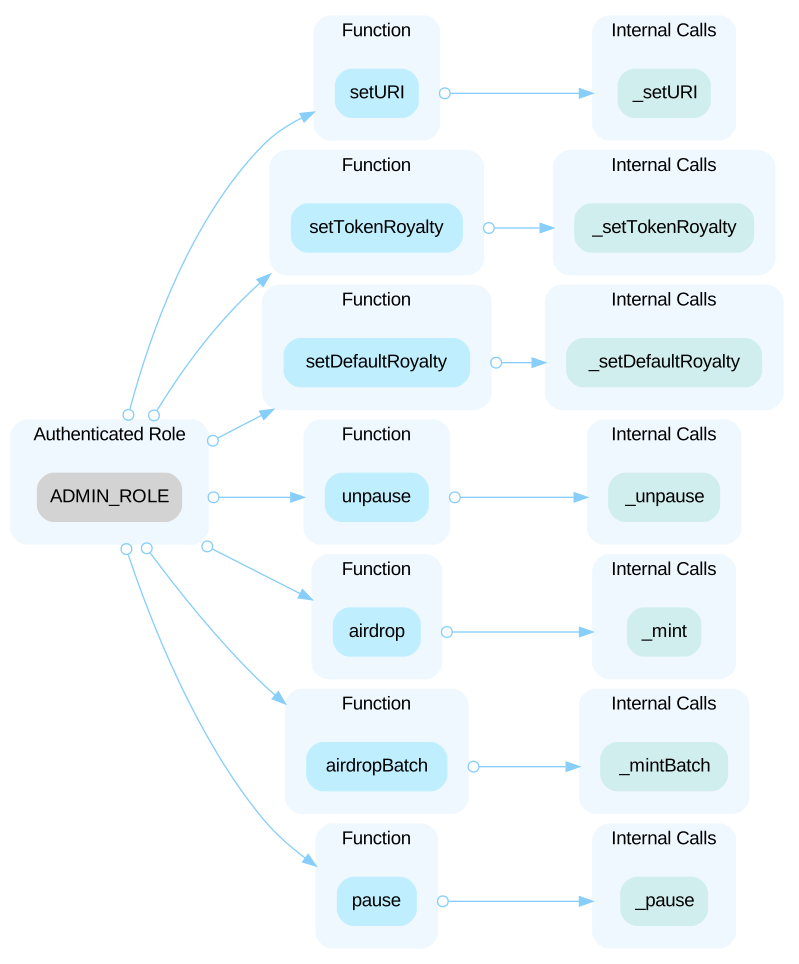 In the contract `MoongateERC1155Airdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 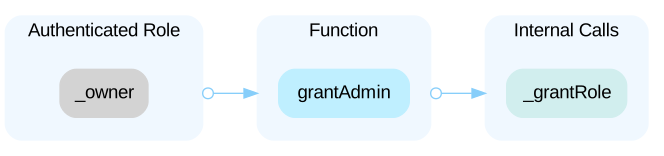 ----- In the contract `MoongateERC721Airdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the base and token URI - change the default and token royalty - pause and unpause the smart contract 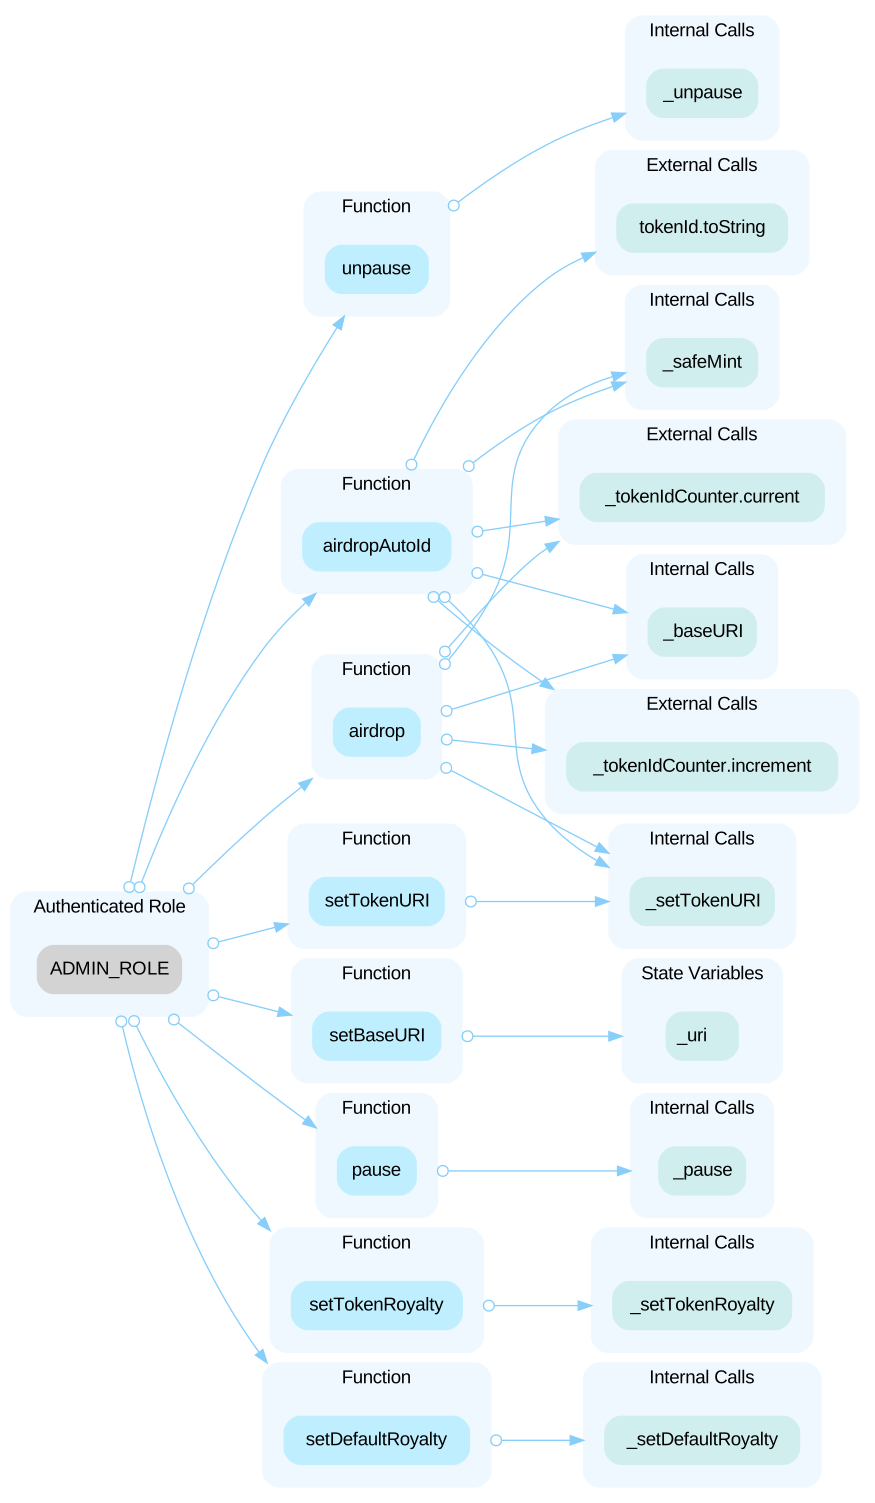 In the contract `MoongateERC721Airdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 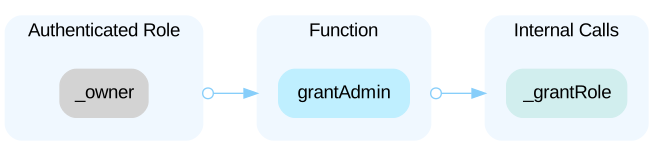 ----- In the contract `MoongateERC721SoulboundAirdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the base and token URI - change the default and token royalty - pause and unpause the smart contract 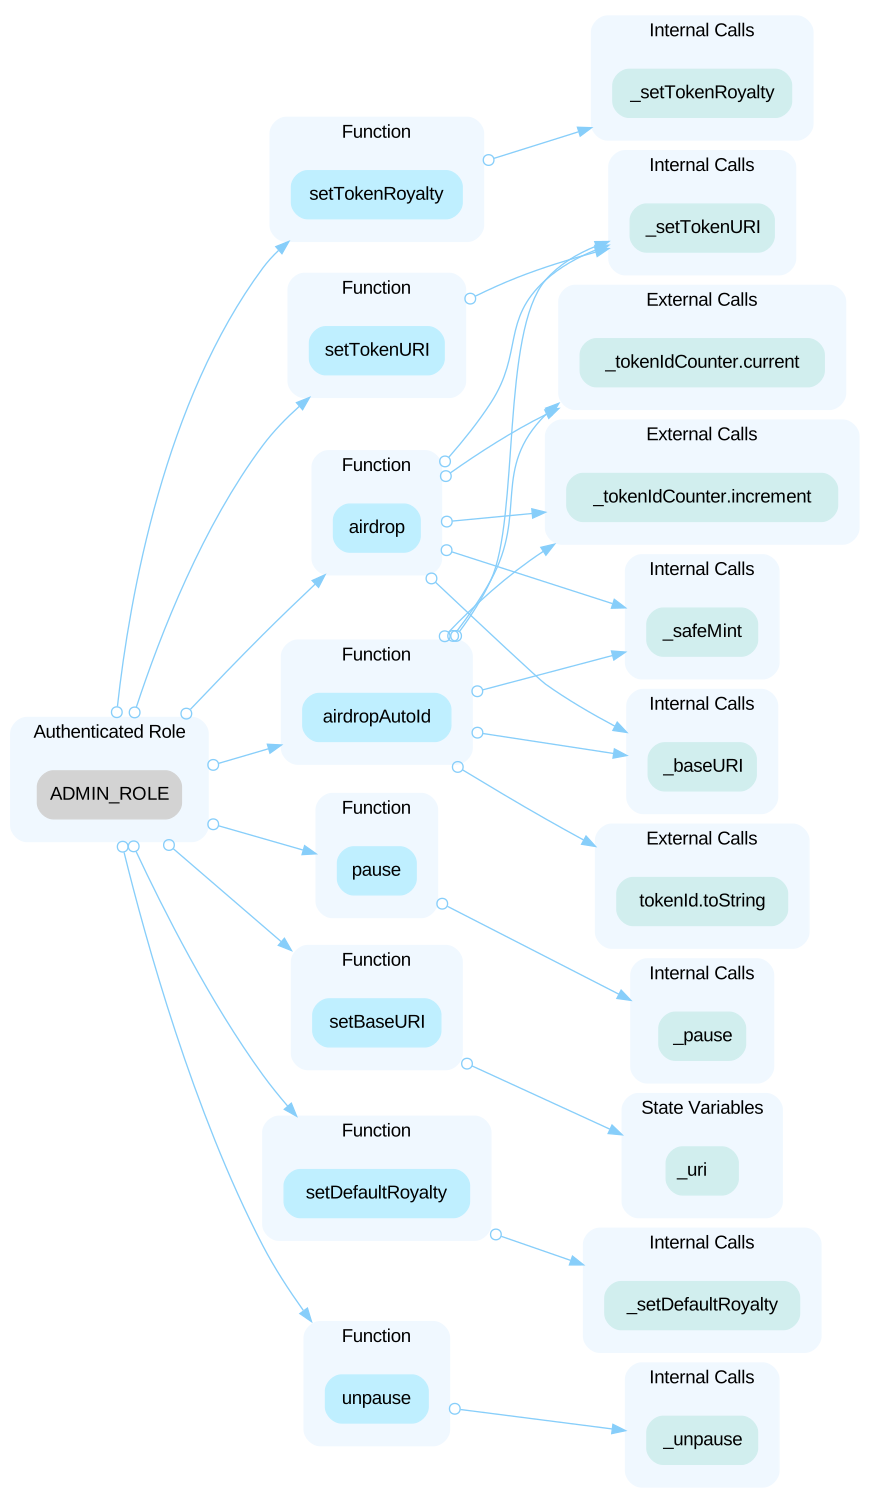 In the contract `MoongateERC721SoulboundAirdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 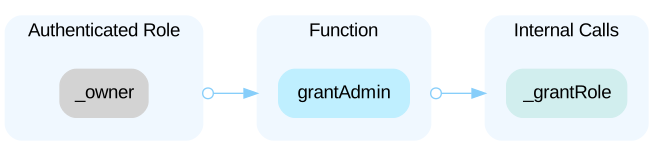
LowCheck-Effect-Interaction pattern not usedOpen
In the `airdrop` and `airdropAutoId` functions, the code invokes `_safeMint(to, tokenId)`, before setting the token URI through `_setTokenURI(tokenId, uri)`. The order of these operations does not follow the recommended `Check-Effect-Interaction pattern`. When `_safeMint` is called, the receiver contract's `onERC721Received` callback could trigger a reentry into the original functions before the `_setTokenURI` is executed. While the issue is present in the code, its current context does not introduce any security impact.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- contracts/templates/MoongateERC721SoulboundAirdrop.sol
- contracts/templates/MoongateERC1155Airdrop.sol
- contracts/templates/MoongateERC721Airdrop.sol
- contracts/factories/MoongateERC1155AirdropFactory.sol
- contracts/factories/MoongateERC721SoulboundAirdropFactory.sol
- contracts/factories/MoongateERC721AirdropFactory.sol
Part of Moongate’s security record
 Moongate
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us