
Moongate audit reports
Moongate has 1 public audit report from CertiK; dated 6 Nov 2024; 5 critical findings, all marked fixed by the firms.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm4
Statuses are the security firms’ own
4 findings are still open or acknowledged in the firms’ reports: 2 high, 2 low (all open).
- High
- 2
- Low
- 2
- High Open
Bypass Management Portal Login
Moongate - Pentest · CertiK · 6 Nov 2024 · Report ↗
- High Open
Centralization Related Risks
Moongate - Audit · CertiK · 6 Nov 2024 · Report ↗
- Low Open
Lack of SSL Pinning
Moongate - Pentest · CertiK · 6 Nov 2024 · Report ↗
- Low Open
Check-Effect-Interaction pattern not used
Moongate - Audit · CertiK · 6 Nov 2024 · Report ↗
Audits1
Newest first
1 other security report listed, not counted
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Moongate - Pentest | Security firm: CertiK | Date: | Scope: Not recorded; see the report | 5 critical findings, fixed | Findings: 5 critical · 2 high · 2 medium · 7 low 14 fixed · 2 open | skynet.certik.com ↗ |
| Moongate - Audit | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 1 high · 5 low 4 fixed · 2 open | skynet.certik.com ↗ |
Findings22
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 5 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 2 |
| Low | 2 | 0 | 10 |
HighBypass Management Portal LoginMoongate - Pentest · CertiK · 6 Nov 2024Open
The Login functionality of the web portal for administrators is based on an invitation code. If the code is valid, another form is displayed for the user to enter their email and receive an access link. However, after the backend verifies the code's validity, it only responds with a true or false, without any token or additional information that can validate in subsequent steps that the user has entered a valid code. Therefore, if the response is intercepted and modified before it reaches the browser, the attacker can access the link access form to generate a new access link without knowing a valid invitation code.
Open the reportHighCentralization Related RisksMoongate - Audit · CertiK · 6 Nov 2024Open
In the contract `MoongateERC1155AirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC1155Airdrop` smart contract. 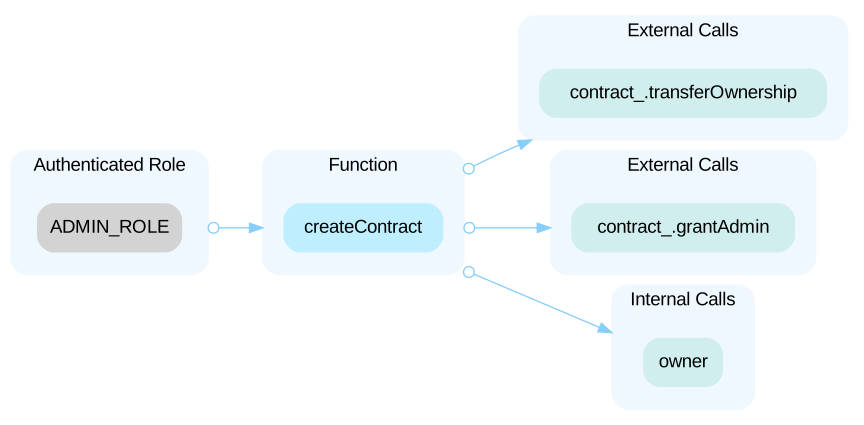 ----- In the contract `MoongateERC721AirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC721AirdropFactory` smart contract. 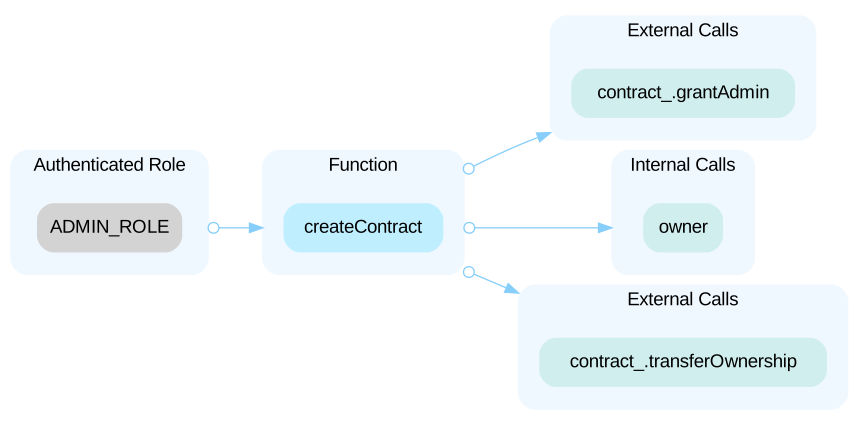 ----- In the contract `MoongateERC721SoulboundAirdropFactory` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and creates new instances of the `MoongateERC721SoulboundAirdropFactory` smart contract. 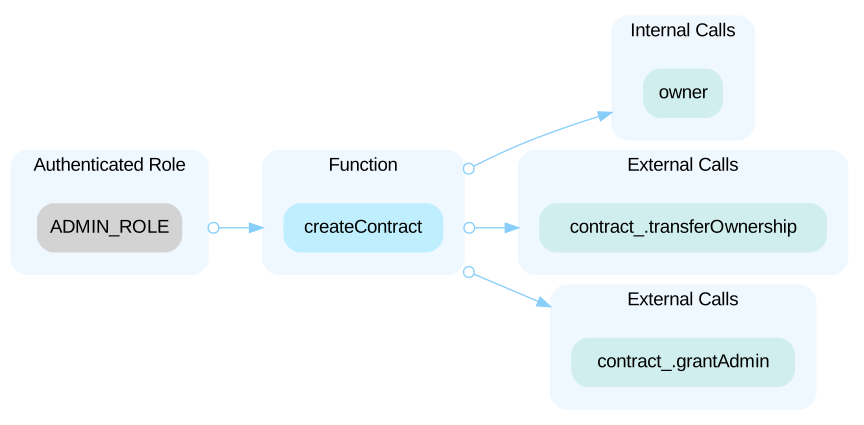 ----- In the contract `MoongateERC1155Airdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the default and token royalty - change the URI - pause and unpause the smart contract 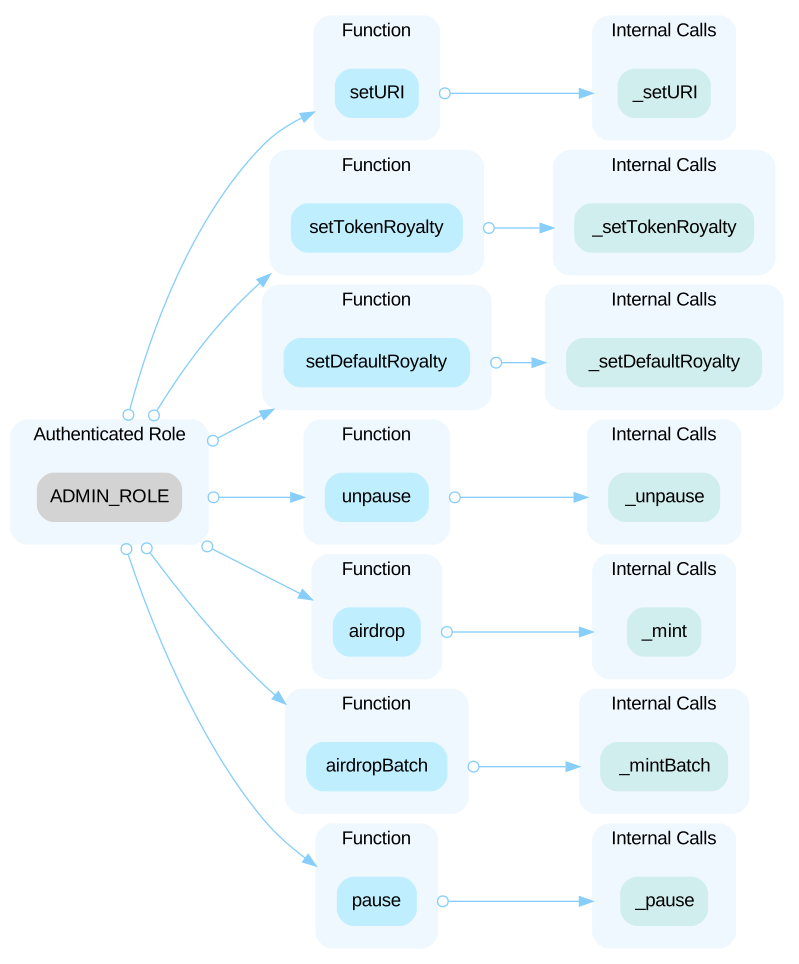 In the contract `MoongateERC1155Airdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 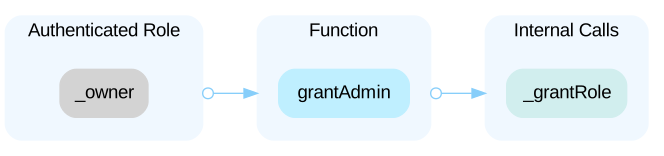 ----- In the contract `MoongateERC721Airdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the base and token URI - change the default and token royalty - pause and unpause the smart contract 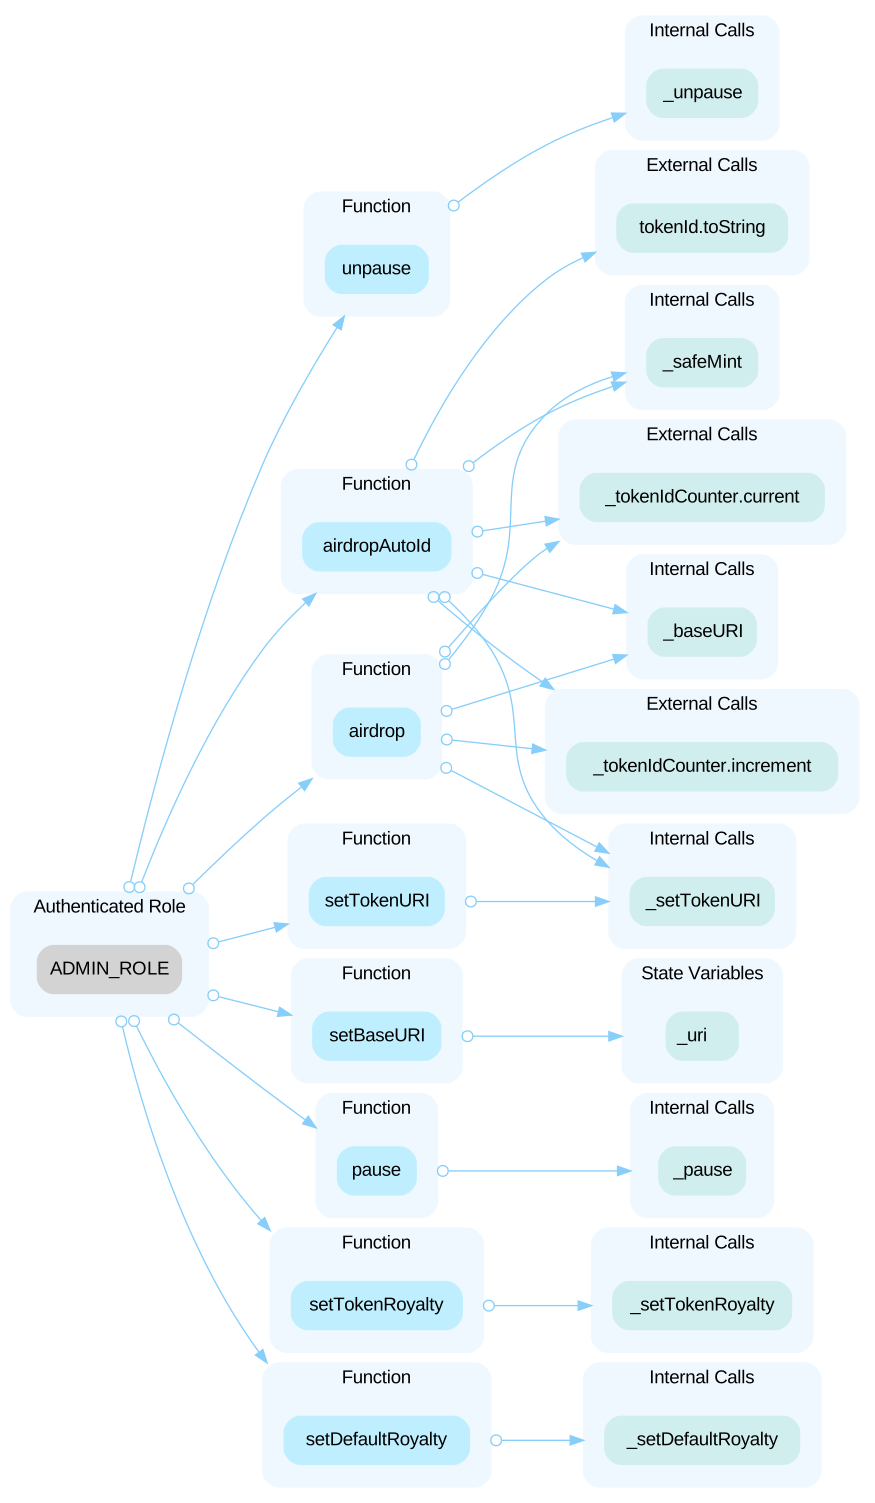 In the contract `MoongateERC721Airdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 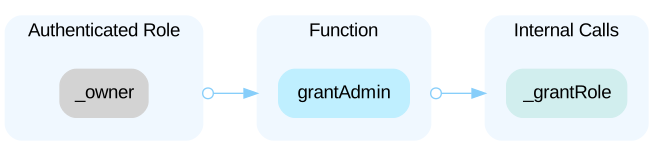 ----- In the contract `MoongateERC721SoulboundAirdrop` the role `ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `ADMIN_ROLE` account may allow the hacker to take advantage of this authority and performs the following actions. - mint new tokens - change the base and token URI - change the default and token royalty - pause and unpause the smart contract 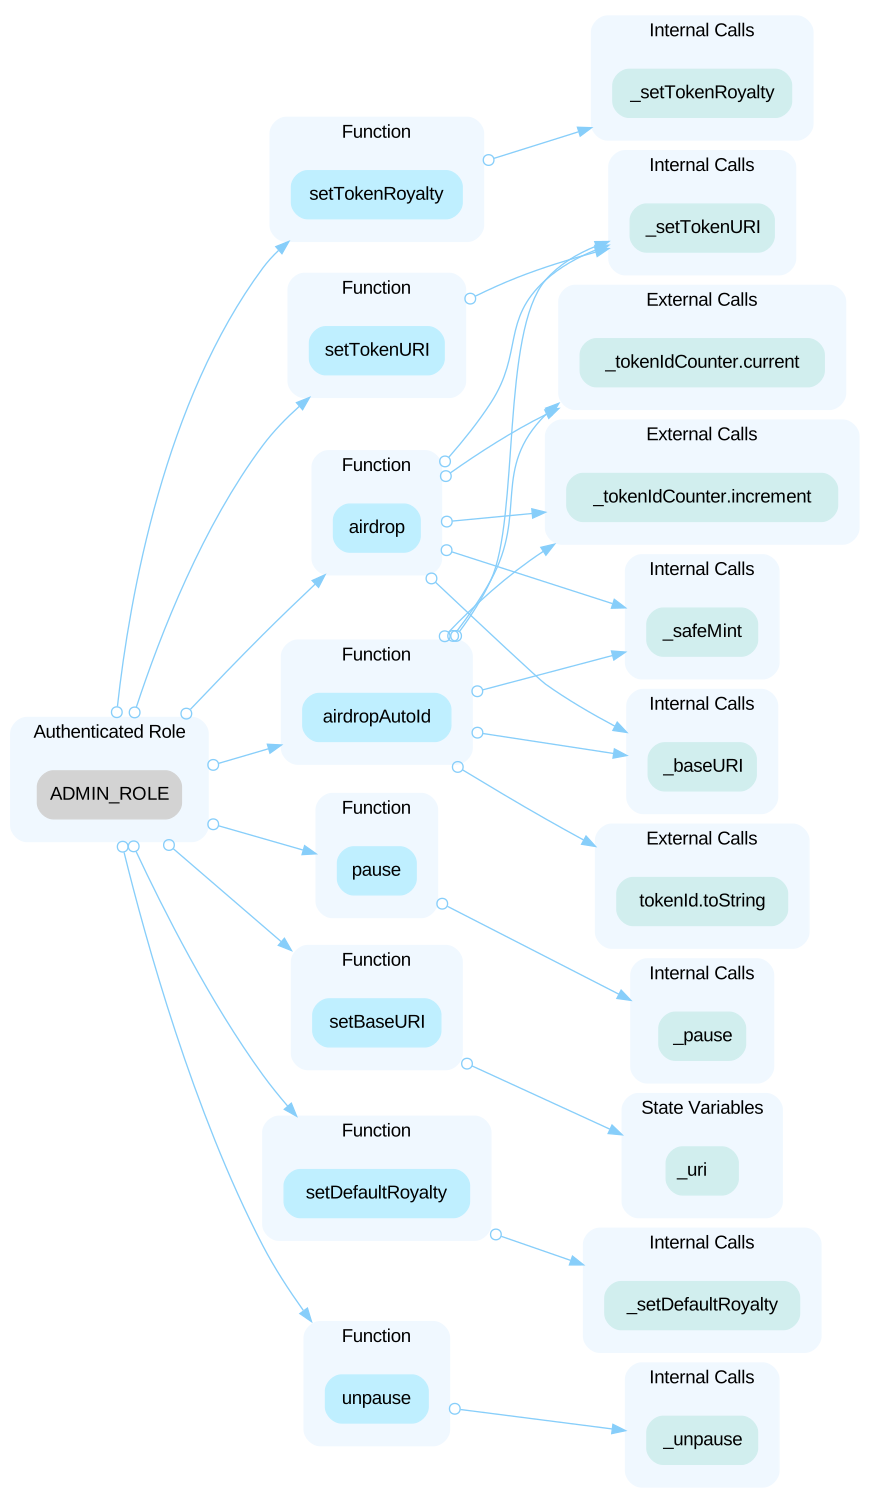 In the contract `MoongateERC721SoulboundAirdrop` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and grants Admin role. 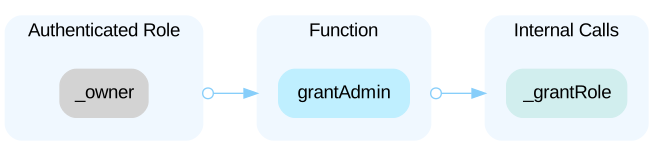
Open the reportLowLack of SSL PinningMoongate - Pentest · CertiK · 6 Nov 2024Open
Certificate pinning is the process of associating the backend server with a particular X.509 certificate or public key instead of accepting any certificate signed by a trusted certificate authority. After storing ("pinning") the server certificate or public key, the mobile app will subsequently connect to the known server only. Withdrawing trust from external certificate authorities reduces the attack surface (after all, there are many cases of certificate authorities that have been compromised or tricked into issuing certificates to impostors). The certificate can be pinned and hardcoded into the app or retrieved at the time the app first connects to the backend. In the latter case, the certificate is associated with ("pinned" to) the host when the host is seen for the first time. This alternative is less secure because attackers intercepting the initial connection can inject their own certificates.
Open the reportLowCheck-Effect-Interaction pattern not usedMoongate - Audit · CertiK · 6 Nov 2024Open
In the `airdrop` and `airdropAutoId` functions, the code invokes `_safeMint(to, tokenId)`, before setting the token URI through `_setTokenURI(tokenId, uri)`. The order of these operations does not follow the recommended `Check-Effect-Interaction pattern`. When `_safeMint` is called, the receiver contract's `onERC721Received` callback could trigger a reentry into the original functions before the `_setTokenURI` is executed. While the issue is present in the code, its current context does not introduce any security impact.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Moongate: questions
Is Moongate audited?
Trustblock holds 1 public audit report for Moongate, dated 6 Nov 2024. The latest is by CertiK (“Moongate - Pentest”).
Who audited Moongate?
CertiK wrote the report Trustblock holds for Moongate.
Are there open findings in Moongate’s audits?
4 findings are still open or acknowledged in the firms’ reports: 2 high, 2 low (all open). Of 5 critical findings: all marked fixed by the firms. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="moongate"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us