
1Cent security record
As of 3 Nov 2026, 1Cent has 1 audit report on Trustblock, by CertiK, dated 21 Sep 2022. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| 1cent dream | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings14
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 11 | 0 | 0 |
HighCentralization Risks in 1Cent.sol1cent dream · CertiK · 21 Sep 2022Open
In the contract `BABYTOKEN`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 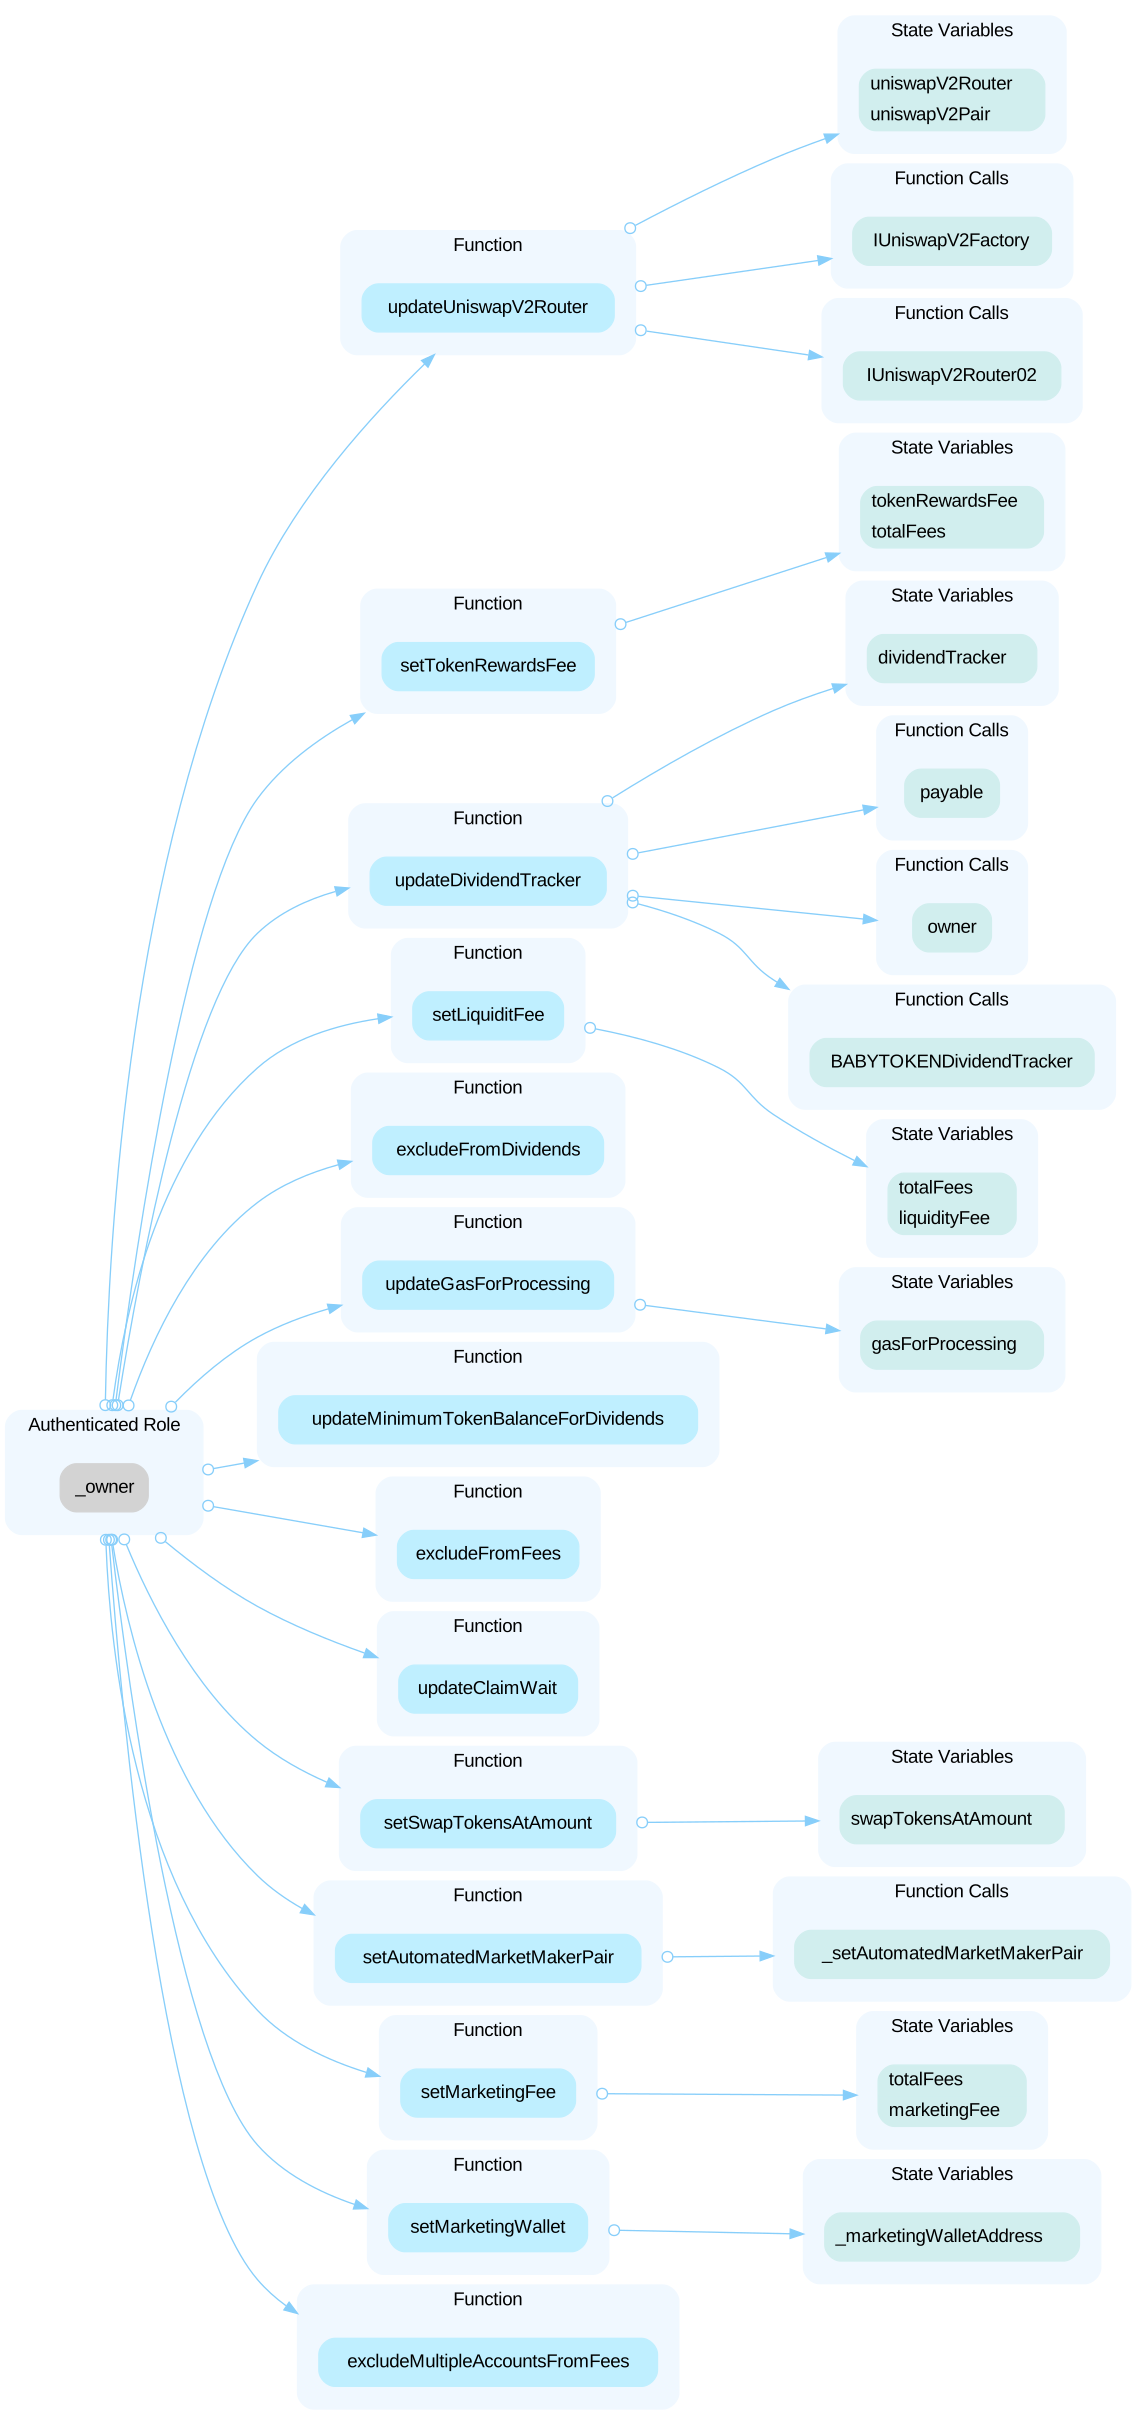
Open the reportHighCentralized Control of Contract Upgrade1cent dream · CertiK · 21 Sep 2022Open
ERC20Upgradeable are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Open the reportHighInitial Token Distribution1cent dream · CertiK · 21 Sep 2022Open
All of the tokens are distributed to the contract deployer when deploying the contract, which could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
Open the reportLowInconsistency between Function Name and Functiona1cent dream · CertiK · 21 Sep 2022Open
According to the function name, this function `distributeCAKEDividends()` is supposed to distribute dividends to token holders. However, the function appears to only update `magnifiedDividendPerShare` and `totalDividendsDistributed`, and not actually sends dividends to token holders.
Open the reportLowMissing Emit Events1cent dream · CertiK · 21 Sep 2022Open
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportLowMissing Error Messages1cent dream · CertiK · 21 Sep 2022Open
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
Open the reportLowMissing Zero Address Validation1cent dream · CertiK · 21 Sep 2022Open
Address should be checked before assignment to make sure it is not zero addresses.
Open the reportLowPotential Reentrancy Attack1cent dream · CertiK · 21 Sep 2022Open
A reentrancy attack can occur when the contract creates a function that makes an external call to another untrusted contract before resolving any effects. If the attacker can control the untrusted contract, they can make a recursive call back to the original function, repeating interactions that would have otherwise not run after the external call resolved the effects.
Open the reportLowRedundant Statements1cent dream · CertiK · 21 Sep 2022Open
When the transfer amount is 0, calling super._transfer() has no effect but waste gas.
Open the reportLowThird Party Dependencies1cent dream · CertiK · 21 Sep 2022Open
The contract is serving as the underlying entity to interact with third party Pancakeswap protocols. The scope of the audit treats 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
Open the reportShow 4 more
LowTypo in the Comment1cent dream · CertiK · 21 Sep 2022Open
The spelling of 'exlcude' is a typo.
Open the reportLowUnreachable Code1cent dream · CertiK · 21 Sep 2022Open
Given the require(false) statement, the code block from line 2233 to line 2239 in function `transfer()` will never be executed and is unnecessary.
Open the reportLowUnused Return Value1cent dream · CertiK · 21 Sep 2022Open
The return value of an external call is not stored in a local or state variable.
Open the reportLowVariables That Could Be Declared as Immutable1cent dream · CertiK · 21 Sep 2022Open
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="1cent"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us