Brewlabs has 3 public audit reports from CertiK and Paladin; the latest is CertiK, 3 Apr 2024; 2 critical findings, 1 open, 1 marked fixed. It also holds 5 deployed contracts on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Statuses are the security firms’ own
19 findings are still open or acknowledged in the firms’ reports: 1 critical, 5 high, 2 medium, 11 low (14 open, 5 acknowledged).
Centralization Risks in BrewlabsTreasury.sol
Brewlabs Treasury · CertiK · 29 Aug 2022 · Report ↗
Centralization Related Risks
Brewlabs Marketplace and PoolFactory · CertiK · 3 Apr 2024 · Report ↗
Centralized Control of Contract Upgrade
Brewlabs Marketplace and PoolFactory · CertiK · 3 Apr 2024 · Report ↗
Untitled finding
Audit Report · Paladin · 5 Oct 2023 · Report ↗
Untitled finding
Audit Report · Paladin · 5 Oct 2023 · Report ↗
Untitled finding
Audit Report · Paladin · 5 Oct 2023 · Report ↗
Untitled finding
Audit Report · Paladin · 5 Oct 2023 · Report ↗
Untitled finding
Audit Report · Paladin · 5 Oct 2023 · Report ↗
`BrewsMarketplace.supportsInterface()` Always Ret
Brewlabs Marketplace and PoolFactory · CertiK · 3 Apr 2024 · Report ↗
Missing Emit Events
Brewlabs Marketplace and PoolFactory · CertiK · 3 Apr 2024 · Report ↗
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Brewlabs Marketplace and PoolFactory | Security firm: CertiK | Date: | Scope: Files listed | 1 critical finding, fixed | Findings: 1 critical · 3 high · 1 medium · 11 low 9 fixed · 2 acknowledged · 5 open | skynet.certik.com ↗ |
| Audit Report | Security firm: Paladin | Date: | Scope: 5 addresses on BNB Chain | None open | Findings: 6 high · 3 medium · 18 low 17 fixed · 3 acknowledged · 7 open | paladinsec.co ↗ |
| Brewlabs Treasury | Security firm: CertiK | Date: | Scope: Files listed | 1 open critical finding | Findings: 1 critical · 7 low 6 fixed · 2 open | skynet.certik.com ↗ |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 1 | 0 | 1 |
| High | 3 | 2 | 4 |
| Medium | 1 | 1 | 2 |
| Low | 9 | 2 | 25 |
In the contract `BrewlabsTreasury` the role `_owner` has authority over the functions shown in the diagram below. In fact, every external function can only be called by the `_owner` account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and gain complete control over the contract. In particular, they can withdraw all the ETH and pool tokens from the script and keep it for themselves. 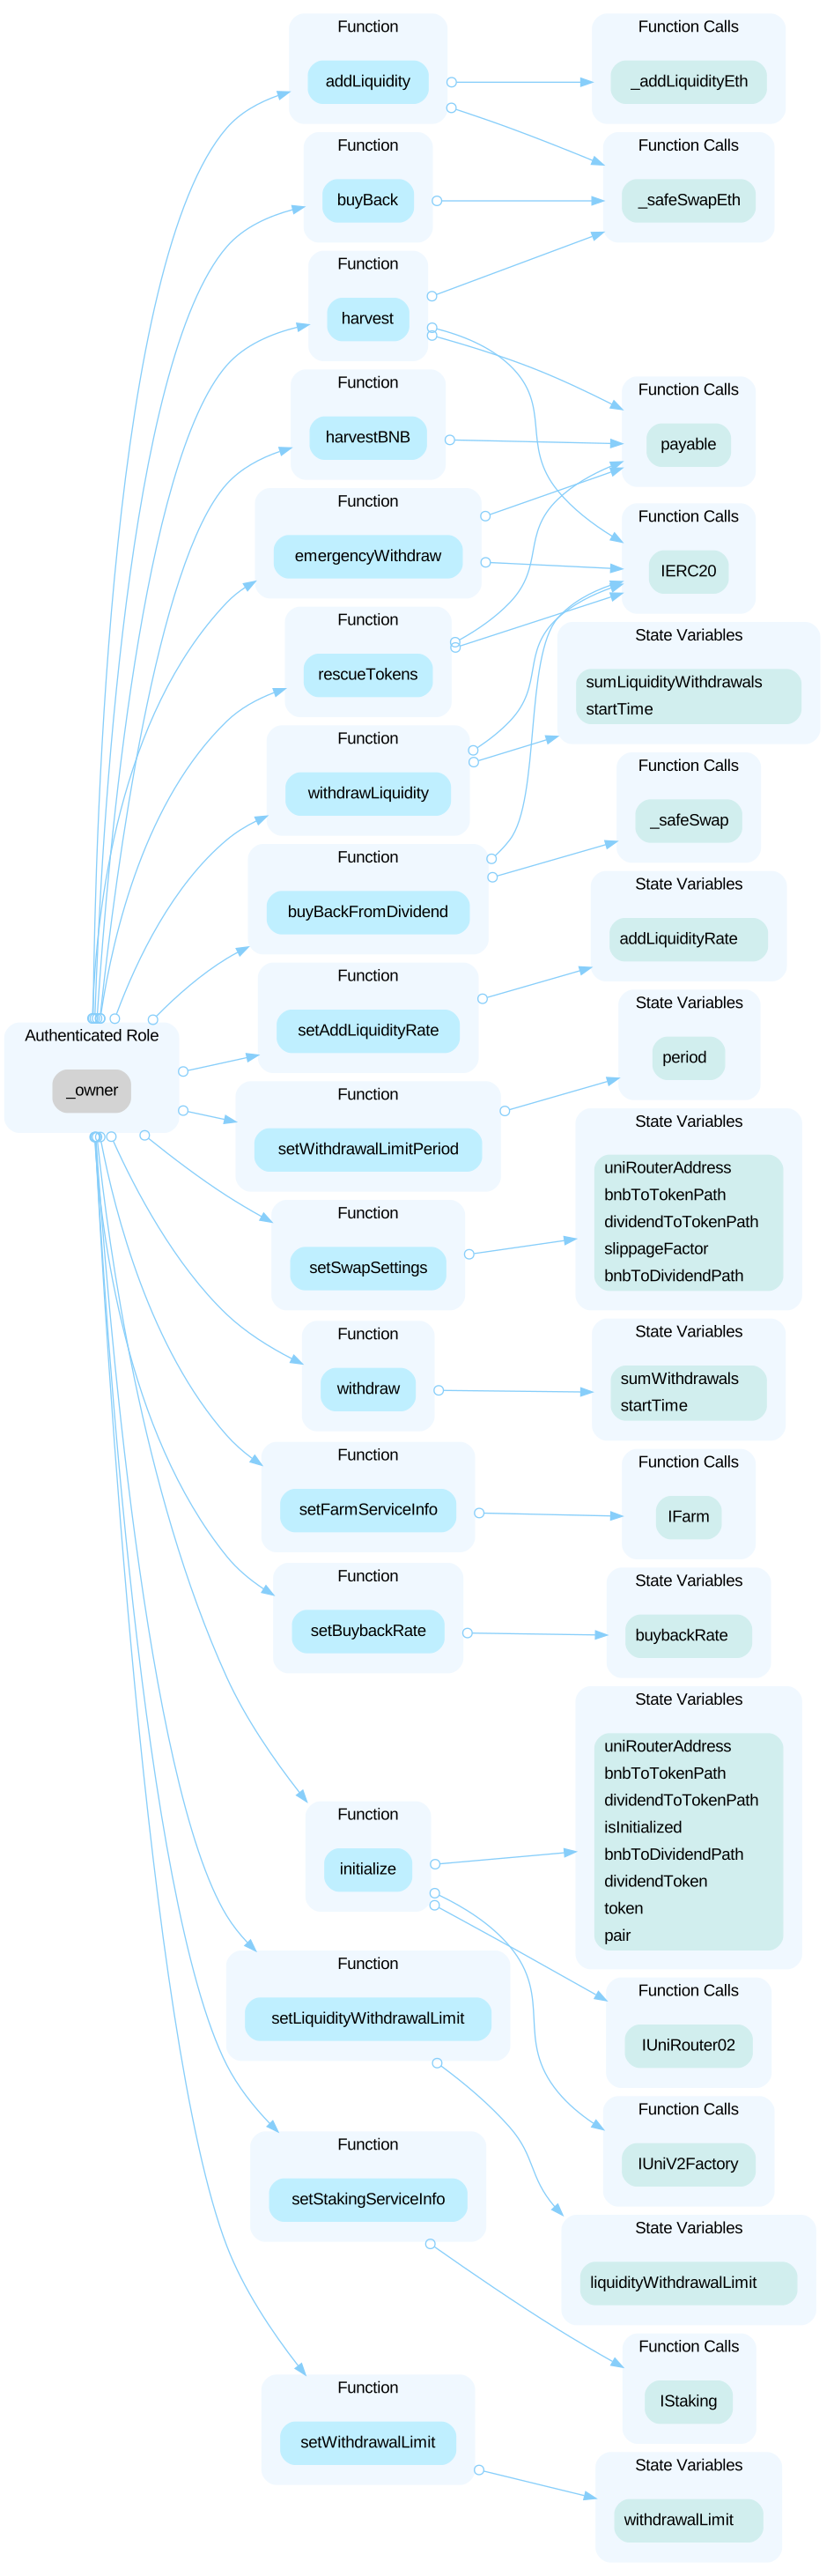
Open the reportThe report gives no description here.
Open the reportThe report gives no description here.
Open the reportThe report gives no description here.
Open the reportThe report gives no description here.
Open the reportThe function `BrewsMarketplace.supportsInterface()` is overridden and will consistently return `false`, which is unusual because it's designed to return true for supported interface identifiers.
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportRead-only reentrancy occurs when a contract makes external calls before updating its state variables. If another contract accesses these variables during the external call, it may operate on outdated information, leading to unexpected behavior.
Open the reportThe functions calling `_transferServiceFee()` are marked as payable, and there's a validation to ensure the input native token meets the minimum required amount. However, if the input native token exceeds this amount, the function currently lacks a mechanism to refund the excess. This oversight could lead to unintentional loss of funds for the called. Implementing a refund logic for the excess amount is crucial to prevent the potential loss of caller funds.
Open the reportThe contracts do not protect their initializers. An attacker can call the initializer and assume ownership of the logic contract, whereby she can perform privileged operations that trick unsuspecting users into believing that she is the owner of the upgradeable contract.
Open the reportThe report gives no description here.
Open the reportThe report gives no description here.
Open the reportThe report gives no description here.
Open the reportThe contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=376 uint256[] memory amounts = IUniRouter02(uniRouterAddress).getAmountsOut(_amountIn, _path); ``` ```solidity=381 IUniRouter02(uniRouterAddress).swapExactETHForTokensSupportingFeeOnTransferTokens{value: _amountIn}( ... ``` ```solidity=403 uint256[] memory amounts = IUniRouter02(uniRouterAddress).getAmountsOut(_amountIn, _path); ``` ```solidity=410 IUniRouter02(uniRouterAddress).swapExactTokensForTokensSupportingFeeOnTransferTokens( ... ``` ```solidity=437 (amountToken, amountETH, liquidity) = IUniRouter02(uniRouterAddress).addLiquidityETH{value: _ethAmt}( ... ``` - The contract `ZAH` interacts with third party contracts with `IUniRouter02` interface via `uniRouterAddress`. ```solidity=95 pair = IUniV2Factory(IUniRouter02(_uniRouter).factory()).getPair(_bnbToTokenPath[0], address(token)); ``` - The contract `BrewlabsTreasury` interacts with third party contracts with `IUniV2Factory` interface via `IUniRouter02(_uniRouter).factory()`.
Open the report| Address | Chain | Source code |
|---|---|---|
| 0x5c71…7d230x5c71e01556b01b6346a4435b145a15aa3a957d23 | Chain: BNB Chain | Source code: Verified source |
| 0xa681…53d90xa681c75ff9976f8559e2ca14e7b42bd9746a53d9 | Chain: BNB Chain | Source code: Verified source |
| 0x13bb…de1e0x13bbdbb16de07f4dc10c773061da92f4002fde1e | Chain: BNB Chain | Source code: Verified source |
| 0x9df9…43ad0x9df9d5a7597cd4bf781d4fa9b98077376f6643ad | Chain: BNB Chain | Source code: Verified source |
| 0xfe2b…38ff0xfe2bf5fc2d131db07c5ef7076856fd7f342738ff | Chain: BNB Chain | Source code: Verified source |
Trustblock holds 3 public audit reports for Brewlabs, dated 29 Aug 2022 to 3 Apr 2024. The latest is by CertiK (“Brewlabs Marketplace and PoolFactory”).
2 security firms wrote the reports Trustblock holds for Brewlabs: CertiK and Paladin.
19 findings are still open or acknowledged in the firms’ reports: 1 critical, 5 high, 2 medium, 11 low (14 open, 5 acknowledged). Of 2 critical findings: 1 open, 1 marked fixed. Statuses are the security firms’ own.
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="brewlabs"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us