
FortKnoxster DieFi security record
As of 3 Nov 2026, FortKnoxster DieFi has 2 audit reports by 2 security firms on Trustblock; the latest is by HashEx, dated 28 Sep 2022. Those reports list no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits2
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| FortKnoxster Token | Security firm: HashEx | Date: | Scope: 1 address on Ethereum | No open critical findings | Open · IPFS |
| FortKnoxster - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Findings4
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 2 |
HighCentralization Risks in `DieFiForwarder.sol` andFortKnoxster - Audit · CertiK · 23 Sep 2022Fixed
In the contract `DieFiForwarder` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below and the following functions: * `grantRole()` * `revokeRole()` Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and: * Pause or unpause the function `execute()` from executing meta transactions by the `RELAY_ROLE` address, with functions `pause()` and `unpause()`. * Grant or revoke the `RELAY_ROLE` to/from any address with functions `grantRole()` and `revokeRole()`. A user with the `DEFAULT_ADMIN_ROLE` also has the ability to grant/revoke this role to/from any address, and grant/revoke the `RELAY_ROLE` that is described below. 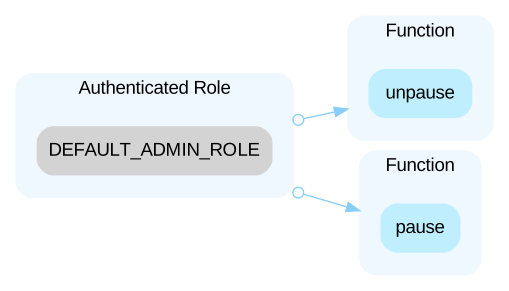 --- In the contract `DieFiForwarder` the role `RELAY_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `RELAY_ROLE` account may allow the hacker to take advantage of this authority and: * Verify a signature against the given `ForwardRequest` variables and execute the meta transaction in place of the signature signer. 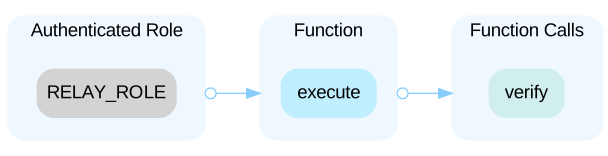 --- In the contract `DieFiPolicy` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below and the following functions: * `grantRole()` * `revokeRole()` Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and: * Grant or revoke the `DEFAULT_ADMIN_ROLE` to or from any address. The `DEFAULT_ADMIN_ROLE` has the ability to call the function described below. * Change the `subscriptionManager` address to any address with function `setSubscriptionManager()`. The `subscriptionManager` address is used throughout the contract to call external `policy` functions. 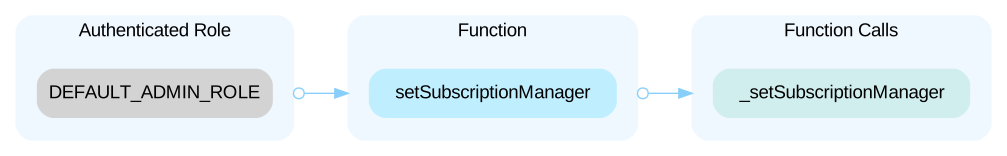
Open the reportLowChecks Effects Interaction Pattern ViolatedFortKnoxster - Audit · CertiK · 23 Sep 2022Fixed
A reentrancy attack can occur when the contract creates a function that makes an external call to another untrusted contract before resolving any effects. If the attacker can control the untrusted contract, they can make a recursive call back to the original function, repeating interactions that would have otherwise not run after the external call resolved the effects. If a recursive call is preformed on either function `execute()` or `createPolicy()`, the ordering of events emitted will be inaccurate compared to the actual execution timeline of the external calls. ### External call ```solidity=62 (bool success, bytes memory returndata) = req.to.call{gas: req.gas, value: req.value}( abi.encodePacked(req.data, req.from) ); ``` ### Events emitted after the call ```solidity=78 emit MetaTransactionExecuted(req.from, req.to, req.data); ``` --- ### External call ```solidity=66 ISubscriptionManager(subscriptionManager).createPolicy{value: msg.value }( _policyId, _policyOwner, _size, _startTimestamp, _endTimestamp ); ``` ### Events emitted after the call ```solidity=74 emit DieFiPolicyCreated( _policyId, _policyOwner, _size, _startTimestamp, _endTimestamp, msg.value ); ```
Open the reportLowFunction Should Be Declared ExternalFortKnoxster - Audit · CertiK · 23 Sep 2022Fixed
The functions which are never called internally within the contract should have external visibility for gas optimization.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0x16484d73ac08d2355f466d448d2b79d2039f6ebb | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="fortknoxster"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us