
GigaSwap security record
As of 3 Nov 2026, GigaSwap has 1 audit report on Trustblock, by CertiK, dated 7 Feb 2024. That report lists no open critical findings.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Gigaswap - Audit | Security firm: CertiK | Date: | Scope: Files named in the report | 1 critical finding, fixed | Open · skynet.certik.com |
Findings30
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 2 | 0 | 3 |
| Medium | 0 | 0 | 8 |
| Low | 3 | 0 | 13 |
HighCentralization Related RisksGigaswap - Audit · CertiK · 7 Feb 2024Open
In the contract `Farming` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 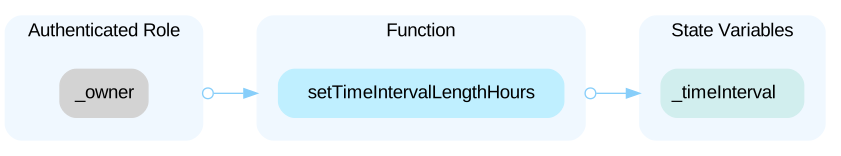 In the contract `FeeSettings` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 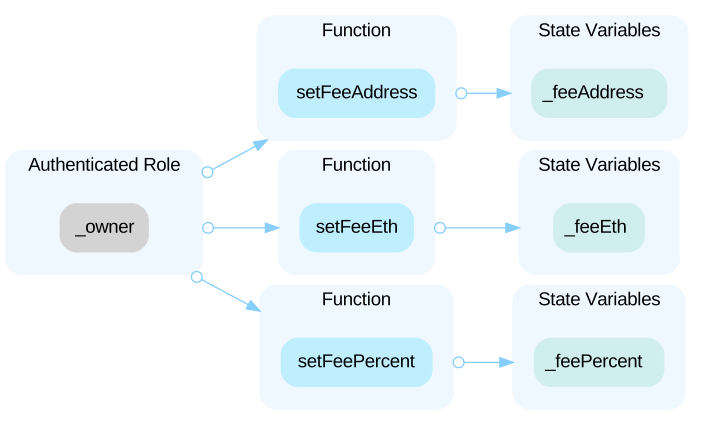 In the contract `FeeSettingsWriter` the role `_factory` has authority over the functions shown in the diagram below. Any compromise to the `_factory` account may allow the hacker to take advantage of this authority. 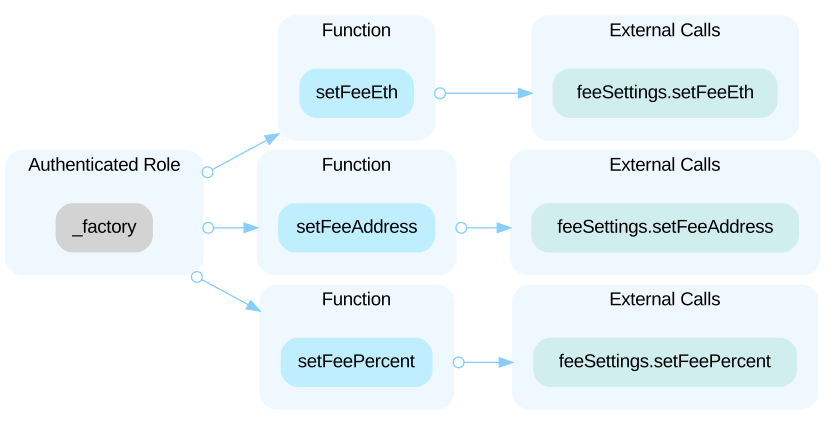 In the contract `FeeSettingsWriter` the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage of this authority. 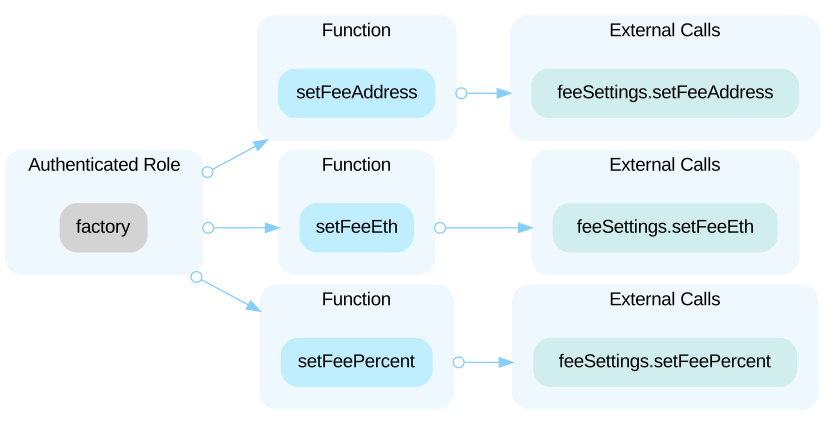 In the contract `Erc20Sale` the role `antibot` has authority over the functions shown in the diagram below. Any compromise to the `antibot` account may allow the hacker to take advantage of this authority. 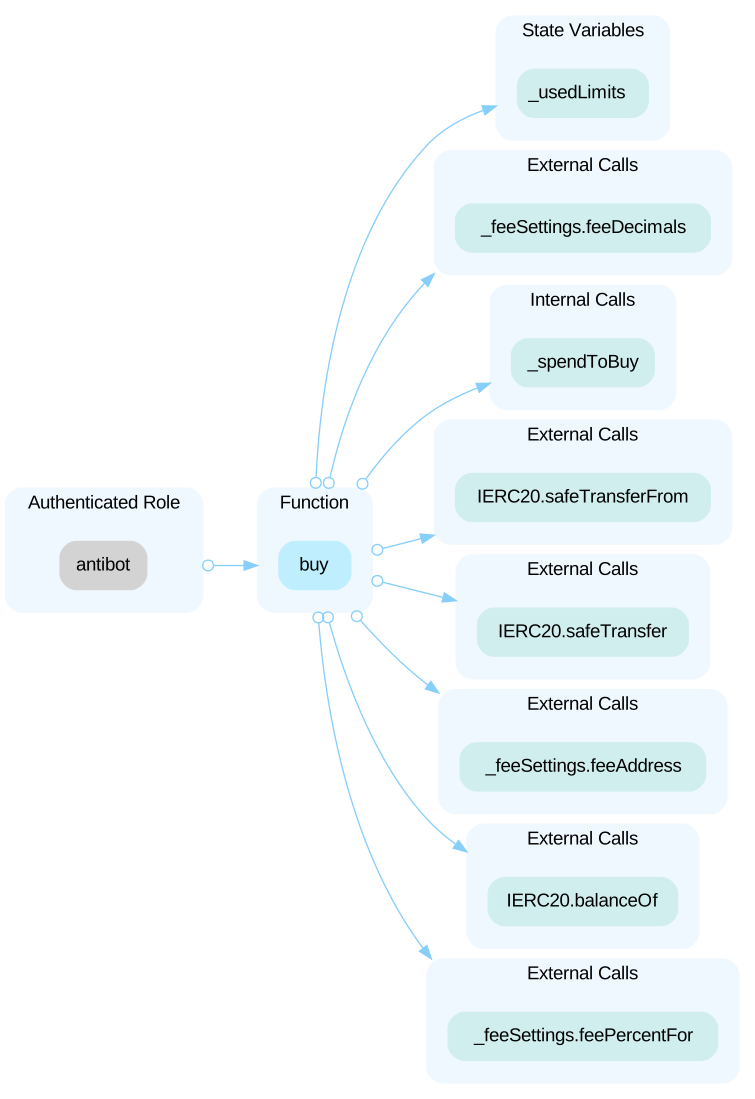 In the contract `Erc20SaleWeth` the role `antibot` has authority over the functions shown in the diagram below. Any compromise to the `antibot` account may allow the hacker to take advantage of this authority. 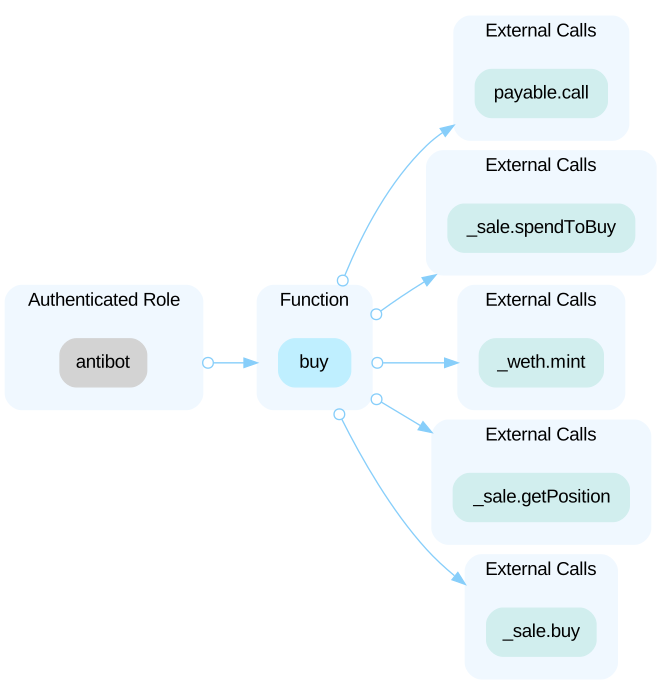 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 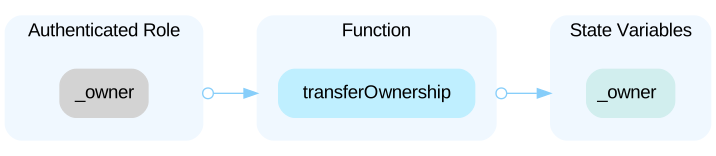 In the contract `TradableErc20` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 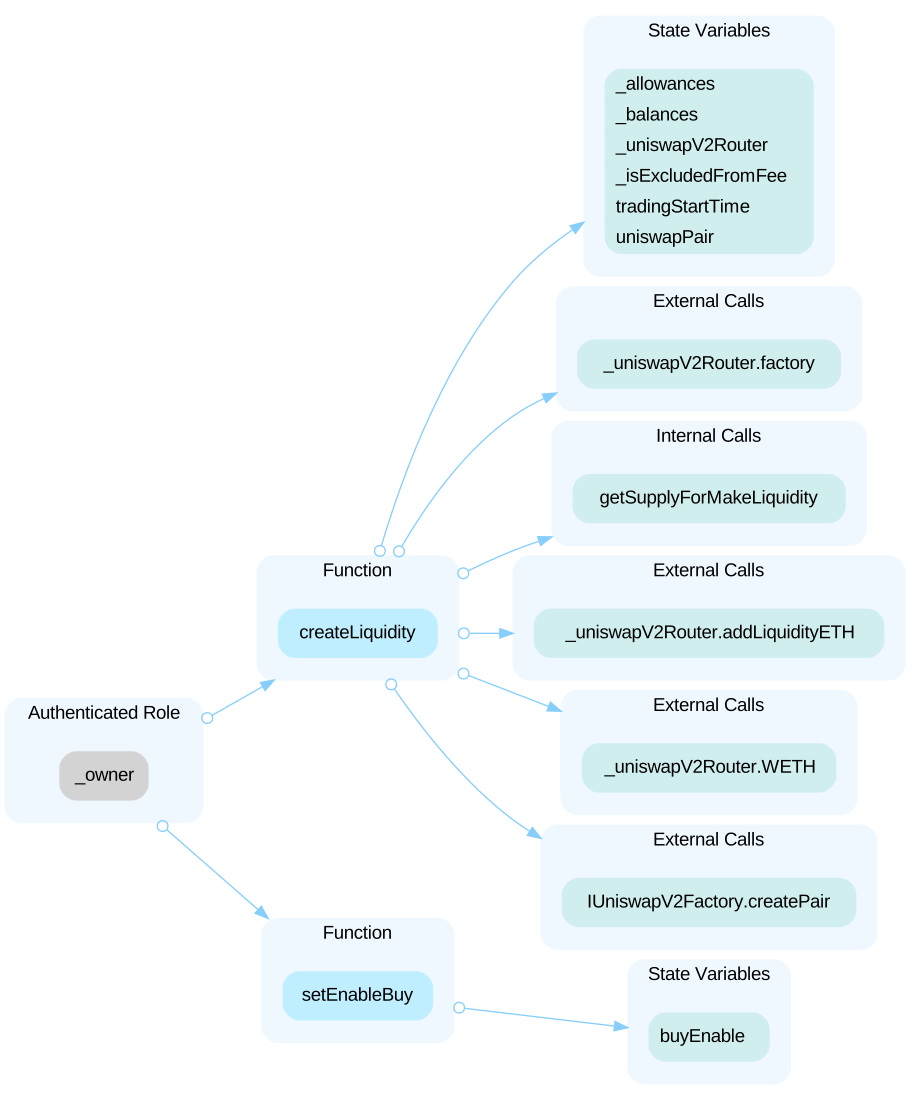 In the contract `TradableErc20` the role `_withdrawAddress` has authority over the functions shown in the diagram below. Any compromise to the `_withdrawAddress` account may allow the hacker to take advantage of this authority. 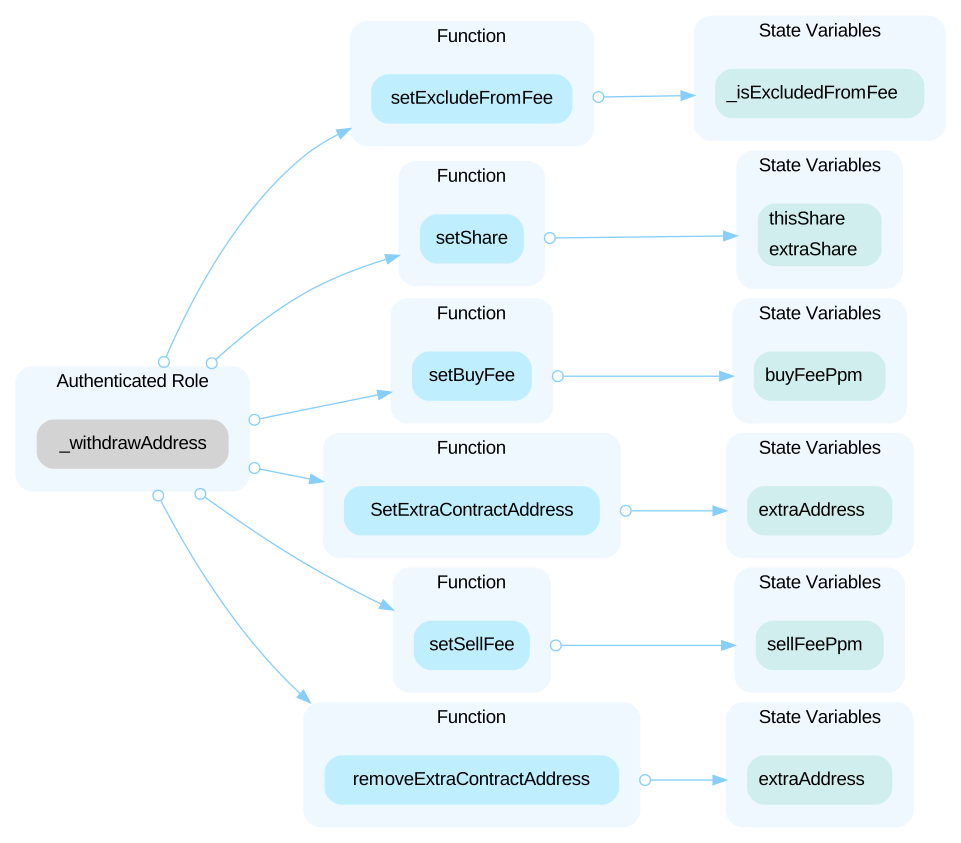 In the contract `TradableErc20` the role `_withdrawer` has authority over the functions shown in the diagram below. Any compromise to the `_withdrawer` account may allow the hacker to take advantage of this authority. 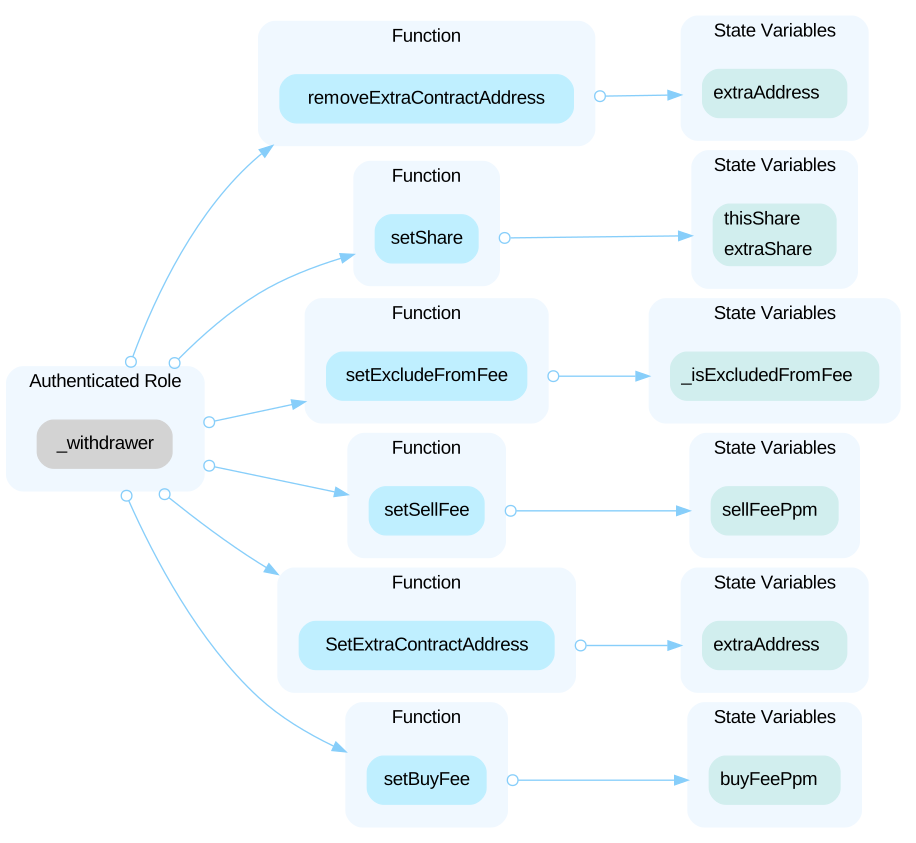 In the contract `Withdrawable` the role `_withdrawAddress` has authority over the functions shown in the diagram below. Any compromise to the `_withdrawAddress` account may allow the hacker to take advantage of this authority. 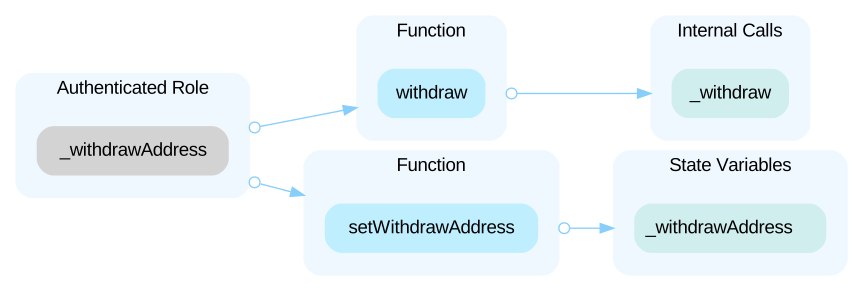 In the contract `Withdrawable` the role `_withdrawer` has authority over the functions shown in the diagram below. Any compromise to the `_withdrawer` account may allow the hacker to take advantage of this authority. 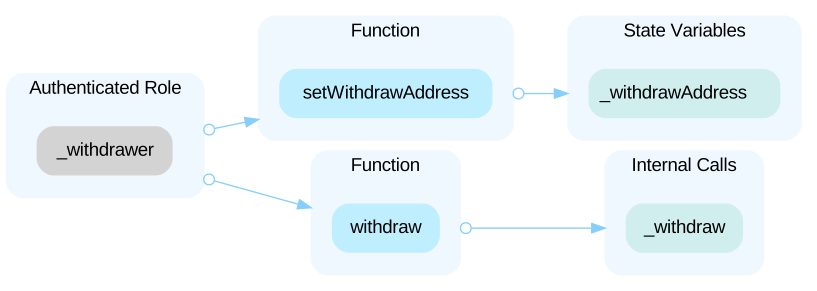 In the contract `Erc20ForFactory` the role `_factory` has authority over the functions shown in the diagram below. Any compromise to the `_factory` account may allow the hacker to take advantage of this authority. 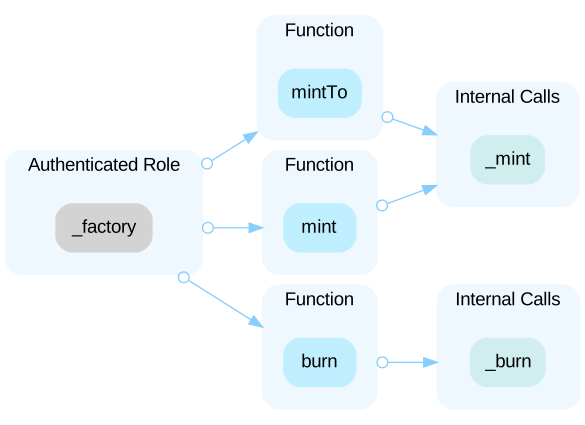 In the contract `Erc20ForFactory` the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage
Open the reportHighFunction `allowance` of Contract `gWETH` ReturnsGigaswap - Audit · CertiK · 7 Feb 2024Open
It is expected that calls of the form `allowance(owner, spender)` return the allowance that address `spender` has over tokens held by address `owner`. However, the implementation of `allowance` in contract `gWETH` returns different values when the `_withoutAllowance[spender]` is `true`. The owner address has the privilege to assign as many addresses as possible to have a max allowance returned no matter what the owner address is.
Open the reportLowDiscussion on `antibot` addressGigaswap - Audit · CertiK · 7 Feb 2024Open
In the contracts `Erc20Sale` and `Erc20SaleWeth`, we noticed that there is an input address called `antibot` in the `buy()` functions. The `antibot` address is used to check if the `msg.sender` is equal to the `antibot` address. From the naming of `antibot` we guess the purpose is to not allow smart contracts to call the address? If so, the current implementation of `require(msg.sender == antibot, 'antibot')` will not help.
Open the reportLowLack of DocumentationGigaswap - Audit · CertiK · 7 Feb 2024Open
The Gigaswap contract lacks comments, natspec, or documentation explaining the specific use case of each function.
Open the reportLowPotential Flashloan AttackGigaswap - Audit · CertiK · 7 Feb 2024Open
Flash loans are a way to borrow large amounts of money for a certain fee. The requirement is that the loans need to be returned within the same transaction in a block. If not, the transaction will be reverted. The `feePercentFor()` and `feeEthFor()` function relies on the balance of gigaToken that are based on-chain, meaning they are susceptible to flash-loan attacks by borrowing money to increase the account amount.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="gigaswap"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us