Incident
Incident,
Source: De.Fi incident database.
- Audits before it
- 4.
- Audits since
- None on Trustblock.

As of 3 Nov 2026, Hashflow has 4 audit reports by 3 security firms on Trustblock; the latest is by Quantstamp, dated 22 Mar 2023. Those reports list no open critical findings. It also holds 2 deployed contracts on 2 chains and 1 incident (latest 13 Jun 2023).
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Hashflow Hashverse | Security firm: Quantstamp | Date: | Scope: Files named in the report | No open critical findings | Open · certificate.quantstamp.com |
| Hashflow Token | Security firm: HashEx | Date: | Scope: 2 addresses on Ethereum and BNB Chain | No open critical findings | Open · hashex.org |
| Hashflow Token | Security firm: HashEx | Date: | Scope: 1 address on Ethereum | No open critical findings | Open · IPFS |
| Hashflow-Audit3 | Security firm: CertiK | Date: | Scope: Files named in the report | No open critical findings | Open · skynet.certik.com |
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 1 |
| Medium | 0 | 0 | 1 |
| Low | 3 | 5 | 20 |
In the contract `HashflowFactory` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set contract addresses used to create a new pool. 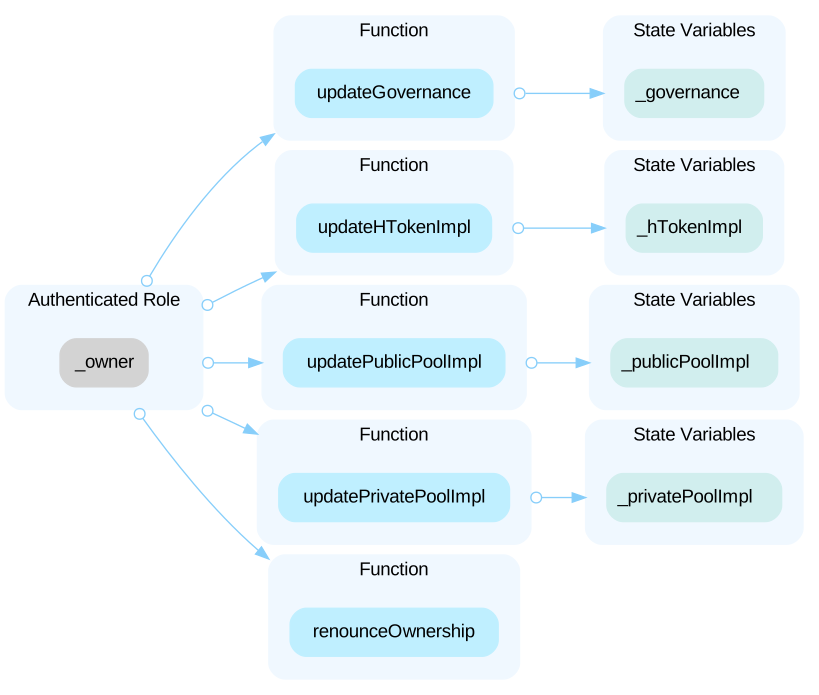 In the contract `HashflowGovernance` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify critical parameters of the Hashflow protocol. 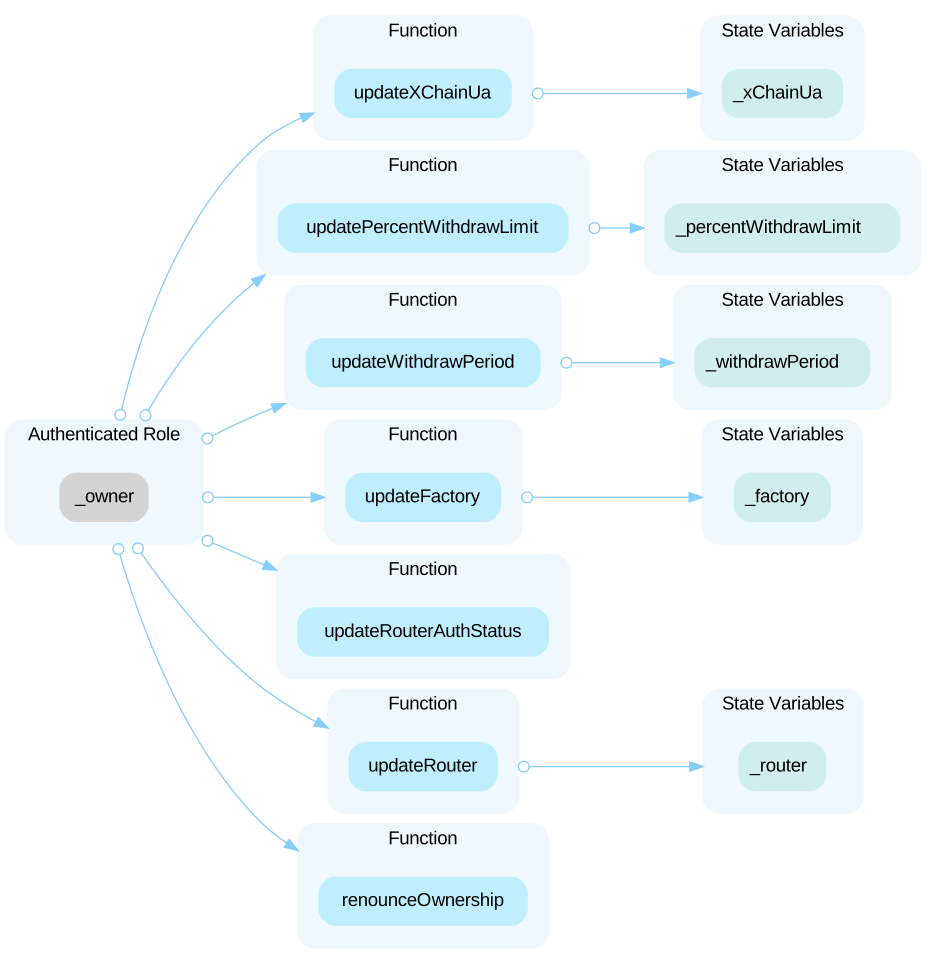 In the contract `HashflowRouter` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and withdraw funds from the router. 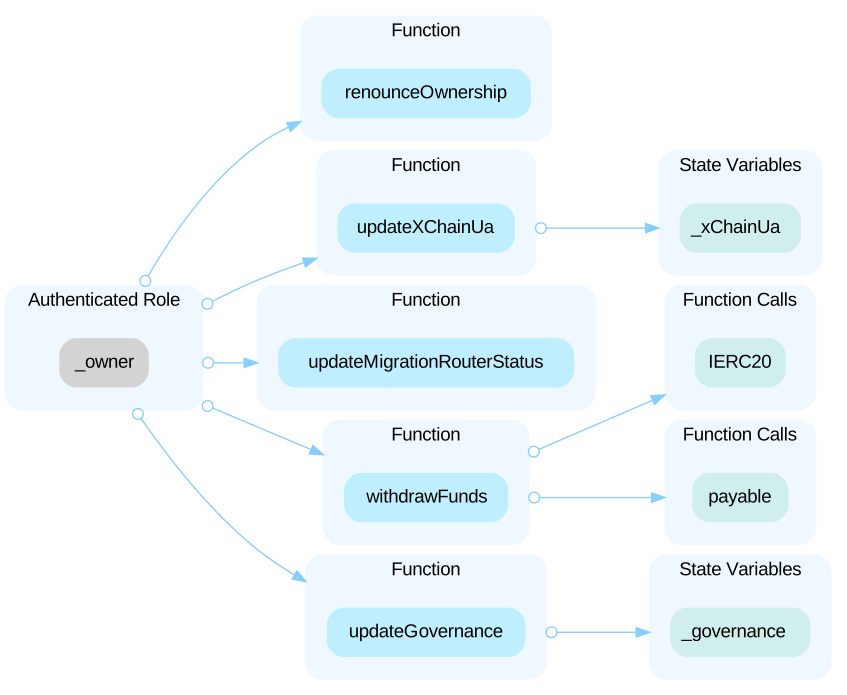 Furthermore, the role `factory` has authority over the functions shown in the diagram below. Any compromise to the `factory` account may allow the hacker to take advantage of this authority and add/remove authorized pools. 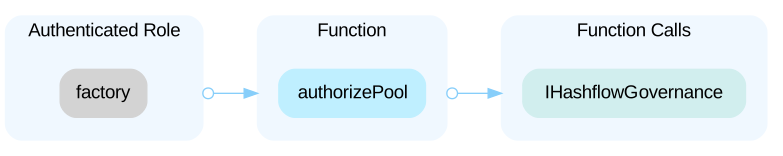 In the contract `HashflowPool` the role `_operations` has authority over the functions shown in the diagram below. Any compromise to the `_operations` account may allow the hacker to take advantage of this authority and update pool properties and drain the funds. 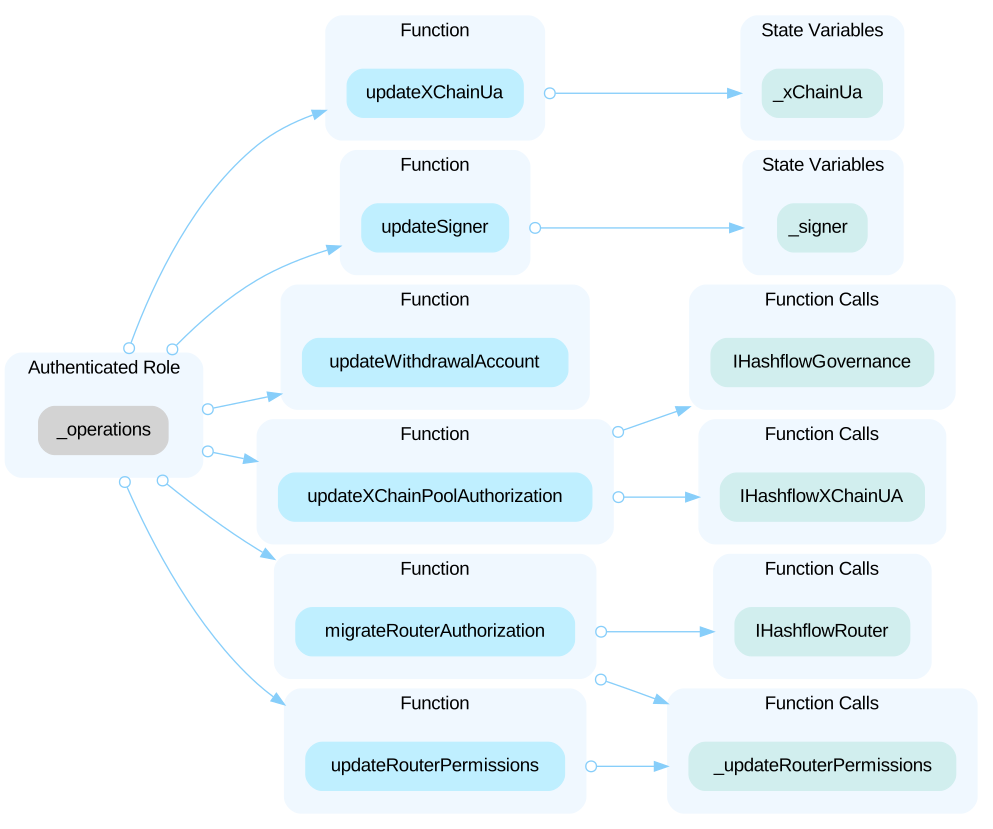 In the contract `HashflowPrivatePool` the role `_authorizedRouter` has authority over the functions shown in the diagram below. Any compromise to the `_authorizedRouter` account may allow the hacker to take advantage of this authority. 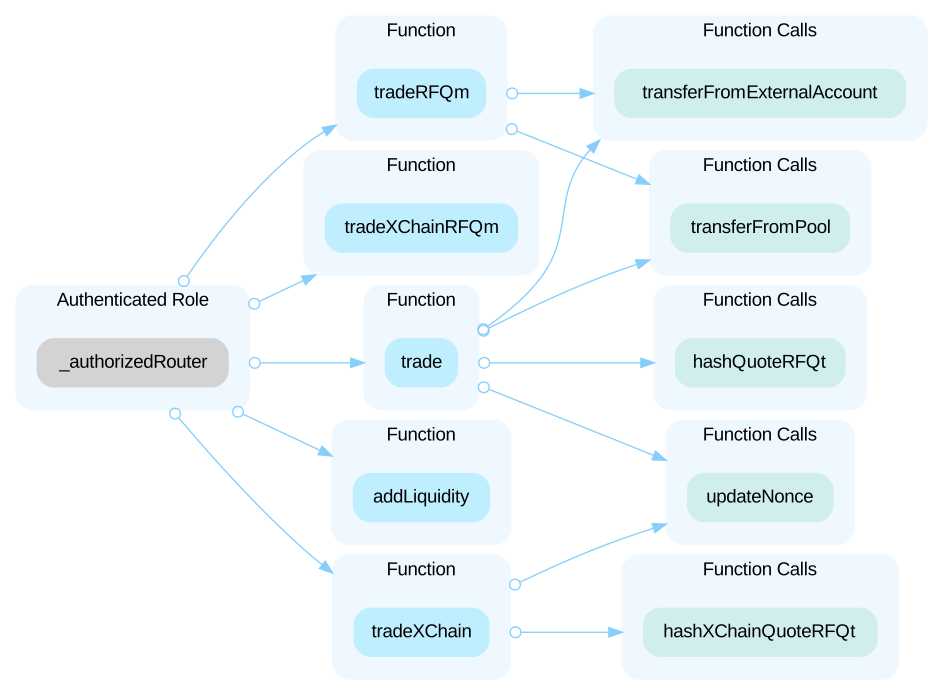 Furthermore, the role `_operations` has authority over the functions shown in the diagram below. Any compromise to the `_operations` account may allow the hacker to take advantage of this authority and remove pool liquidity. 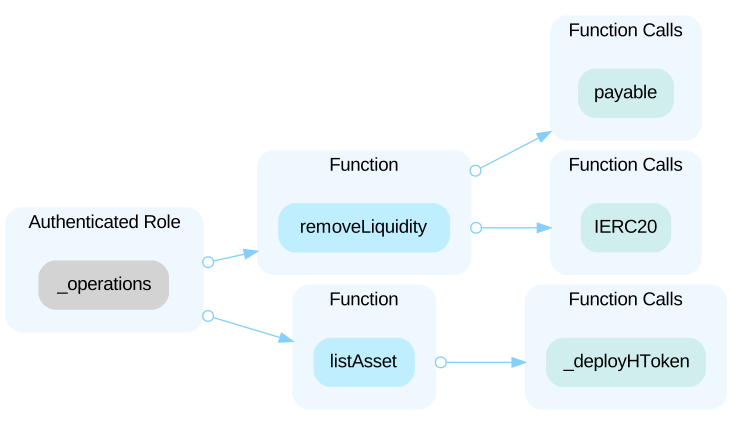 Additionally, the role `_xChainUa` has authority over the functions shown in the diagram below. Any compromise to the `_xChainUa` account may allow the hacker to take advantage of this authority and withdraw funds from the pool. 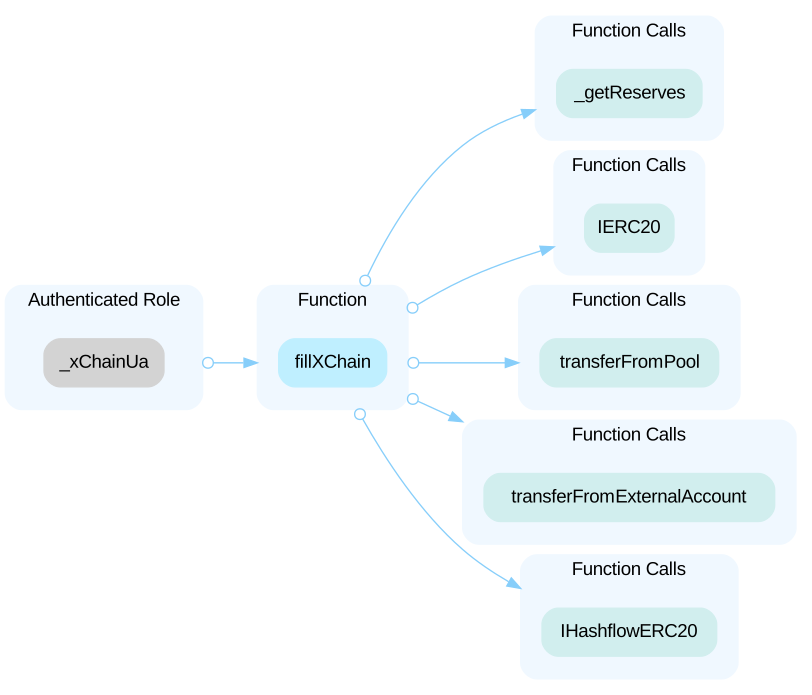 In the contract `HashflowPublicPool` the role `_authorizedRouter` has authority over the functions shown in the diagram below. Any compromise to the `_authorizedRouter` account may allow the hacker to take advantage of this authority and remove pool liquidity. 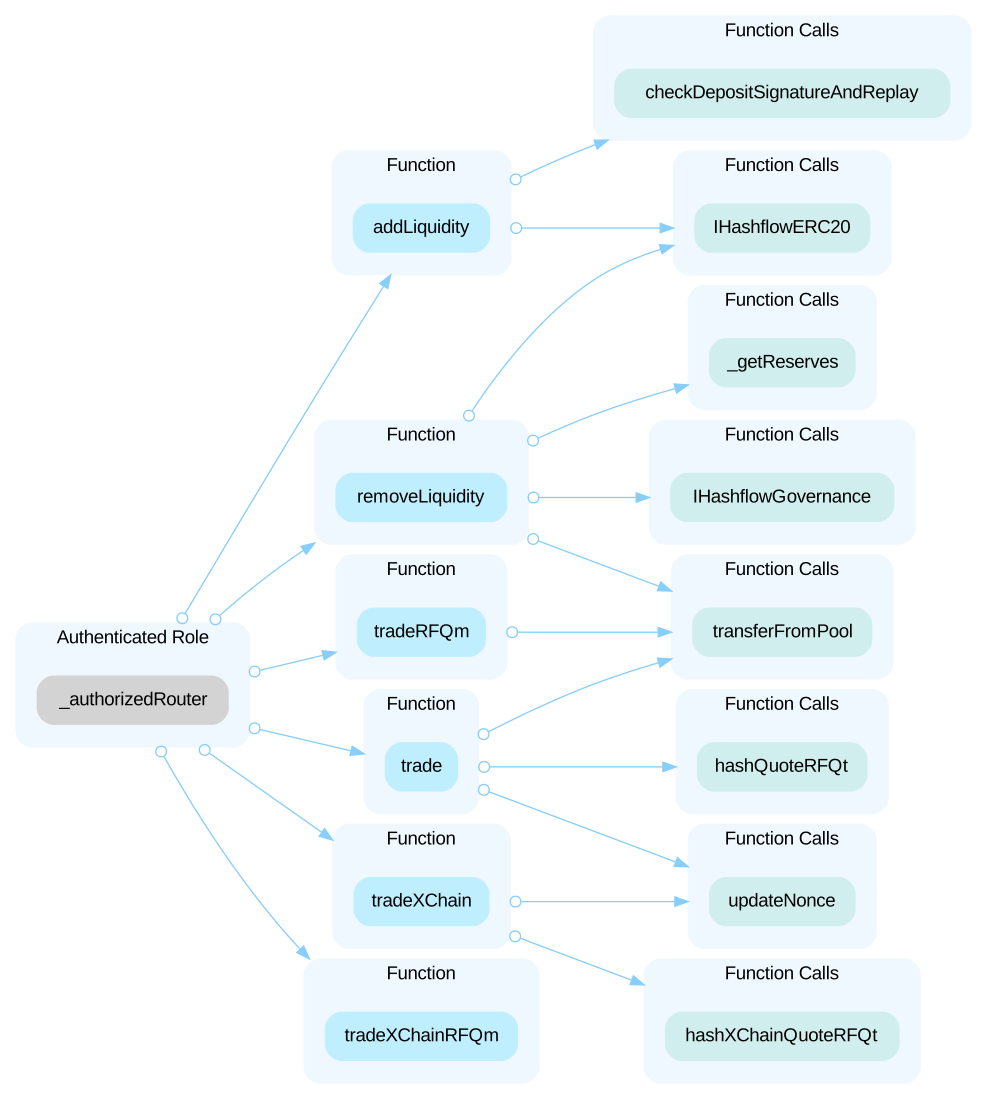 Furthermore, the role `_operations` has authority over the functions shown in the diagram below. Any compromise to the `_operations` account may allow the hacker to take advantage of this authority and withdraw funds from the pool. 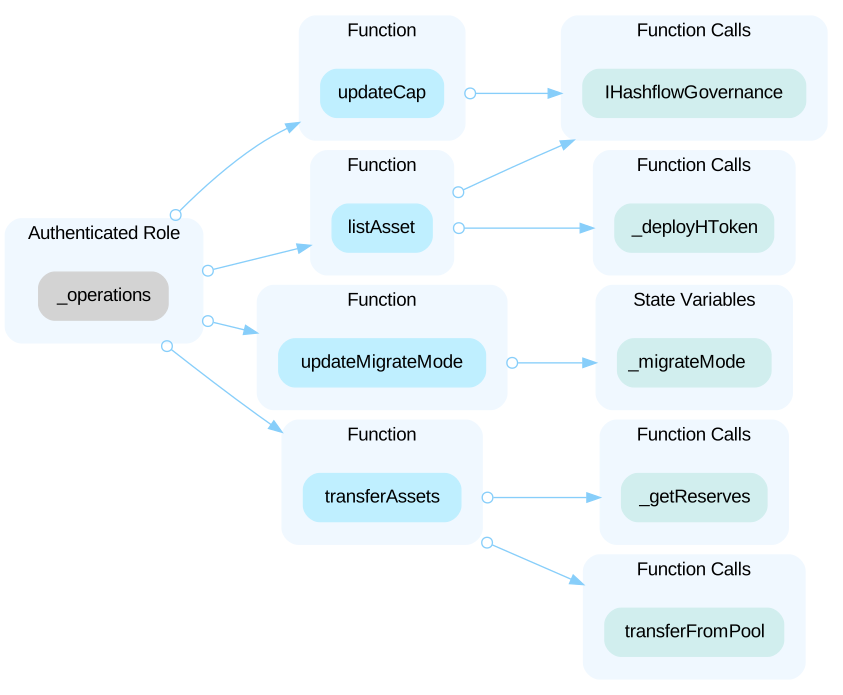 Additionally, the role `_xChainUa` has authority over the functions shown in the diagram below. Any compromise to the `_xChainUa` account may allow the hacker to take advantage of this authority and withdraw funds from the pool. 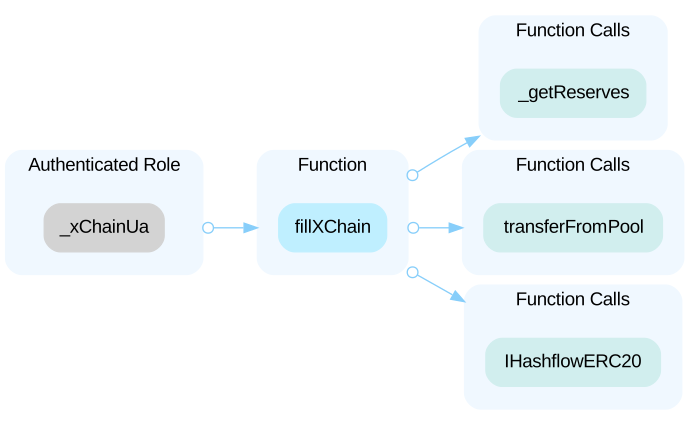 Finally, regarding the contract `HashflowPublicPool`, the role `_withrawalAccountAuth` has authority over the function `transferAssets()`. Any compromise to the `_withrawalAccountAuth` account may allow the hacker to take advantage of this authority and withdraw funds from the pool. In the contract `HashflowXChainUA` the role `_lzEndpoint` has authority over the functions shown in the diagram below. Any compromise to the `_lzEndpoint` account may allow the hacker to take advantage of this authority and withdr
Open the reportProjects may rely on block timestamps for various purposes. Given the cross-chain nature of this application, it is important to note that different networks may impose different requirements for their validators when it comes to setting the timestamp of a block, and attackers may be able to manipulate timestamps for their own purposes. If a smart contract relies on a timestamp, it must take this into account.
Open the reportIn discussion with the client, it was determined that the vast majority of user interactions with the dApp will occur in off-chain components, meaning the proper functioning of the system as a whole largely depends on off-chain code that is not within the scope of this audit. This makes it difficult for us to evaluate the risks associated with interacting with the application, especially when there is a lack of documentation for these off-chain computations (e.g. quest reward mechanism, Merkle tree computations). Furthermore, the cross-chain component of the application will be facilitated by a relaying system that is not within the scope of this audit.
Open the reportIn discussion with the Hashflow team, we learned that they plan to operate specialized Wormhole relayers and have the client relay the VAA as a fallback measure. It should be noted that the current implementation does not work with the [generic relayer](https://book.wormhole.com/technical/relayer/genericRelayer.html), which is currently only available on testnet. The generic relayer system requires that there is a function in the target contract on the destination chain called `receiveWormholeMessages()` as an entry point for execution. However, this function is not implemented in contracts that receive VAAs from Wormhole, e.g. `RenovaAvatarSatellite` and `RenovaItemBase`. For a reference implementation, see the last section of the Wormhole documentation on Best Practices [here](https://book.wormhole.com/technical/evm/bestPractices.html). This would additionally require proper use of nonces, as they are used to batch VAAs before they are relayed. However, they are currently hardcoded to zero.
Open the reportThe report gives no description here.
Open the reportNo description was provided.
Open the reportAttached through a shared contract address. Our incident data ends in Oct 2026.
Source: De.Fi incident database.
| Address | Chain | Source code |
|---|---|---|
| 0xb3999f658c0391d94a37f7ff328f3fec942bcadc | Chain: BNB Chain | Source code: Verified source |
| 0xb3999f658c0391d94a37f7ff328f3fec942bcadc | Chain: Ethereum | Source code: Verified source |
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="hashflow"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us