
Memecoin security record
As of 3 Nov 2026, Memecoin has 1 audit report on Trustblock, by CertiK, dated 27 Nov 2023. That report lists no open critical findings.
Record last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Audits1
Newest first
Findings13
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 7 | 0 | 2 |
HighCentralization Related RisksMemeland · CertiK · 27 Nov 2023Acknowledged
In the contract `MemecoinFiresaleV1` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and perform, including but not limited to, the following: - Modify the state of the Firesale at will. - Change the address of the `signer`. - Change the address of the `upgrader`. - Withdraw a certain amount of ETH that is available when the firesale is `FINISHED`. - Modify the `unitPrice` and `bulkSaleUnits` price. - Set a different contract upgrader. - Modify the refund start date to any date. - Withdraw the unclaimed refund. 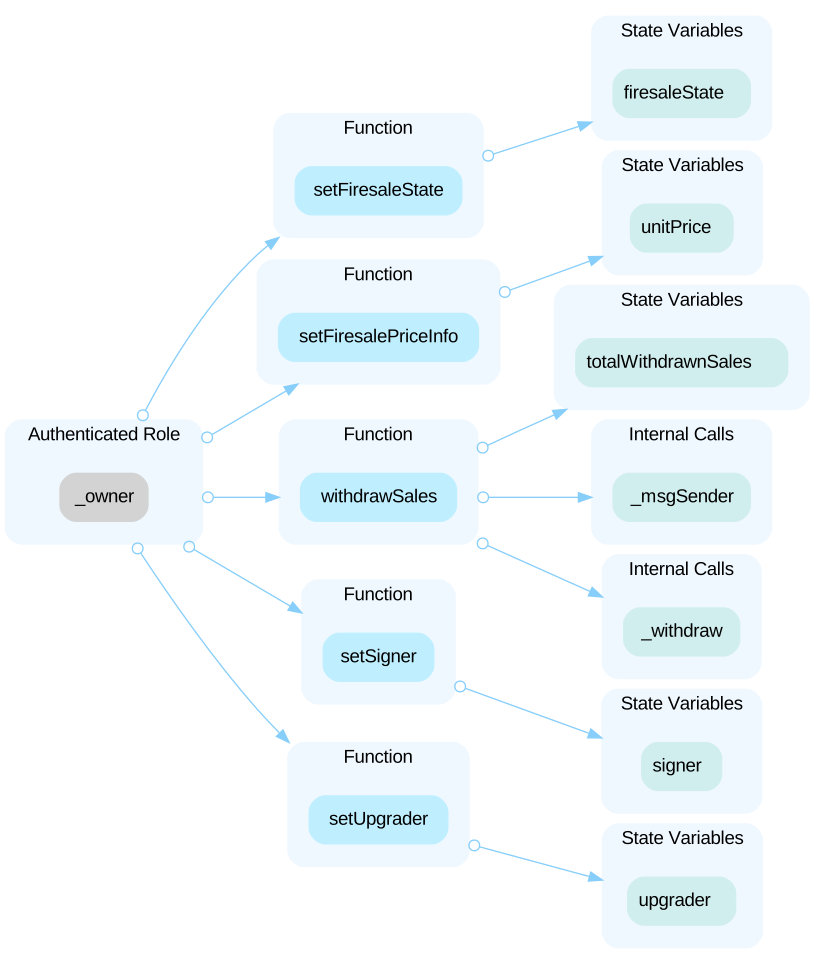 Moreover, the `signer` account has the authority to authorize the `reserve` and `refund` calls by eligible accounts by issuing valid signatures. Any compromise to this authority may allow an hacker to leverage it and authorize the reserve and the refund to arbitrary accounts. In the contract `MemecoinClaim` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - Arbitrarily set a start claim date. - Withdraw the contract reserves. - Alter the claim schedule. - Add basis points for a claim type. - Add new addresses eligible for the claim. - Set a different claim token address. - Add new claimable NFT tokens. - Airdrop NFT and fungible tokens. - Set a different contract upgrader. 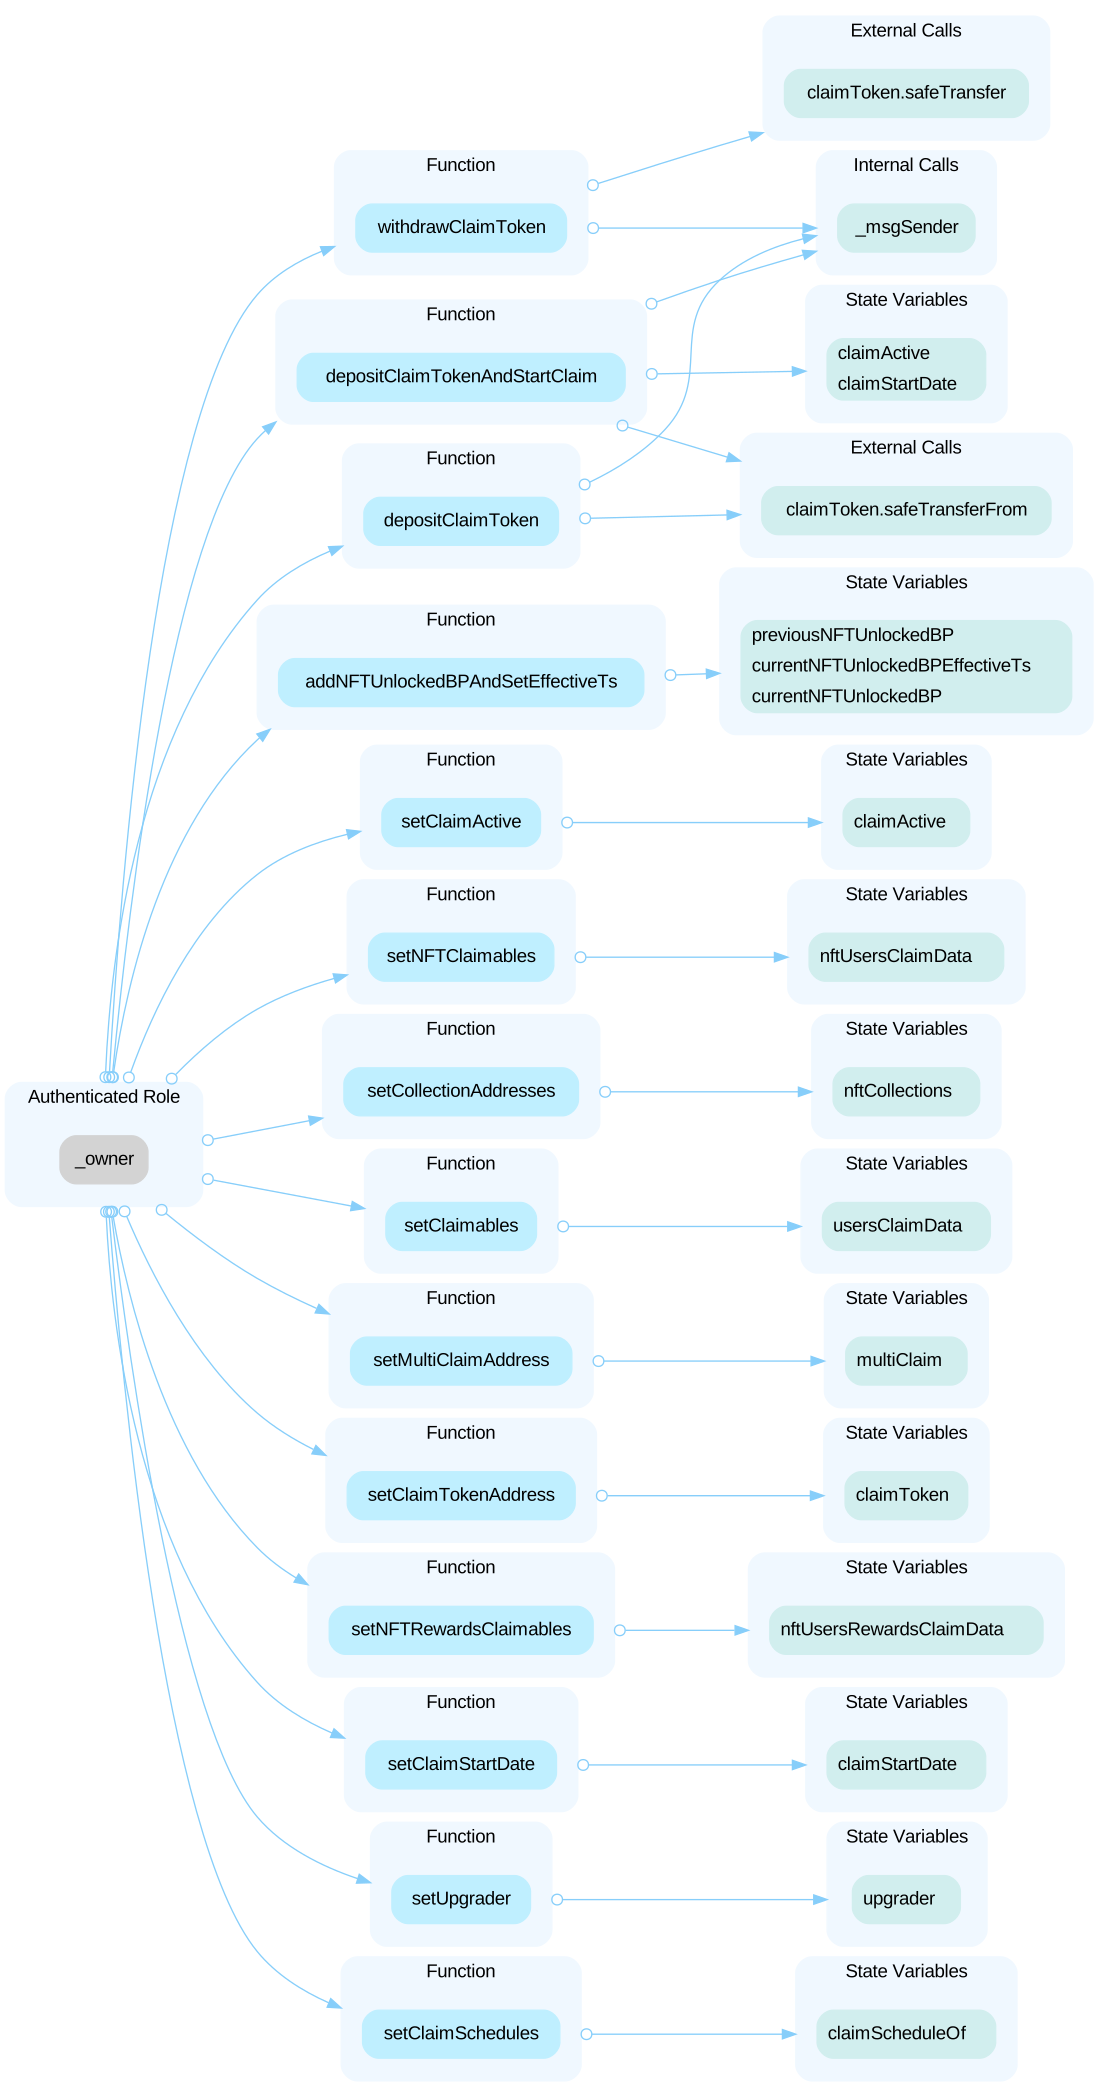 In the contract `Memecoin` the role `_owner` has authority over the function `setTokenPool`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the `tokenPool` address at will.
Open the reportHighCentralized Control of Contract UpgradeMemeland · CertiK · 27 Nov 2023Acknowledged
In the contracts `MemecoinFiresaleV1` and `MemecoinClaim` the account `upgrader` has the authority to update the implementation contract. Any compromise to the `upgrader` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the proxy contract storage.
Open the reportHighInitial Token DistributionMemeland · CertiK · 27 Nov 2023Acknowledged
All of the tokens tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="memeland"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us