
Miracle Play audit reports
Miracle Play has 1 public audit report from CertiK; dated 21 Jun 2024; 1 critical finding, marked fixed by the firm. It also holds 3 deployed contracts on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm7
Statuses are the security firms’ own
7 findings are still open or acknowledged in the firms’ reports: 3 high, 4 low (3 open, 4 acknowledged).
- High
- 3
- Low
- 4
- High Open
Centralization Risks
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- High Open
Centralized Control of Contract Upgrade
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- High Open
Minting and Claiming Centralization Risks
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- Low Acknowledged
Cross Chain Swap Dependencies
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- Low Acknowledged
Missing Zero Address Validation
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- Low Acknowledged
Redundant Code Components
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
- Low Acknowledged
Third-Party Dependency Usage
Miracle Play - Audit · CertiK · 21 Jun 2024 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Miracle Play - Audit | Security firm: CertiK | Date: | Scope: 3 addresses on Polygon (POS) | 1 critical finding, fixed | Findings: 1 critical · 4 high · 5 medium · 6 low 9 fixed · 4 acknowledged · 3 open | skynet.certik.com ↗ |
Findings16
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 3 | 0 | 1 |
| Medium | 0 | 0 | 5 |
| Low | 0 | 4 | 2 |
HighCentralization RisksMiracle Play - Audit · CertiK · 21 Jun 2024Open
In the contract `TokenMigrateERC20` the role `MIGRATION_ROLE` has authority over the functions `setMerkleRoot()`. Any compromise to the `MIGRATION_ROLE` account may allow the hacker to take advantage of this authority and change the `ownershipMerkleRoot`. In the contract `TokenERC20M` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set `primarySaleRecipient`, `platformFeeBps`, `platformFeeRecipient`, and `contractURI`. 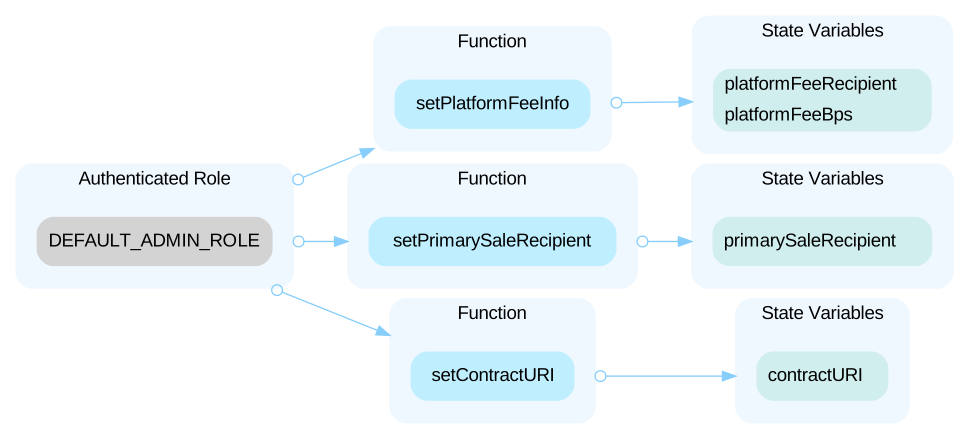 In the contract `BridgeCore` the role `DEFAULT_ADMIN_ROLE` has authority over the functions `changeFeeRecipient()`. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and change the `feeRecipient`. In the contract `ERC1155Staking` the role `DEFAULT_ADMIN_ROLE` has authority over the functions as follows: - `adminUnstakeUser()`, to unstake tokens on behalf of a user. - `adminUnstakeAll()`, to unstake all tokens from all users. - `confiscateERC1155FromUser()`, to confiscate staked ERC-1155 tokens from a specific user. - `setDaoAddress()`, to change the value of `daoAddress`. - `setManagerFeeWallet()`, to change the value of `ManagerWallet`. - `setDAOFeePercentage()`, to change the value of `DAO_FEE_PERCENTAGE`. - `setFeeManagerPercentage()`, to change the value of `MANAGER_FEE_PERCENTAGE`. - `setAgentFeePercentage()`, to change the value of `AGENT_FEE_PERCENTAGE`. - `setPoolStartTime()`, to change the value of `poolStartTime`. - `setPoolFinished()`, to change the value of `POOL_FINISHED`.
Open the reportHighCentralized Control of Contract UpgradeMiracle Play - Audit · CertiK · 21 Jun 2024Open
In the contract `Bridge`, the role admin has the authority to update the implementation contract behind the `Bridge` contract. Any compromise to the admin account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Open the reportHighMinting and Claiming Centralization RisksMiracle Play - Audit · CertiK · 21 Jun 2024Open
In the contract `TokenERC20M` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint any amount of tokens to any address. 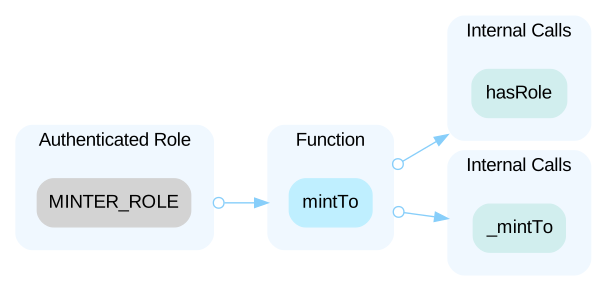 In the contract `BridgeCore` the role `minterAndBurnerRole` has authority over the functions as follows: - `sendERC1155ToUser()`, to mint Drop1155 to order receiver. - `sendERC20ToUser()`, to mint TokenERC20 to order receiver. Any compromise to the `minterAndBurnerRole` account may allow the hacker to take advantage of this authority. In the contract `ERC1155Staking` the role `FACTORY_ROLE` has authority over the functions `claimAgent()`. Any compromise to the `FACTORY_ROLE` account may allow the hacker to take advantage of this authority and claim the reward for a user.
Open the reportContracts3
| Address | Chain | Source code |
|---|---|---|
| 0x5755241a4c8afef6166b1fa361294222eff0ea88 | Chain: Polygon (POS) | Source code: Verified source |
| 0x87d6f8edeccbcca766d2880d19b2c3777d322c22 | Chain: Polygon (POS) | Source code: Verified source |
| 0x625d3fd726cc86f1463b50376dec62359d61a1f0 | Chain: Polygon (POS) | Source code: Verified source |
Miracle Play: questions
Is Miracle Play audited?
Trustblock holds 1 public audit report for Miracle Play, dated 21 Jun 2024. The latest is by CertiK (“Miracle Play - Audit”).
Who audited Miracle Play?
CertiK wrote the report Trustblock holds for Miracle Play.
Are there open findings in Miracle Play’s audits?
7 findings are still open or acknowledged in the firms’ reports: 3 high, 4 low (3 open, 4 acknowledged). Of 1 critical finding: marked fixed by the firm. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="miracle-play"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us