
Moret audit reports
Moret has 1 public audit report from CertiK; dated 22 Sep 2022; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm10
Statuses are the security firms’ own
10 findings are still open or acknowledged in the firms’ reports: 2 high, 8 low (all open).
- High
- 2
- Low
- 8
- High Open
Centralization Risks
Moret · CertiK · 22 Sep 2022 · Report ↗
- High Open
Initial Token Distribution
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Ambiguous Error Messages and Events
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Commented Out Code
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Missing Error Messages
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Third Party Dependency
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Unchecked Value of ERC-20 `transfer()`/`transferF
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Uninitialized State Variable
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Unlocked Compiler Version
Moret · CertiK · 22 Sep 2022 · Report ↗
- Low Open
Variables That Could Be Declared as `constant`
Moret · CertiK · 22 Sep 2022 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Moret | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 1 medium · 16 low 9 fixed · 10 open | skynet.certik.com ↗ |
Findings19
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 8 | 0 | 8 |
HighCentralization RisksMoret · CertiK · 22 Sep 2022Open
In the contract `Moret` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and withdraw pool tokens, set the protocol fee, modify protocol recipient, etc. 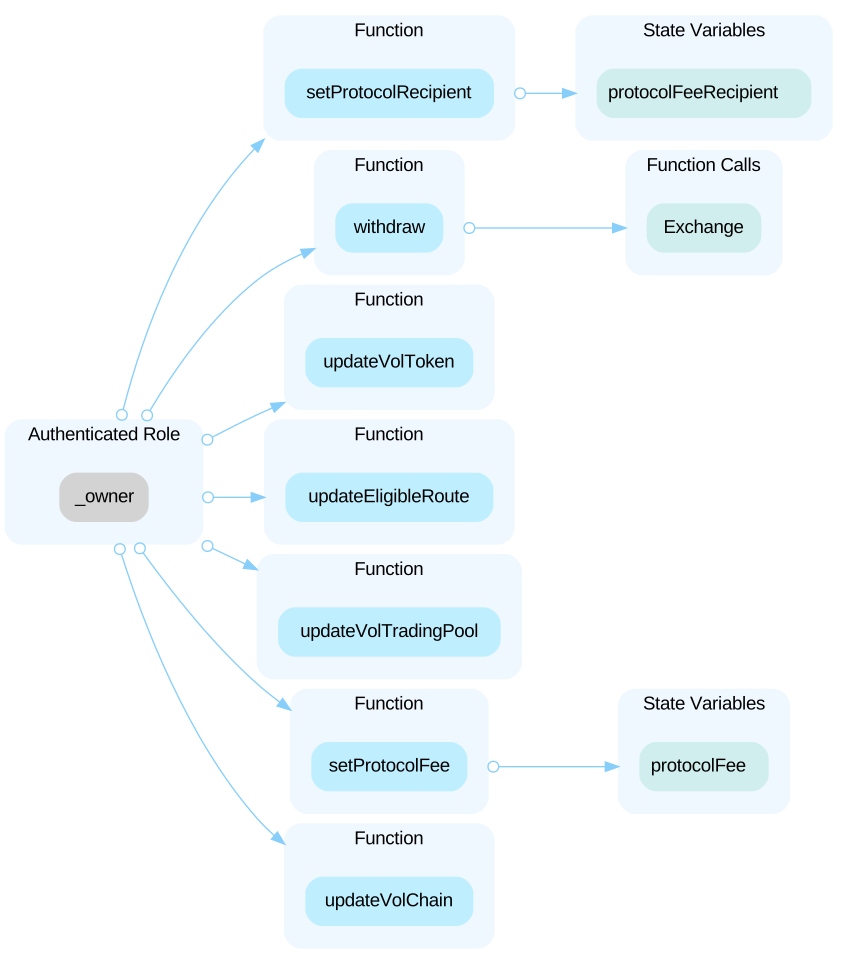 Furthermore, the role `broker` has authority over the `mint()` function. Any compromise to the `broker` address may allow the hacker to take advantage of this authority and mint any amount of tokens. In the contract `MarketMaker` the role `hedgingBot` has authority over the functions shown in the diagram below. Any compromise to the `hedgingBot` account may allow the hacker to take advantage of this authority and trade swaps/loans and modify loan interest. 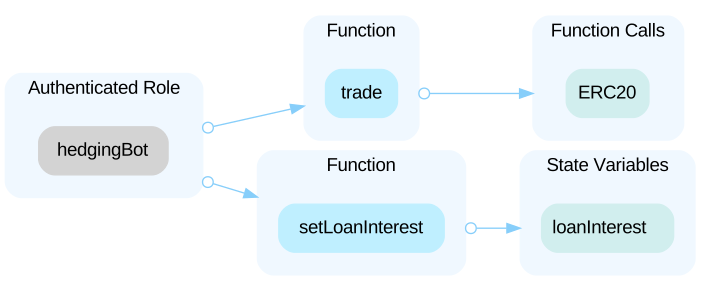 Furthermore, the role `exchange` has authority over the `settlePayment()` function. Any compromise to the `exchange` address may allow the hacker to take advantage of this authority and send option payouts. In the contract `Pool` the role `exchange` has authority over the functions shown in the diagram below. Any compromise to the `exchange` account may allow the hacker to take advantage of this authority and mint and burn Pool tokens. 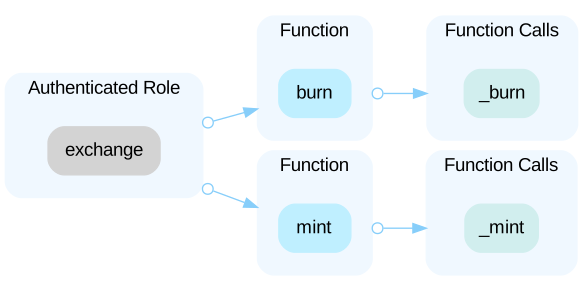 Furthermore, the role `_owner` has authority over the function `setPoolParameters()`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update some of the parameters of the contract. In the contract `Migrations` the role `owner` has authority over the function `setCompleted()`. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and change the value of the last completed migration. In the contract `OptionVault` the role `EXCHANGE` has authority over the functions `addOption()`, `stampActiveOption()` and `stampExpiredOption()`. Any compromise to the `EXCHANGE` account may allow the hacker to take advantage of this authority and add new option contracts, stamp option as an active contract and stamp option as an expired contract. In the contract `VolatilityChain` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and reset volatility parameters and remove tenors. 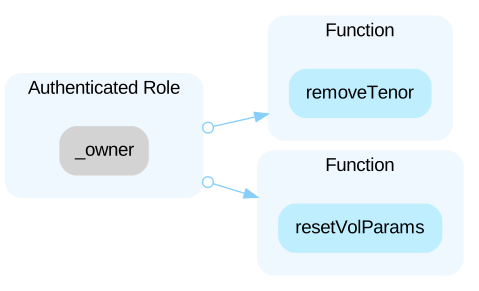 Furthermore, the role `UPDATE_ROLE` has authority over the function `update()`. Any compromise to the `UPDATE_ROLE` account may allow the hacker to take advantage of this authority and update volatility. In the contract `VolatilityToken` the role `EXCHANGE` has authority over the functions `mint()`, `burn()` and `pay()`. Any compromise to the `EXCHANGE` account may allow the hacker to take advantage of this authority and mint and burn as much tokens as they wanted.
Open the reportHighInitial Token DistributionMoret · CertiK · 22 Sep 2022Open
Tokens are sent to deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
Open the reportLowAmbiguous Error Messages and EventsMoret · CertiK · 22 Sep 2022Open
The highlighted error messages do not describe the error correctly.
Open the reportLowCommented Out CodeMoret · CertiK · 22 Sep 2022Open
Commented out code is redundant.
Open the reportLowMissing Error MessagesMoret · CertiK · 22 Sep 2022Open
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
Open the reportLowThird Party DependencyMoret · CertiK · 22 Sep 2022Open
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. - The contract `VolatilityChain` interacts with third party contract with `AggregatorV3Interface` interface via `priceInterface`. ```solidity=21 AggregatorV3Interface internal priceInterface; ```
Open the reportLowUnchecked Value of ERC-20 `transfer()`/`transferFMoret · CertiK · 22 Sep 2022Open
The linked `transfer()`/`transferFrom()` invocations do not check the return value of the function call which should yield a `true` result in case of a proper ERC-20 implementation.
Open the reportLowUninitialized State VariableMoret · CertiK · 22 Sep 2022Open
One or more state variables are used without being initialized in the constructor. ```solidity=27 mapping(uint256=>EnumerableSet.UintSet) internal latestBookTimeSet; ``` - `latestBookTimeSet` is never initialized, but used in `VolatilityChain.update()`.
Open the reportLowUnlocked Compiler VersionMoret · CertiK · 22 Sep 2022Open
The contract has unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
Open the reportLowVariables That Could Be Declared as `constant`Moret · CertiK · 22 Sep 2022Open
The linked variables could be declared as `constant` since these state variables are never modified.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
Moret: questions
Is Moret audited?
Trustblock holds 1 public audit report for Moret, dated 22 Sep 2022. The latest is by CertiK (“Moret”).
Who audited Moret?
CertiK wrote the report Trustblock holds for Moret.
Are there open findings in Moret’s audits?
10 findings are still open or acknowledged in the firms’ reports: 2 high, 8 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="moret"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us