
OSCAR audit reports
OSCAR has 1 public audit report from CertiK; dated 24 Jan 2025; no critical findings reported. It also holds 1 deployed contract on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm8
Statuses are the security firms’ own
8 findings are still open or acknowledged in the firms’ reports: 2 high, 6 low (all open).
- High
- 2
- Low
- 6
- High Open
Centralization Risks (devWallet)
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- High Open
Initial Token Distribution
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
Miscalculation of Max Holding
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
Missing Error Messages
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
State Variable Should Be Declared Constant
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
Unnecessary Unlimited LP Token Approval in `addLP
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
Unused state variable
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
- Low Open
Variables That Could Be Declared as Immutable
Oscar - Audit · CertiK · 24 Jan 2025 · Report ↗
Audits1
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| Oscar - Audit | Security firm: CertiK | Date: | Scope: 1 address on Ethereum | None open | Findings: 3 high · 7 low 2 fixed · 8 open | skynet.certik.com ↗ |
Findings10
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 6 | 0 | 1 |
HighCentralization Risks (devWallet)Oscar - Audit · CertiK · 24 Jan 2025Open
In the contract `OSCAR`, the role `devWallet` has authority over the functions shown in the diagram below. Any compromise to the `devWallet` account may allow the hacker to take advantage of this authority and withdraw the contract's ETH balance to the dev wallet owner, withdraw collected `OSCAR` tokens to the dev wallet, and perform token swaps for a specified percentage to swap collected `OSCAR` tokens to WETH and send to the `marketingWallet`. 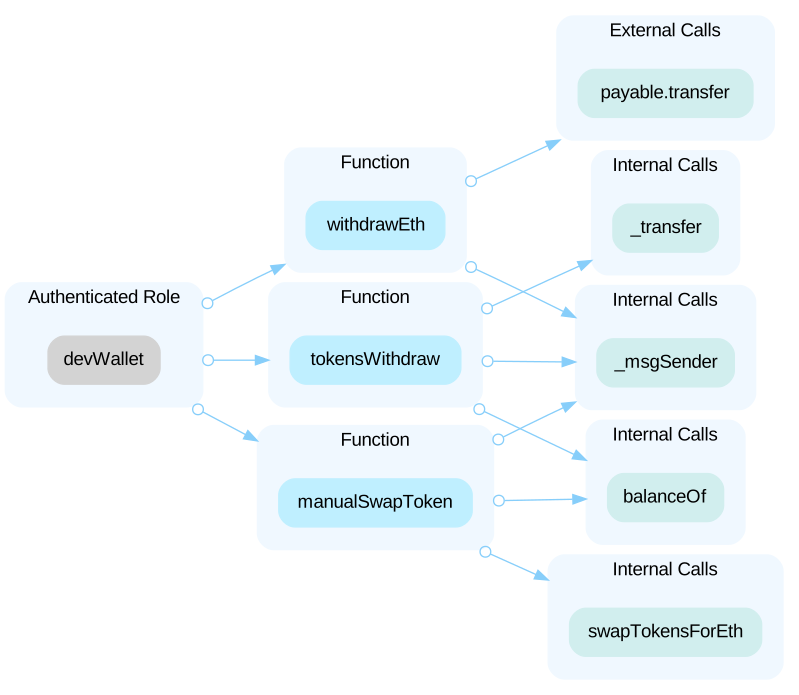
Open the reportHighInitial Token DistributionOscar - Audit · CertiK · 24 Jan 2025Open
All of the `OSCAR` tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportLowMiscalculation of Max HoldingOscar - Audit · CertiK · 24 Jan 2025Open
The transaction may be charged fees, so the max holding of the receiver should be the sum of the held tokens and the amount received from the transfer. The fees should not be included in the max holding.
Open the reportLowMissing Error MessagesOscar - Audit · CertiK · 24 Jan 2025Open
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
Open the reportLowState Variable Should Be Declared ConstantOscar - Audit · CertiK · 24 Jan 2025Open
State variables that never change should be declared as `constant` to save gas. ```solidity=513 uint256 public initialTotalSupply = 1000000000 * 10**_decimals; ``` - `initialTotalSupply` should be declared `constant`.
Open the reportLowUnnecessary Unlimited LP Token Approval in `addLPOscar - Audit · CertiK · 24 Jan 2025Open
In the `addLPToUniswap()` function, the contract owner adds liquidity to the DEX pair and sends the received LP tokens to the wallet address `0xf75ABFB159a5a960F854be03575Df74277cB72e8`. The contract grants unlimited approval of LP tokens to the DEX router, which is unnecessary because the token contract itself does not retain any LP tokens.
Open the reportLowUnused state variableOscar - Audit · CertiK · 24 Jan 2025Open
Some state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. Variable `deadAddress` in `OSCAR` is never used in `OSCAR`. ```solidity=510 address private constant deadAddress = address(0xdead); ```
Open the reportLowVariables That Could Be Declared as ImmutableOscar - Audit · CertiK · 24 Jan 2025Open
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0xebb66a88cedd12bfe3a289df6dfee377f2963f12 | Chain: Ethereum | Source code: Verified source |
OSCAR: questions
Is OSCAR audited?
Trustblock holds 1 public audit report for OSCAR, dated 24 Jan 2025. The latest is by CertiK (“Oscar - Audit”).
Who audited OSCAR?
CertiK wrote the report Trustblock holds for OSCAR.
Are there open findings in OSCAR’s audits?
8 findings are still open or acknowledged in the firms’ reports: 2 high, 6 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="oscar"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us