
OSCAR security record
As of 14 Oct 2026, OSCAR has 1 audit report on Trustblock, by CertiK, dated 24 Jan 2025. That report lists no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits and findings, contracts and incidents up to Oct 2026. Statuses are the security firms’ own. Trustblock does not review code.
Audits1
Newest first
| Audit | Security firm | Date | Scope | Critical findings | Report |
|---|---|---|---|---|---|
| Oscar - Audit | Security firm: CertiK | Date: | Scope: 1 address on Ethereum | No open critical findings | Open · skynet.certik.com |
Findings10
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 6 | 0 | 1 |
HighCentralization Risks (Owner)Oscar - Audit · CertiK · 24 Jan 2025Fixed
In the contract `OSCAR`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add liquidity to Uniswap, exclude account from fees, exclude address from max transaction, enable trading and swapping, remove transaction and wallet limits, set automated market maker pair, set the buy and sell fees, update the swap threshold amount. 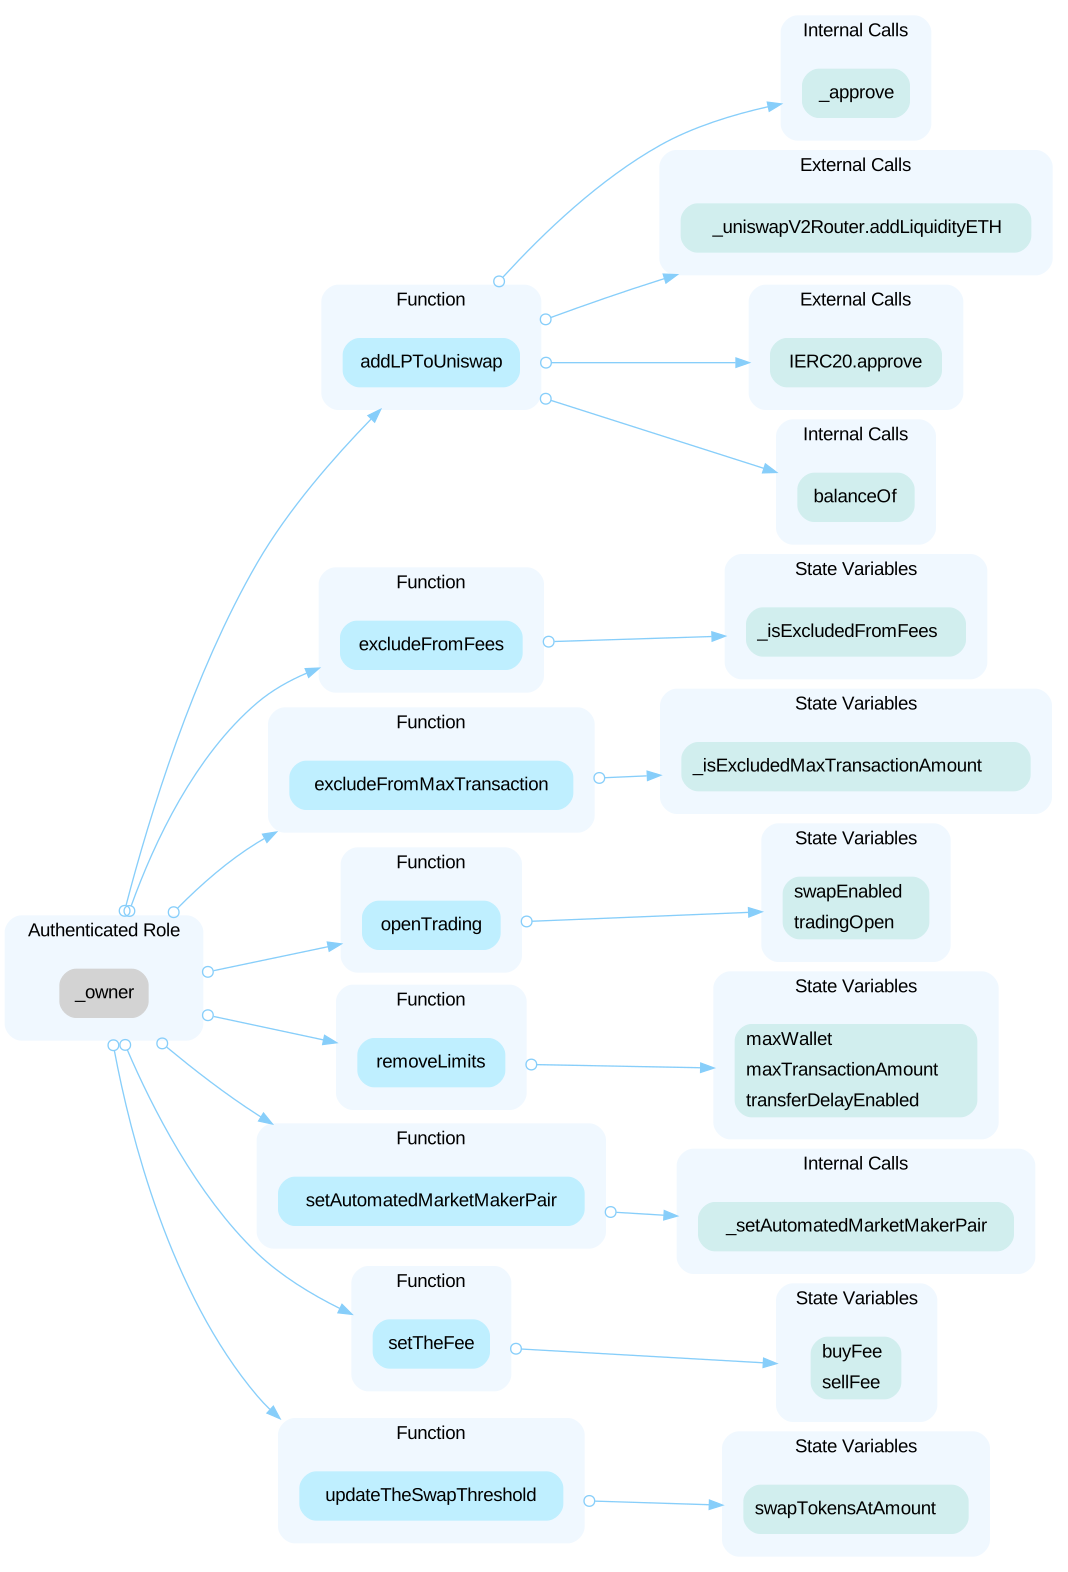 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the contract ownership or renounce contract ownership. 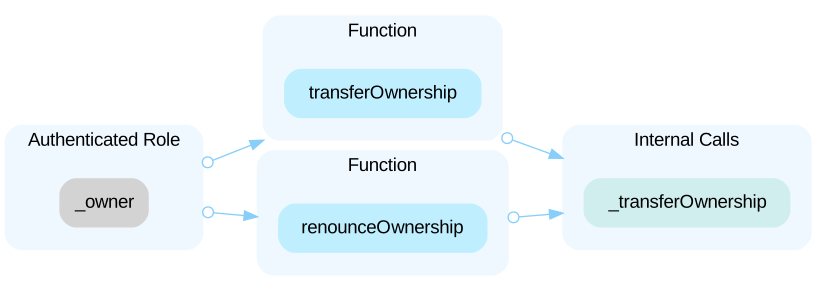
Open the reportLowVulnerability to Sandwich AttackOscar - Audit · CertiK · 24 Jan 2025Fixed
In the `swapTokensForEth()` function, the minimum swap output amount (`amountOutMin`) is set to zero, which opens up the contract to sandwich attacks. A sandwich attack can occur when an attacker notices a transaction involving token swaps or liquidity additions that lack slippage restrictions or minimum output amount settings. The attacker can exploit this by frontrunning the transaction to purchase one of the assets, thereby manipulating the exchange rate, and then backrunning the transaction to sell the asset for a profit. ```solidity=689 _uniswapV2Router.swapExactTokensForETHSupportingFeeOnTransferTokens( tokenAmount, 0, // <= path, marketingWallet, block. Timestamp ); ``` The `swapTokensAtAmount` threshold, which dictates when the `swapBack()` function is triggered, is set to a high value of 2,000,000,000,000,000. Given that the `Oscar` token has 9 decimals, this threshold is excessively large, increasing the profitability of a sandwich attack when the contract accumulates fees reaching this amount.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0xebb66a88cedd12bfe3a289df6dfee377f2963f12 | Chain: Ethereum | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="oscar"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us