As of 3 Nov 2026, UVToken has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 24 Feb 2023. Those reports list no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 1 | 0 | 1 |
| Medium | 0 | 2 | 4 |
| Low | 8 | 2 | 6 |
The following contracts(see "Contracts") contain Privileged functions(see "Privileged Function") can only call by privileged roles. Any compromise to the Owner account may allow a hacker to take advantage of this authority to modify the project configurations and withdraw funds from the contract. **"Contracts"** * UVTPledge.sol * UVCMine.sol **"Privileged Roles"** * owner_ **"Privileged Functions"** In UVCMine.sol: * setOwner * setMiner * setNumMint * setUvc * setCycle * withdrawErc20Token In UVCPledge.sol: * withdrawErc20Token * withdrawEth * SetToken * SetOwner * createPledge
Open the reportThe application is signed with v1 signature scheme, making it vulnerable to Janus vulnerability on Android <7.0 The Janus vulnerability stems from the possibility to add extra bytes to APK files and to DEX files. On the one hand, an APK file is a zip archive, which can contain arbitrary bytes at the start, before its zip entries (actually more generally, between its zip entries). The JAR signature scheme only takes into account the zip entries. It ignores any extra bytes when computing or verifying the application’s signature. On the other hand, a DEX file can contain arbitrary bytes at the end, after the regular sections of strings, classes, method definitions, etc. A file can, therefore, be a valid APK file and a valid DEX file at the same time. References: - https://www.xda-developers.com/janus-vulnerability-android-apps/ - https://medium.com/mobis3c/exploiting-apps-vulnerable-to-janus-cve-2017-13156-8d52c983b4e0
Open the reportWhen analyzing the `Info.plist` file, we found that the application sets `NSAllowsArbitraryLoads` to `true`, which completely disables ATS for all network connections.
Open the reportIt was found that cleartext traffic was configured to be permitted within the `AndroidManifest.xml` file of the Android application package.
Open the reportThe `UvToken` application does not adequately detect if the device is rooted/jailbroken. As a result, the data which is stored by the applications can be exposed when the device is rooted or jailbroken.
Open the reportOn mobile devices, a screenshot of the current activity is taken when an application goes into the background and displayed for aesthetic purposes when the app returns to the foreground. This feature may pose a security risk. Sensitive data may be exposed if the user background the application while sensitive data is displayed. A malicious application that is running on the device and able to continuously capture the screen may also expose data. 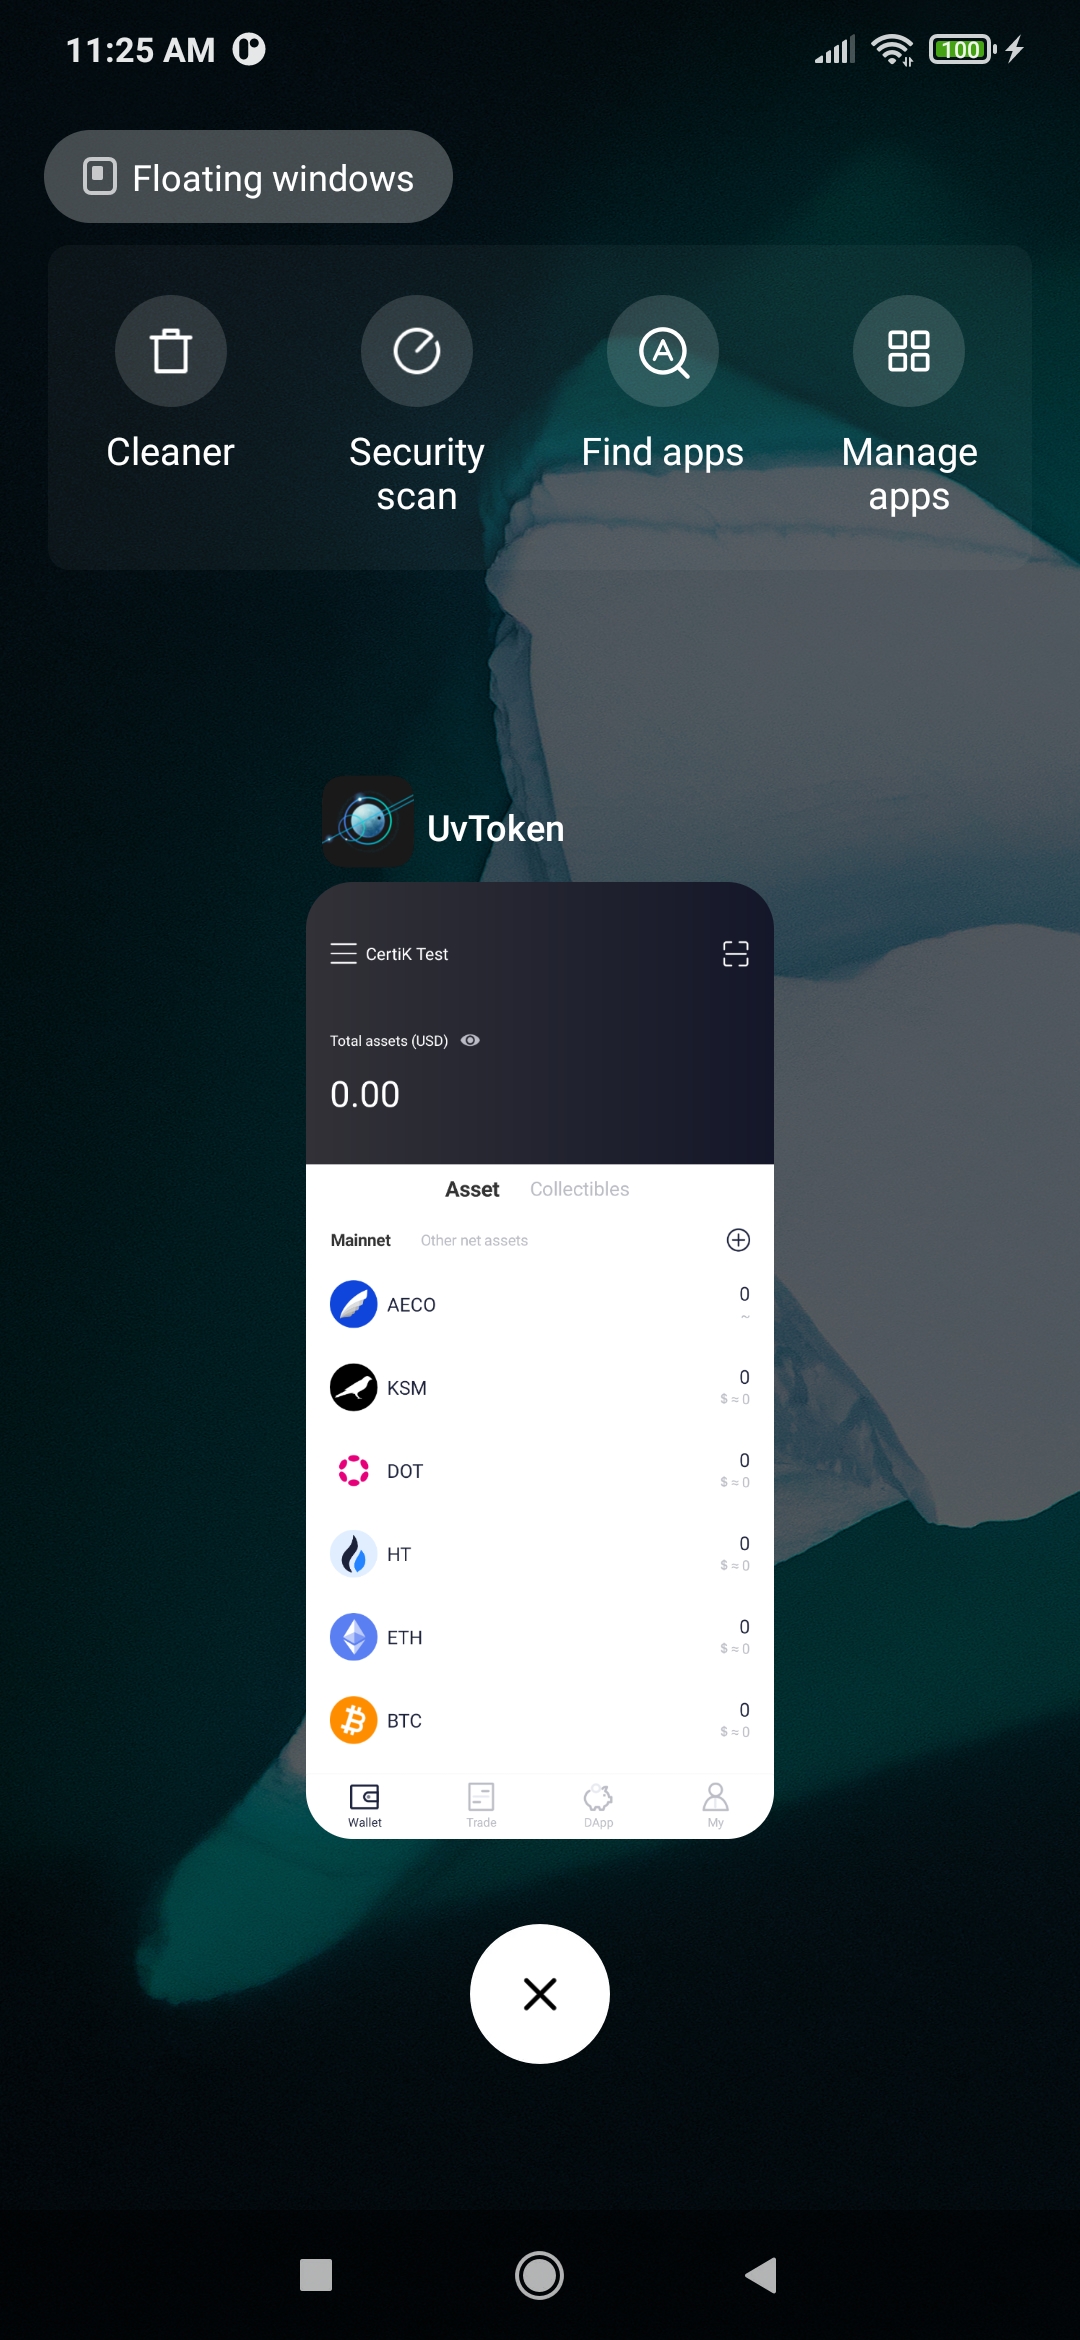 Even though the iOS version was blurring the content of the screenshot when the application was in background, it is worth mentioning that it was not done right after using the multitask gesture, but after exiting it. Other secure applications tend to blur the content right when the multitask functionality is used.
Open the reportThe iOS and Android applications were interacting with third party services located on different domains.
Open the reportThe UvToken iOS application used the data directory to store information related to the user, like the HTTP Cache, which contains session information and temporary files, but the protection classes associated to those items were not sufficiently secure. When a new file is created on the data directory, it is assigned a protection class by the application that creates it. Each class uses different policies to determine when the data is accessible. Data Protection is an encryption framework provided by Apple to offer file encryption capabilities to the file system. This framework is active by default although the default settings are rarely appropriate. The default option for items in the data directory is `NSFileProtectionCompleteUntilFirstUserAuthentication`. As the name implies, items are encrypted until the first time the user log in, then all files are saved in clear text.
Open the reportThe affected endpoints used a wildcard SSL certificate. Such certificates offer a cost-effective means of extending SSL/TLS coverage across multiple servers and applications. However, although wildcard certificates are cryptographically no weaker than dedicated certificates, the effective security level is reduced to that of the weakest application or component.
Open the report| Address | Chain | Source code |
|---|---|---|
| 0xa9bd…85690xa9bdd634725eab26ab297e969071fadc45118569 | Chain: BNB Chain | Source code: Verified source |
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="uvtoken"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us