As of 3 Nov 2026, UVToken has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 24 Feb 2023. Those reports list no open critical findings. It also holds 1 deployed contract on 1 chain.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Newest first
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 1 | 0 | 1 |
| Medium | 0 | 2 | 4 |
| Low | 8 | 2 | 6 |
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. ```solidity=427 payToken(tokenAddress_, _userAddr, _pledgeAmount); ``` - Transferring tokens by `_pledgeAmount`. - This function call executes the following operation. ```solidity=429 IPledge_.insertUVTPledge(_userAddr, _pledgeAmount); ``` - The `_pledgeAmount` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
Open the reportMobile applications need to have an option for the users to log out and erase all stored data. This way, they can be in full control of the information that remains in the devices. The risk of this finding was raised to medium because of the lack of root/jailbreak detection and the weak password policy in use. See the screenshot below showing a message indicating that it is not possible to delete the active wallet. Therefore, one wallet will always remain stored: 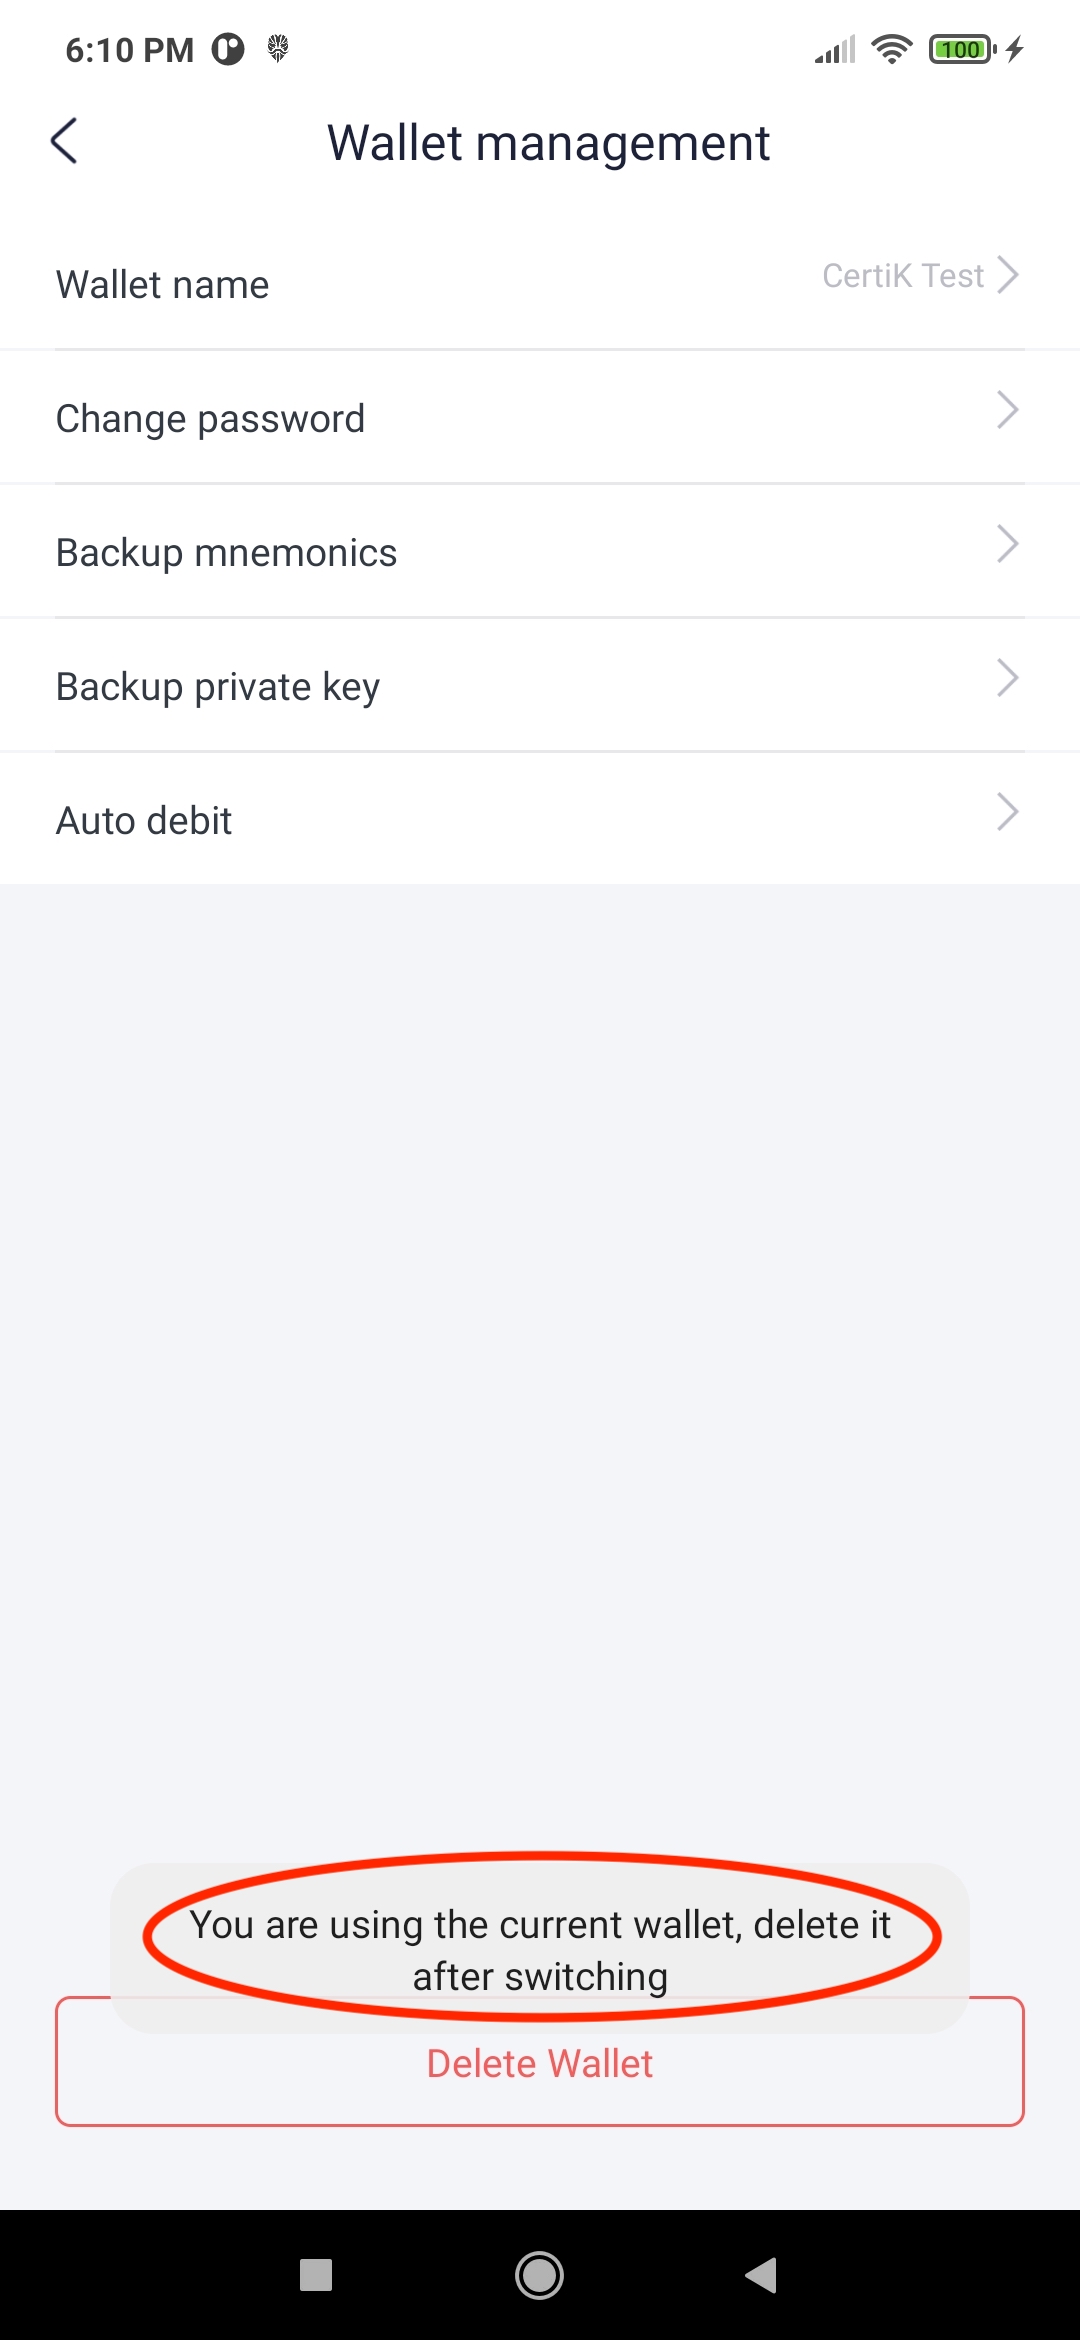
Open the reportThere should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportThe contract is serving as the underlying entity to interact with one or more out-of-scope dependencies. The scope of the audit treats out-of-scope entities as black boxes and assume their functional correctness. ```solidity=277 IFinance public IFinance_; ``` - The contract `UVTPledge` interacts with out-of-scope contract with `IFinance` interface via `IFinance_`. --- ```solidity=279 IERC20 public tokenAddress_; ``` - The contract `UVTPledge` interacts with out-of-scope contract with `IERC20` interface via `tokenAddress_`. --- ```solidity=324 function createPledge(IPledge _IPledge, bool _isValid) external authorised ``` - The contract `UVTPledge` interacts with out-of-scope contract with `IPledge` interface via `_IPledge`.
Open the report| Address | Chain | Source code |
|---|---|---|
| 0xa9bd…85690xa9bdd634725eab26ab297e969071fadc45118569 | Chain: BNB Chain | Source code: Verified source |
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="uvtoken"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us