
BlastUP audit reports
BlastUP has 3 public audit reports from CertiK and Hacken; the latest is Hacken, 15 May 2024; no critical findings reported.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm15
Statuses are the security firms’ own
15 findings are still open or acknowledged in the firms’ reports: 3 high, 1 medium, 11 low (all open).
- High
- 3
- Medium
- 1
- Low
- 11
- High Open
Centralization Related Risks
BlastUP - Addendum · CertiK · 21 Mar 2024 · Report ↗
- High Open
Initial Token Distribution
BlastUP - Addendum · CertiK · 21 Mar 2024 · Report ↗
- High Open
Centralization Related Risks
BlastUP - Audit · CertiK · 29 Feb 2024 · Report ↗
- Medium Open
Signature Replay In Tier Registration
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
`decimals()` is not a part of the `ERC-20` standard
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
Centralization Risk For Privileged Actors
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
Fee-On-Transfer Token Handling Flaw
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
Inconsistent Validation Checks Across Token Setting Functions
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
Lack of Boundary Checks
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
- Low Open
Missing Validation of Tier Hierarchy
BlastUp / Launchpad · Hacken · 15 May 2024 · Report ↗
Audits3
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| BlastUp / Launchpad | Security firm: Hacken | Date: | Scope: Files listed | None open | Findings: 2 medium · 9 low 3 fixed · 8 open | hacken.io ↗ |
| BlastUP - Addendum | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 2 high · 5 low 4 fixed · 3 open | Original removed |
| BlastUP - Audit | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 1 high · 2 medium · 4 low 3 fixed · 4 open | Original removed |
Findings34
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 1 | 0 | 3 |
| Low | 11 | 0 | 7 |
HighCentralization Related RisksBlastUP - Addendum · CertiK · 21 Mar 2024Open
In the contract `PresaleBlast`, the `OPERATOR_ROLE` role has the authority to toggle the contract's pause state. This action can impact the regular operation of the subsequent functions: - `depositUSDBTo()` - `depositUSDB()` - `depositWETHTo()` - `depositWETH()` The pause state also impacts the following functions in the `Presale` contract: - `depositUSDCTo()` - `depositUSDC()` - `depositUSDTTo()` - `depositUSDT()` - `depositCoinTo()` - `depositCoin()` Moreover, the `OPERATOR_ROLE` and `DEFAULT_ADMIN_ROLE` roles are established within the `Presale` contract and assigned to the address `operator` and the address `DAO`, respectively. The role `OPERATOR_ROLE` has authority over the functions shown in the list below. * `setStage(uint256 stageIterator_)` - Enables the operator to set the presale stage. It will allow the operator to change presale stage to a later stage which requires higher costs. * `updateTotalSold(uint256 amount)` - Permits the operator to manually adjust the total tokens sold. * `pause()` - Pause the contract, stopping most of its operations. * `unpause()` - Unpause the contract, resuming its operations. The role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the list below. * `updateProtocolWallet(address wallet)` - Allows the admin to update the address of the `protocolWallet`. * `rescueFunds(IERC20 token, uint256 amount)` - Allows the admin to withdraw specified ERC20 tokens or native coins from the contract. The `Presale` contract also inherit `AccessControl` contract from Openzeppelin, the role `DEFAULT_ADMIN_ROLE` alse has authority over the functions from its parent contract list below. * `grantRole(bytes32 role, address account)` - Grants `role` to `account`. * `revokeRole(bytes32 role, address account)` - Revokes `role` from `account`. Any compromise to the `OPERATOR_ROLE` account or `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority, change some important state variables, and even withdraw all assets in the contract through the `rescueFunds()` function and manage the ownership of contracts.
Open the reportHighInitial Token DistributionBlastUP - Addendum · CertiK · 21 Mar 2024Open
All of the `BLP` tokens are sent to the address `daoAddress`. This is a centralization risk because the address `daoAddress` can distribute tokens without obtaining the consensus of the community. Any compromise to this address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighCentralization Related RisksBlastUP - Audit · CertiK · 29 Feb 2024Open
In the contracts `Presale` and `PresaleBSC` the role `_owner` has authority over the functions shown in the list and diagram below. * `updateProtocolWallet(address wallet)` - Allows the owner to update the address of the `protocolWallet`. * `setStage(uint256 stageIterator_)` - Enables the owner to set the presale stage. It will allow the owner to change presale stage to a later stage which require higher costs. * `updateTotalSold(uint256 amount)` - Permits the owner to manually adjust the total tokens sold. * `pause()` - Pause the contract, stopping most of its operations. * `unpause()` - Unpause the contract, resuming its operations. * `rescueFunds(IERC20 token, uint256 amount)` - Allows the owner to withdraw specified ERC20 tokens or native coins from the contract. The `Presale` and `PresaleBSC` contract also inherit `Ownable` contract from Openzeppelin, the role `_owner` also has authority over the functions from its parent contract list below. * `renounceOwnership()` - Renounce the ownership of contract to leave the contract without an owner. * `transferOwnership()` - Transfers ownership of the contract to a new account. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, change some important state variables, and even withdraw all assets in the contract through the `rescueFunds()` function and manage the ownership of contracts. 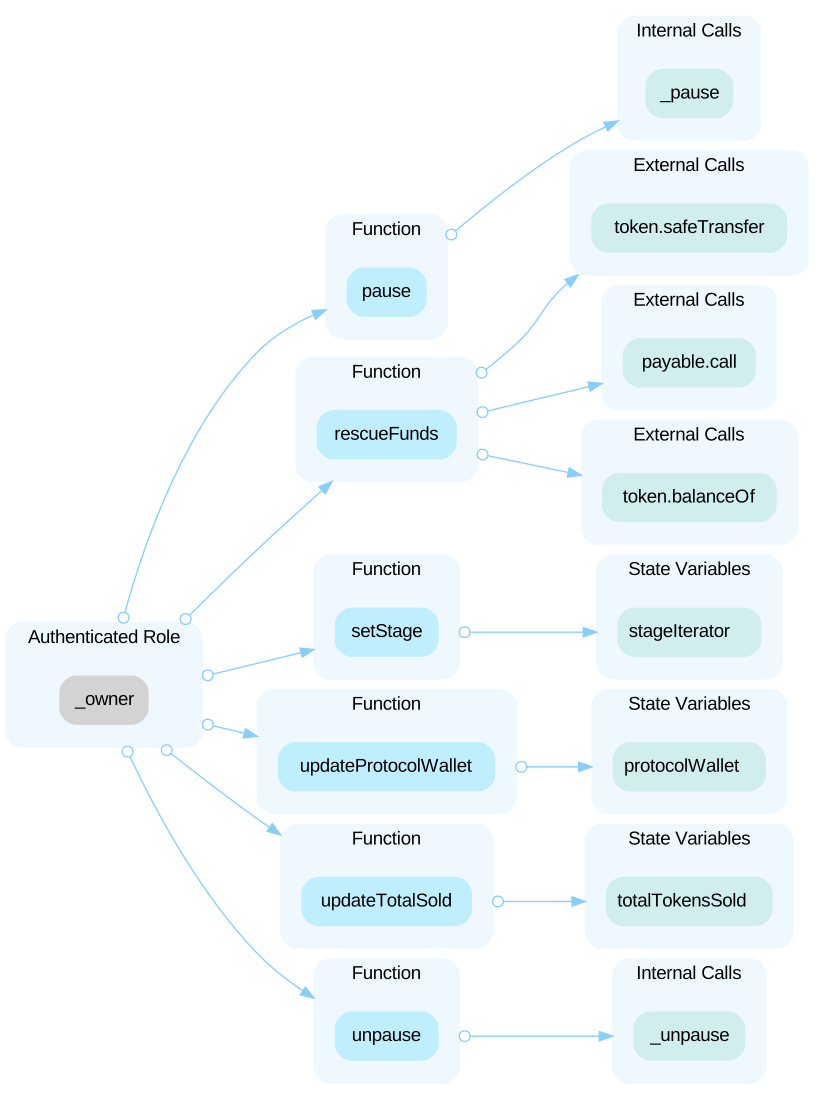
Open the reportMediumSignature Replay In Tier RegistrationBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLow`decimals()` is not a part of the `ERC-20` standardBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowCentralization Risk For Privileged ActorsBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowFee-On-Transfer Token Handling FlawBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowInconsistent Validation Checks Across Token Setting FunctionsBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowLack of Boundary ChecksBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowMissing Validation of Tier HierarchyBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportShow 5 more
LowPrivileged Functions Susceptible to Front-RunningBlastUp / Launchpad · Hacken · 15 May 2024Open
The report gives no description here.
Open the reportLowPurpose of Project DesignBlastUP - Addendum · CertiK · 21 Mar 2024Open
The audit team would like to confirm the project design: ## Centralized Functions with Timelock Mechanism The presale contracts include several centralized functions that can only be executed by accounts with the `DEFAULT_ADMIN_ROLE` or `OPERATOR_ROLE` roles. Some functions use a timelock mechanism. There is a defect in the current mechanism: the wait time for these functions to execute is set by updating `_timestamps[selector]` only on the first invocation of the function. However, after the function's logic has actually been executed, the value of `_timestamps[selector]` does not change, allowing subsequent executions to proceed immediately without waiting. For example, in the `updateProtocolWallet` function: ```solidity //NOTE function selector is: 0xe308a099 function updateProtocolWallet(address wallet) external onlyRole(DEFAULT_ADMIN_ROLE) { uint256 delayedTill = _timestamps[0xe308a099]; if(delayedTill > 0 && delayedTill <= block.timestamp) { protocolWallet = wallet; } else { _timestamps[0xe308a099] = block.timestamp + DEFAULT_DELAY; } } ``` The timestamp is set upon the first call, but if the condition `delayedTill > 0 && delayedTill <= block.timestamp` is true, the function executes and updates the `protocolWallet`, but it does not reset the `_timestamps[0xe308a099]`. This means that after the initial delay, the function can be called again without waiting for the `DEFAULT_DELAY`, defeating the purpose of the timelock. ## Purpose of `updateTotalSold` function The `updateTotalSold` function is utilized to revise the `totalTokensSold` tally during the presale phase. The audit team would like to understand the purpose of this particular metric, as opposed to the actual value of sales.
Open the reportLowChainlink aggregators return the incorrect priceBlastUP - Audit · CertiK · 29 Feb 2024Open
The function `_calculateAmount` calls `latestRoundData()` from Chainlink to acquire the token's price. Chainlink aggregators have a built in circuit breaker if the price of an asset goes outside of a predetermined price band. The result is that if an asset experiences a huge drop in value (i.e. LUNA crash) the price of the oracle will continue to return the `minAnswer` instead of the actual price of the asset. See [Chainlink's docs](https://docs.chain.link/data-feeds#check-the-latest-answer-against-reasonable-limits) for more info. Chainlink's `latestRoundData` pulls the associated aggregator and requests round data from it. ChainlinkAggregators have `minAnswer` and `maxAnswer` circuit breakers built into them. This means that if the price of the asset drops below the `minAnswer`, the protocol will continue to value the token at `minAnswer` instead of it's actual value. This will allow users to exploit certain parts of the protocol. This discreprency could cause major issues within the protocol and potentially lead to loss of funds. This is exactly what happened to [Venus on BSC when LUNA imploded](https://rekt.news/venus-blizz-rekt/).
Open the reportLowMissing Emit EventsBlastUP - Audit · CertiK · 29 Feb 2024Open
Functions that update state variables should emit relevant events as notifications. Especially in the `setStage()` function, there is a corresponding event in the contract that can be emitted, but it has not been used.
Open the reportLowMissing Zero Address ValidationBlastUP - Audit · CertiK · 29 Feb 2024Open
The `to` address input in these functions are missing a check that it is not `address(0)`.
Open the reportContracts
No deployed address is recorded for these audits.
The reports name a repository or files. Open a report to see its scope.
BlastUP: questions
Is BlastUP audited?
Trustblock holds 3 public audit reports for BlastUP, dated 29 Feb 2024 to 15 May 2024. The latest is by Hacken (“BlastUp / Launchpad”).
Who audited BlastUP?
2 security firms wrote the reports Trustblock holds for BlastUP: CertiK and Hacken.
Are there open findings in BlastUP’s audits?
15 findings are still open or acknowledged in the firms’ reports: 3 high, 1 medium, 11 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="blastup"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us